Hooketh
 humoud/hooketh
A set of scripts that ease working with frida
android-securitydebuggersdynamic-analysis-sandboxing+2
humoud/hookethA set of scripts that ease working with frida
 idanshechter/cve-2017-13208-scanner
Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.
 acloudinthebluesky/cve-2019-6447-es-file-explorer
Technical analysis and safety-conscious research harness for CVE-2019-6447 in ES File Explorer for Android
 pealeap/cve-2026-21018
Minimal PoC for a Samsung SveService buffer overflow, demonstrating an out-of-bounds write via Binder to crash the Android system service without…
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
 rmdycz/k80pro-miro-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for RedMi K80pro miro OS 3.0.304.0
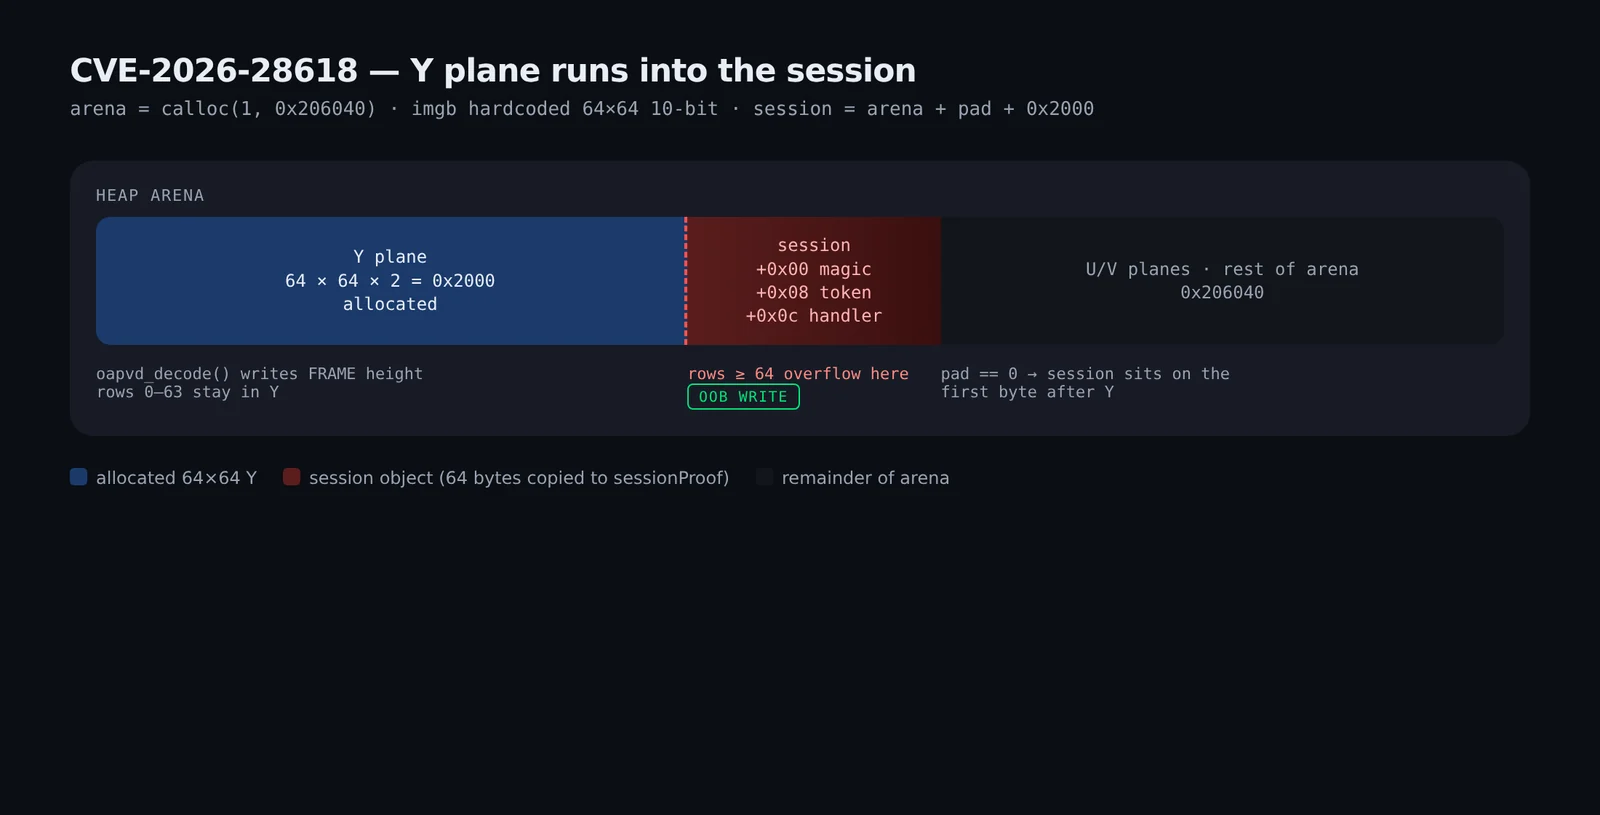 raafatabualazm/streambox-cve-2026-28618
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch
 anksgls-sj/-help-vivo-y200i-5.10.218-gki-cve-2026-43499-stack-reclaim-reaches-0x300-need-0x318
Research notes and PoC development for CVE-2026-43499 (GhostLock) kernel UAF on vivo Y200i Android 14, covering futex PI-chain stack-reclaim…
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 trinadh465/platform_art_aosp10_r33_cve-2021-0511
Android Runtime (ART) platform patch for CVE-2021-0511, addressing a security vulnerability in AOSP 10.
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…
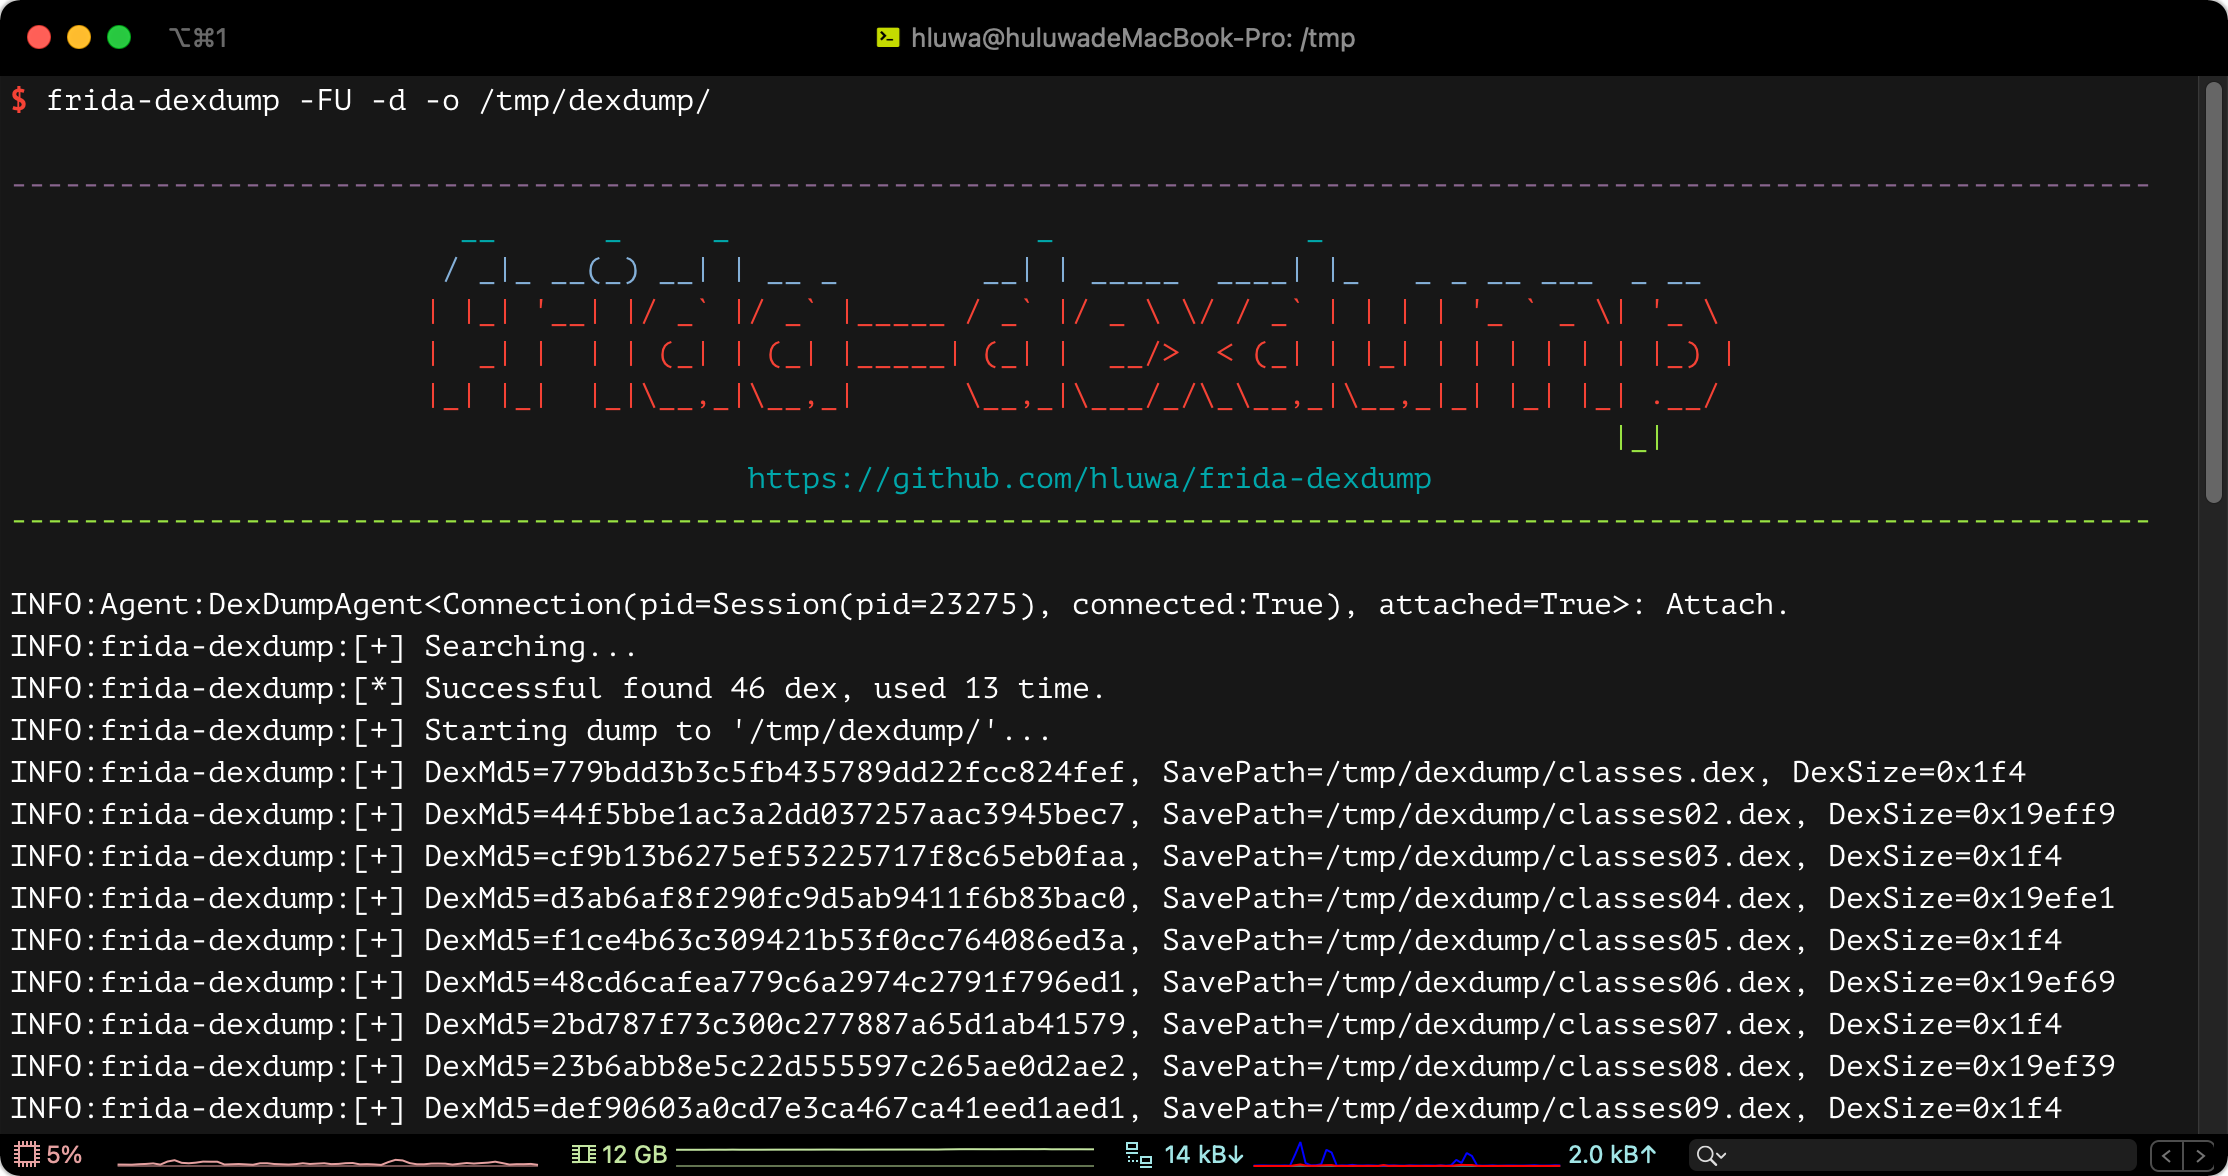 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
 ptswarm/reflutter
Flutter Reverse Engineering Framework
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
 nighthawkk/jnisleuth-mcp
Automated Android JNI RegisterNatives recovery, stripped ARM64 .so type reconstruction, OLLVM BR X8 deobfuscator, and universal LLM/MCP bridge for…
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…