skills
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
command-and-controleducationexploitation+9
671
specterops/skillsReusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 uwctcjnwlk/web3-decoder
Burp Suite extension for decoding Ethereum JSON-RPC calls and smart contract interactions, supporting multiple chains and automatic ABI retrieval.
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 orbitcurve/firmware-reverse-engineering
Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…
 ctn-qvo/auto_extract_offsets
Automated offset calculator for CVE-2026-43499, enabling precise memory offset computation for vulnerability exploitation and binary analysis.
 ugvxb/cve-2026-9490
The ACCSvc service creates a Named Pipe with a weak Security Descriptor that allows any authenticated user to connect and send messages. When a…
 aploium/shootback
a reverse TCP tunnel let you access target behind NAT or firewall
 iss4cf0ng/openshell
Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…
 null-event/cve-2024-11467
VMWare Horizon client for macOS LPE due to an XPC logic flaw. Belated POC for an 0-day I responsibly disclosed to Omnissa.
 thannikudam/topazterminator
C-based tool exploiting the vulnerable wsftprm.sys kernel driver to terminate protected EDR/AV processes on Windows, including PPL processes, via…
 pl4tyz/cve-2025-14611-centrestack-and-triofox-full-poc-exploit
CVE-2025-14611 CentreStack and Triofox full Poc/Exploit
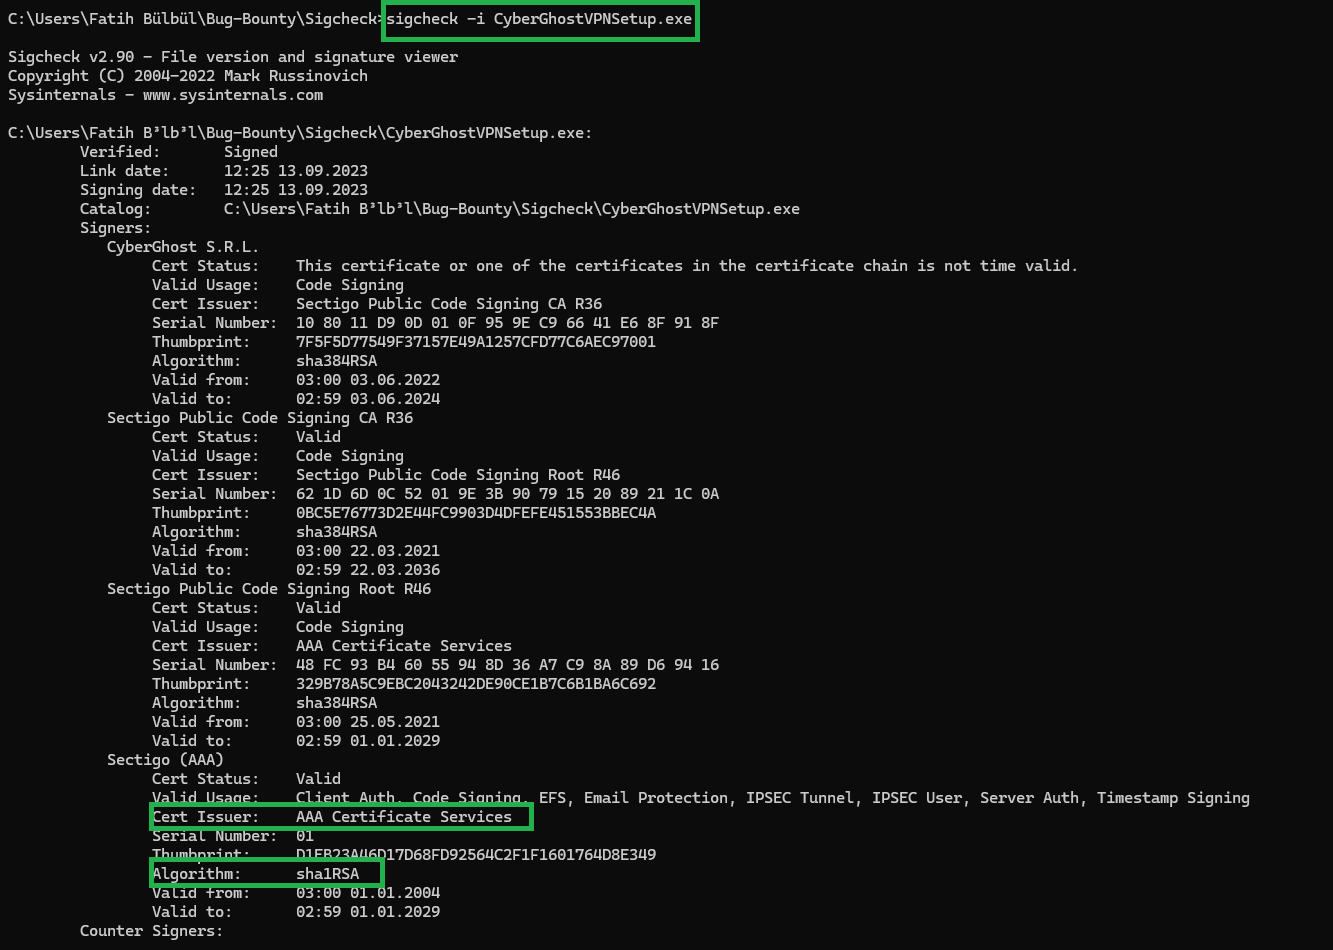 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 jarm222/cve-2025-26244
The graph functionality of DeimosC2 v1.1.0-Beta is vulnerable to Stored Cross-Site Scripting (XSS), allowing the theft of session cookie and…
 xepor/xepor
Flask-like routing framework for mitmproxy to intercept, modify, and spoof HTTP requests/responses. Enables rapid development of MITM scripts for…
 trailofbits/rpcinvestigator
Windows RPC interface discovery and analysis tool with visual endpoint enumeration, PE parsing, symbol resolution, real-time ETW sniffing, and…
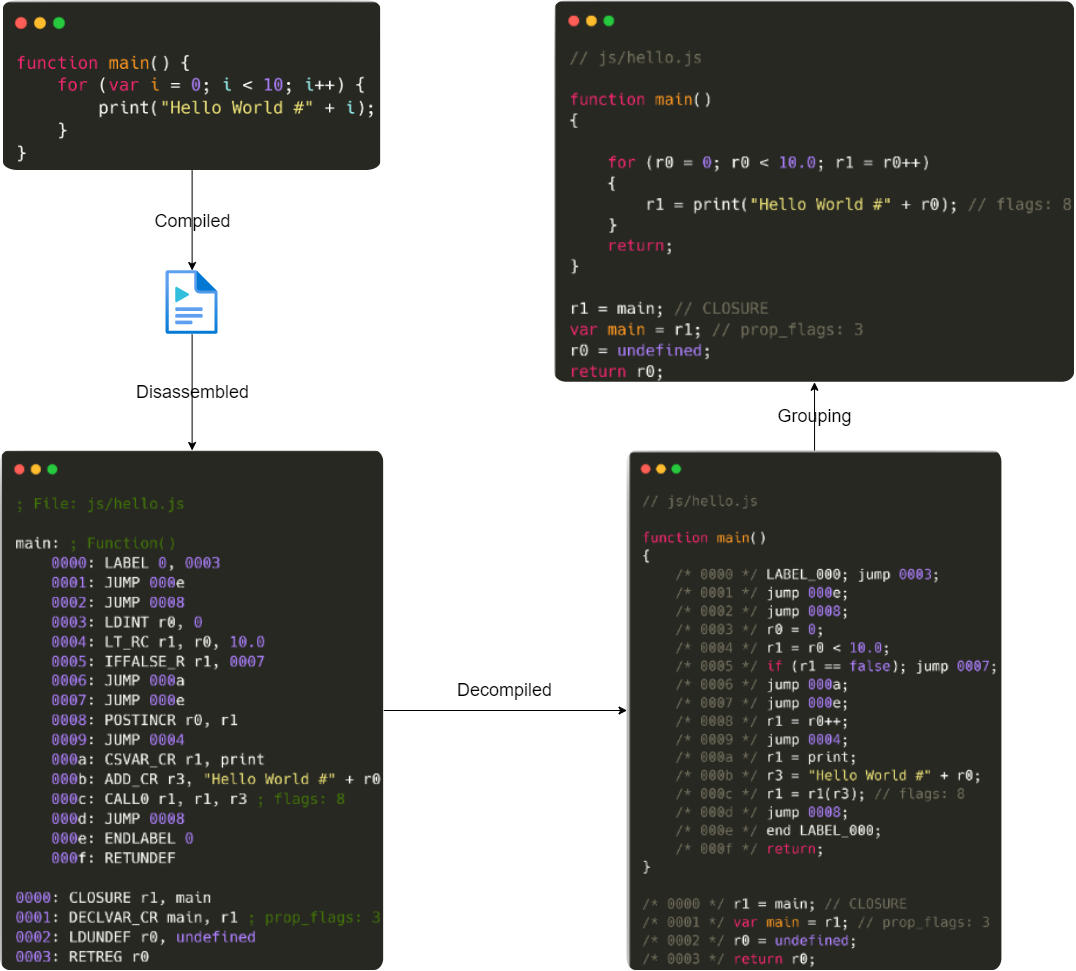 nccgroup/detaped
Detaped is a Python disassembler and decompiler for Duktape. The intended use is for source code review and analysis in situations where you only…