

libloong
 libriscv/libloong
The fastest LoongArch sandbox
binary-analysisembedded-systems-securityfuzzing+3
libriscv/libloongThe fastest LoongArch sandbox
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
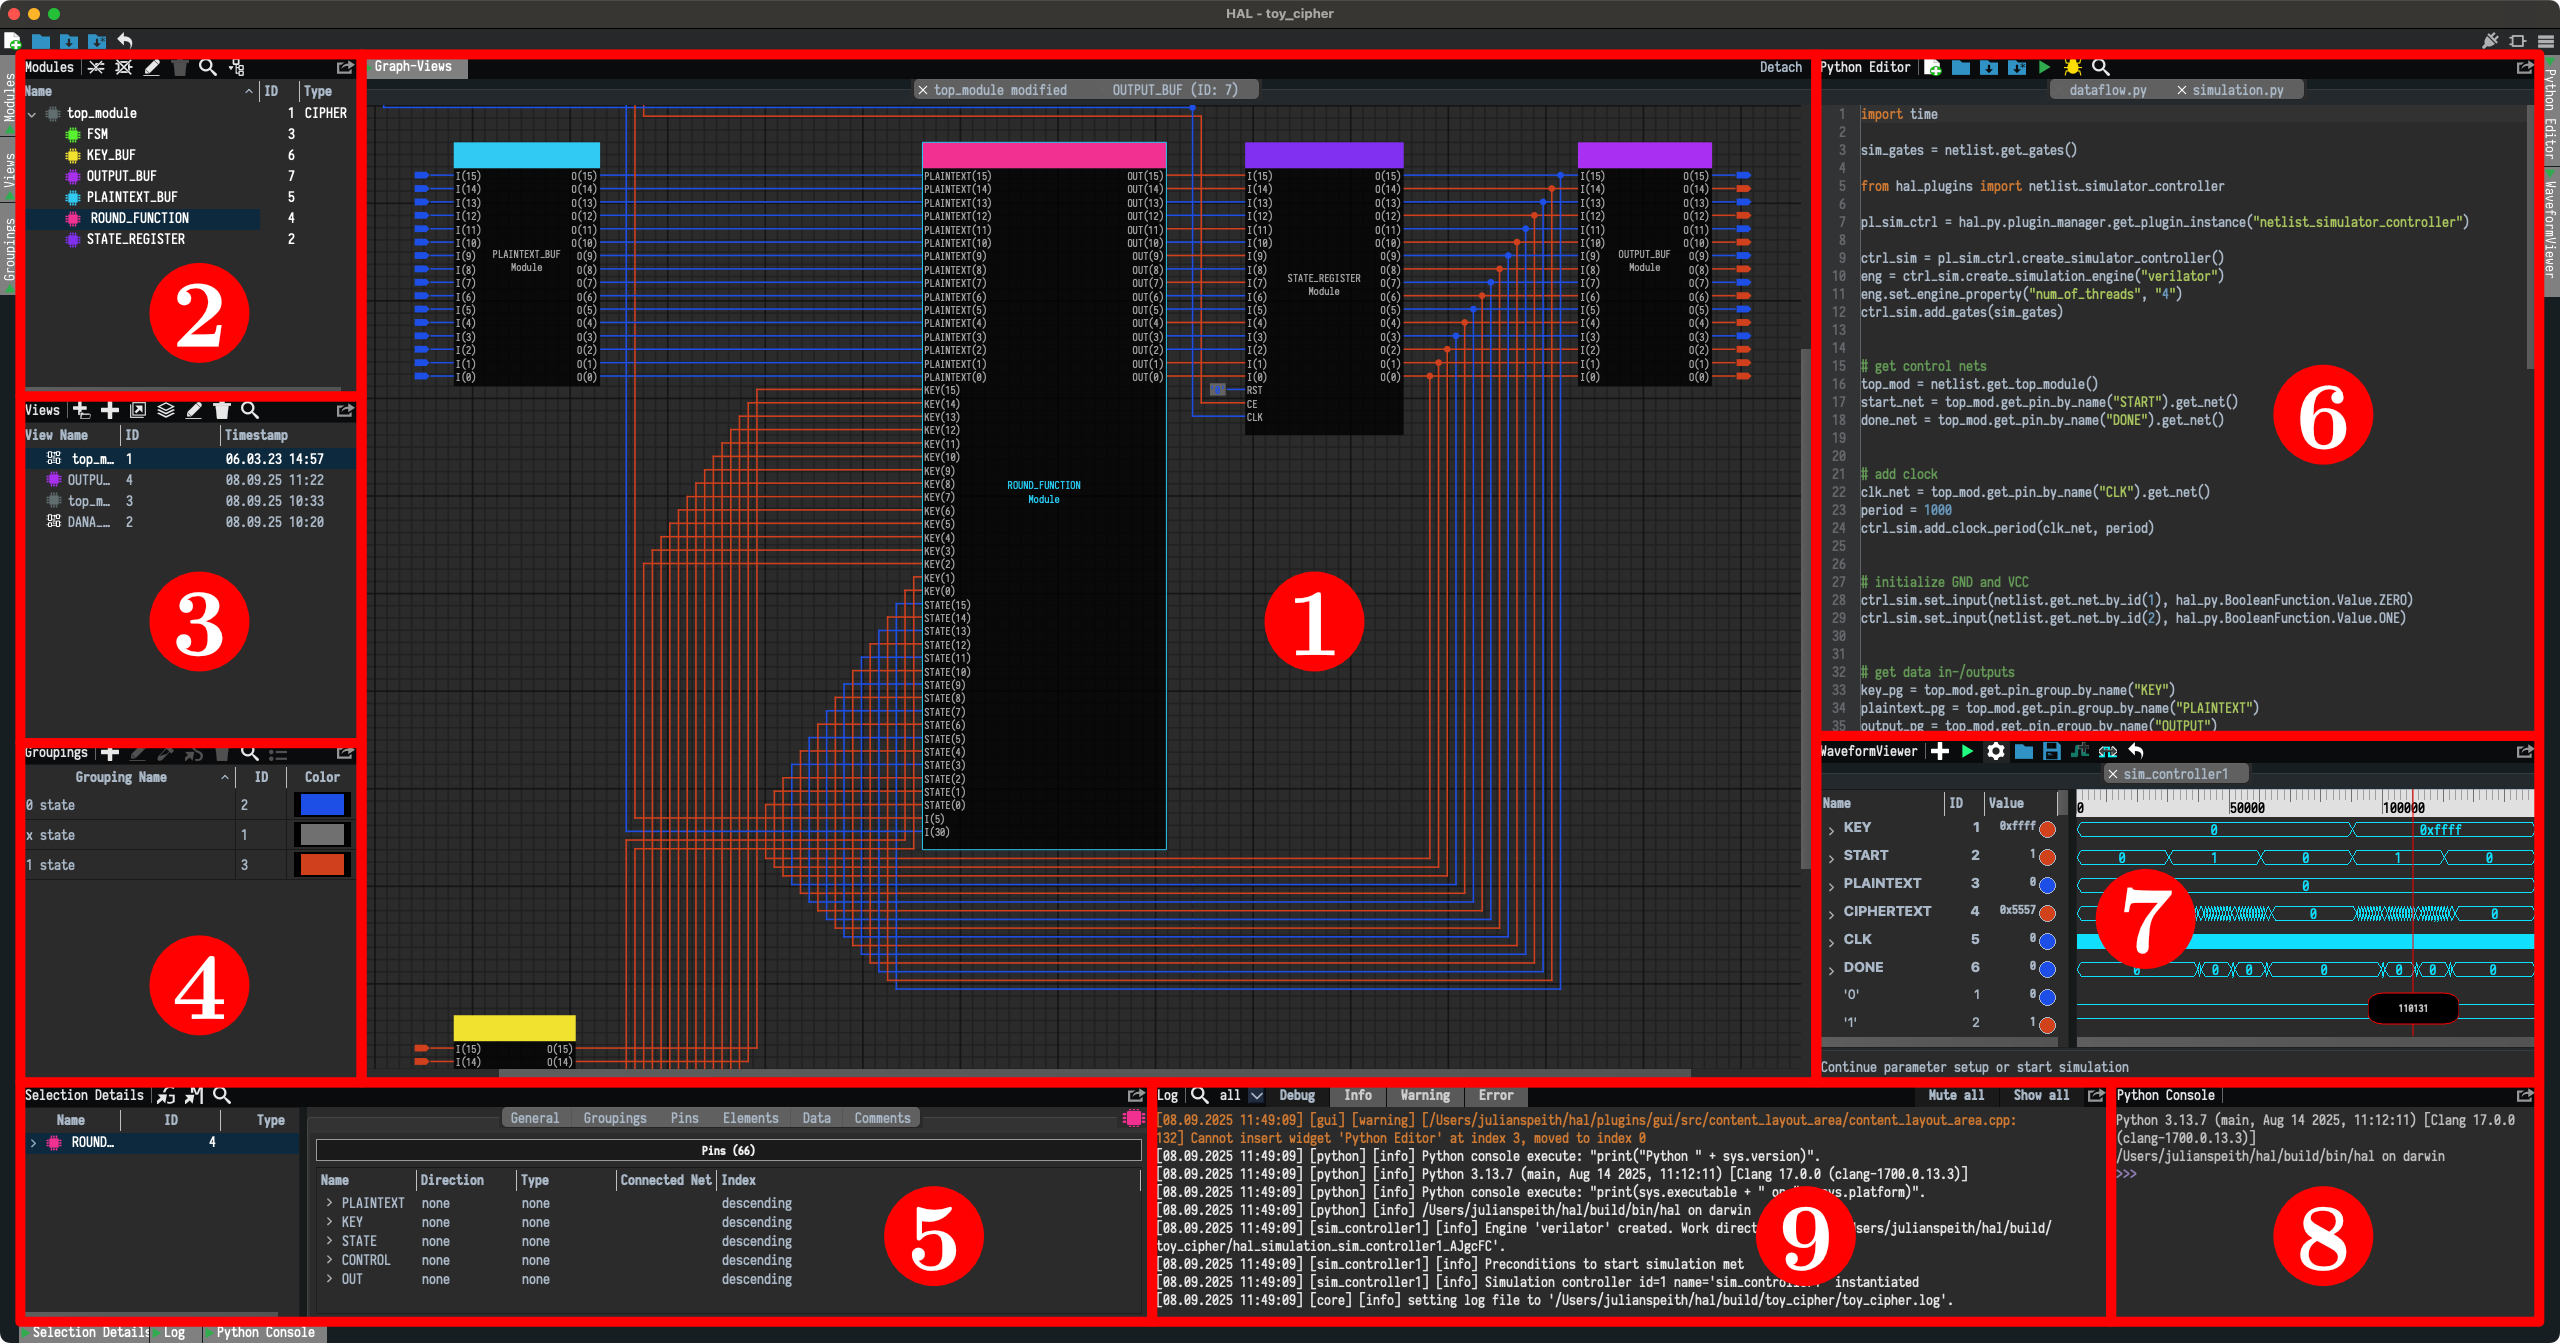
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
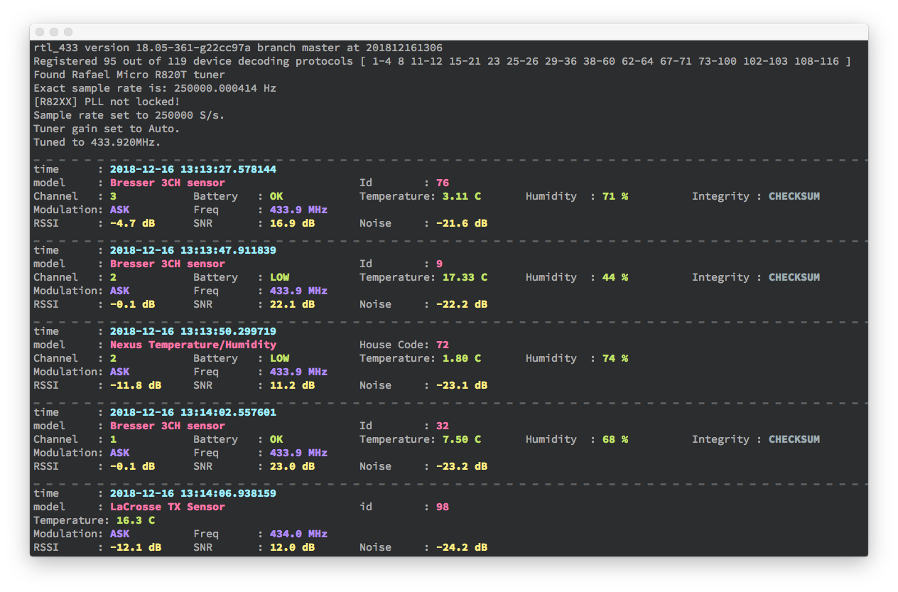 merbanan/rtl_433
Program to decode radio transmissions from devices on the ISM bands (and other frequencies)
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 0xor0ne/awesome-list
Cybersecurity oriented awesome list
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 bmax121/apatch
The patching of Android kernel and Android system
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 dosx-dev/obfus.h
Macro-header for compile-time C obfuscation (tcc, win x86/x64)
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 zardus/ctf-tools
Some setup scripts for security research tools.