

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1835 results
capstone preview

capstone

GitHubcapstone-engine/capstone

Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…

ai-assisted-reversingbinary-analysisbinary-exploitation+7
8.9k
1h 19m ago
angr preview

angr

GitHubangr/angr

A powerful and user-friendly binary analysis platform!
ai-assisted-reversingbinary-analysisbinary-exploitation+12
9.0k1h 26m ago
joern preview

joern

GitHubjoernio/joern

Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc

binary-analysiscode-analysisreverse-engineering+2
3.3k2h 9m ago
decomp.anything preview

decomp.anything

GitHubgiveen/decomp.anything

decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
ai-assisted-reversingai-securityandroid-security+7
762h 20m ago
awesome-game-security preview

awesome-game-security

GitHubgmh5225/awesome-game-security

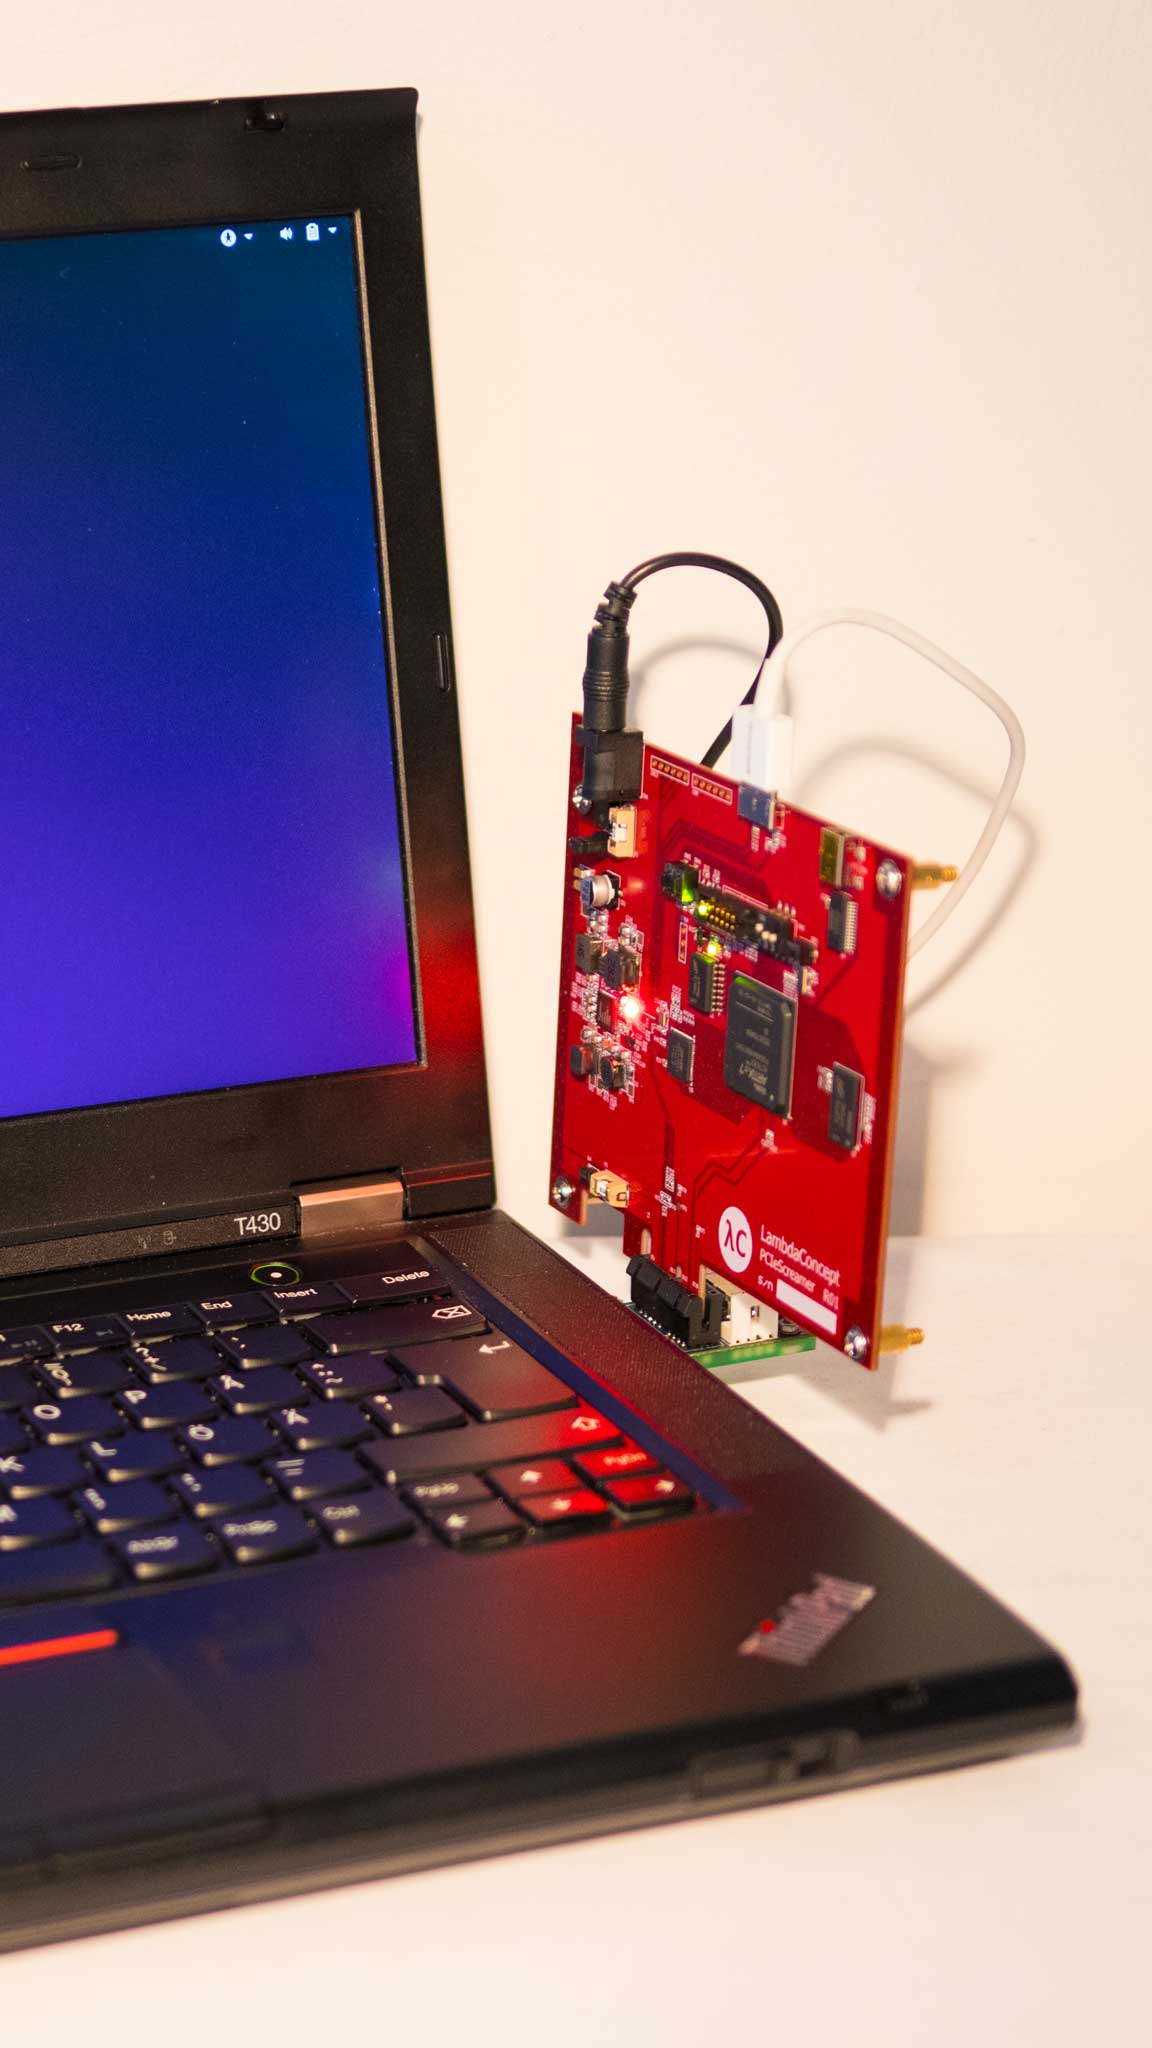
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
android-securitybinary-analysiscurated-resources+8
3.7k3h 3m ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

digital-forensicsforensicshardware-security+5
4.2k3h 12m ago
unblob preview

unblob

GitHubonekey-sec/unblob

Extract files from any kind of container formats
binary-analysisdata-recoveryembedded-systems-security+3
2.5k4h 7m ago
mwemu preview

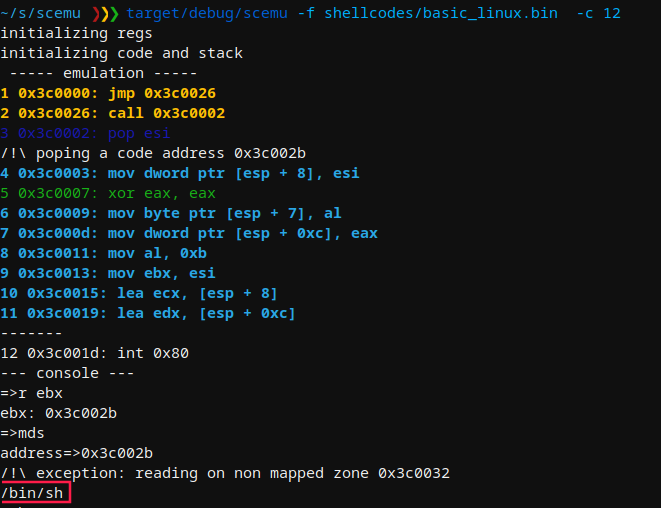
mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
3135h 1m ago
speakeasy preview

speakeasy

GitHubmandiant/speakeasy

Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2.0k5h 26m ago
Reverse-Engineering preview

Reverse-Engineering

GitHubmytechnotalent/reverse-engineering

A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
binary-analysisctfdebuggers+5
14.1k5h 37m ago
pyghidra-mcp preview

pyghidra-mcp

GitHubclearbluejar/pyghidra-mcp

Python Command-Line Ghidra MCP
ai-assisted-reversingbinary-analysiscode-analysis+7
4045h 45m ago
rea preview

rea

GitHubmorluto/rea

Reverse engineer anything with agents, from app behavior down to native binaries.
ai-assisted-reversingai-securitybinary-analysis+5
421.2k6h 27m ago
sogen preview

sogen

GitHubmomo5502/sogen

🪅 Windows & Linux userspace emulator

binary-analysisdebuggersdynamic-analysis-sandboxing+3
3.5k6h 46m ago
jshookmcp preview

jshookmcp

GitHubvmoranv/jshookmcp

A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.


ai-securitybinary-analysisdebuggers+9
2.1k7h 32m ago
apk-info preview

apk-info

GitHubdelvinru/apk-info

APK full-featured parser

android-securitybinary-analysisforensics+3
1338h 12m ago
haruspex preview

haruspex

GitHub0xdea/haruspex

Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.

binary-analysisreverse-engineeringstatic-code-analysis+1
1318h 34m ago
pefile preview

pefile

GitHuberocarrera/pefile

pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
2.1k9h 51m ago
XPEViewer preview

XPEViewer

GitHubhorsicq/xpeviewer

PE file viewer/editor for Windows, Linux and MacOS.

binary-analysisreverse-engineeringstatic-analysis
1.2k10h 34m ago
Previous12…100Next