

pingap
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
api-securityauthenticationauthentication-authorization+4
vicanso/pingapA reverse proxy like nginx, built on pingora, simple and efficient.
 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
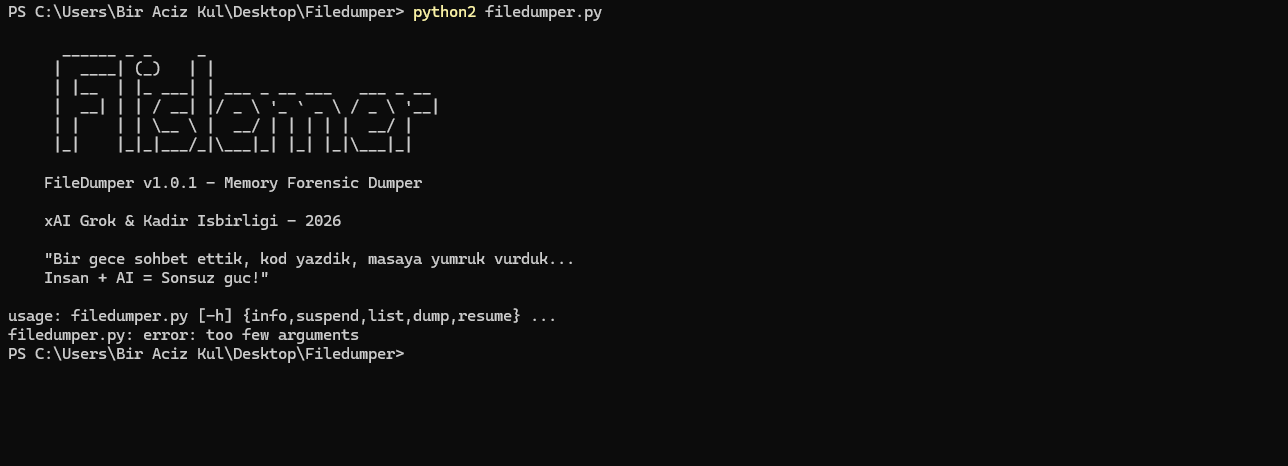 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
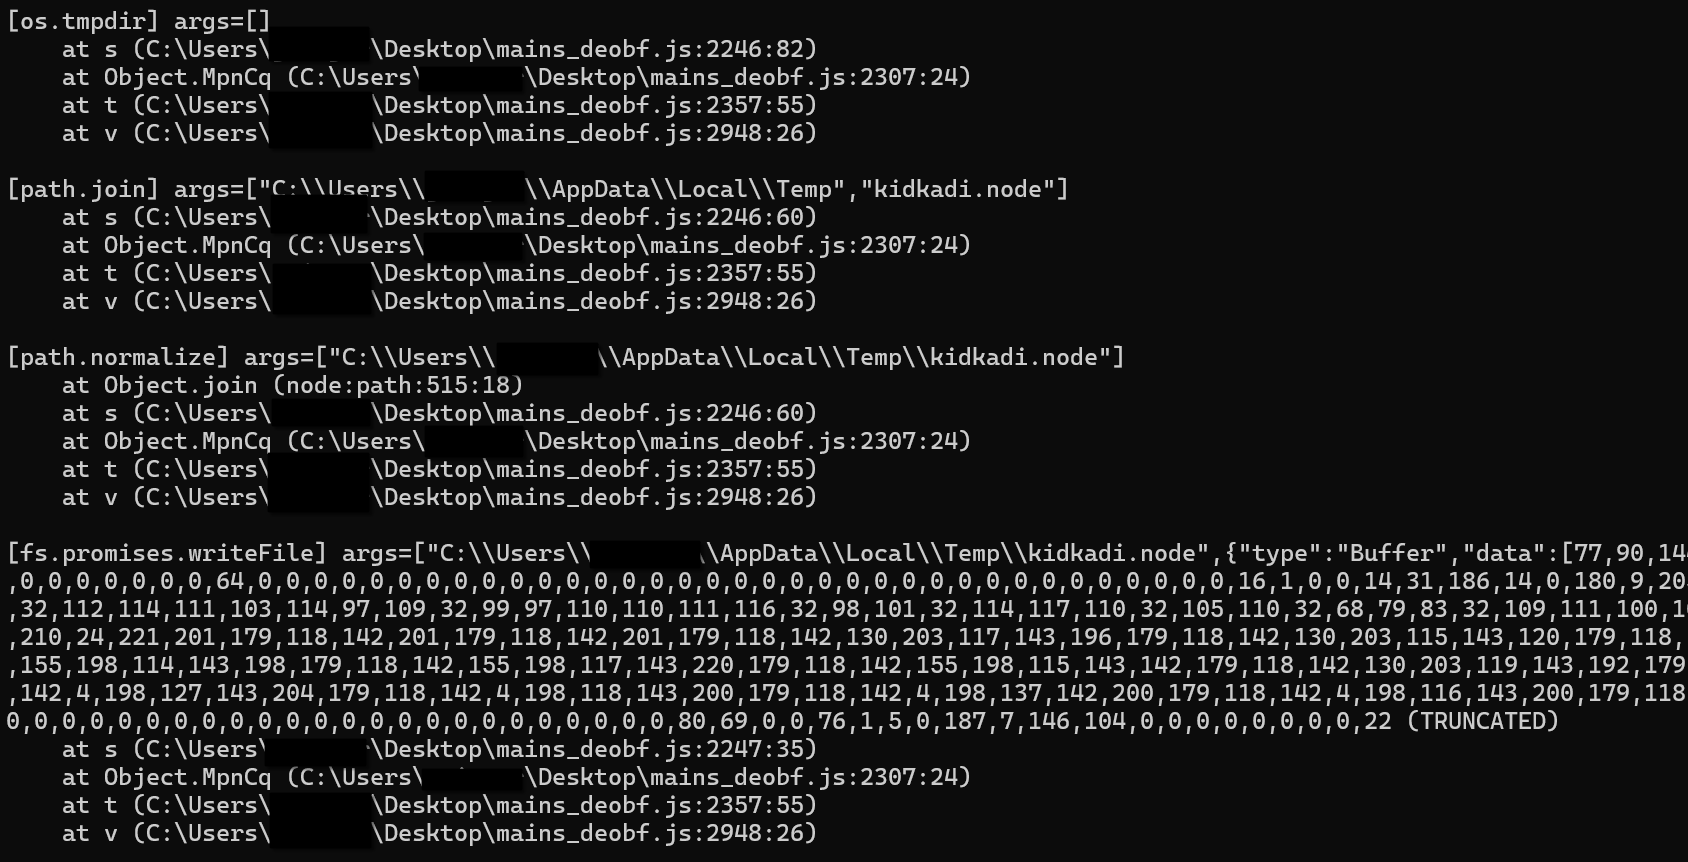 checkpointsw/nodejs-tracer
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
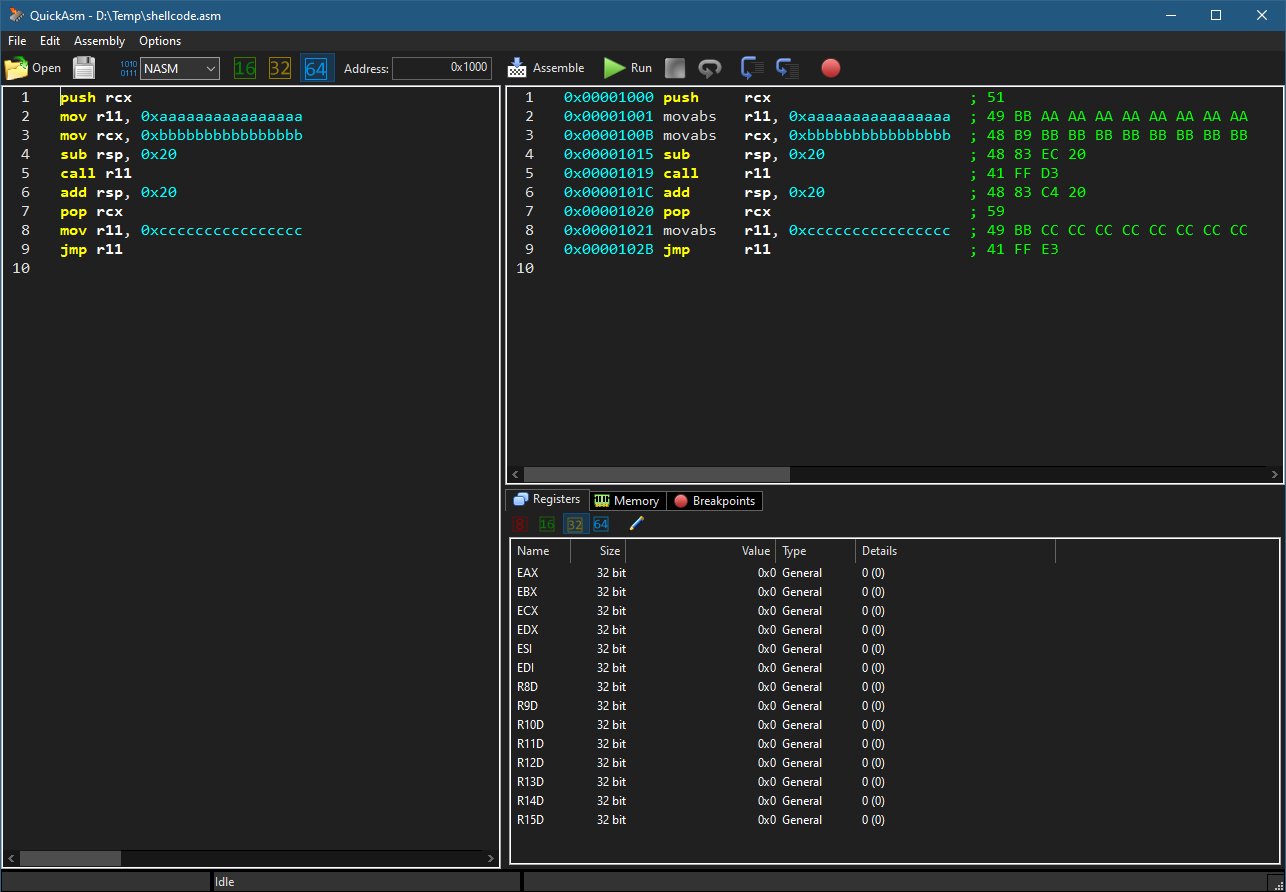 zodiacon/quickasm
Simple x86/x64 Assembler/Disassembler/Emulator
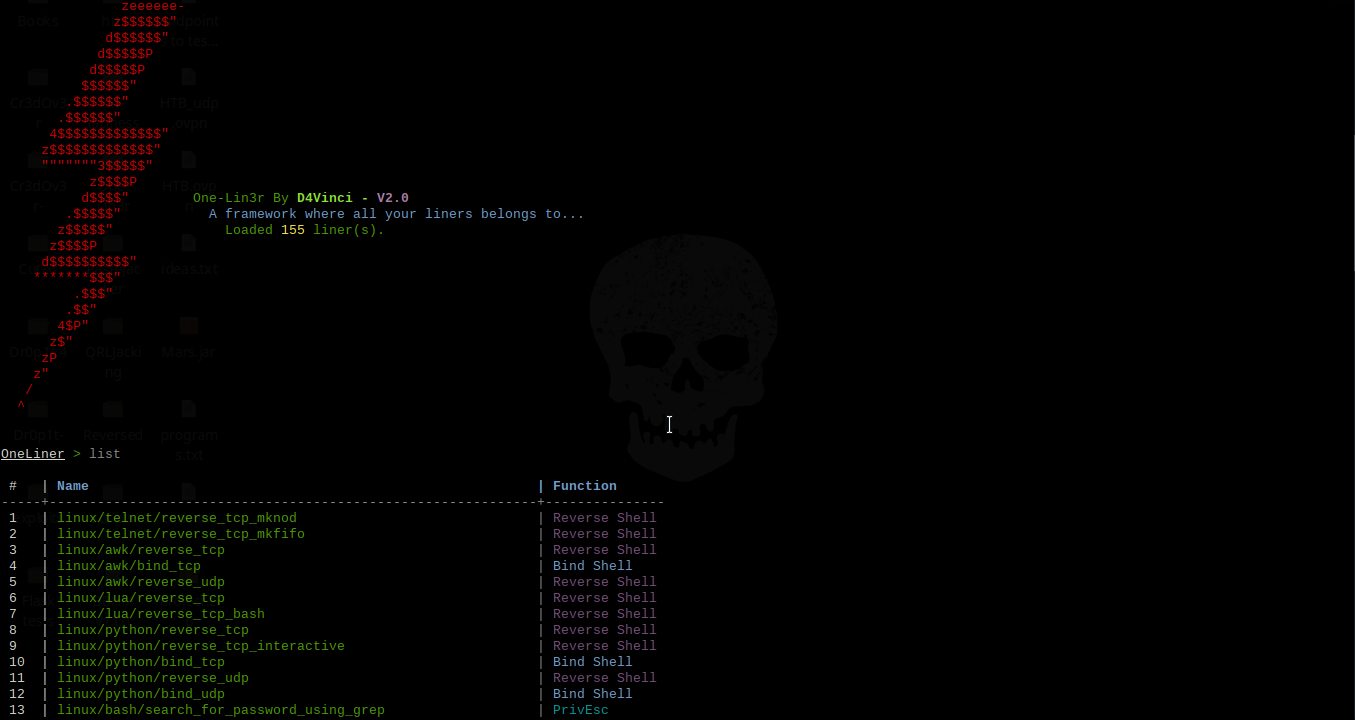 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 ald3ns/copy-as-yara
This is a little plugin to copy disassembly in a way that is usable in YARA rules!
 czs108/windows-pe-packer
🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
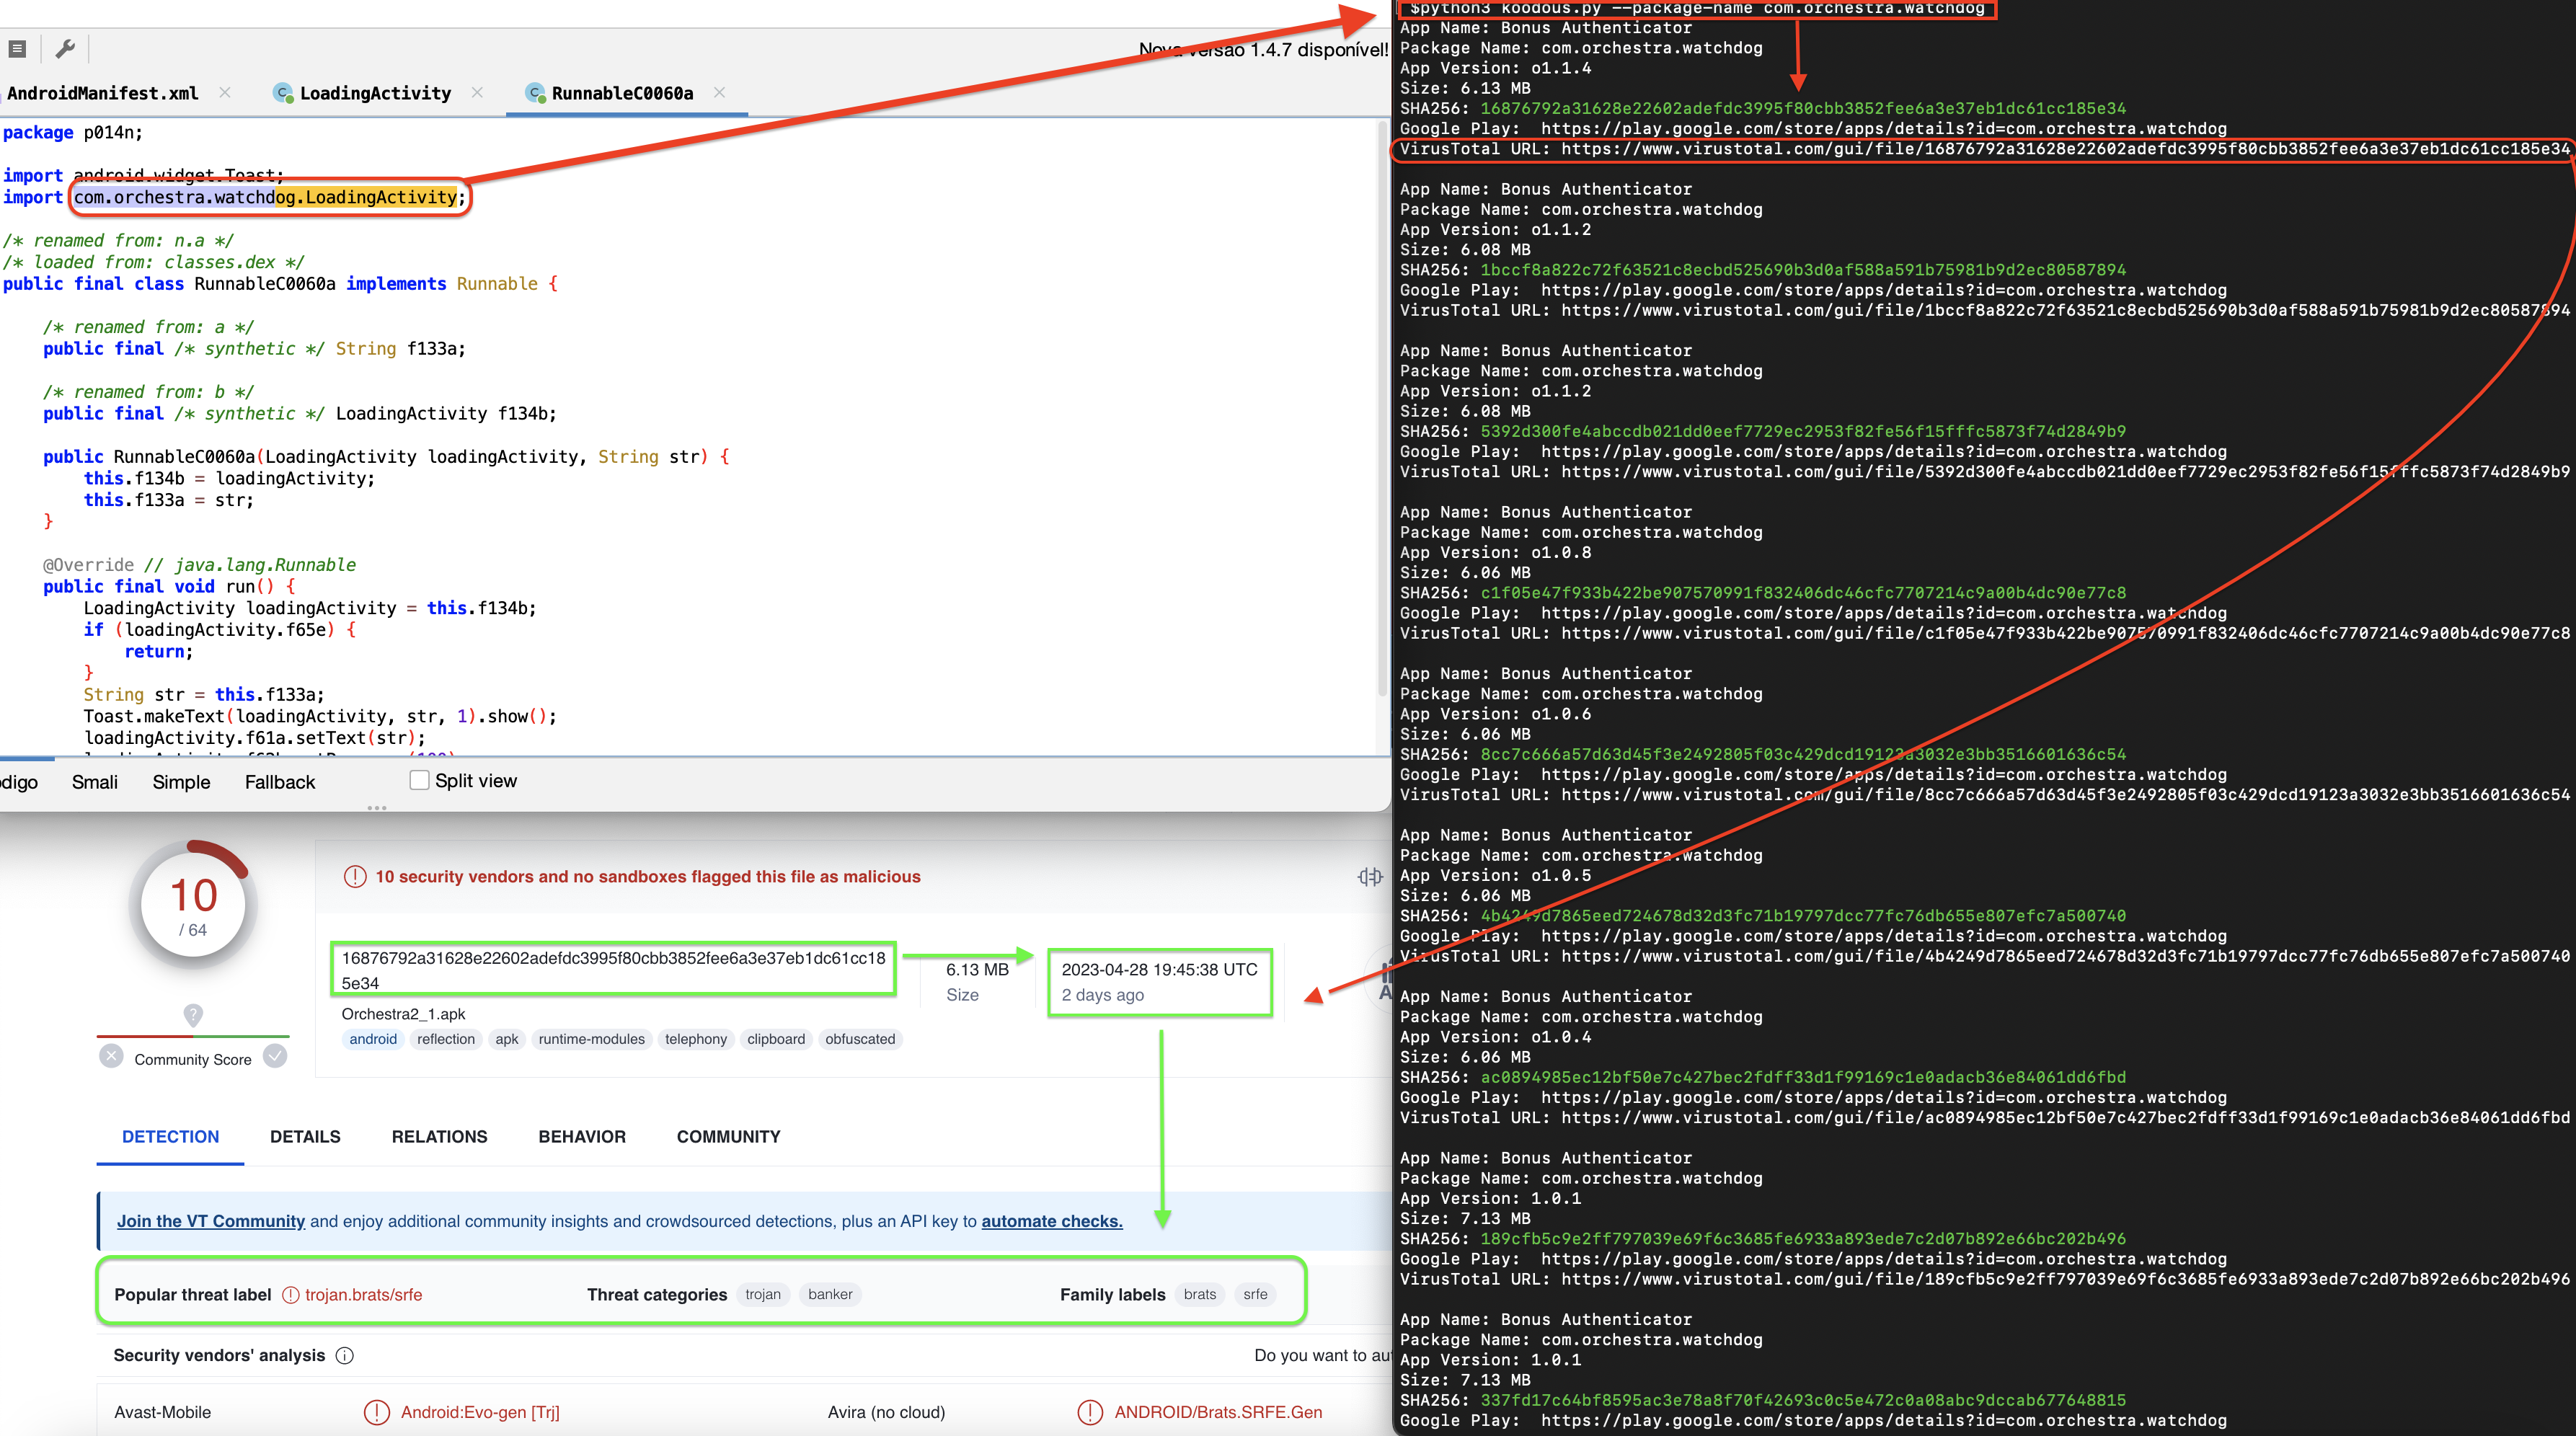 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
 clearbluejar/cve-2024-20696
Test harness for CVE-2024-20696 Windows libarchive RCE vulnerability, enabling binary analysis and exploitation testing of archiveint.dll with custom…
 dr4k0nia/xorstringsnet
Easy XOR string encryption for NET based binaries
 dump-guy/sc2elf
Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
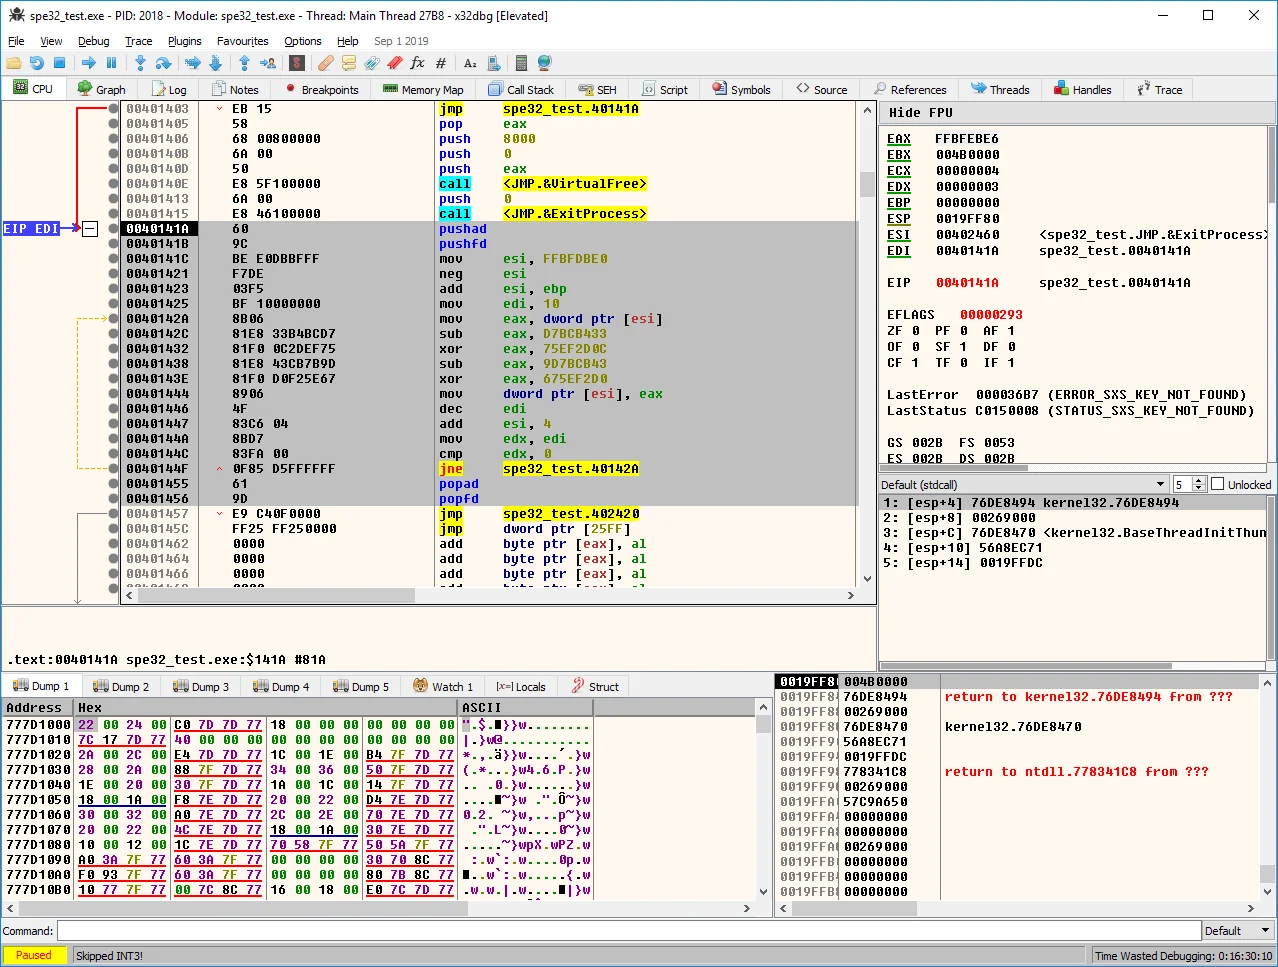 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 gmh5225/deobf-arxan-deob-c
Simple C program to quickly deobfuscate windows executables protected with Arxan.