SuperGhidra
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
ai-assisted-reversingandroid-securitybinary-analysis+8
166
yuatemycat/superghidraPython toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
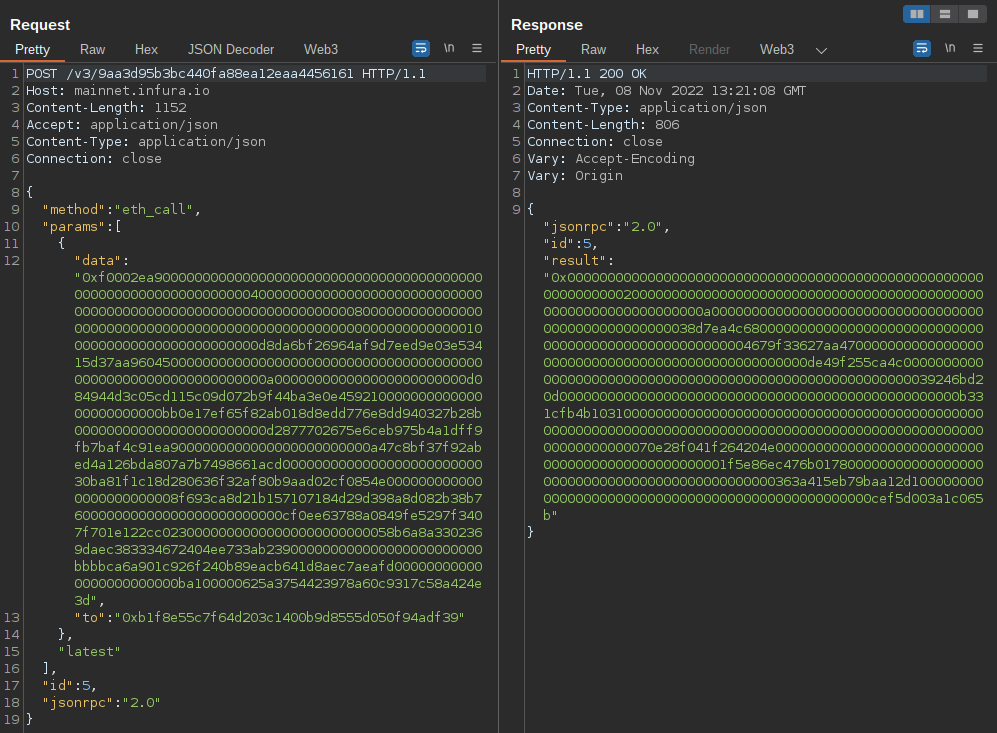 uwctcjnwlk/web3-decoder
Burp Suite extension for decoding Ethereum JSON-RPC calls and smart contract interactions, supporting multiple chains and automatic ABI retrieval.
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 saeidshirazi/awesome-android-security
A curated list of Android Security materials and resources For Pentesters and Bug Hunters
 ultrasina/androidreverse
Android reverse engineering entirely on-device. Radare2 binary analysis, 8 Java decompilers, Flutter & Unity il2cpp support.
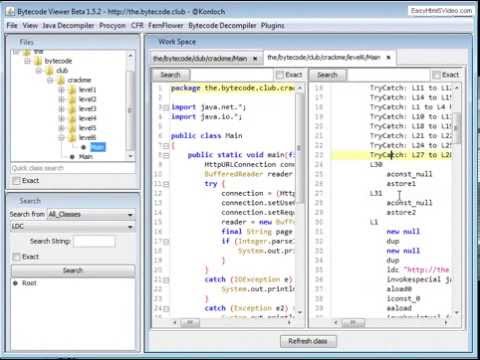 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
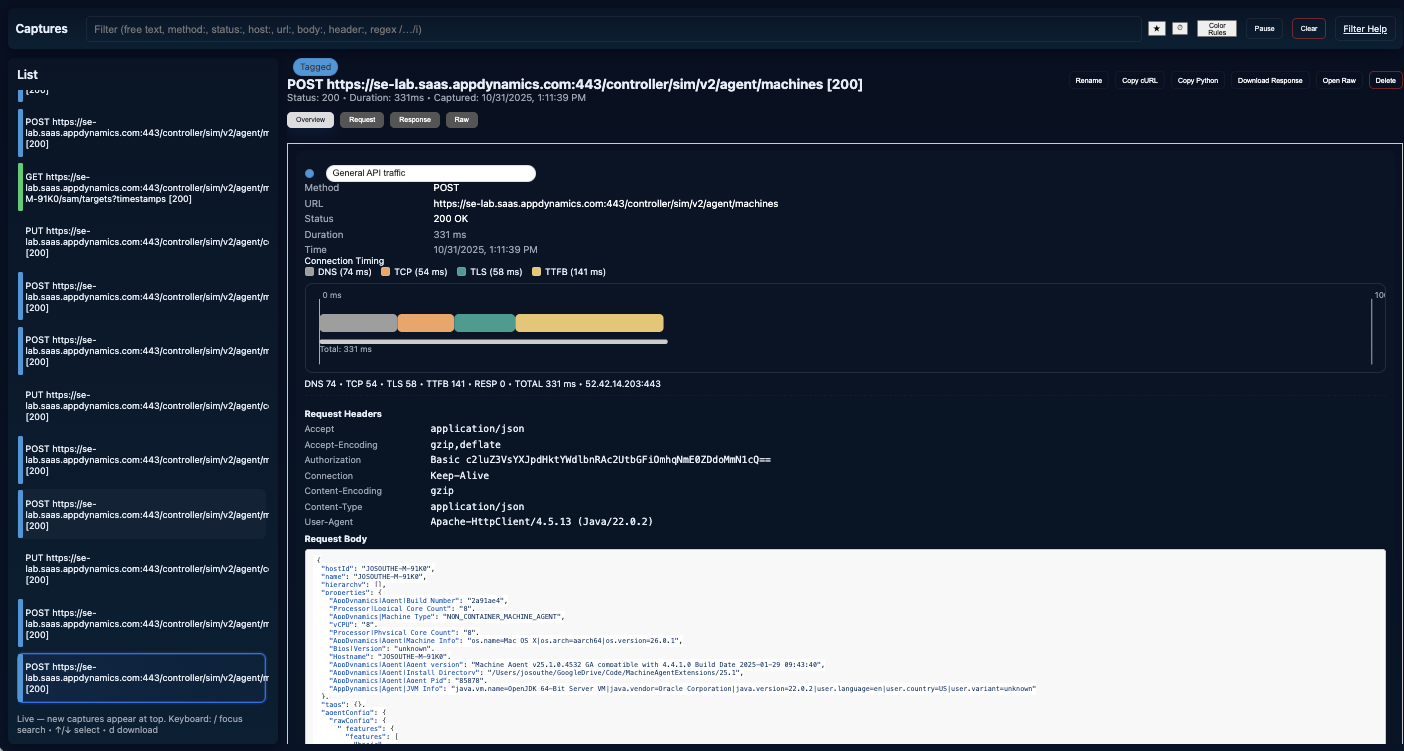 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
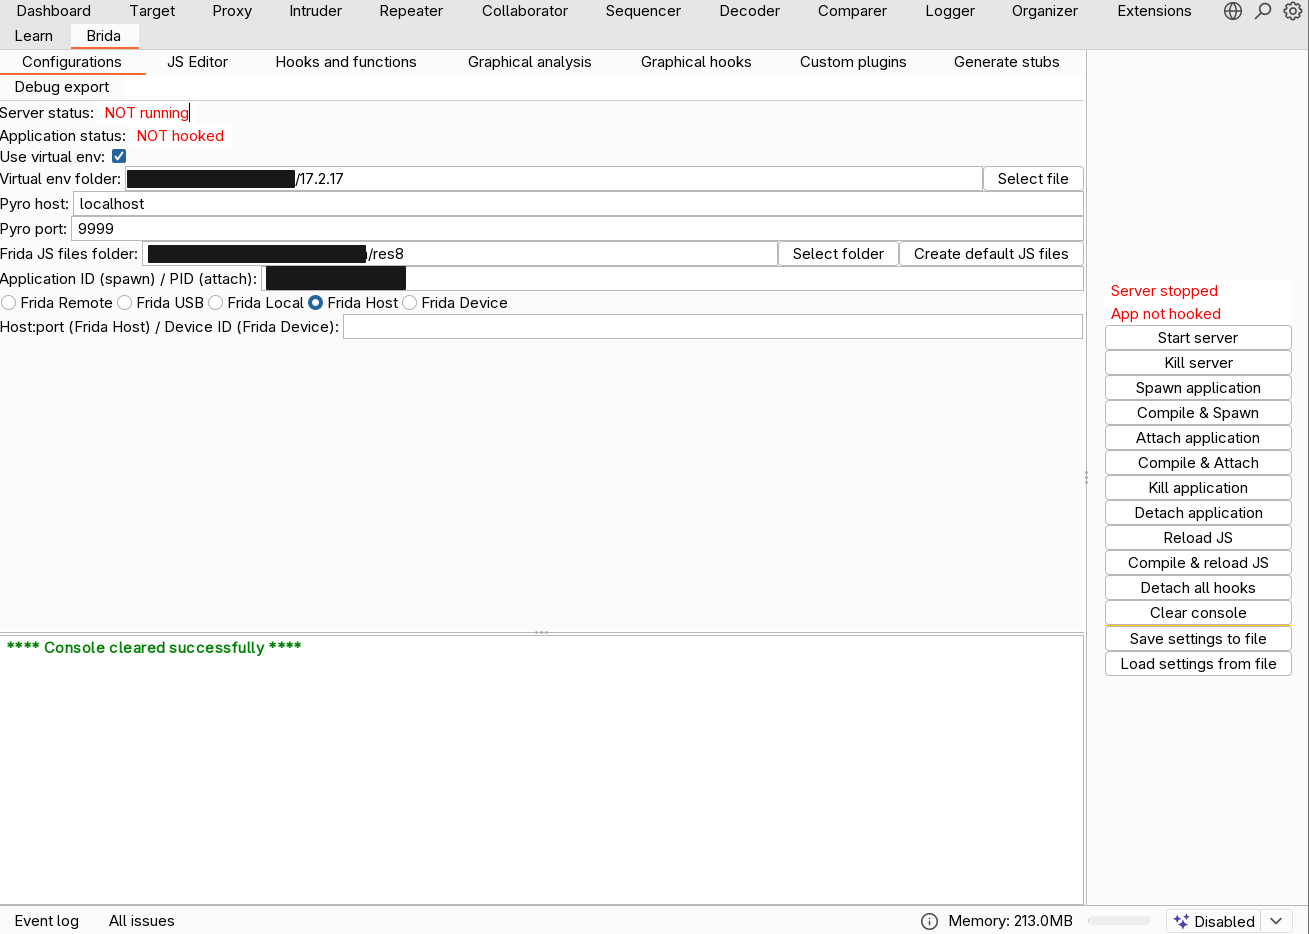 federicodotta/brida
The new bridge between Burp Suite and Frida!