

Detect-It-Easy
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.3k
horsicq/detect-it-easyProgram for determining types of files for Windows, Linux and MacOS.
 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 bb1nfosec/information-security-tasks
Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…
 vahpem/rust-deobf
Recover what obfuscation hides in Rust binaries (strings, crates, library functions, flattened control flow) via static analysis + Unicorn emulation,…
 fareedfauzi/mantis
Multi-Source Analysis & Threat Intelligence Search
 suffixing/apkscope
Android reverse engineering for humans and AI agents: typed Java in milliseconds, xrefs, API and secret recon, APK diff, re-signing, a native viewer…
 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 ph4ntom-rev/ph4ntom-vitrum
Autonomous in-vitro static malware dissection & Global CTI/Dropper Hunter (v2.3) theoretical architecture [Anti-Evasion / TLP:AMBER]
 frida/frida
Main repo for hosting release binaries
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 anasfik/flutterguard
Offline on-device Android APK auditor for Flutter apps: parses manifests, DEX and libapp.so to surface permissions, SDKs, endpoints, secrets and…
 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
 cosmic-zip/witchcraft
WITCHCRAFT is a cyberdeck toolkit built for runners who dive deep into the mesh. It’s your all-in-one rig for data-ghosting, ICE-breaking, and…
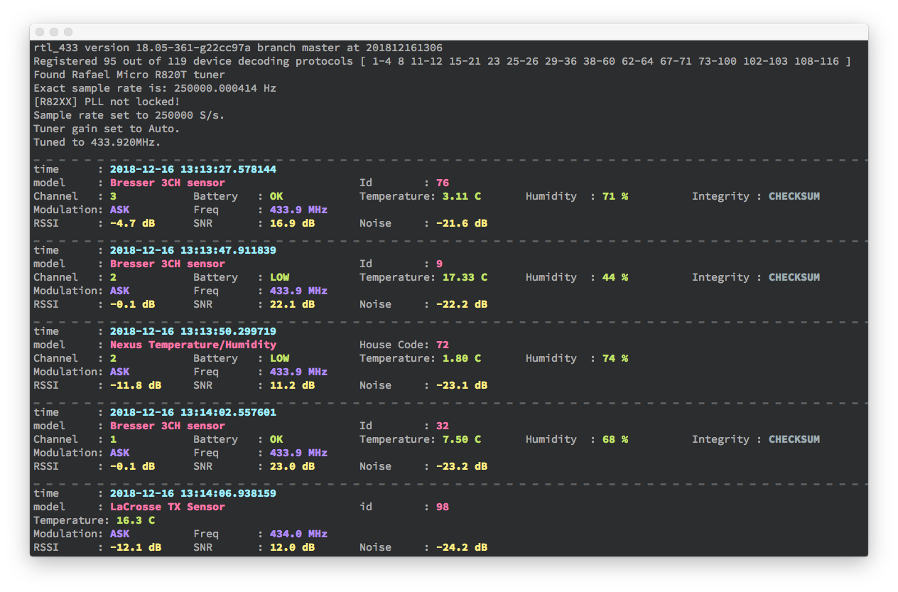 merbanan/rtl_433
Program to decode radio transmissions from devices on the ISM bands (and other frequencies)
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 nmatt0/moria
IoT firmware identification and extraction