
mtkclient
 bkerler/mtkclient
Mediatek Flash and Repair Utility
android-securitydata-recoveryembedded-systems-security+5
bkerler/mtkclientMediatek Flash and Repair Utility
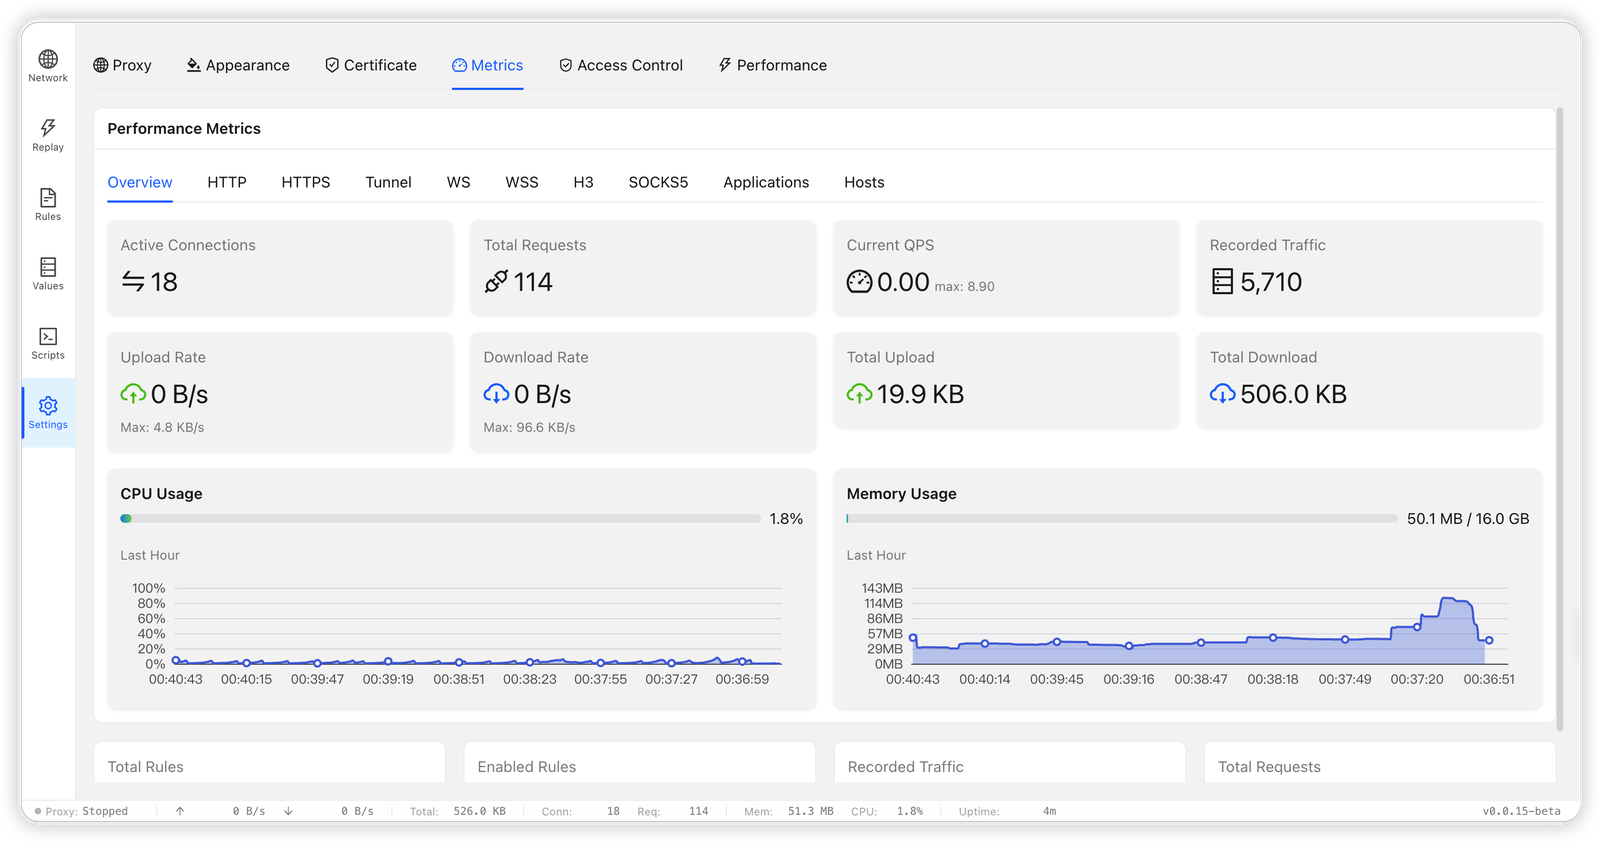 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 onekey-sec/unblob
Extract files from any kind of container formats
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
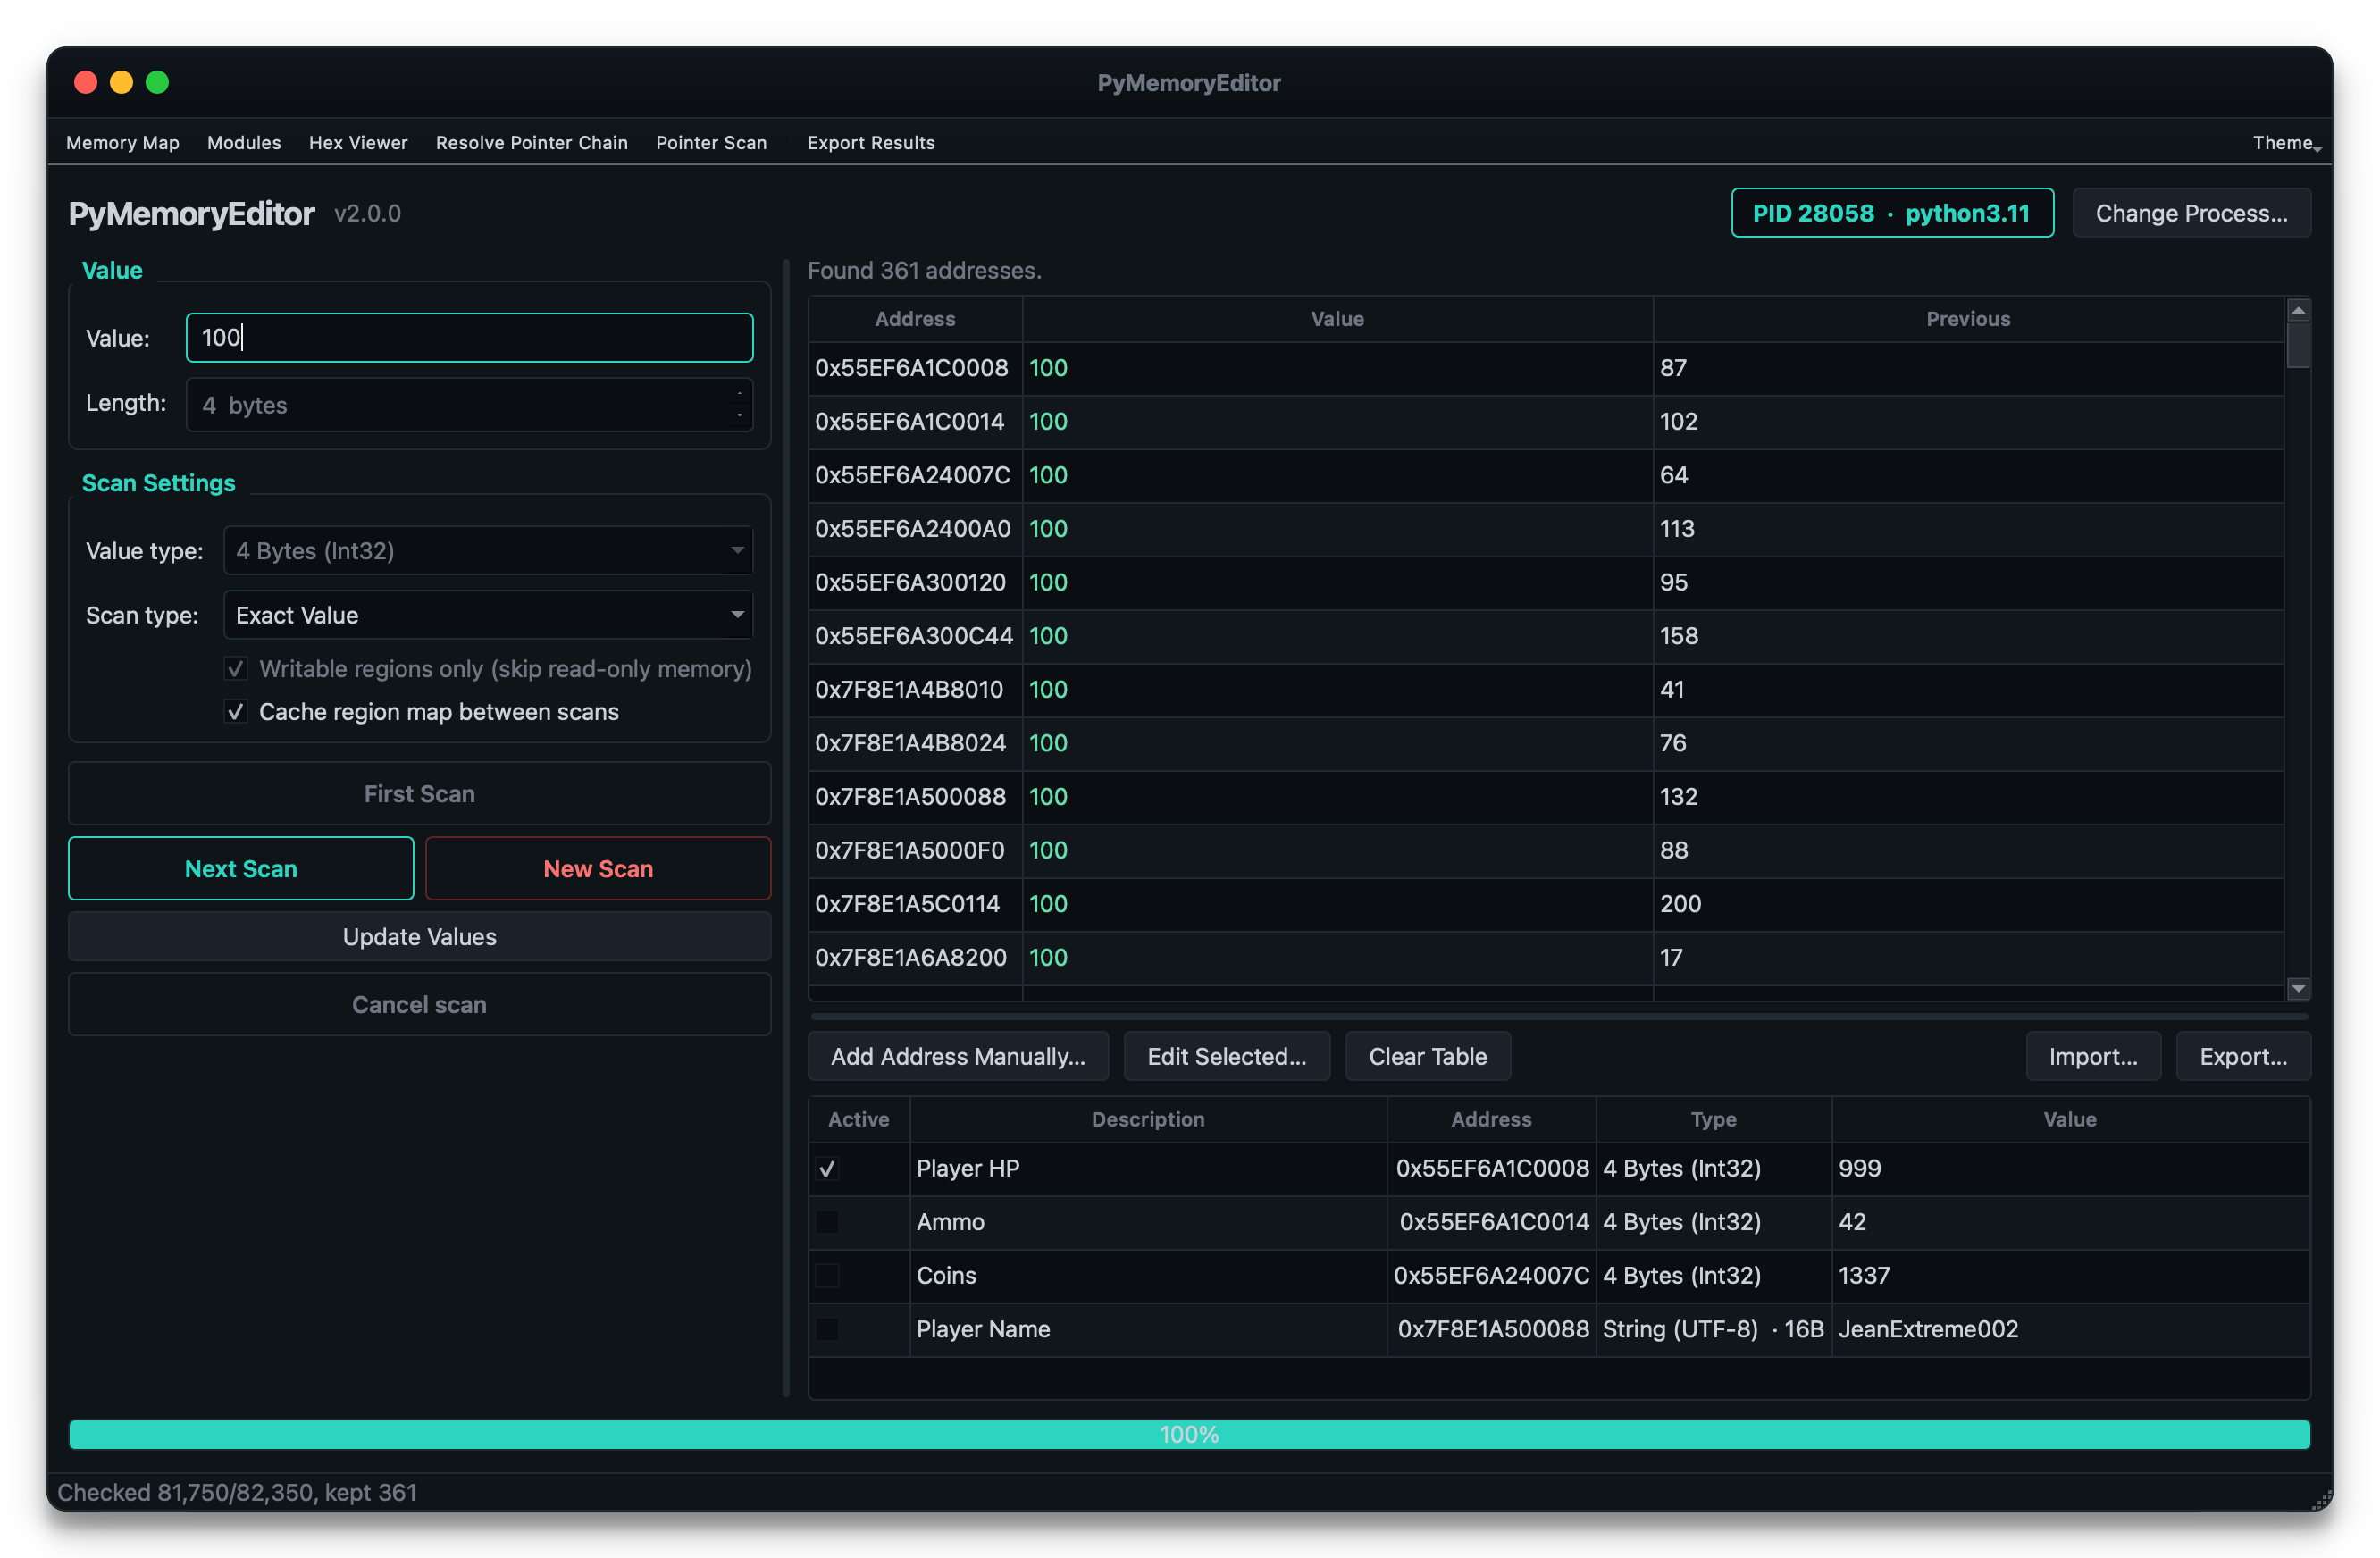 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 dosx-dev/obfus.h
Macro-header for compile-time C polymorphic obfuscation (tcc, win x86/x64)
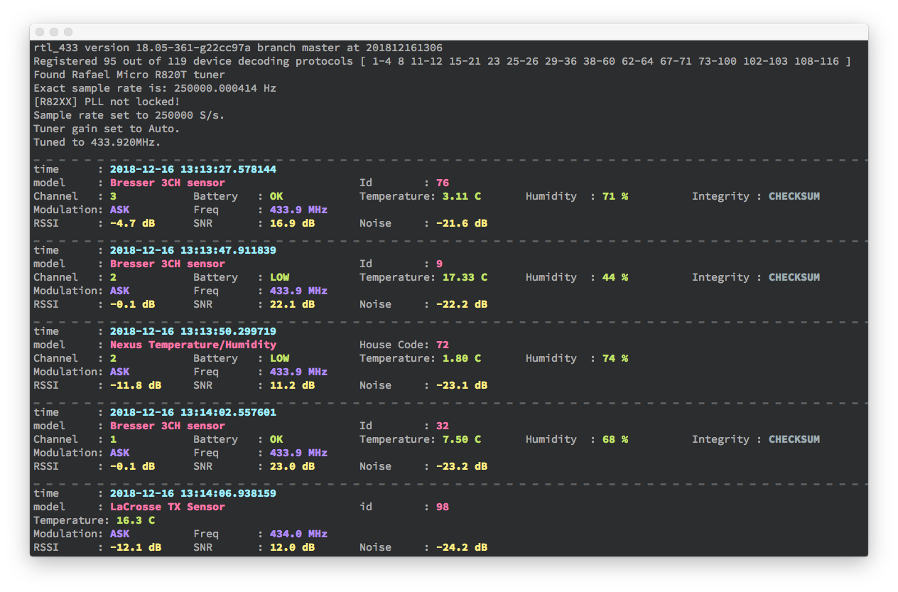 merbanan/rtl_433
Program to decode radio transmissions from devices on the ISM bands (and other frequencies)
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…