
RPC-Triage
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
binary-analysisreconnaissancered-teaming+3
14
talha-nazeef-ahmed/rpc-triageA zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
 leochen-coremind/spd_flasher
CVE-2022-38694 Hardened Exploit - RP2350 USB Host Auto Flasher for Unisoc devices
 warpedatom/offsetinspect
PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
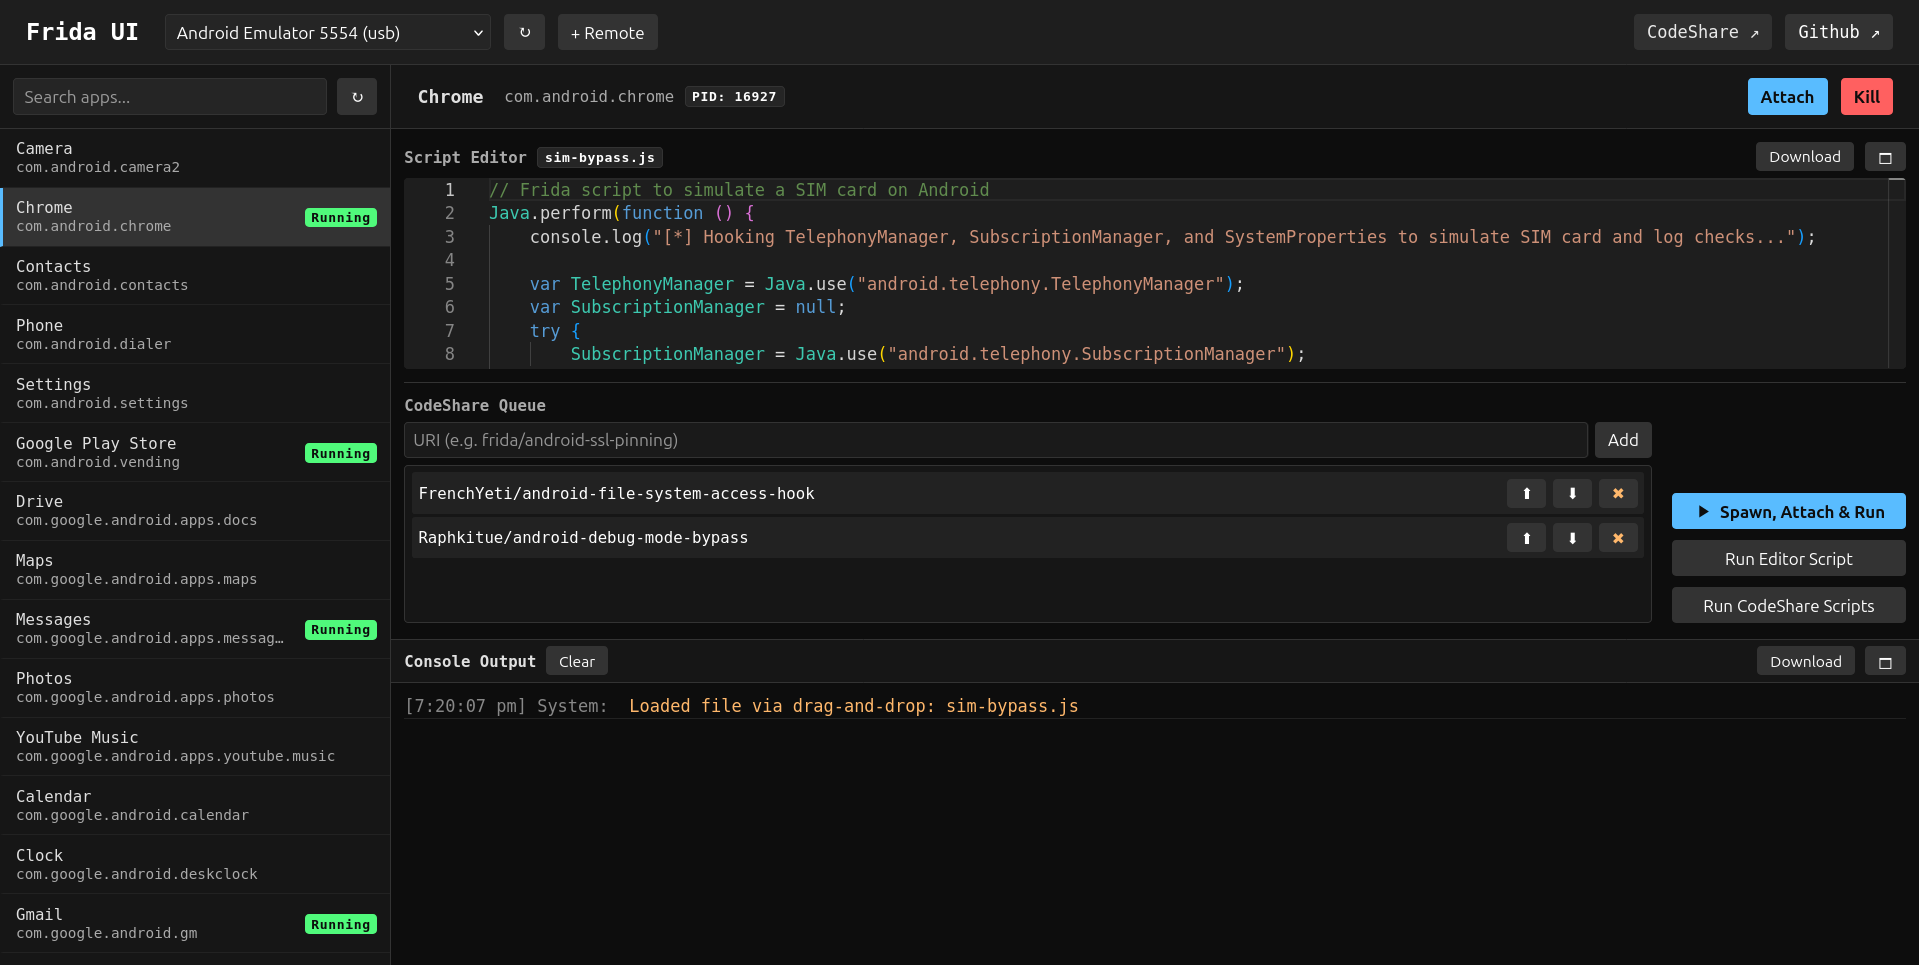 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
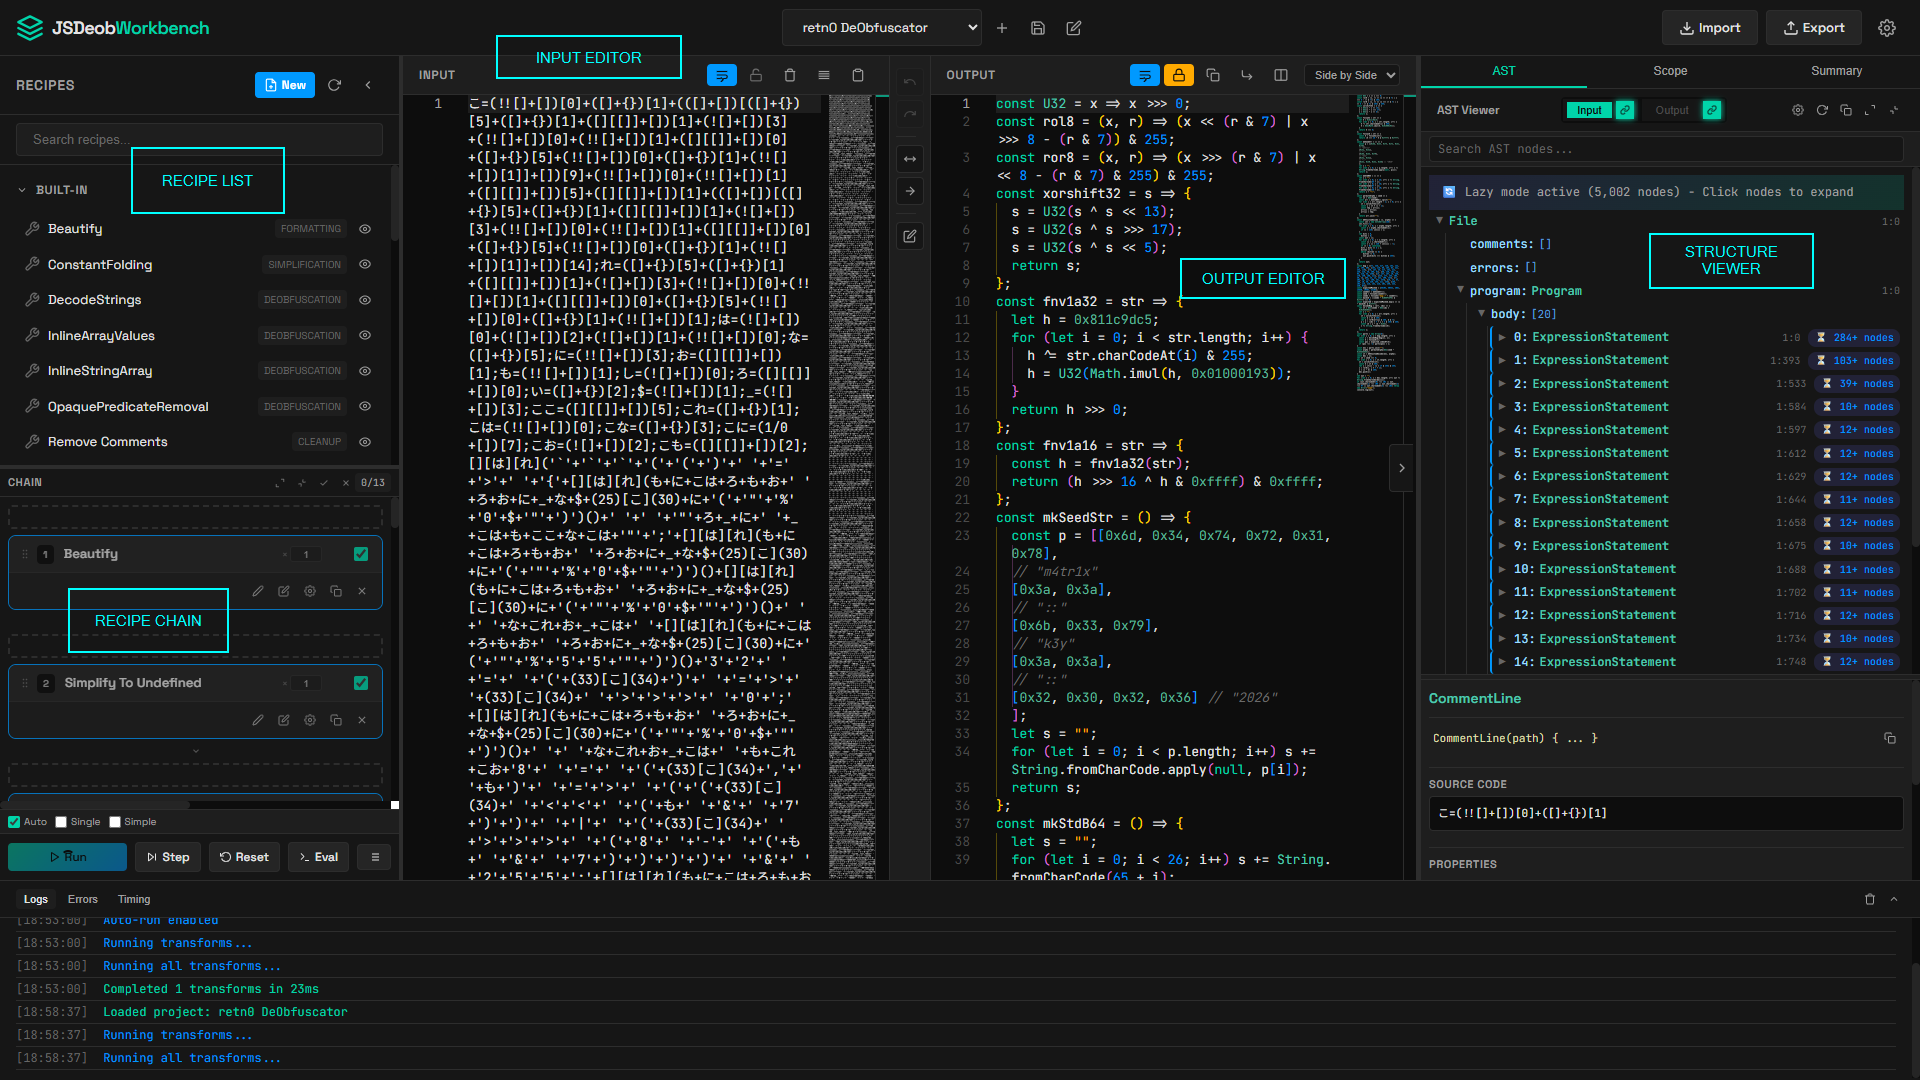 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
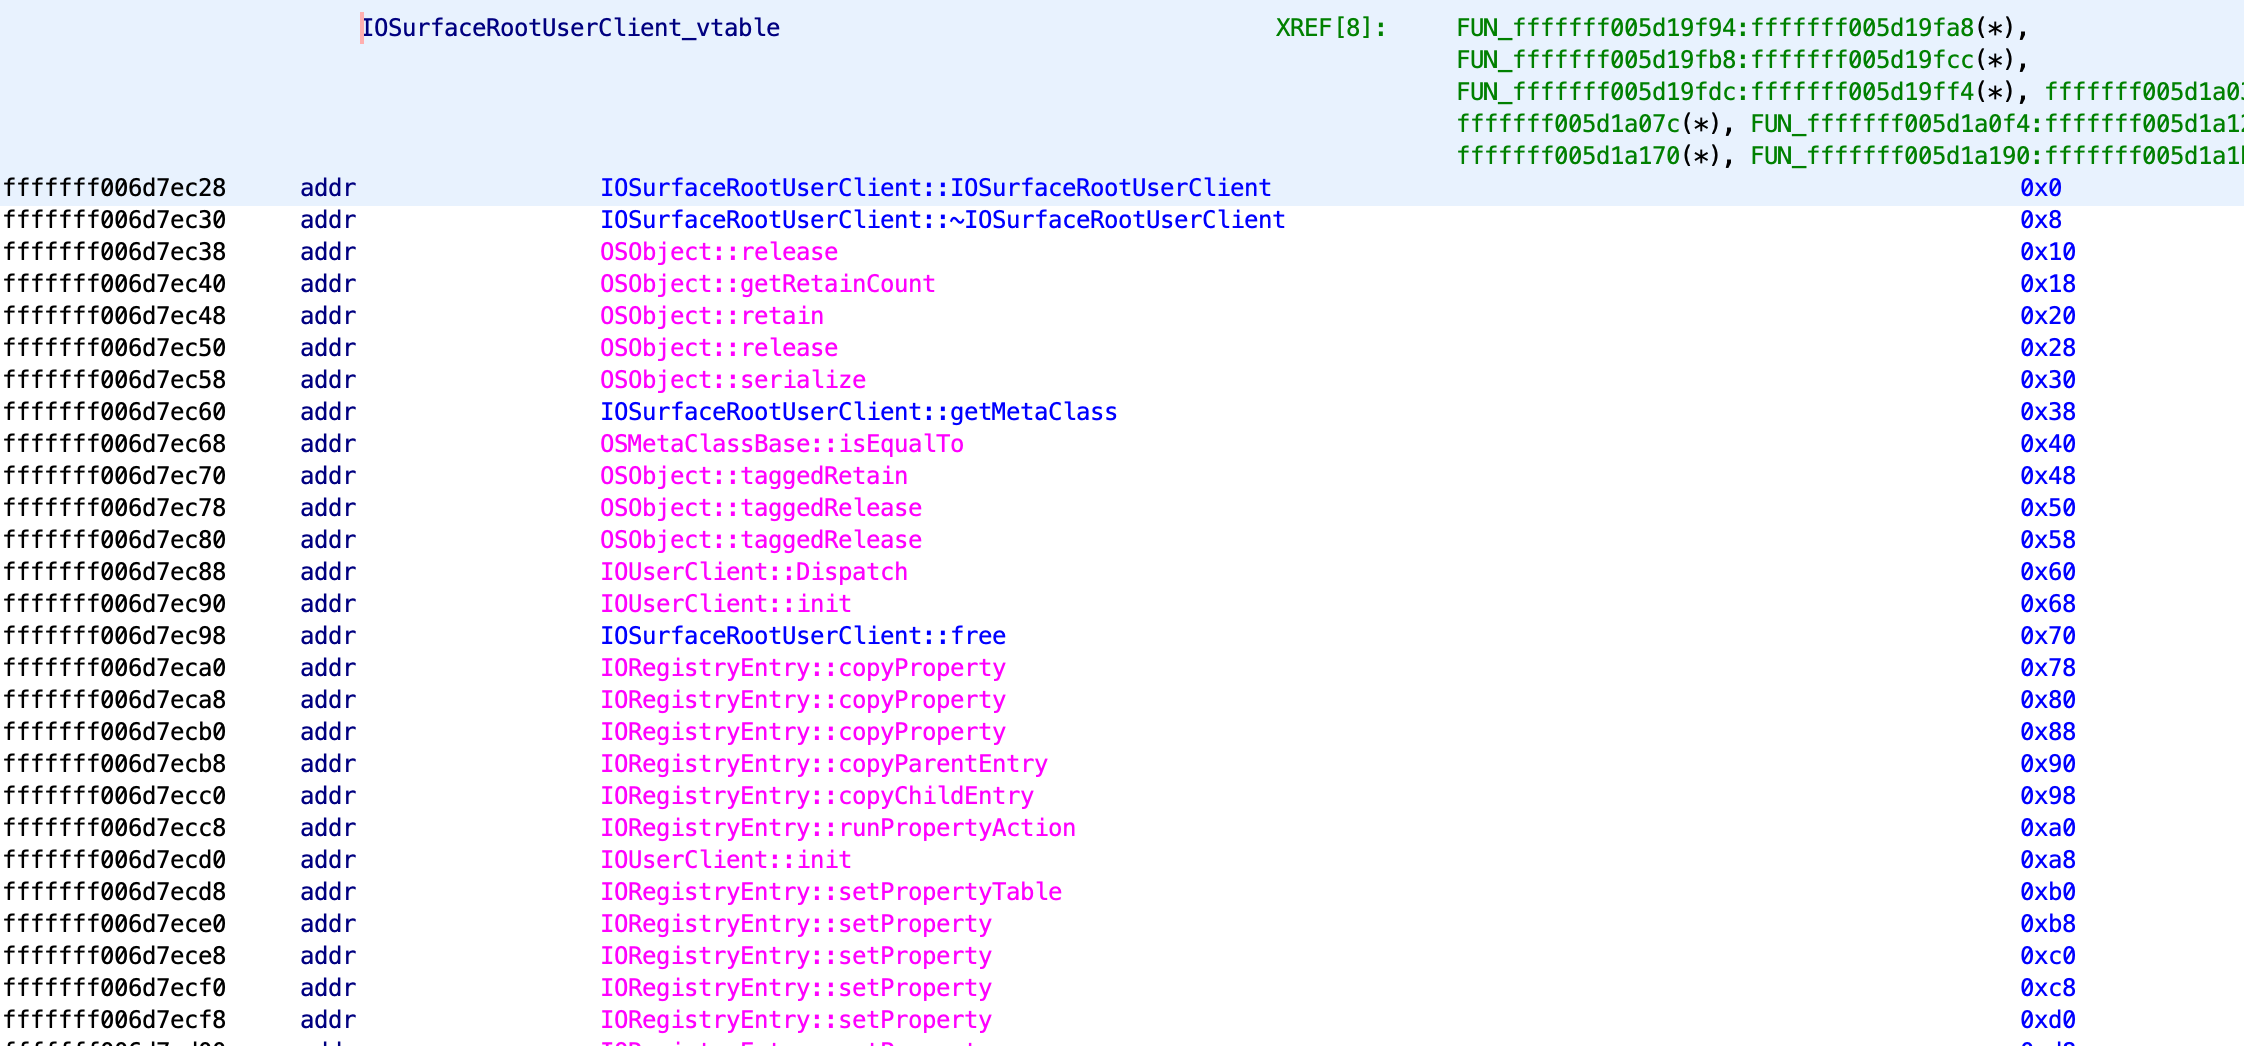 0x36/ghidra_kernelcache
a Ghidra framework for iOS kernelcache reverse engineering
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…