
CVE-2026-88773
 scyrix-llc/cve-2026-88773
Technical analysis of a NetScaler nsppe HTTP/1.1 chunk-size integer-wrap request smuggling flaw, with disassembly, wire-level PoC flows, and firmware…
binary-analysisexploitationfirmware-analysis+5
1
scyrix-llc/cve-2026-88773Technical analysis of a NetScaler nsppe HTTP/1.1 chunk-size integer-wrap request smuggling flaw, with disassembly, wire-level PoC flows, and firmware…
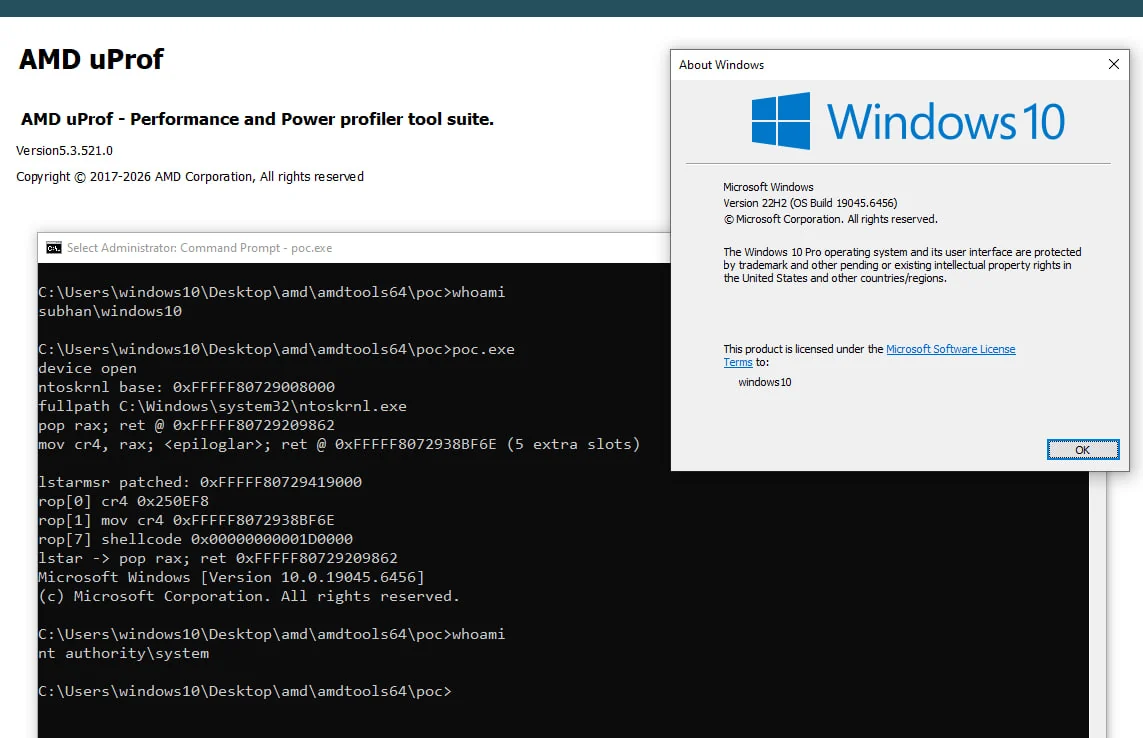 mein-0/mercilessamd
Proof-of-concept exploiting AMD AmdTools64.sys MSR read/write IOCTLs to overwrite IA32_LSTAR, bypass SMEP and escalate from administrator to SYSTEM…
 cylancevulnresearch/reflectivedllrefresher
Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
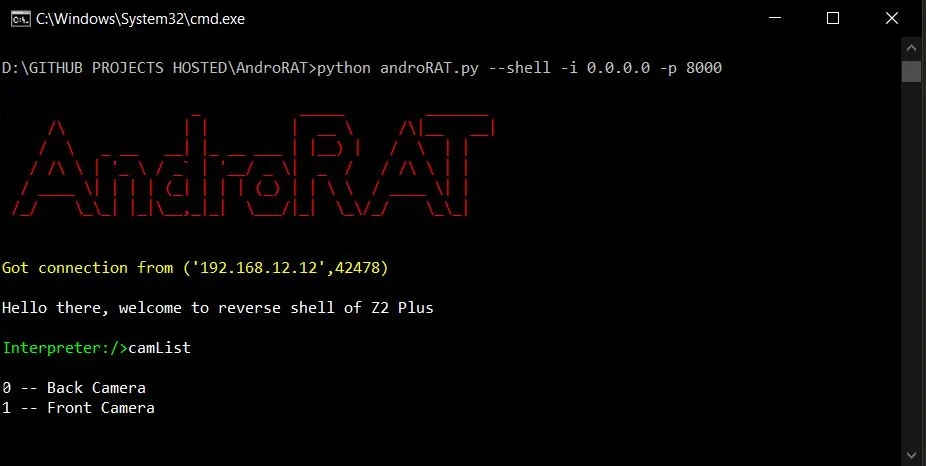 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 ivancabrera02/whfb-pincapture
Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 backdoorskid/win-def-clickfix
A scanner that estimates whether Microsoft Defender is likely to flag a command as ClickFix.
 cookiengineer/actual-php2shell
:robot: NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
 eset/malware-research
Code written as part of our various malware investigations
 gmh5225/no-access-protection-x86
It encrypts the text section and set the protection to NO_ACCESS.
 mandiant/goresym
Parses Go binaries to recover symbols, function metadata, types, file paths, and embedded strings, including stripped or UPX-packed samples, with IDA…
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 c8dhjp4tyv-bit/jbl-wave-buds2-firmware-research
Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…
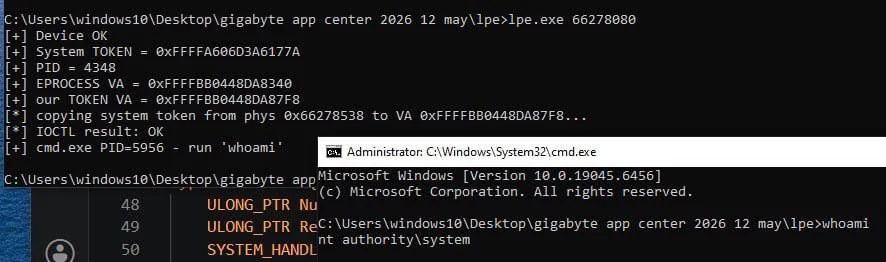 mein-0/knockgiga
Proof-of-concept local privilege escalation exploiting Gigabyte gdrv3.sys IOCTLs to write the SYSTEM token into a user process via an unchecked…
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 luftwaffe66/gobfuscator
Obfuscates Go source code via AES-256 string encryption with runtime decryption, identifier renaming, and comment removal to hinder reverse…
 icicle-emu/icicle-python
Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…