ghostlock-app
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
android-securitybinary-analysisexploitation+4
1.4k3 days ago
yukonga/ghostlock-appGhostLock One-Tap Execution App (CVE-2026-43499)
 knight0x07/bibi-windows-wiper-analysis
Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
 synacktiv/pridelocker-analysis
This repository contains a IDA Python script to recover PrideLocker ESX encryptor strings and a YARA rule
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
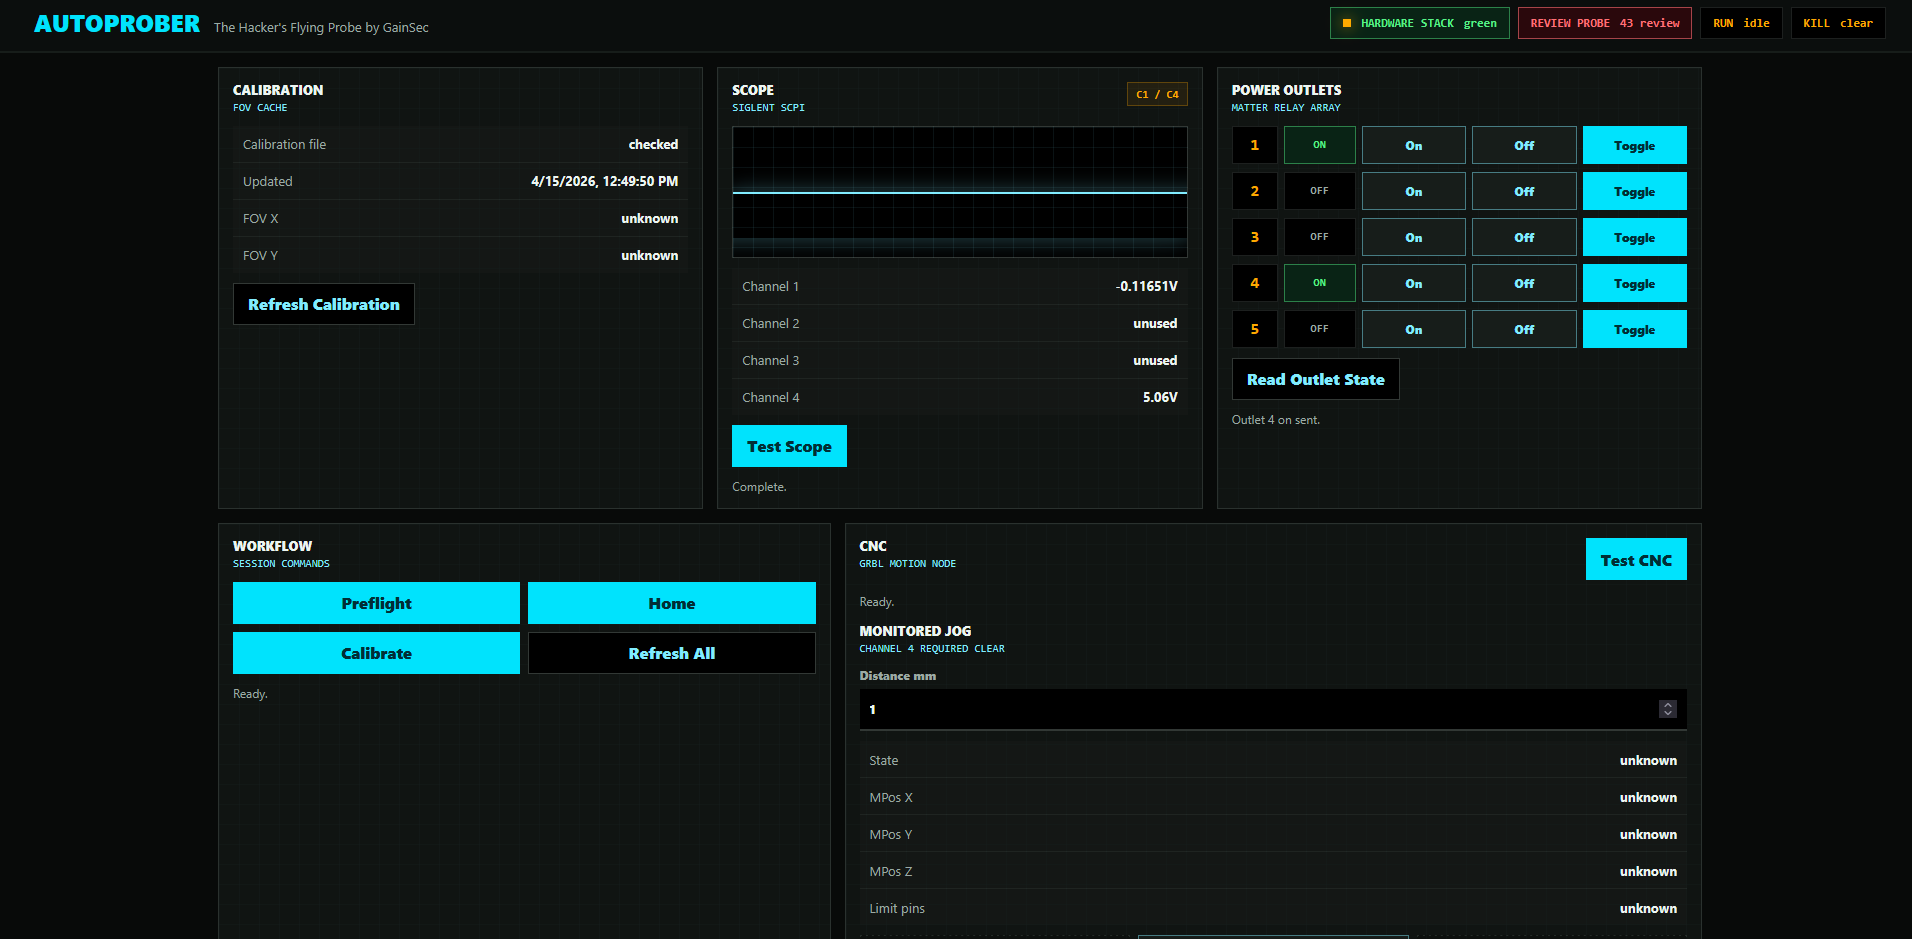 gainsec/autoprober
Hardware hacker’s flying probe automation stack for agent-driven target discovery, microscope mapping, safety-monitored CNC motion, probe review,…
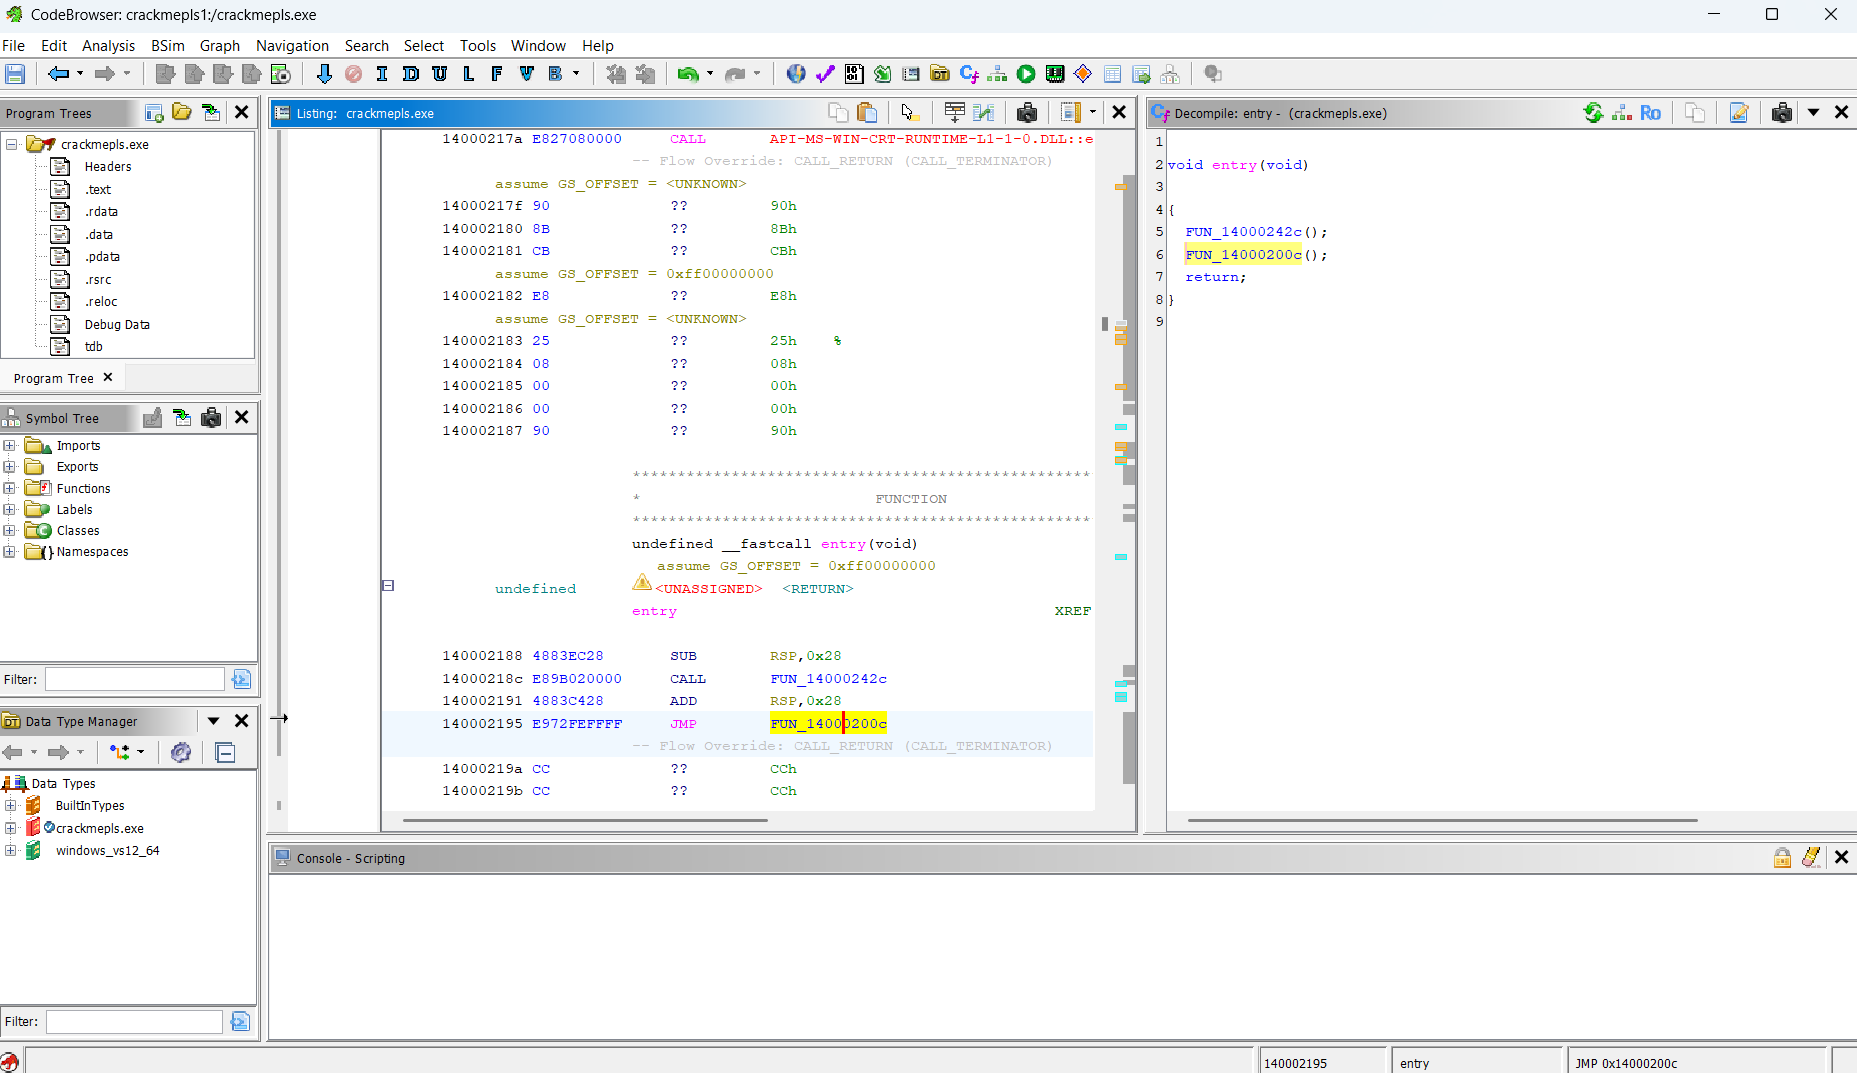 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
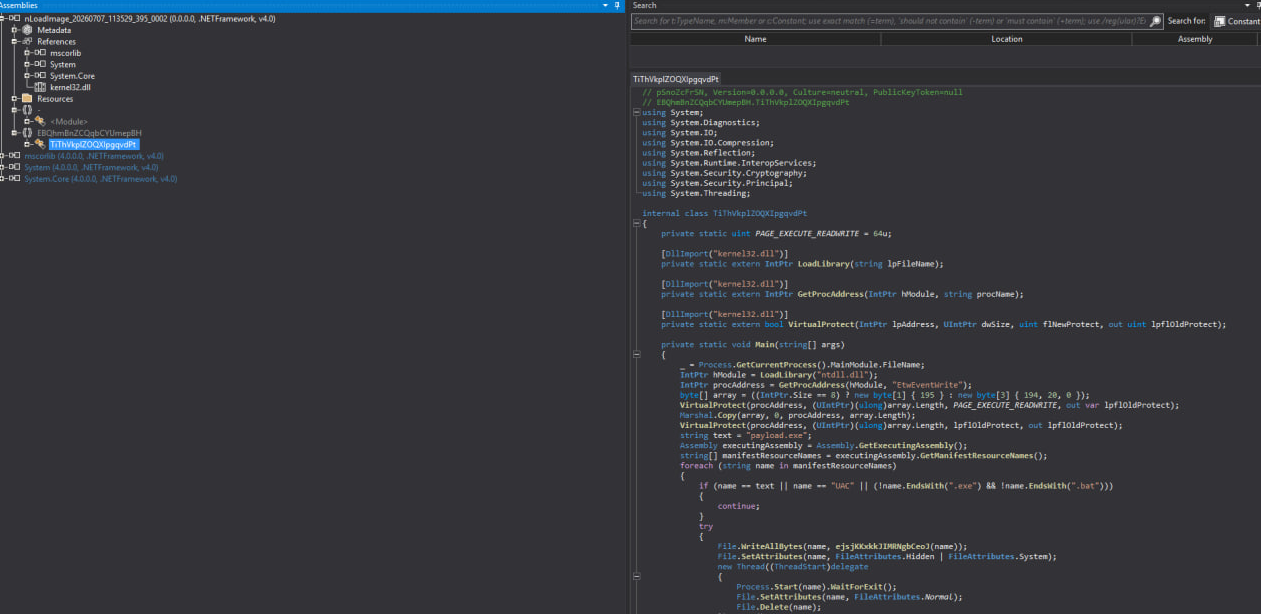 zypherion-technologies/nemesis
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 oalabs/hashdb-ida
HashDB API hash lookup plugin for IDA Pro