

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
27 results
blackarch preview

blackarch

GitHubblackarch/blackarch

An ArchLinux based distribution for penetration testers and security researchers.

curated-resourceseducationexploit-frameworks+8
3.5k5h 11m ago
Amadey-Loader-Multi-Stage-Malware-with-Keylogging-Clipboard-Hijack-Privilege-Escalation-Analysis preview

Amadey-Loader-Multi-Stage-Malware-with-Keylogging-Clipboard-Hijack-Privilege-Escalation-Analysis

GitHubkaandemir993/amadey-loader-multi-stage-malware-with-keylogging-clipboard-hijack-privilege-escalation-analysis

Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…
binary-analysisdebuggersdynamic-analysis-sandboxing+5
411 days ago
OffensiveRust preview

OffensiveRust

GitHubtrickster0/offensiverust

Rust Weaponization for Red Team Engagements.
binary-exploitationcommand-and-controleducation+9
3.0k3 years ago
accfly preview

accfly

GitHubtezeb/accfly

Disclosure of Accfly camera vulnerabilities: CVE-2020-25782, CVE-2020-25783, CVE-2020-25784, CVE-2020-25785.
binary-exploitationembedded-systems-securityexploitation+6
35 years ago
DracOS preview

DracOS

GitHubscreetsec/dracos

Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
educationexploitationforensics+8
589 years ago
Brosec preview

Brosec

GitHubgabemarshall/brosec

Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.
encryption-decryption-toolsexploitationinformation-gathering+7
3495 years ago
GWTMap preview

GWTMap

GitHubreverseclabs/gwtmap

Maps attack surface of GWT applications by extracting obfuscated RPC endpoints and generating serialized request payloads for security testing.
information-gatheringpenetration-testingreverse-engineering+2
1161 year ago
pyrebox preview
Archived

pyrebox

GitHubcisco-talos/pyrebox

Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
binary-analysisdebuggersdigital-forensics+5
1.7k2 years ago
Linksys-WRT54GL-Exploitation preview

Linksys-WRT54GL-Exploitation

GitHubumbertodellamonica/linksys-wrt54gl-exploitation

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
binary-analysisdebuggerseducation+9
25 months ago
GoDefender preview
Archived

GoDefender

GitHubkiexitdispatcher/godefender

Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
anti-botbinary-analysisdefensive-tools+3
85810 months ago
mal_unpack preview

mal_unpack

GitHubhasherezade/mal_unpack

Dynamic unpacker based on PE-sieve
binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
8446 months ago
matrix-rs preview
Archived

matrix-rs

GitHubmemn0ps/matrix-rs

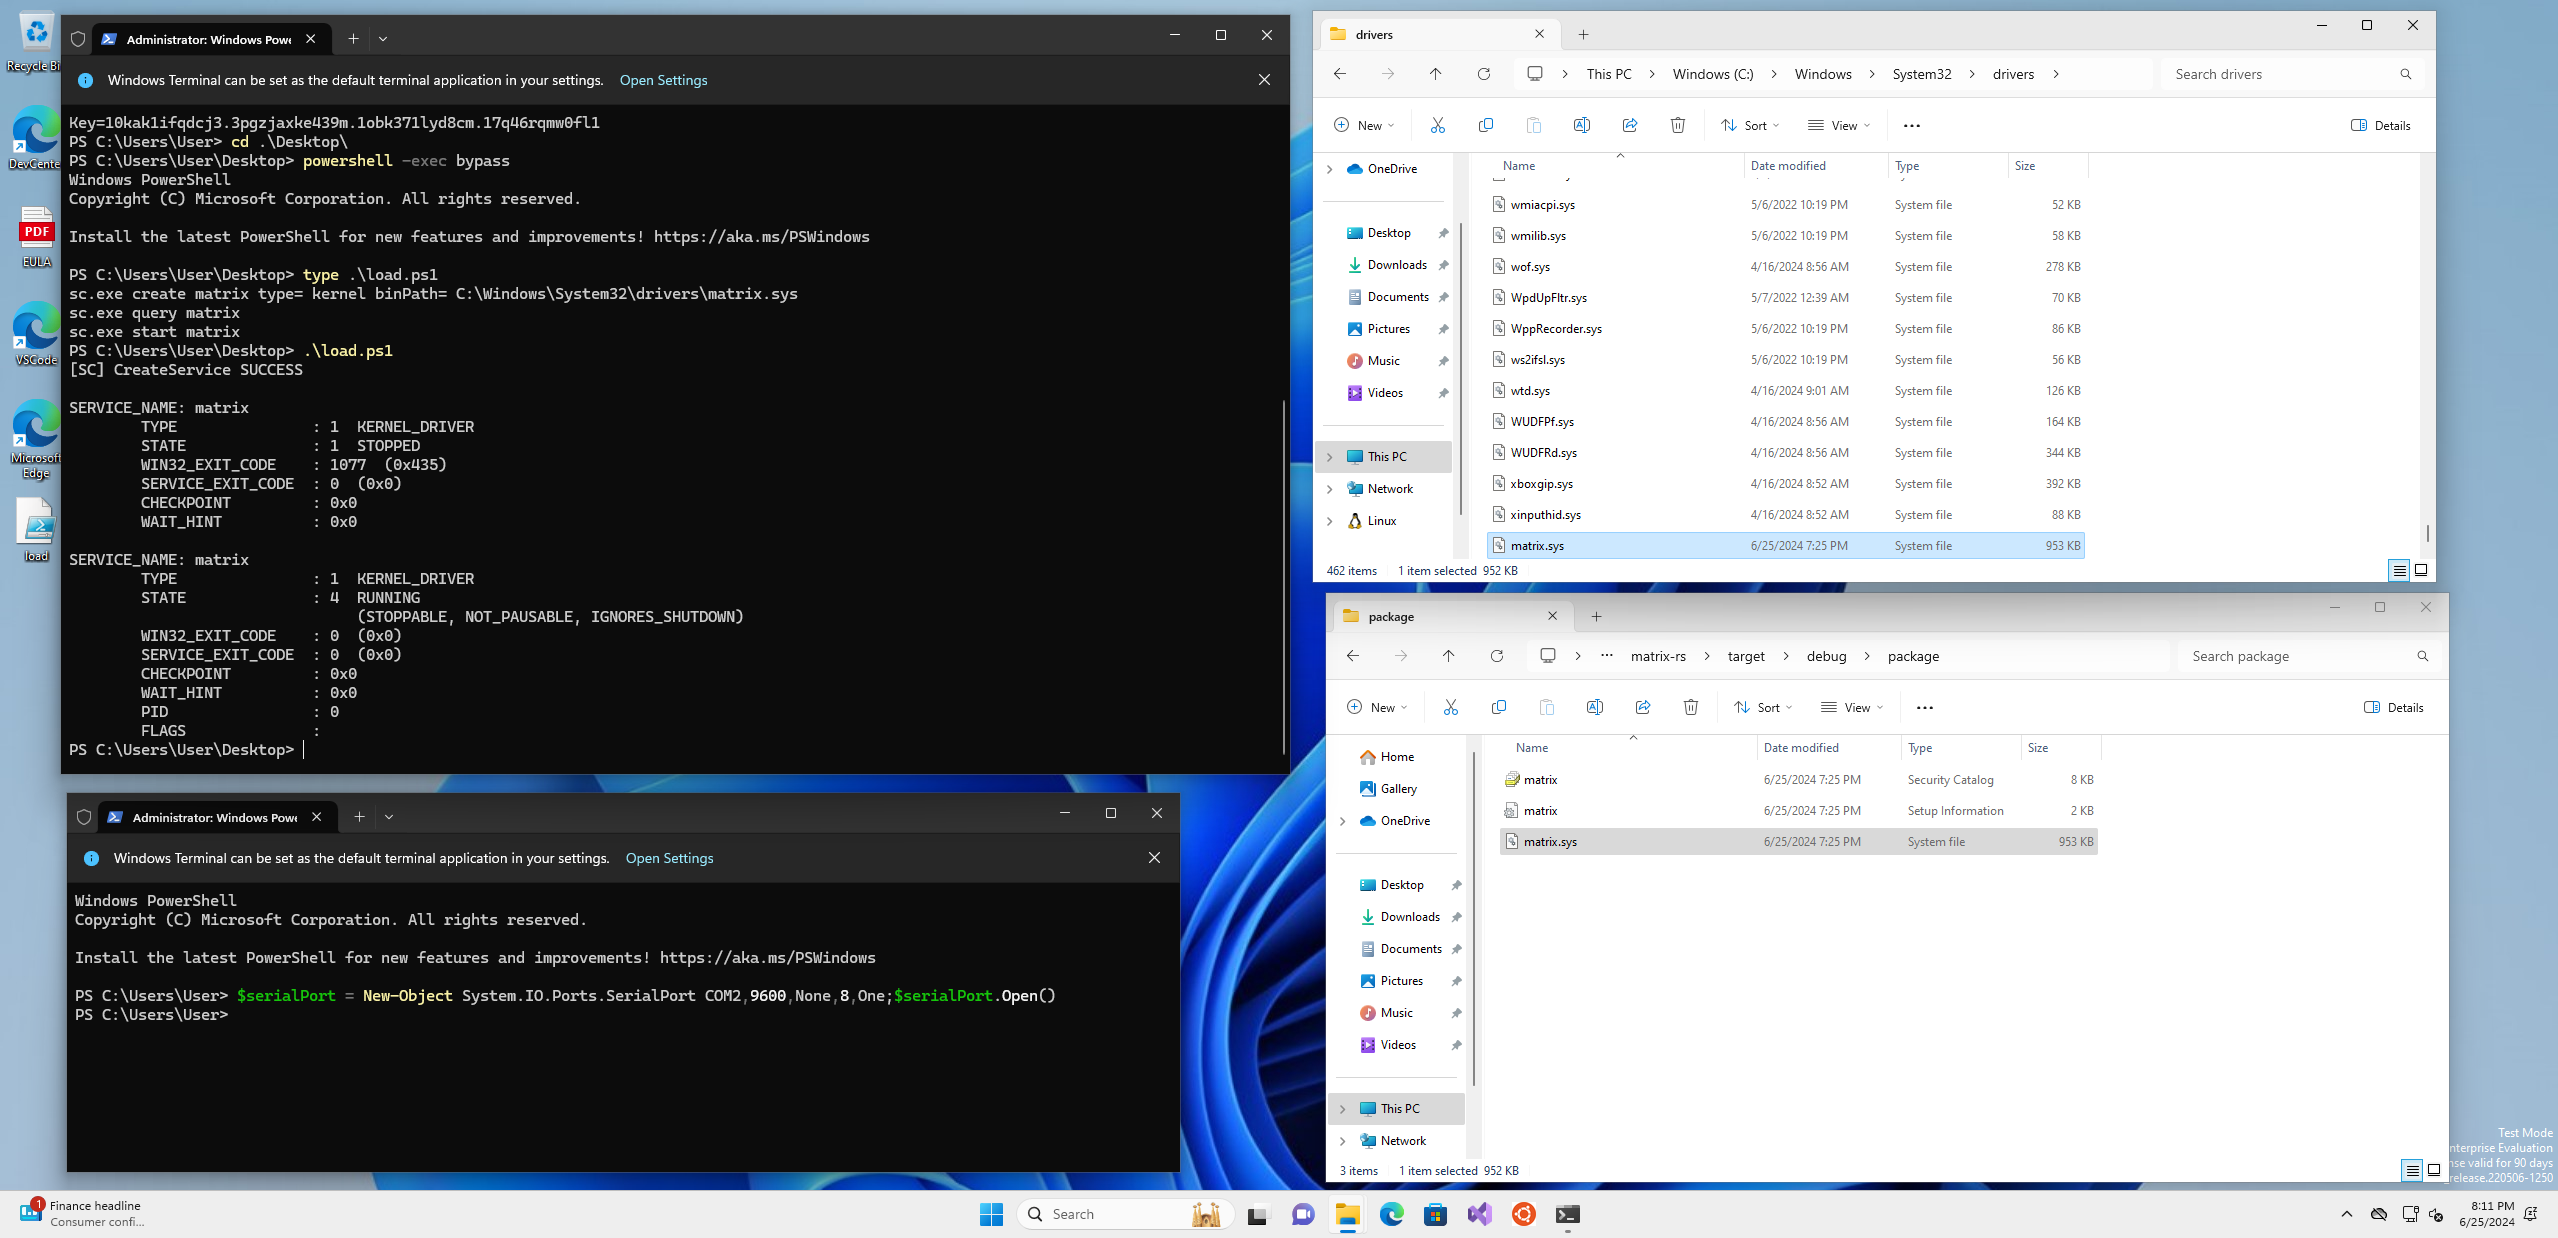
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
dynamic-code-analysiseducationids-ips-evasion+3
3605 months ago
peCloakCapstone preview

peCloakCapstone

GitHubv-p-b/pecloakcapstone

Platform independent peCloak fork based on Capstone

binary-analysisids-ips-evasionmalware-analysis+2
10911 years ago
Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis preview

Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis

GitHubkaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
binary-analysisdigital-forensicsdynamic-analysis-sandboxing+6
26 days ago
hyperhives-macos-infostealer-analysis preview

hyperhives-macos-infostealer-analysis

GitHubdarksp33d/hyperhives-macos-infostealer-analysis

Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…

curated-resourceseducationforensics+6
336 months ago
CVE-2024-20154 preview

CVE-2024-20154

GitHubharbingerse7en/cve-2024-20154

Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
binary-analysiseducationembedded-systems-security+8
4 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubalberto-galindo/cve-2025-5548

Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
binary-exploitationdebuggerseducation+8
7 months ago
Androl4b preview

Androl4b

GitHubsh4hin/androl4b

A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis

android-securityeducationlabs-practice+4
1.2k6 years ago
Previous12Next