
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
salt preview

salt

GitHubpaolomonti42/salt

SALT - SLUB ALlocator Tracer for the Linux kernel

binary-analysisdebuggerseducation+2
1578 years ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

digital-forensicsforensicshardware-security+5
4.4k3 days ago
idamcp preview

idamcp

GitHubidamcp/idamcp

MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…

ai-assisted-reversingbinary-analysisdebuggers+3
1207 days ago
OffensiveRust preview

OffensiveRust

GitHubtrickster0/offensiverust

Rust Weaponization for Red Team Engagements.
binary-exploitationcommand-and-controleducation+9
3.0k3 years ago
frida-c2-mcp preview

frida-c2-mcp

GitHubs4dp4nd4/frida-c2-mcp

Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
android-securitycommand-and-controldynamic-analysis-sandboxing+8
656 months ago
rikune preview

rikune

GitHublast-emo-boy/rikune

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
binary-analysisdynamic-analysis-sandboxingeducation+8
24014 days ago
volatility preview
Archived

volatility

GitHubvolatilityfoundation/volatility

An advanced memory forensics framework
digital-forensicsforensicsincident-response+4
8.1k1 year ago
machscope preview

machscope

GitHubm10ust/machscope

macOS IPC, launchd, Mach-O, and trust relationship explorer — zero-dependency terminal-native forensic tool
binary-analysisdigital-forensicsforensics+7
11 month ago
CVE-2022-21974 preview
Archived

CVE-2022-21974

GitHub0vercl0k/cve-2022-21974

PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"
binary-exploitationdebuggersexploitation+3
574 years ago
ios.CVE-2026-84616-84607 preview

ios.CVE-2026-84616-84607

GitHubping-2o/ios.cve-2026-84616-84607

research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607
binary-analysiseducationexploitation+6
1122 days ago
intel-me-research preview

intel-me-research

GitHubjatinkapilaq1/intel-me-research

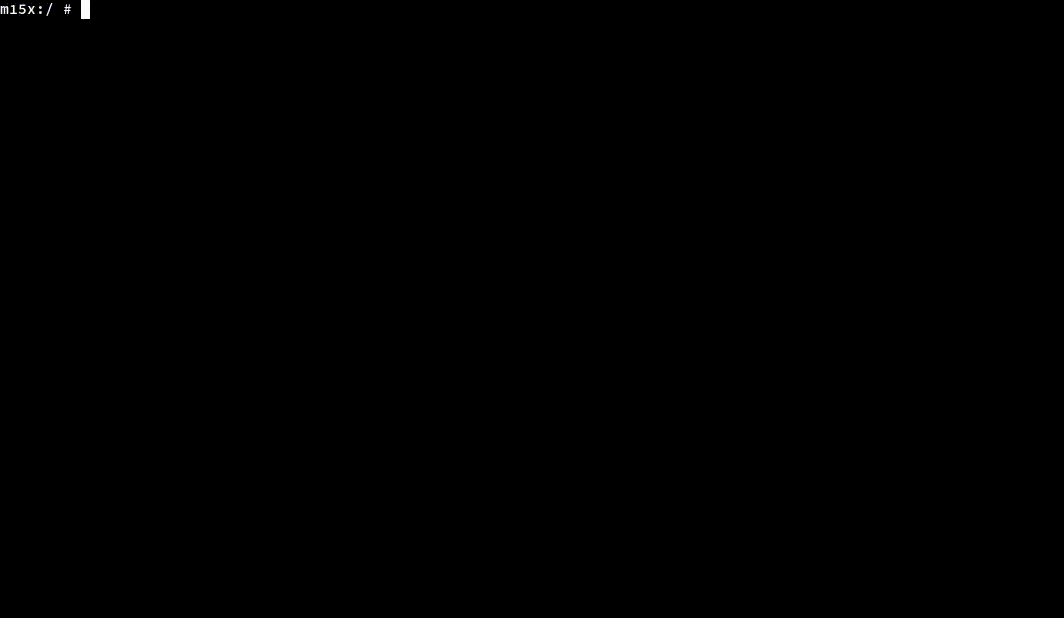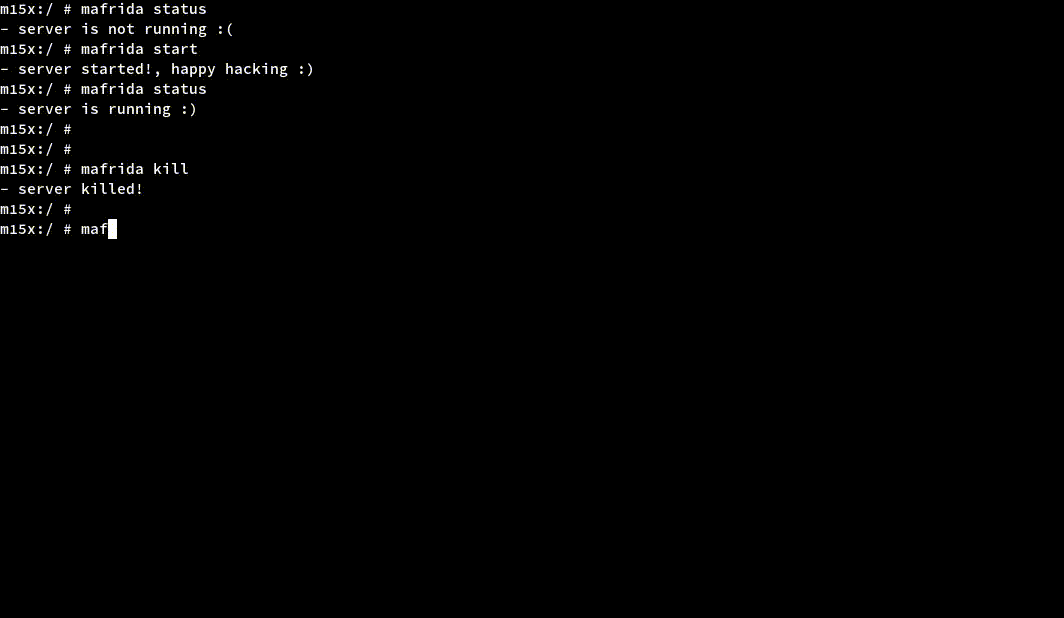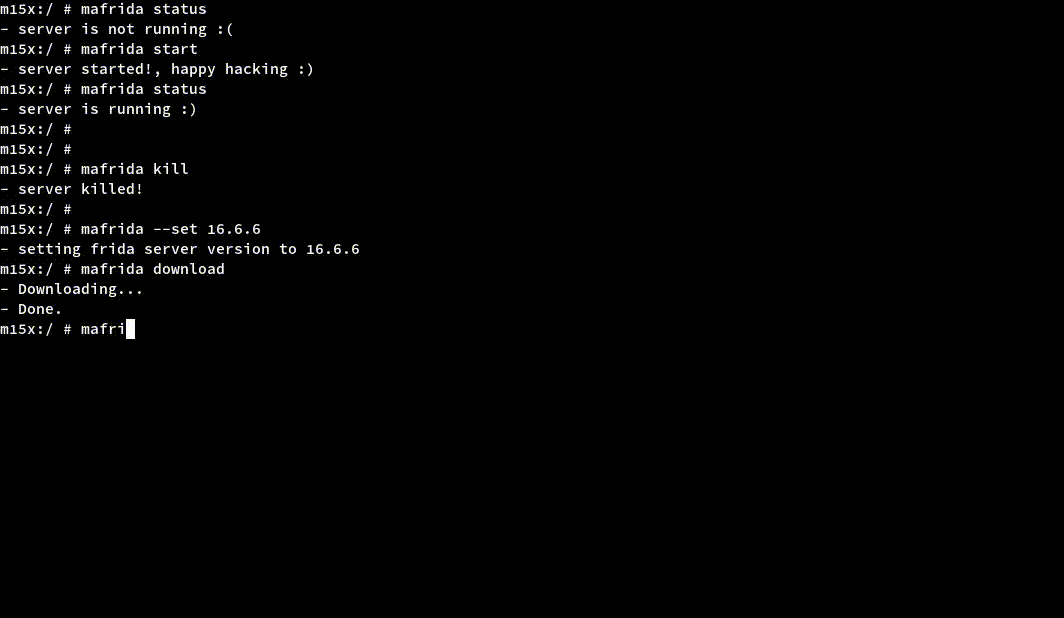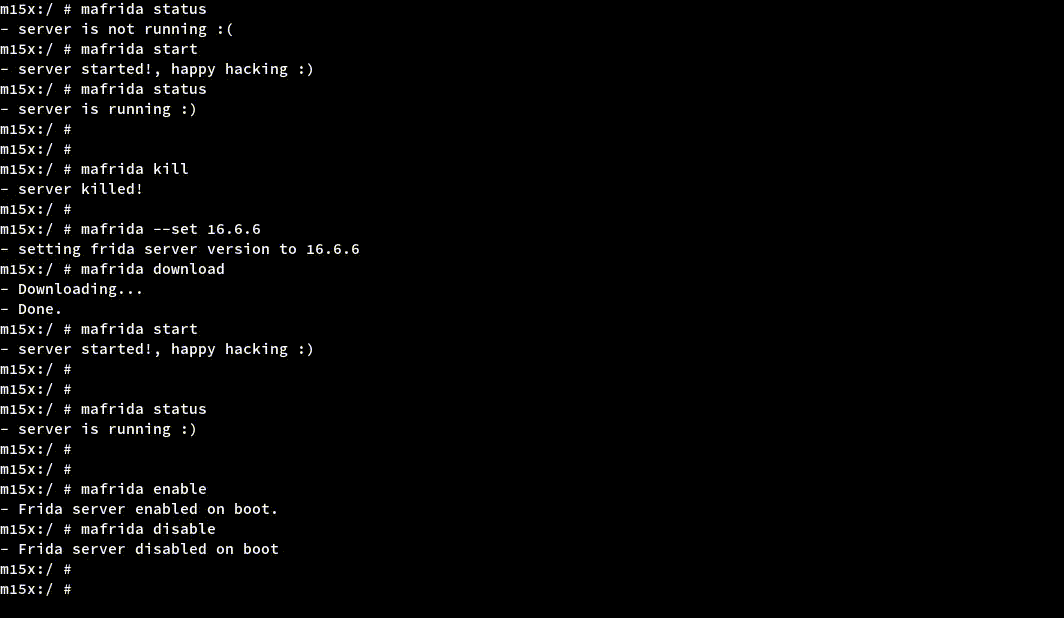
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
binary-analysisembedded-systems-securityfirmware-analysis+4
152 months ago
rekall preview
Archived

rekall

GitHubgoogle/rekall

Rekall Memory Forensic Framework

digital-forensicsforensicsincident-response+3
2.0k5 years ago
MaFrida preview

MaFrida

GitHubtheshinigami/mafrida

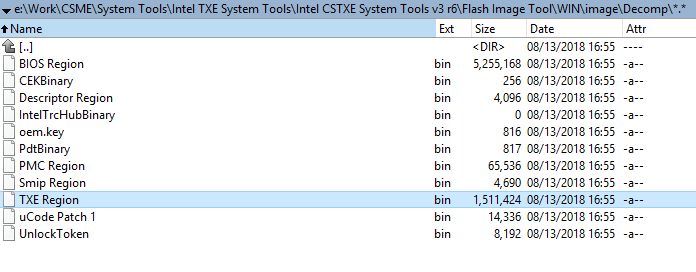
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
android-securitydynamic-analysis-sandboxingdynamic-code-analysis+5
418 days ago
IntelTXE-PoC preview
Archived

IntelTXE-PoC

GitHubptresearch/inteltxe-poc

Intel Management Engine JTAG Proof of Concept

binary-exploitationdebuggersembedded-systems-security+6
5486 years ago
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
binary-analysisdefensive-toolsforensics+6
3902 months ago
Filedumper preview

Filedumper

GitHubseyyidkadir/filedumper

Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
data-recoverydigital-forensicsforensics+3
18 months ago
SOC336-Windows-OLE-Zero-Click-RCE-Exploitation-Detected-CVE-2025-21298 preview

SOC336-Windows-OLE-Zero-Click-RCE-Exploitation-Detected-CVE-2025-21298

GitHubabc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
command-and-controleducationemail-security+9
4 months ago
labs-releases preview

labs-releases

GitHubelastic/labs-releases

Elastic Security Labs releases

curated-resourcesioc-managementmalware-analysis+2
9127 days ago
Previous123Next