
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
sshuttle preview

sshuttle

GitHubsshuttle/sshuttle

Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…

command-and-controldata-exfiltrationdns-analysis+6
13.5k
17h 41m ago
Lab-RATS-v1.6 preview

Lab-RATS-v1.6

GitHubk4n3co/lab-rats-v1.6

Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
android-securitycommand-and-controldata-exfiltration+8
803 days ago
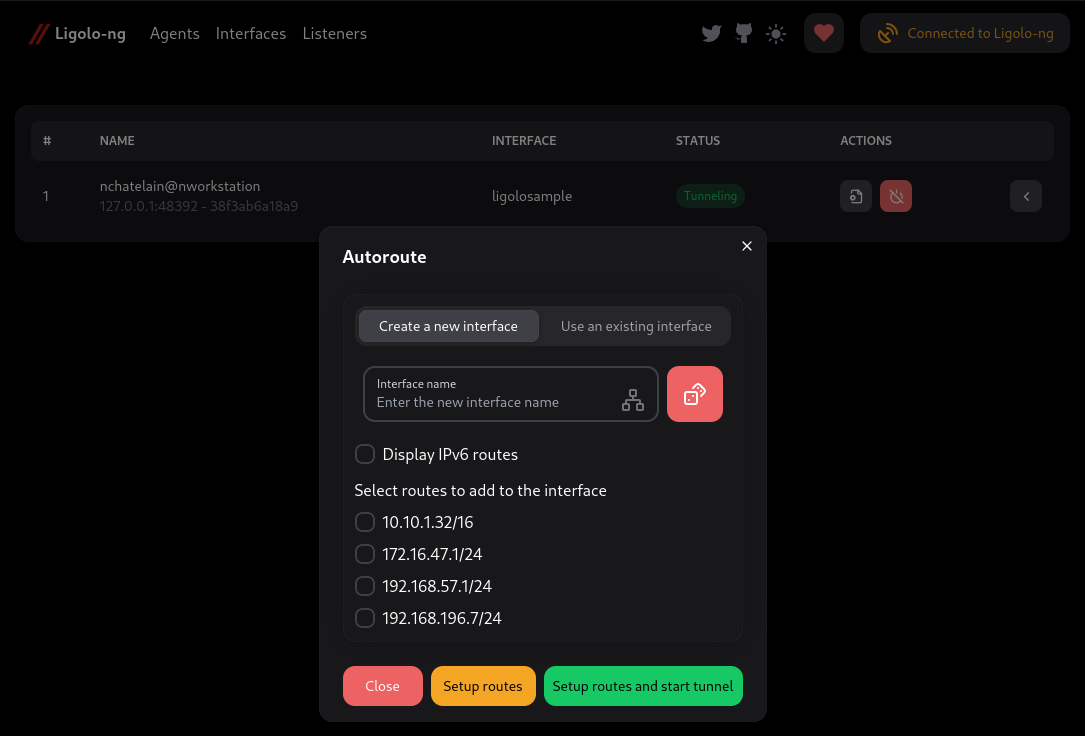
ligolo-ng preview

ligolo-ng

GitHubnicocha30/ligolo-ng

An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
data-exfiltrationgeneral-purpose-utilitiesids-ips-evasion+6
4.8k1 month ago
MicroTrick preview

MicroTrick

GitHubdigiprosec/microtrick

Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…

authenticationembedded-systems-securityexploitation+7
581 month ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.2k1 month ago
CTT-Enhanced-CVE-2026-46339-Exploit-Engine preview

CTT-Enhanced-CVE-2026-46339-Exploit-Engine

GitHubsimoesctt/ctt-enhanced-cve-2026-46339-exploit-engine

Python framework exploiting CVE-2026-46339 for unauthenticated RCE on 9Router via MCP bridge, using temporal sharding and dispersion to evade…
exploitationpayload-developmentred-teaming+3
2 months ago
slot2 preview

slot2

GitHubcenobyte-vincit/slot2

UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…

cloud-securitycommand-and-controldata-exfiltration+5
2 months ago
begal-c2 preview

begal-c2

GitHubxsanflip/begal-c2

Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
command-and-controldata-exfiltrationeducation+6
84 months ago
CVE-2026-23744 preview

CVE-2026-23744

GitHubinzegosec/cve-2026-23744

Exploit for MCPJam Inspector <=1.4.2 that triggers remote code execution via crafted HTTP requests, enabling unauthorized installation of MCP servers…
exploitationpenetration-testingremote-access-trojan+2
17 months ago
PixelCode-Attack preview

PixelCode-Attack

GitHubs3n4t0r-0x0/pixelcode-attack

Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
command-and-controldata-exfiltrationeducation+8
1719 months ago
TelegramRAT preview

TelegramRAT

GitHubmachine1337/telegramrat

Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions

command-and-controlinformation-gatheringpost-exploitation+3
4461 year ago
BloodfangC2 preview

BloodfangC2

GitHubzarkones/bloodfangc2

Modern PIC implant for Windows (64 & 32 bit)

adversarial-attackcommand-and-controlpayload-development+4
1051 year ago
CHAOS preview

CHAOS

GitHubtiagorlampert/chaos

🔥 CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems.
command-and-controlpayload-generationpost-exploitation+3
2.8k2 years ago
malvinci preview

malvinci

GitHubgsoffmarket/malvinci

This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…
command-and-controldata-exfiltrationpayload-development+3
592 years ago
CVE-2023-22527 preview

CVE-2023-22527

GitHubrevoltsecurities/cve-2023-22527

Exploitation tool for CVE-2023-22527 targeting Confluence servers, enabling remote code execution with support for multiple targets, concurrency, and…
exploitationpenetration-testingred-teaming+3
102 years ago
CVE-2023-22527 preview

CVE-2023-22527

GitHubc1ph3rx13/cve-2023-22527

Exploit for Atlassian Confluence RCE (CVE-2023-22527) that executes arbitrary commands on vulnerable servers via OGNL injection.
exploitationpenetration-testingremote-access-trojan+2
42 years ago
metasploit-javapayload preview
Archived

metasploit-javapayload

GitHubrapid7/metasploit-javapayload

Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.

android-securitycommand-and-controlexploitation+7
943 years ago
Sub7 preview

Sub7

GitLabillwill/sub7

Source code for SubSeven 2.1.3

command-and-controlmalware-analysispayload-generation+2
153 years ago
Previous12Next