Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CHAOS — 🔥 CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems. | Kitploit
Tools/GitHubGitHub/tiagorlampert/chaos
Payload GenerationPost-ExploitationCommand and ControlRed TeamingRemote Access ToolRemote Access Trojan
GitHubtiagorlampert/chaos

CHAOS

🔥 CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems.

View Repository
2.8k594722 years agoReviewed by Kitploit
Share

CHAOS logo

CHAOS: Remote Administration Tool

CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems.
Report bug · Request feature · Quick start · Screenshots

Disclaimer

THIS SOFTWARE IS PROVIDED "AS IS" WITHOUT WARRANTY OF ANY KIND. YOU MAY USE THIS SOFTWARE AT YOUR OWN RISK. THE USE IS COMPLETE RESPONSIBILITY OF THE END-USER. THE DEVELOPERS ASSUME NO LIABILITY AND ARE NOT RESPONSIBLE FOR ANY MISUSE OR DAMAGE CAUSED BY THIS PROGRAM.

Table of contents

  • Features
  • Quick start
  • Databases
  • Video
  • Screenshots
  • Contributing
  • Donate
  • Sponsors
  • Copyright and license

Features

Feature
Reverse ShellXX
Download FileXX
Upload FileXX
Delete FileXX
ScreenshotXX
File ExplorerXX
Get OS InfoXX
Run HiddenX
RestartXX
ShutdownXX
Lock screenX
Sign outX
Open UrlXX

Quick start

Some install options are available:

1. Local Development

See more:
# Install dependencies
$ sudo apt install golang git -y

# Get this repository
$ git clone https://github.com/tiagorlampert/CHAOS

# Go into the repository
$ cd CHAOS/

# Run
$ PORT=8080 SQLITE_DATABASE=chaos go run cmd/chaos/main.go

2. Docker

See more:

Linux

# Create a shared directory between the host and container
$ mkdir ~/chaos-container

$ docker run -it -v ~/chaos-container:/database/ -v ~/chaos-container:/temp/ \
  -e PORT=8080 -e SQLITE_DATABASE=chaos -p 8080:8080 tiagorlampert/chaos:latest

Windows

# Create a shared directory between the host and container
$ md c:\chaos-container

$ docker run -it -v c:/chaos-container:/database/ -v c:/chaos-container:/temp/ -e PORT=8080 -e SQLITE_DATABASE=chaos -p 8080:8080 tiagorlampert/chaos:latest

3. Deploy on heroku

Try it now on Heroku with a single click:

Deploy to Heroku

After running go to http://localhost:8080 and login with the default username: admin and password: admin and change the password.

Databases

To connect in a supported database you should set some required environment variables:

  • SQLite:

    • SQLITE_DATABASE = chaos
  • PostgreSQL:

    • POSTGRES_DATABASE = chaos
    • POSTGRES_HOST = localhost
    • POSTGRES_PASSWORD = postgres
    • POSTGRES_PORT = 5432
    • POSTGRES_USER = postgres
    • POSTGRES_SSL_MODE = disable/require //optional
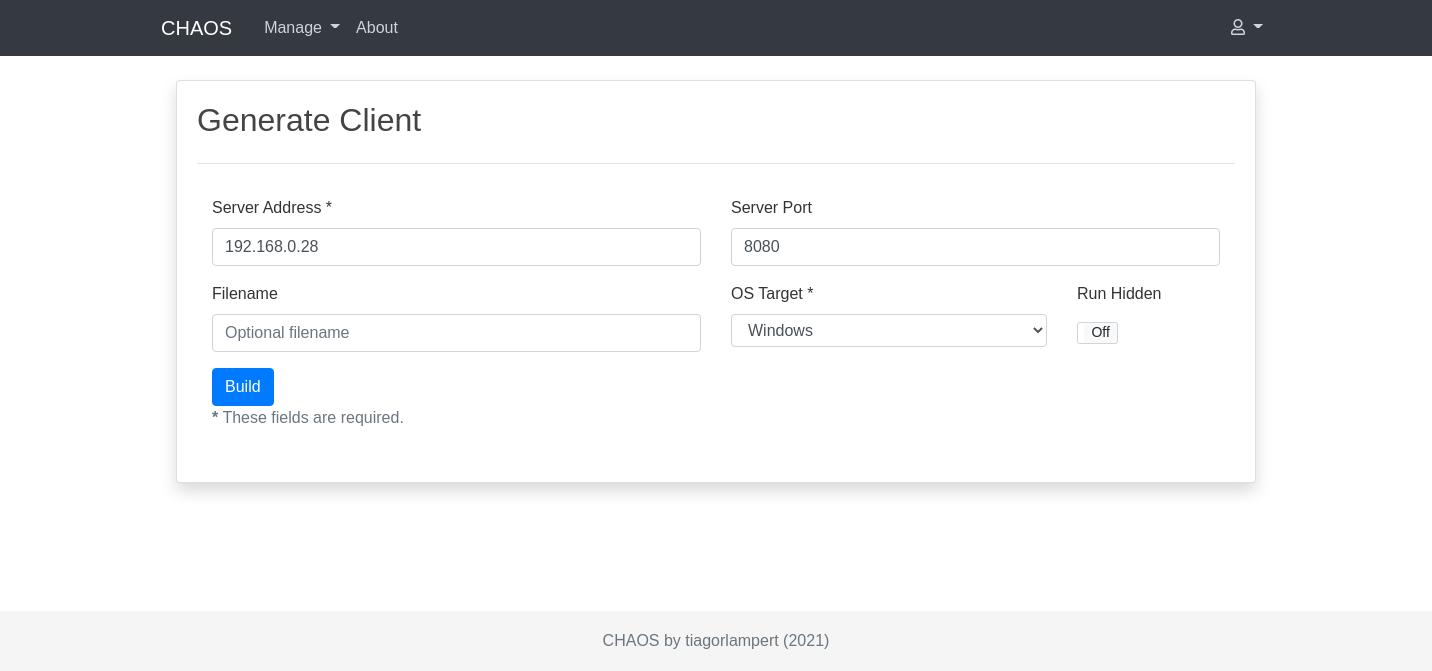
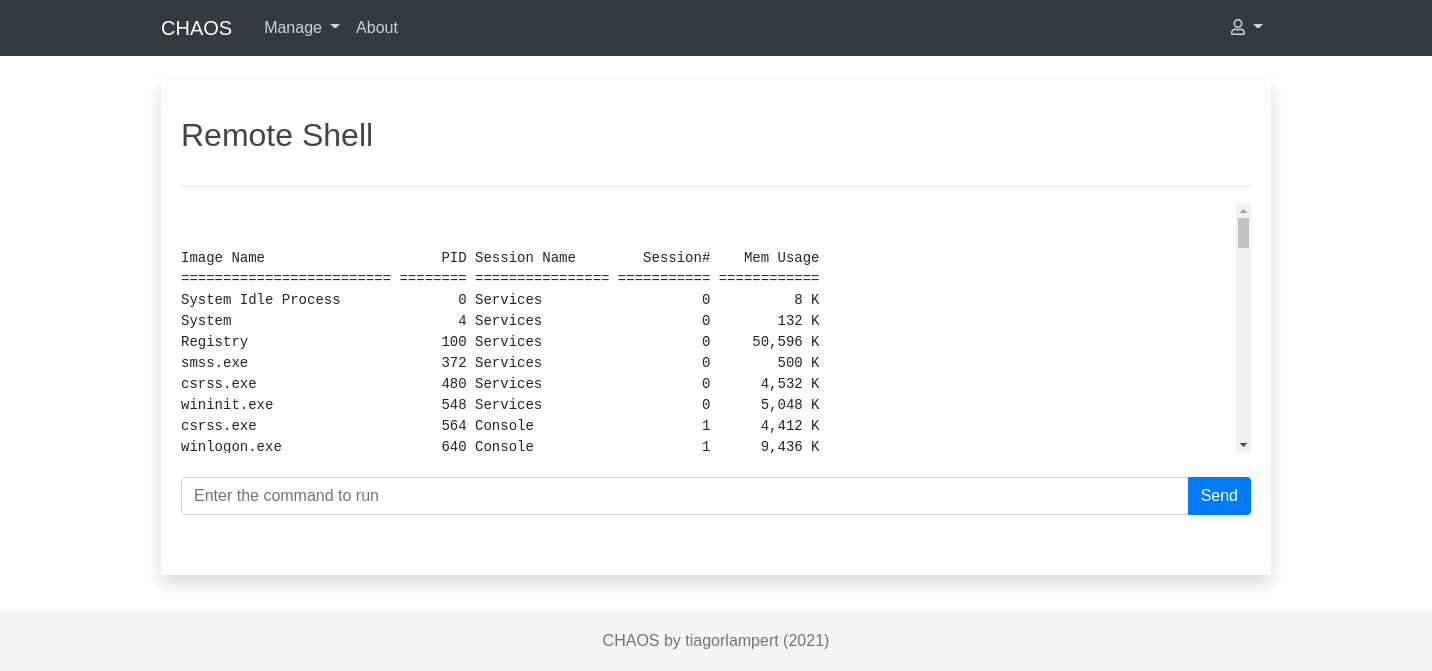
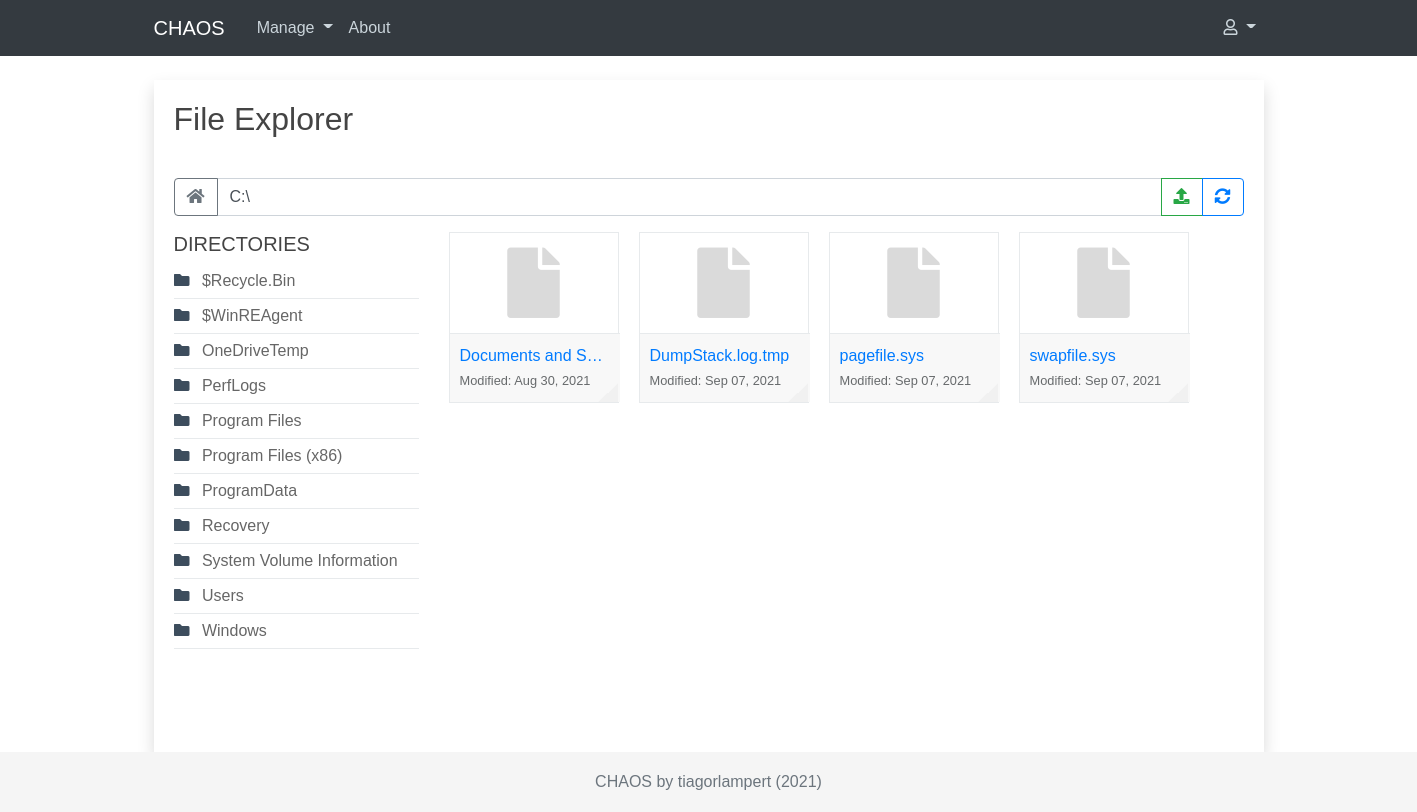
Screenshots

generate

devices

shell

explorer

Contributing

See our contributing guide at CONTRIBUTING.md.

Donate

If you enjoyed this project, give me a cup of coffee. :)
Donate

Copyright and license

The MIT License

Copyright (c) 2017, Tiago Rodrigo Lampert

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →