metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

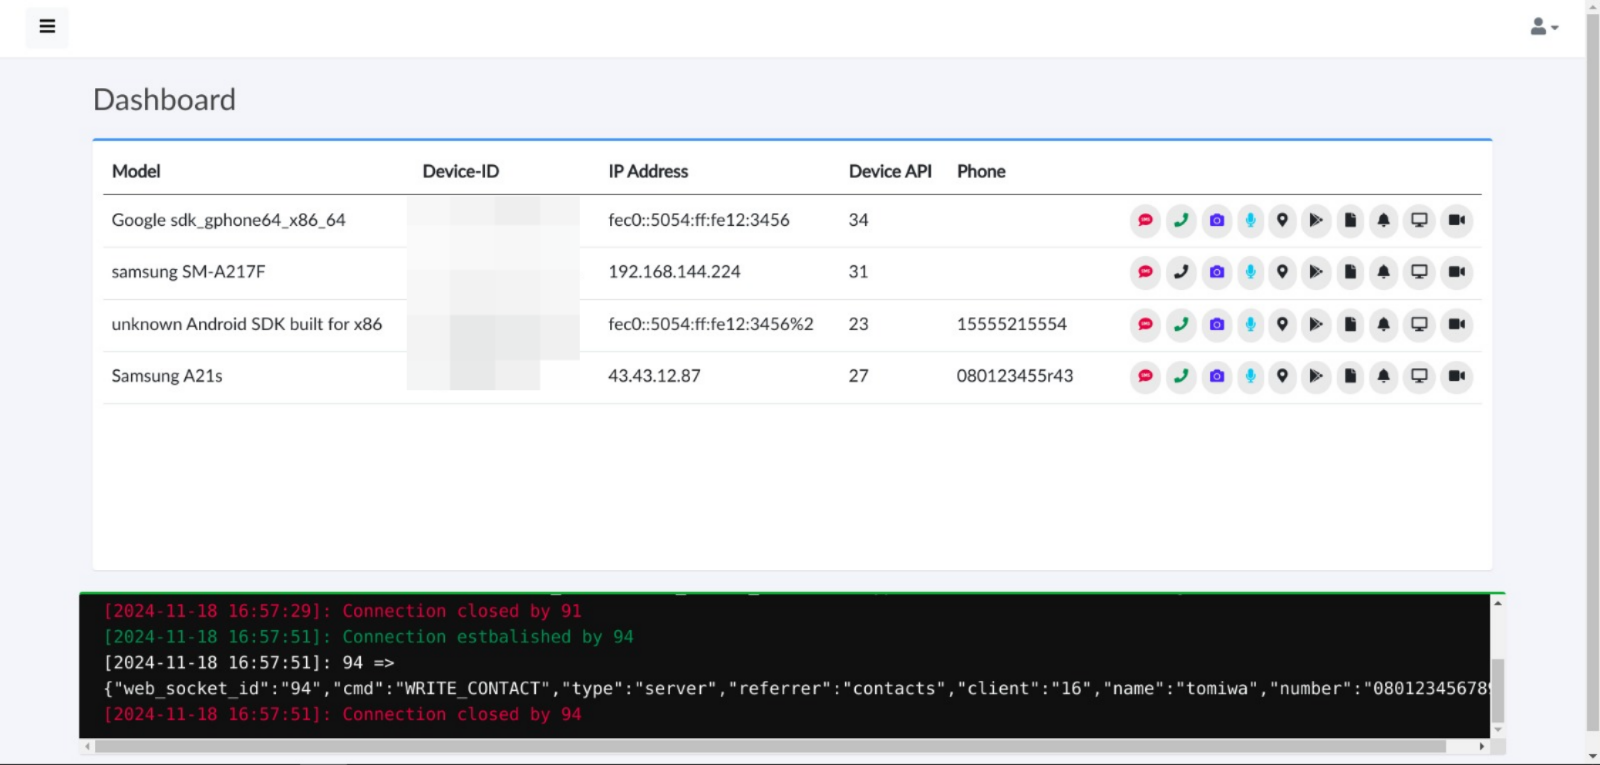
Android remote administration tool

A simple remote tool in C#.

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

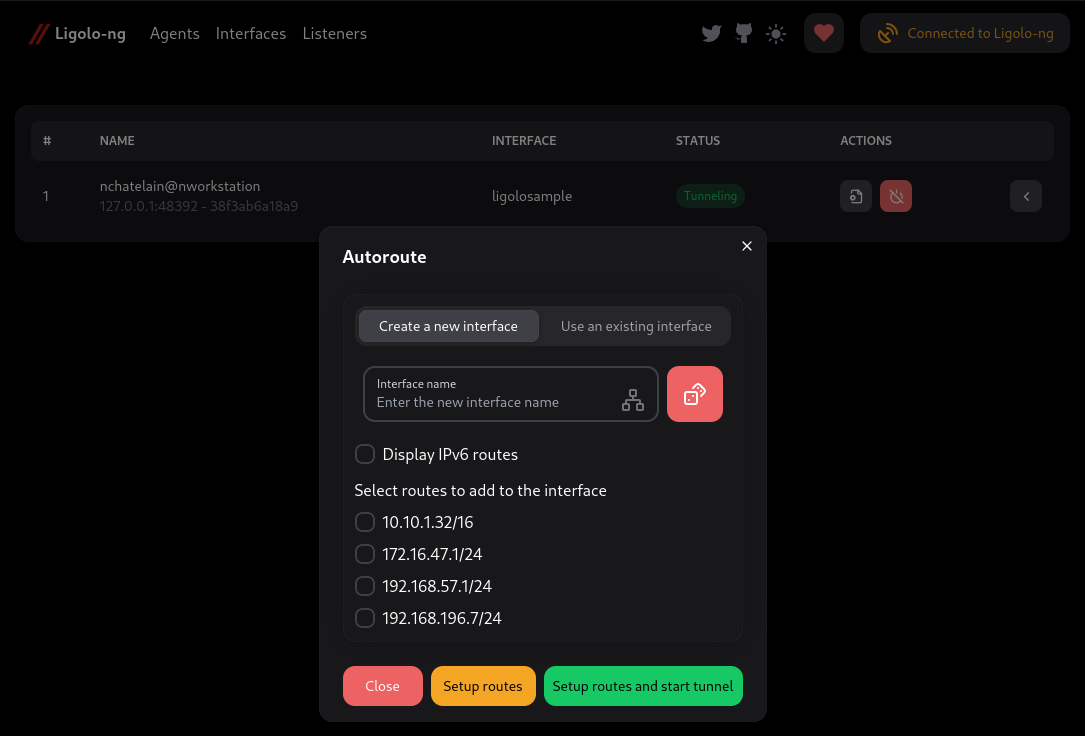
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.

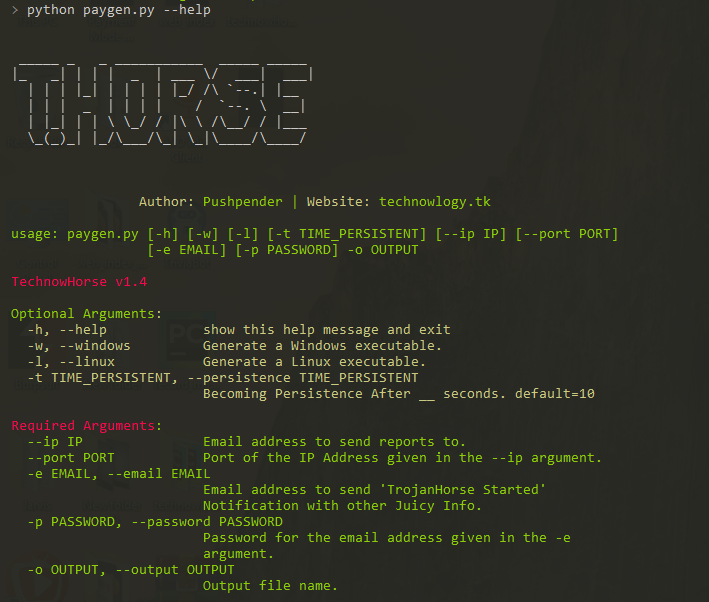
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.

RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…

AdaptixC2 is a highly modular advanced redteam toolkit

Discord Remote Administration Tool fully written in Python3

An Advanced C# .NET Rat, It’s Stable and Contains Many Features.

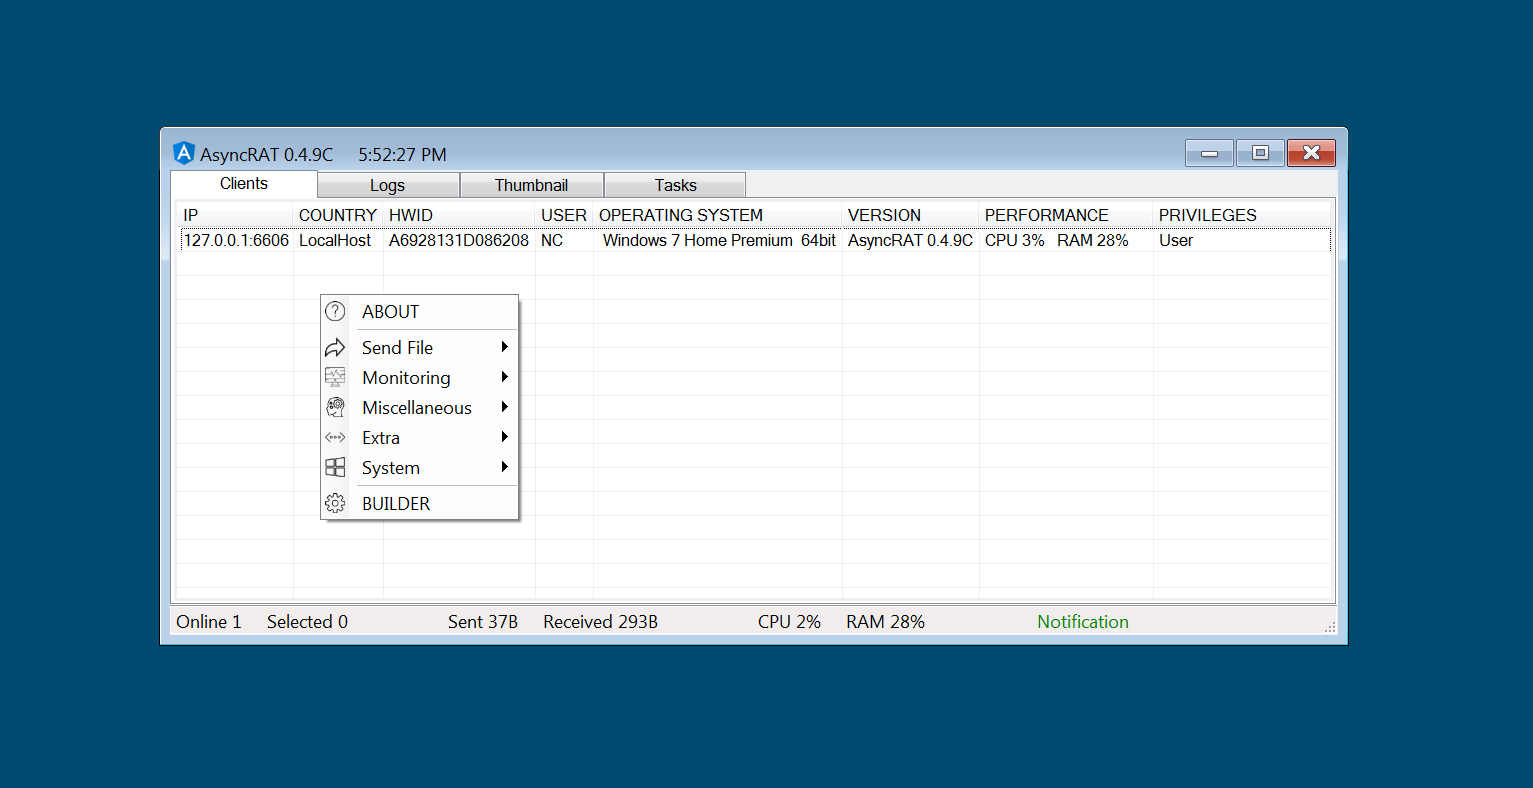
Open-Source Remote Administration Tool For Windows C# (RAT)


🔥 CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems.

DarkAgent Remote Administration Tool RAT by DragonHunter

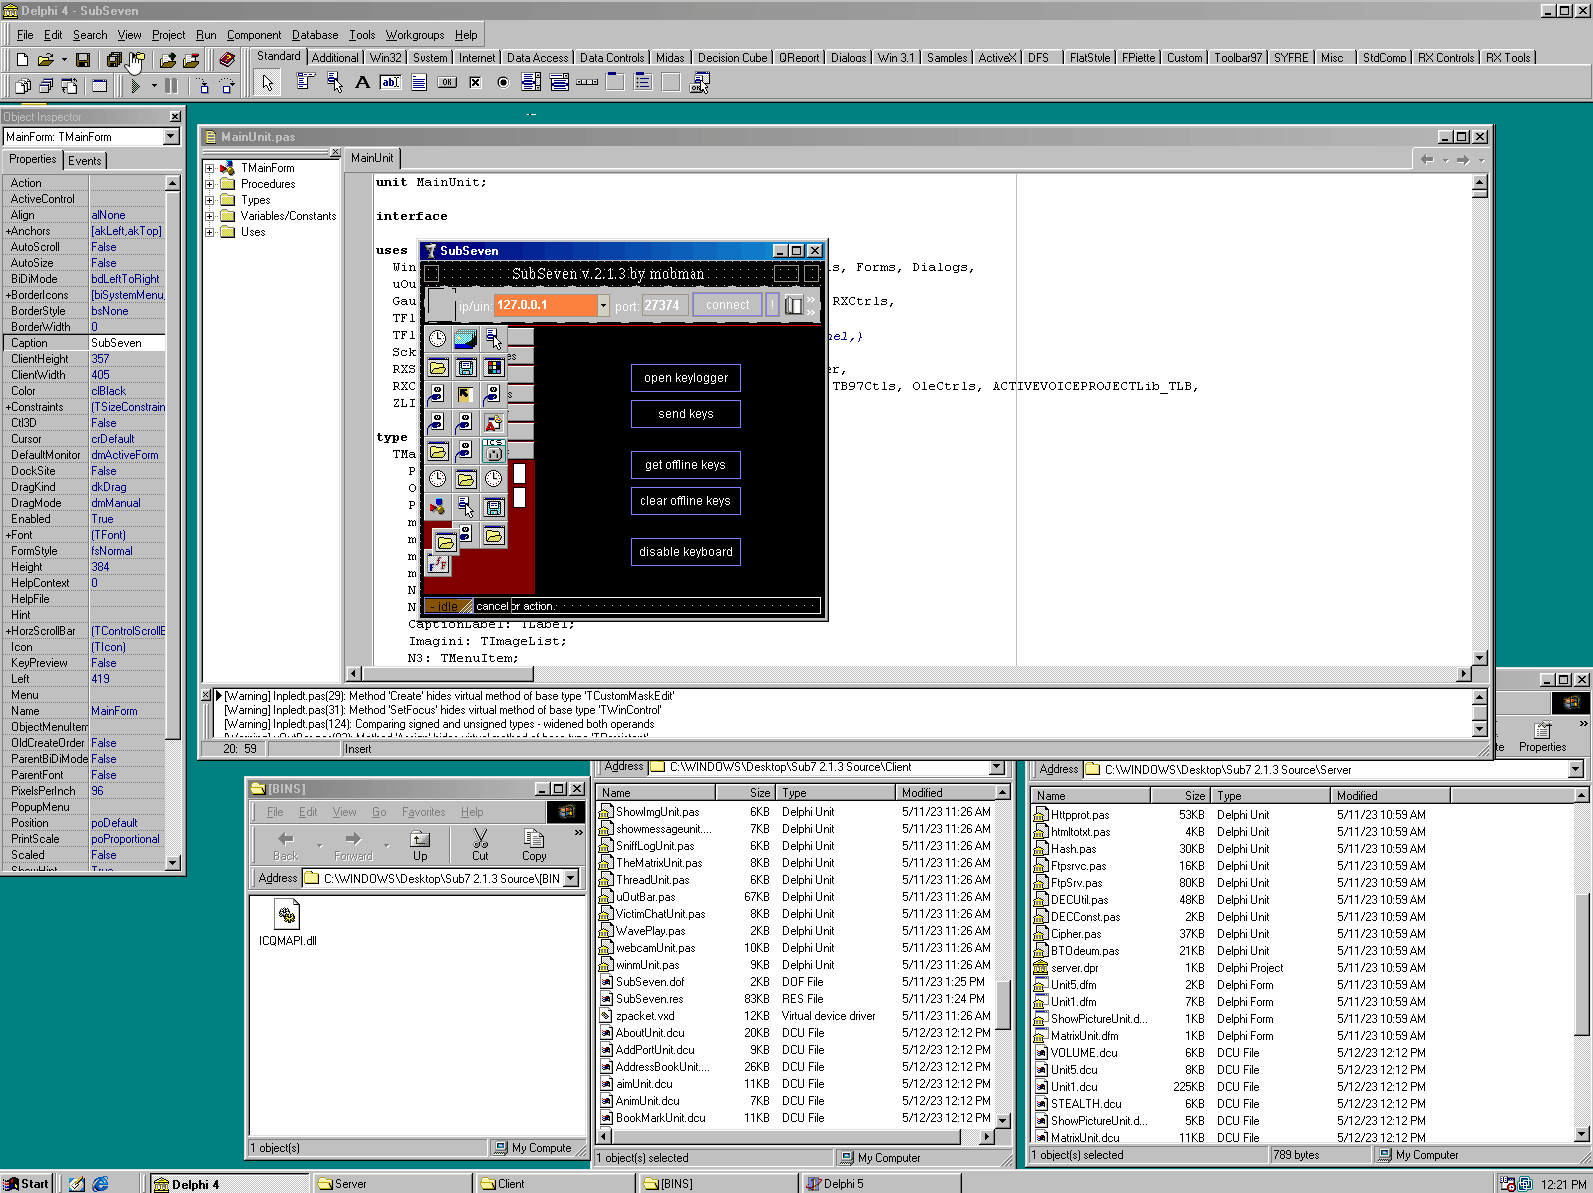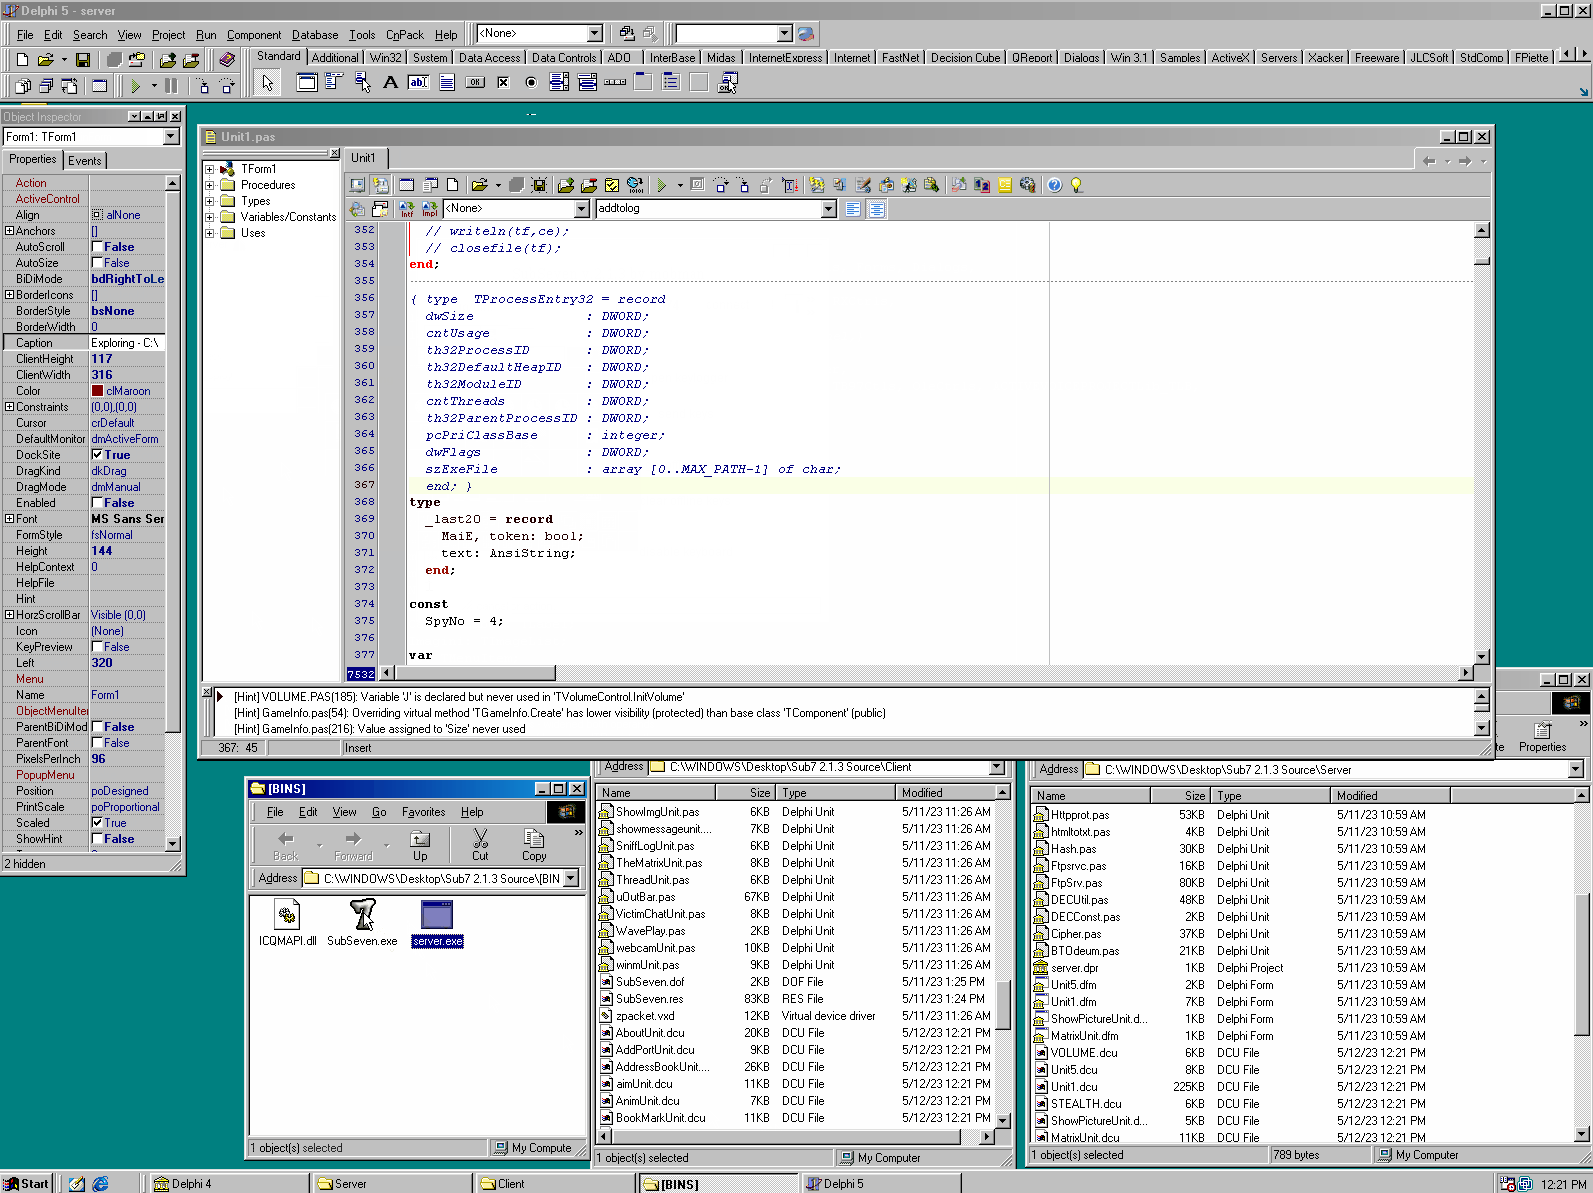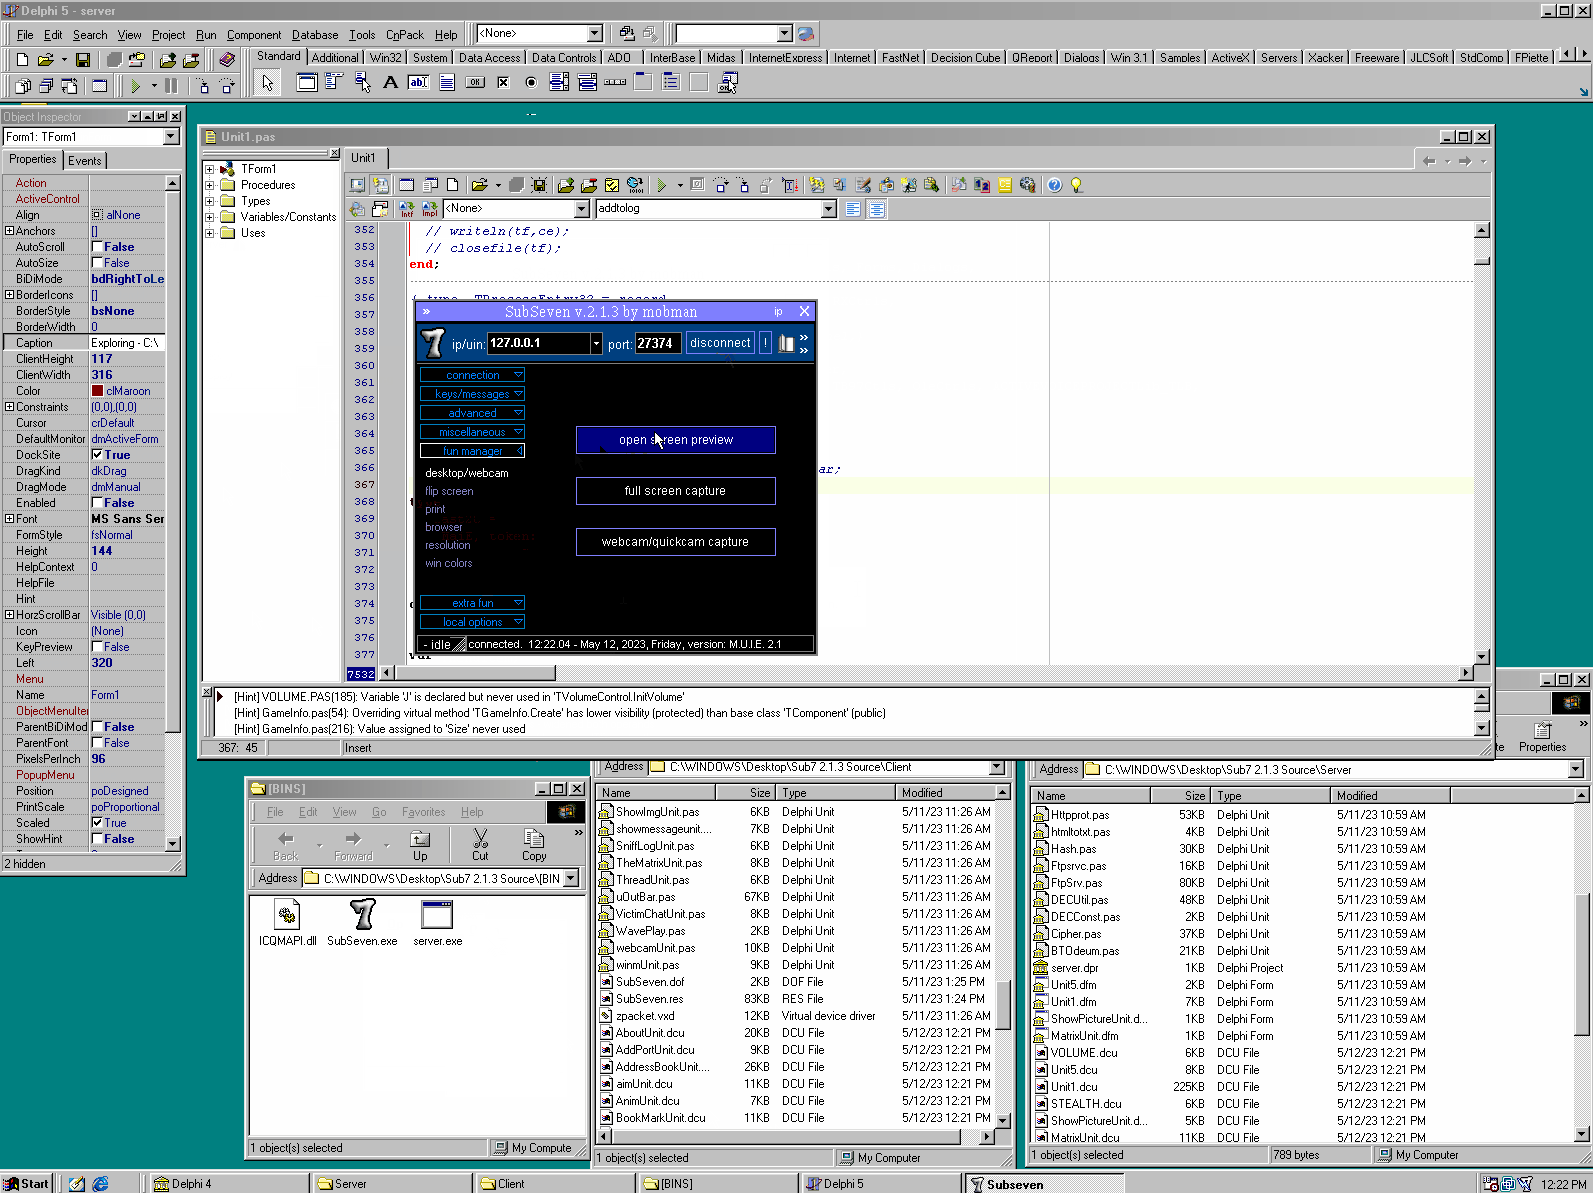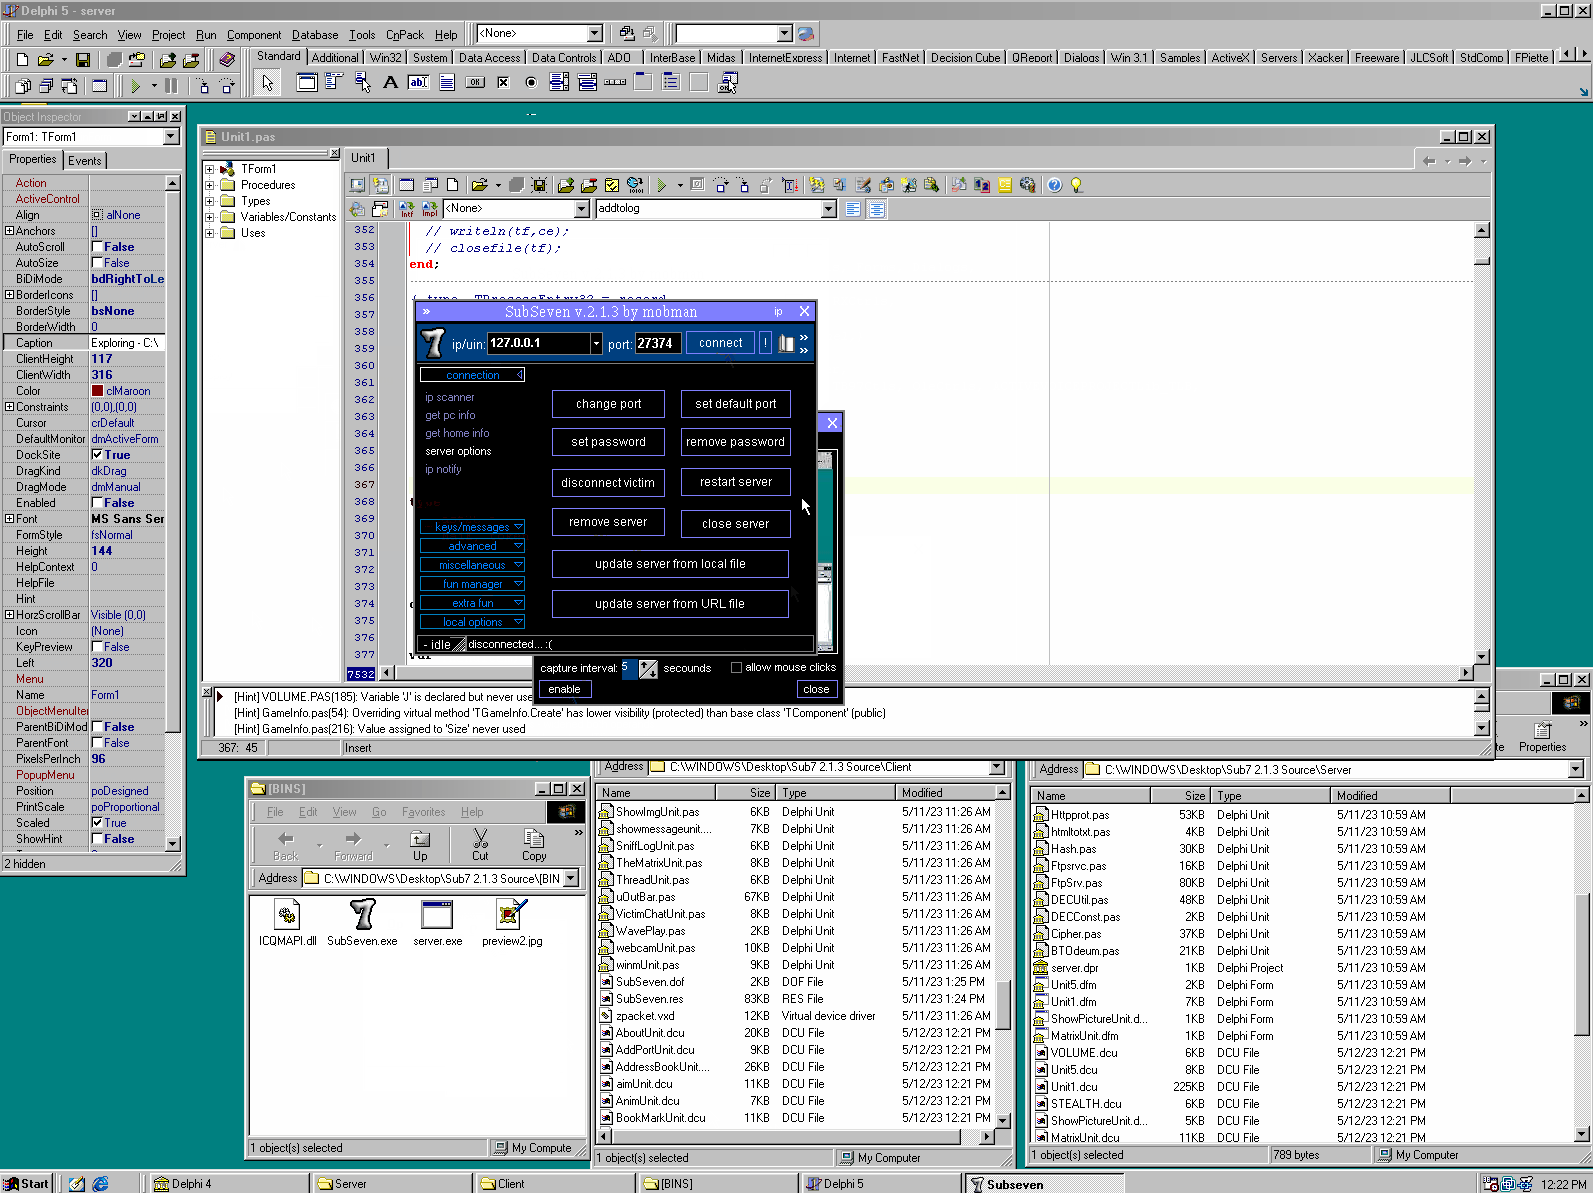
Source code for SubSeven 2.1.3

An evil RAT (Remote Administration Tool) for macOS / OS X.