
Archived
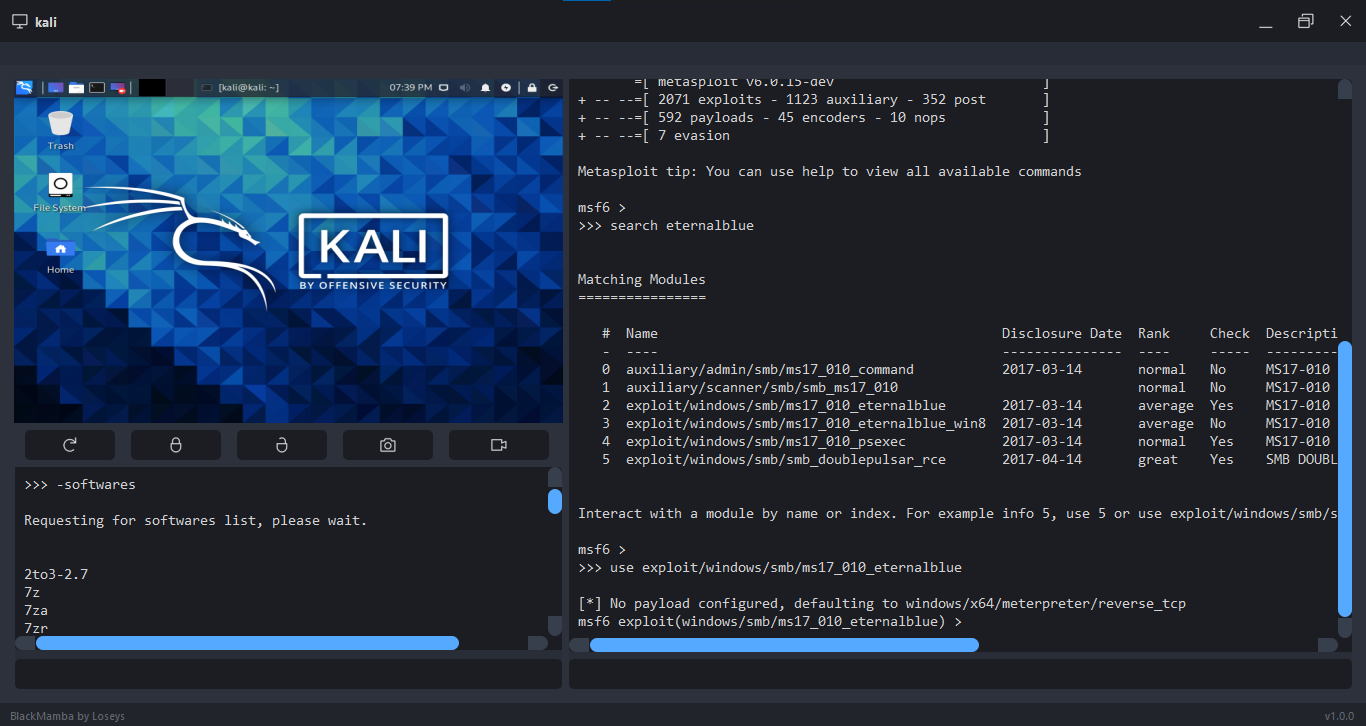
BlackMamba
 loseys/blackmamba
C2/post-exploitation framework
command-and-controldata-exfiltrationencryption-decryption-tools+5
1.2k
loseys/blackmambaC2/post-exploitation framework
 telefonica/ibombshell
Tool to deploy a post-exploitation prompt at any time
 1872892142/jboss-autopwn-1
JBoss Autopwn as featured at BlackHat Europe 2010 - this version incorporates CVE-2010-0738 the JBoss authentication bypass VERB manipulation…
 asang17/cve-2021-40222
Remote Code Execution at Rittal
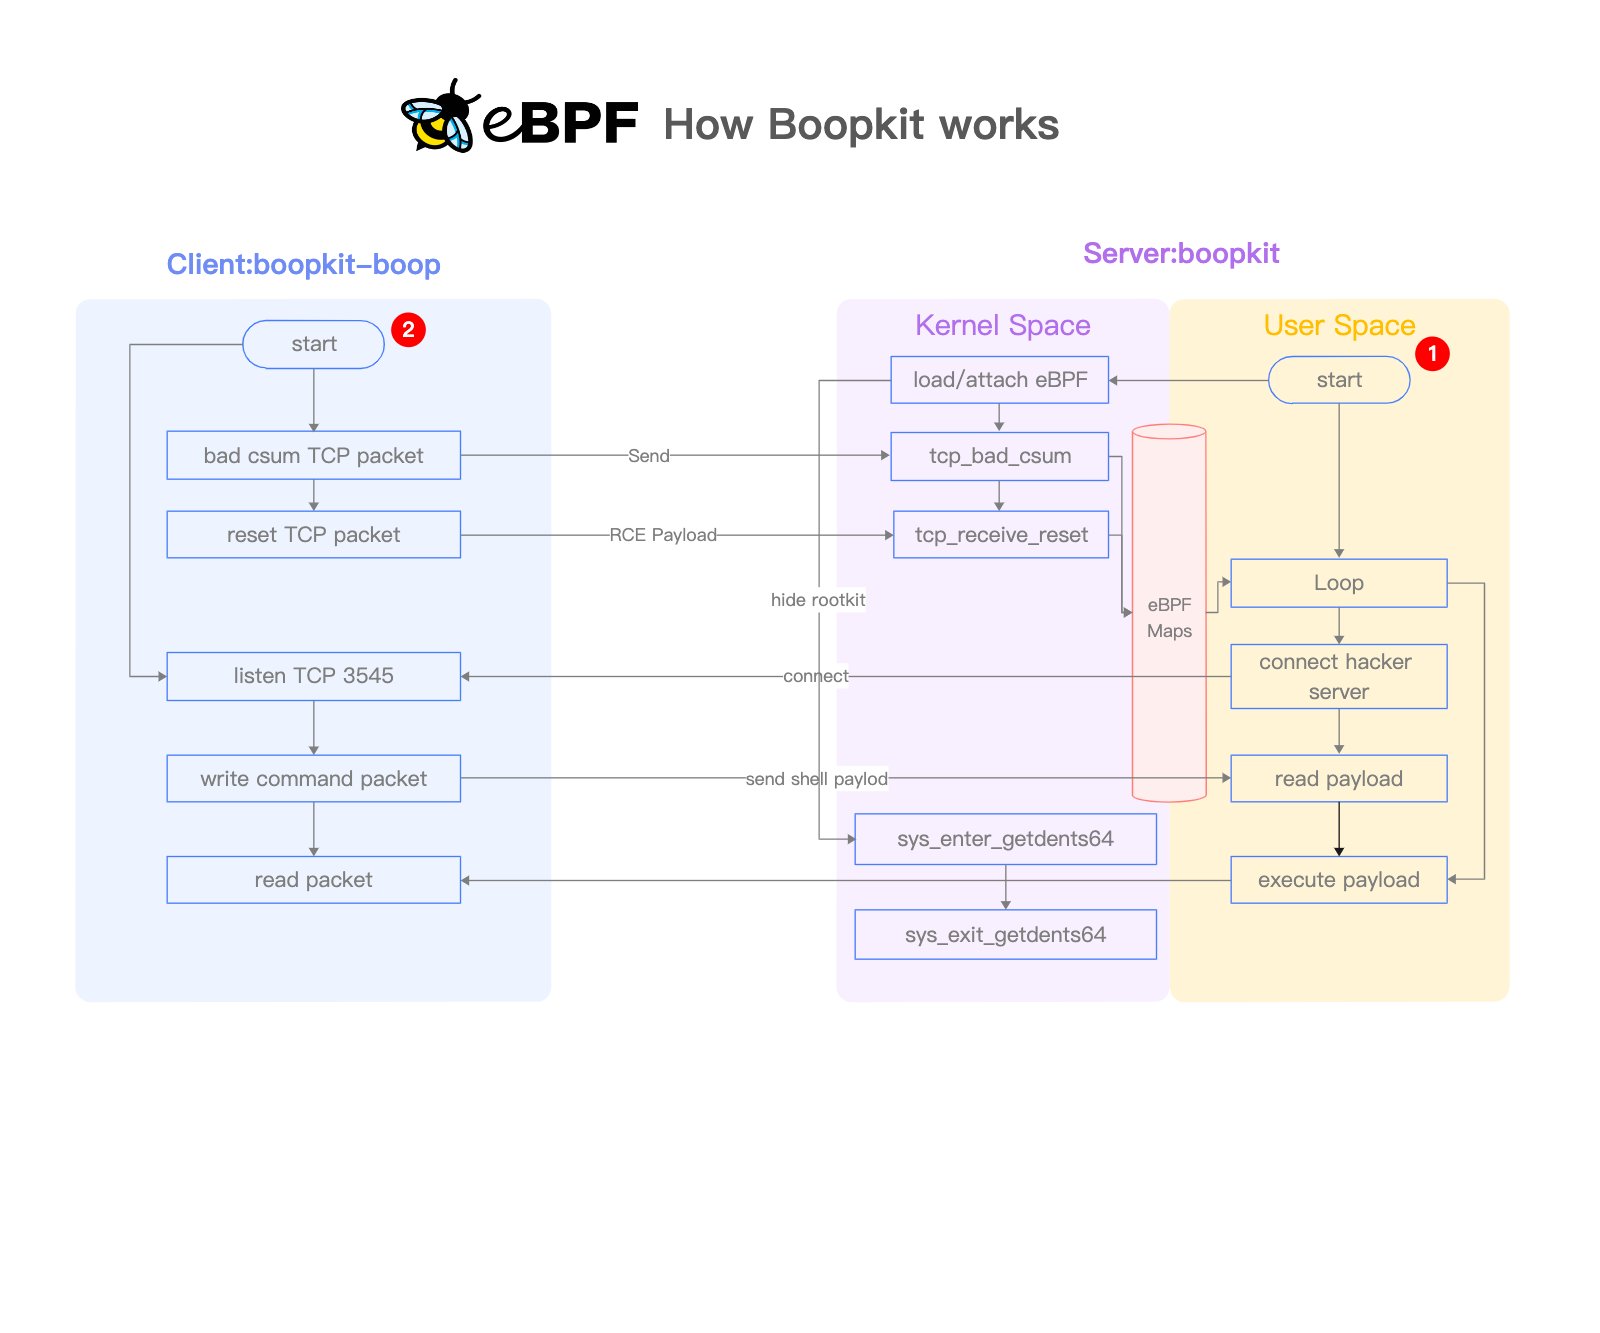 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 ilikenwf/darkagent
DarkAgent Remote Administration Tool RAT by DragonHunter
 offlinemark/poet
[unmaintained] Post-exploitation tool
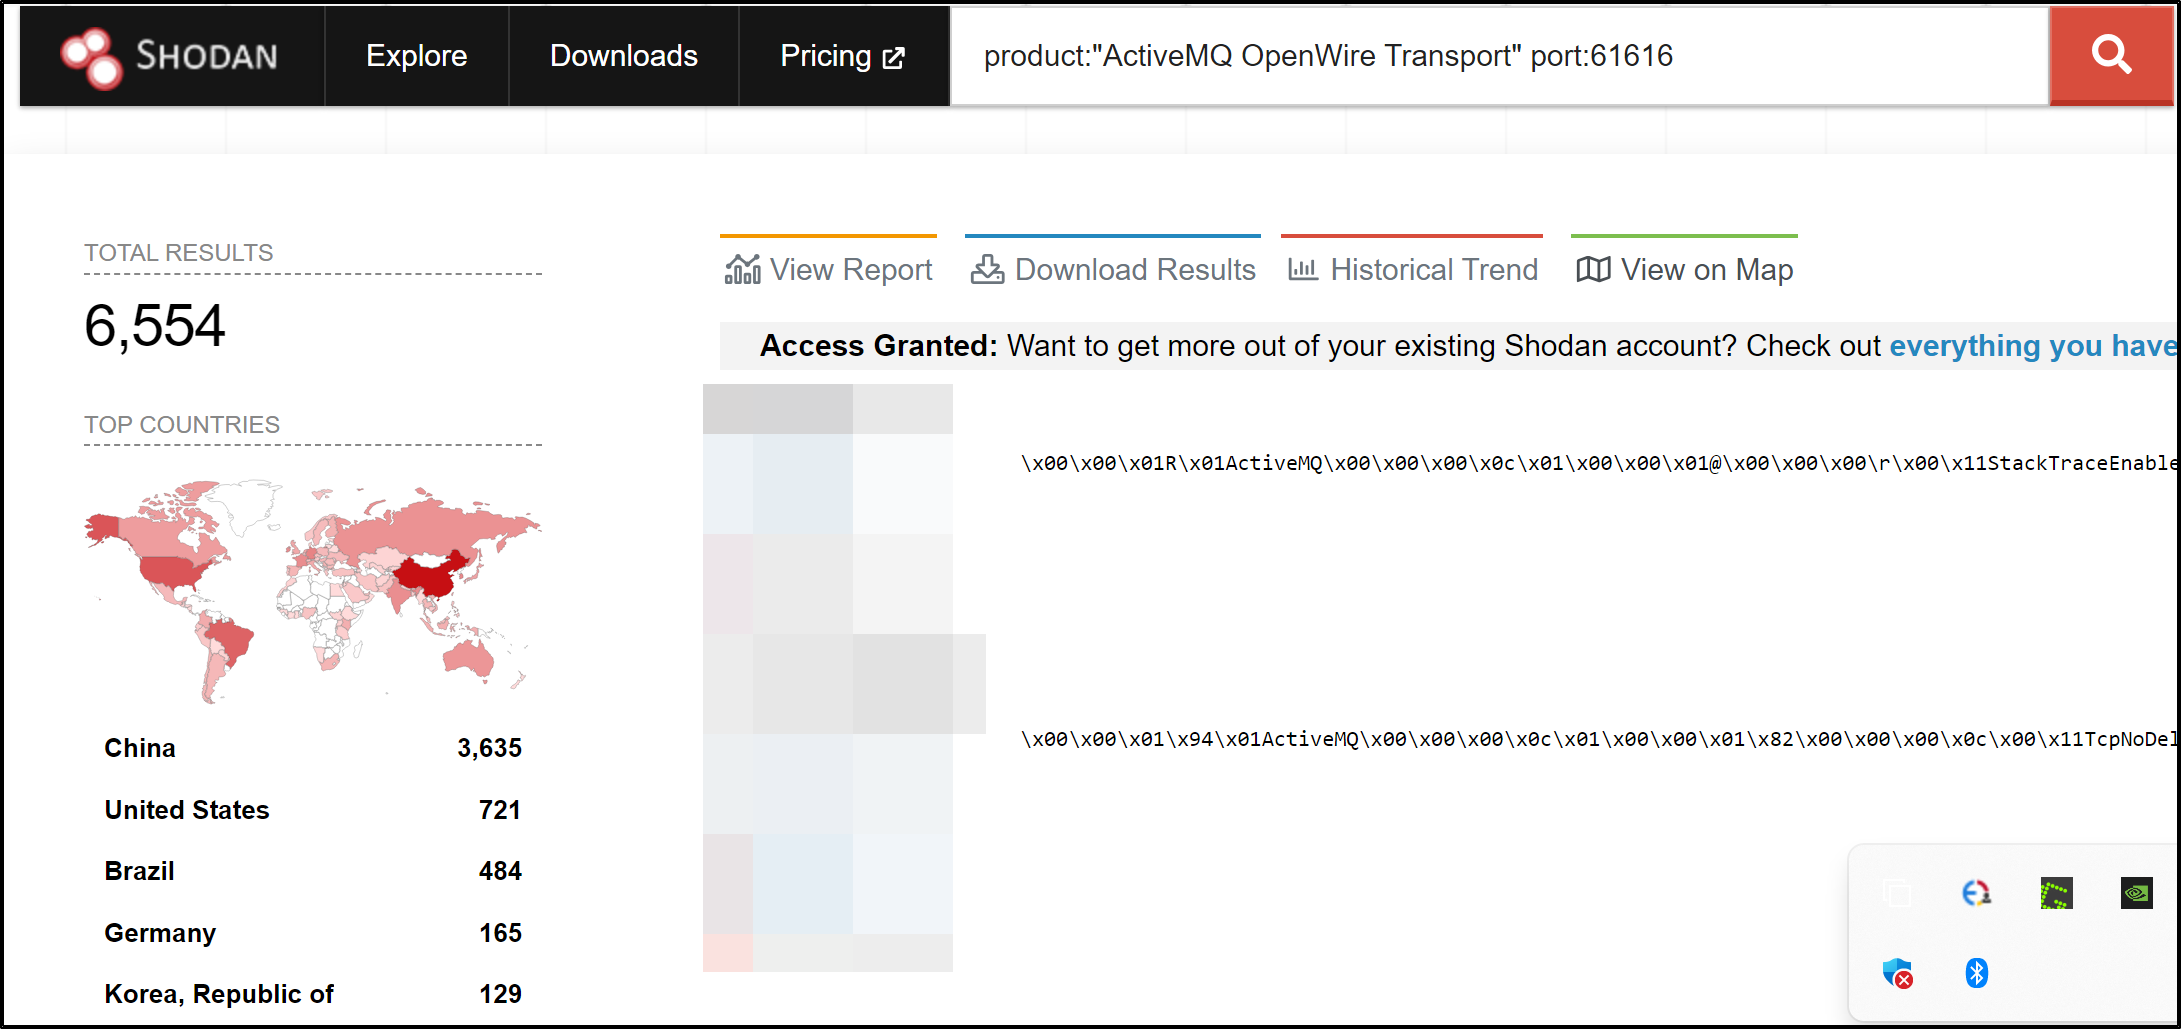 saumyajeetdas/cve-2023-46604-rce-reverse-shell-apache-activemq
Achieving a Reverse Shell Exploit for Apache ActiveMQ (CVE_2023-46604)
 nccgroup/fenrir
PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 casp3r0x0/cve-2026-34159
0 Click RCE exploit for CVE-2026-34159 Lama.cpp RPC server
 osman1337-security/cve-2025-54100
Proof-of-concept for CVE-2025-54100: XSS in PowerShell's Invoke-WebRequest via mshtml.HTMLDocumentClass, enabling remote code execution when curling…
 sanjindedic/fuguhub-8.4-authenticated-rce-cve-2024-27697
Arbitrary Code Execution on FuguHub 8.4
 w4fz5uck5/cve-2019-19781-citrixrce
Citrix Unauthorized Remote Code Execution Attacker - CVE-2019-19781
 gitcollect/jboss-autopwn
Automated JBoss exploitation script deploying JSP shells with bind/reverse shell, Meterpreter, and VNC support for penetration testing.
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
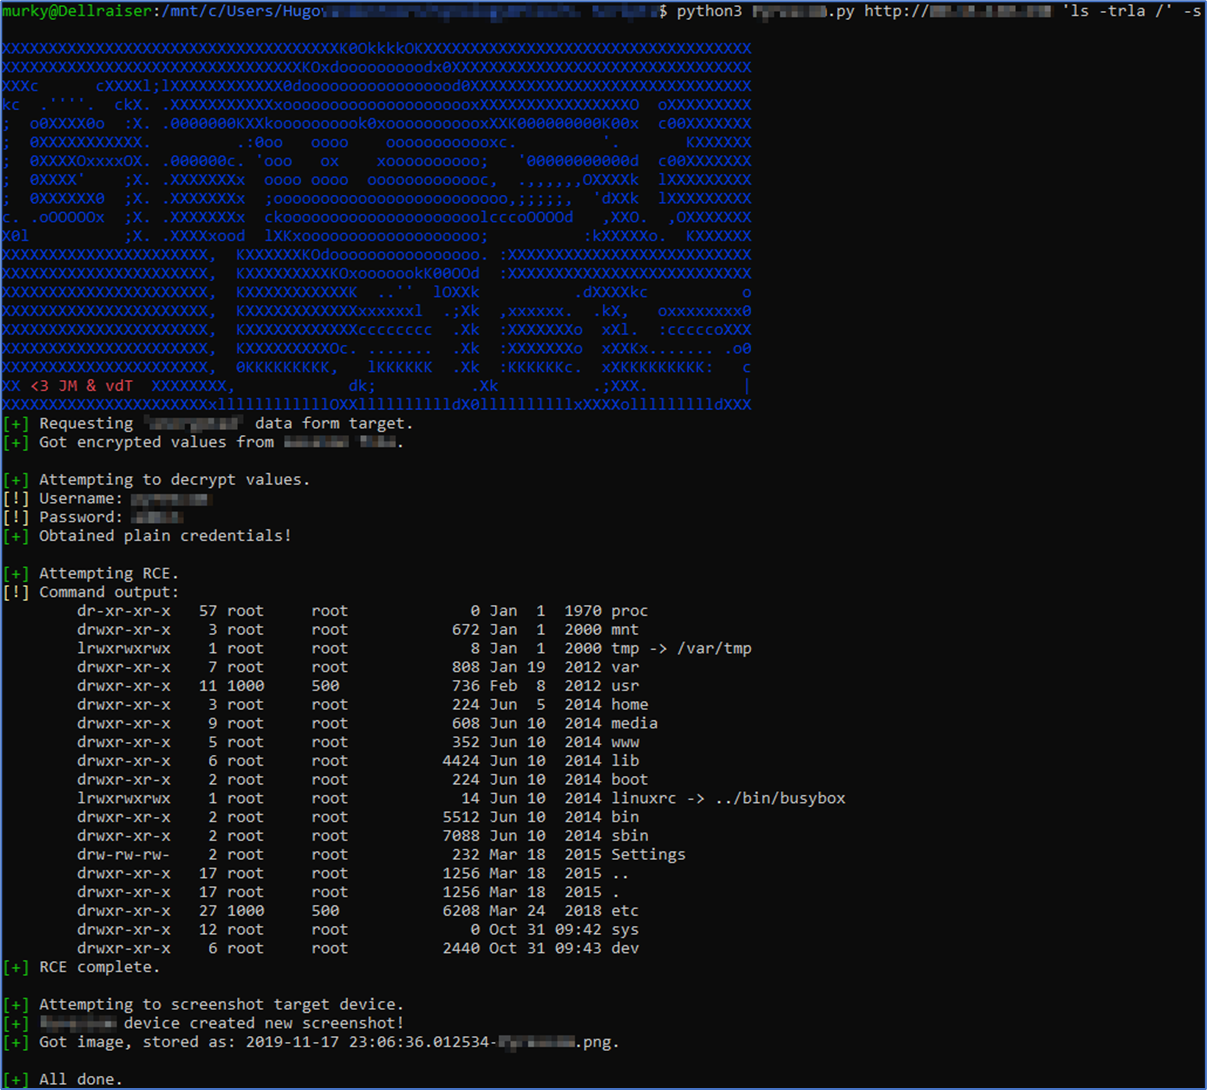 outpost24/pyrescom-termod-poc
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162
 junnythemarksman/cve-2023-38646
Python exploit for Metabase pre-authentication remote code execution (CVE-2023-38646) with reverse shell payload delivery.