
WAREED-DNS-C2
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
command-and-controlids-ips-evasionpayload-development+3
148
faisal-p27/wareed-dns-c2DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 nullsection/chisel-ng
Chisel new generation, written in rust. SSH under WSS with some customization.
 azurit/modsecurity-backdoor
This is a proof-of-concept of malicious software running inside of ModSecurity WAF.
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 synchancybersecurity/crimson-cloak-ish-wrapper-ios-
Wrapper to maximize ISH iOS app capabilities without jailbreak
 rumochnaya/openssh-cve-2024-6387.sh
openssh-cve-2024-6387.sh
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 0xtriboulet/revenant
Revenant - A 3rd party agent for Havoc that demonstrates evasion techniques in the context of a C2 framework
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
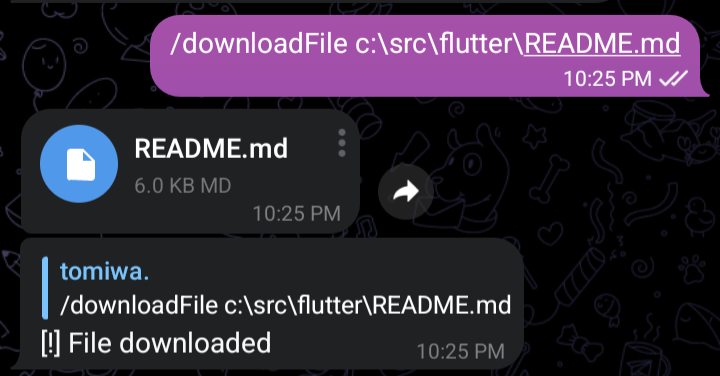 tomiwa-ot/telegram-c2
Control a system remotely via telegram
 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
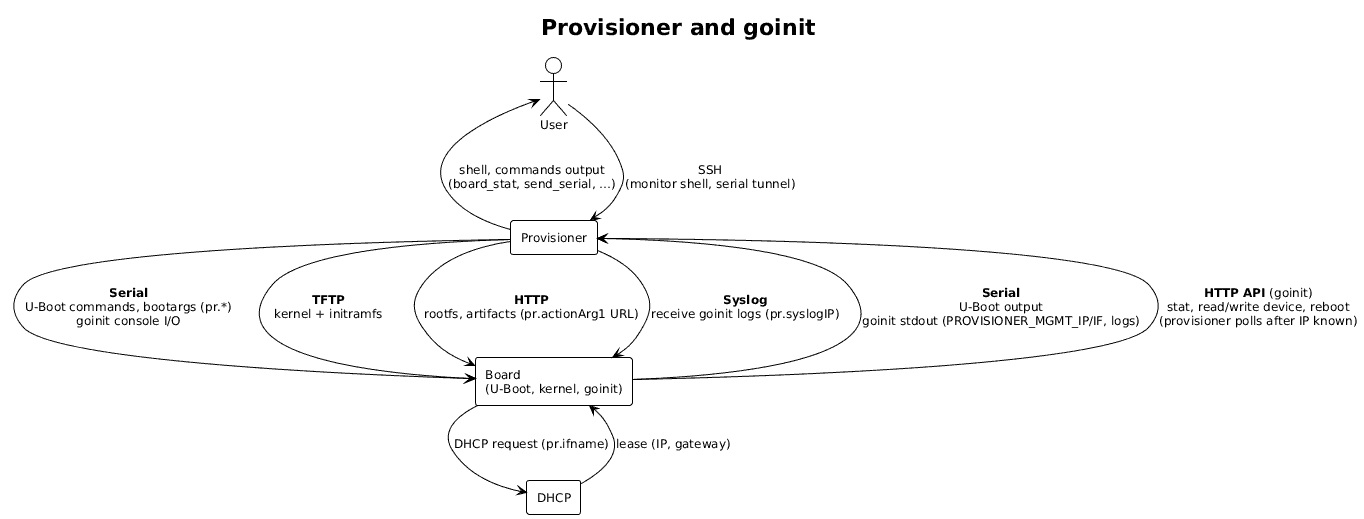 alessandrocarminati/provisioner
Provisioning and sharing system for SBCs
 boydhacks/dameflare
Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges
 barry-mccockiner/cve-2019-0708
A remote code execution vulnerability exists in Remote Desktop Services – formerly known as Terminal Services – when an unauthenticated attacker…
 shadowbyte1/cve-2024-53345
Critical 0 Day in Car Rental Management System Versions 1.0 - 1.3
 identity-threat-labs/article-regresshion-cve-2024-6387
Technical analysis and documentation of CVE-2024-6387, a critical remote code execution vulnerability in OpenSSH, detailing exploitation vectors and…
 fredagsguf/windows-cve-2024-38063
Exploit for CVE-2024-38063, a critical RCE in Windows TCP/IP stack via crafted IPv6 packets, enabling arbitrary code execution and system compromise.