
Auto-PostXploit
 behzadmagzer/auto-postxploit
Windows Auto Post Exploitation - For ReD Team
information-gatheringpenetration-testingpost-exploitation+1
16
behzadmagzer/auto-postxploitWindows Auto Post Exploitation - For ReD Team
 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 thegeekht/loki.rat
Loki.Rat is a fork of the Ares RAT, it integrates new modules, like recording , lockscreen , and locate options. Loki.Rat is a Python Remote Access…
 kljunowsky/cve-2024-27348
Proof-of-concept exploit for unauthenticated remote code execution in Apache HugeGraph Server via Groovy injection. Supports single and multi-target…
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 sxlmnwb/cve-2024-6387
Targeting a signal handler race condition in OpenSSH's server (sshd) on glibc-based Linux systems.
 0x00-0x00/cve-2016-2098
Exploits Ruby on Rails Action Pack remote code execution (CVE-2016-2098) by abusing unrestricted render() to run arbitrary shell commands through a…
 7etsuo/cve-2024-6387-poc
a signal handler race condition in OpenSSH's server (sshd)
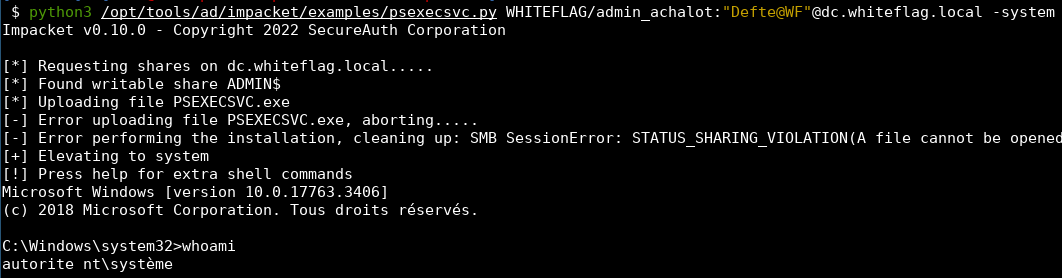 sensepost/susinternals
psexecsvc - a python implementation of PSExec's native service implementation
 yassdev221608/cve-2024-6387_poc
Scans and exploits CVE-2024-6387 (regreSSHion) in OpenSSH servers. Features multi-threaded scanning, banner retrieval, grace time detection, and…
 0xblackash/cve-2026-24061
CVE-2026-24061
 bigbroke/cve-2021-21985
Multiple vulnerabilities in the vSphere Client (HTML5) were privately reported to VMware. Updates and workarounds are available to address these…
 mvrozanti/rat-via-telegram
Windows Remote Administration Tool via Telegram
 jscamposx/hack
Repositorio de investigación de seguridad que contiene una Prueba de Concepto (PoC) para la vulnerabilidad CVE-2021-4034 (PwnKit) y utilidades de…
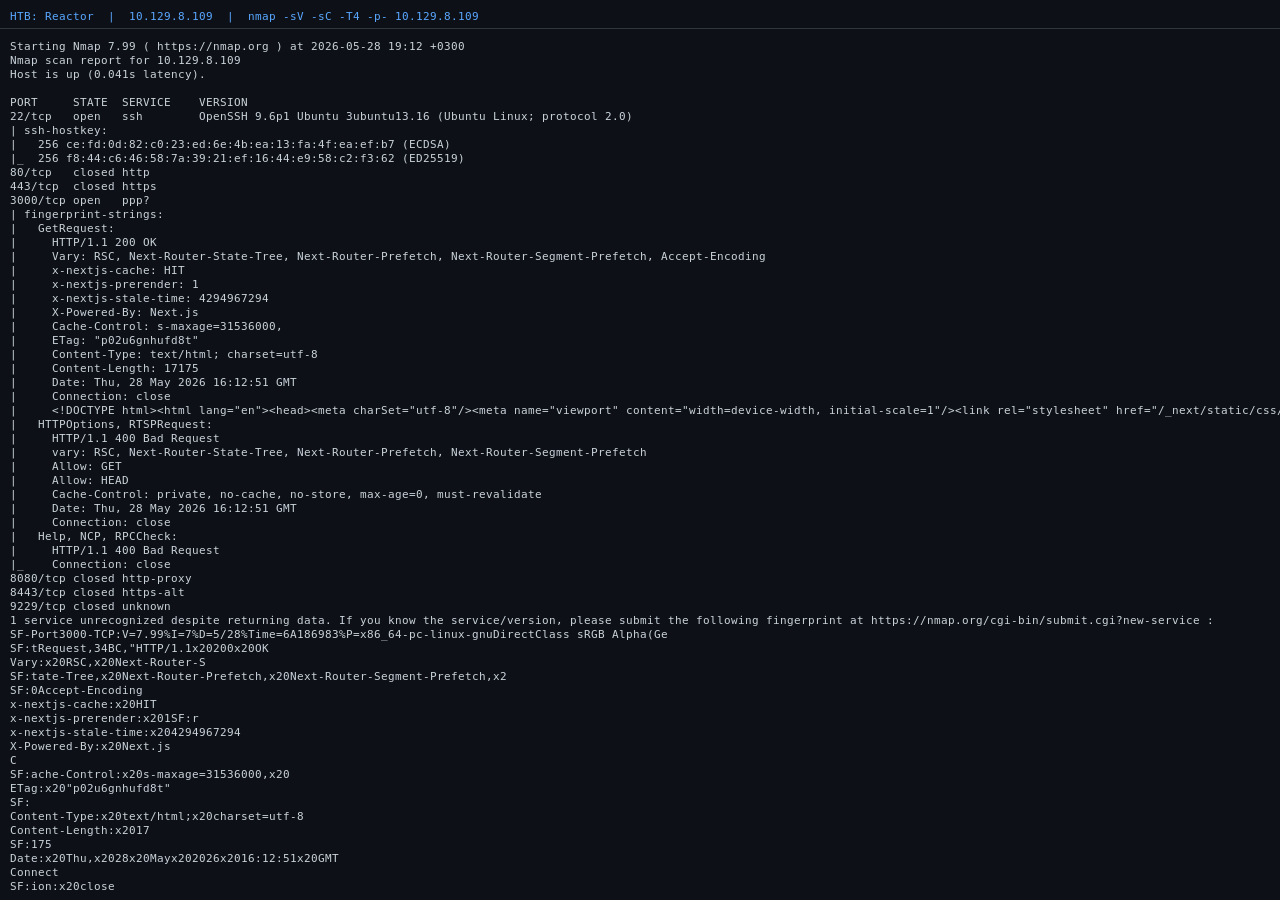 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 entysec/ghost
Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.
 ultrasecurity/telekiller
A Tools Session Hijacking And Stealer Local Passcode Telegram Windows
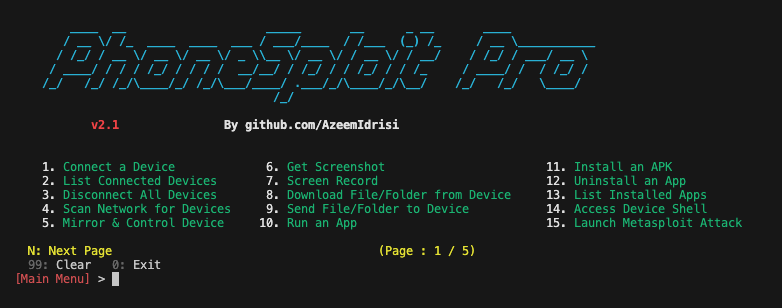 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.