

Koi
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
27
b3rt1ng/koiMulti-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 garvitv14/cve-2025-59287
Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 hackerhouse-opensource/offensivelua
Offensive Lua.
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 nccgroup/phantap
Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
 nccgroup/socksoverrdp
Socks5/4/4a Proxy support for Remote Desktop Protocol / Terminal Services / Citrix / XenApp / XenDesktop
 azurit/modsecurity-backdoor
This is a proof-of-concept of malicious software running inside of ModSecurity WAF.
 lnxg33k/webhandler
Bash simulator to control a server using PHP system functions.
 advancedhacker101/android-c-sharp-rat-server
This is a plugin for the c# R.A.T server providing extension to android based phone systems
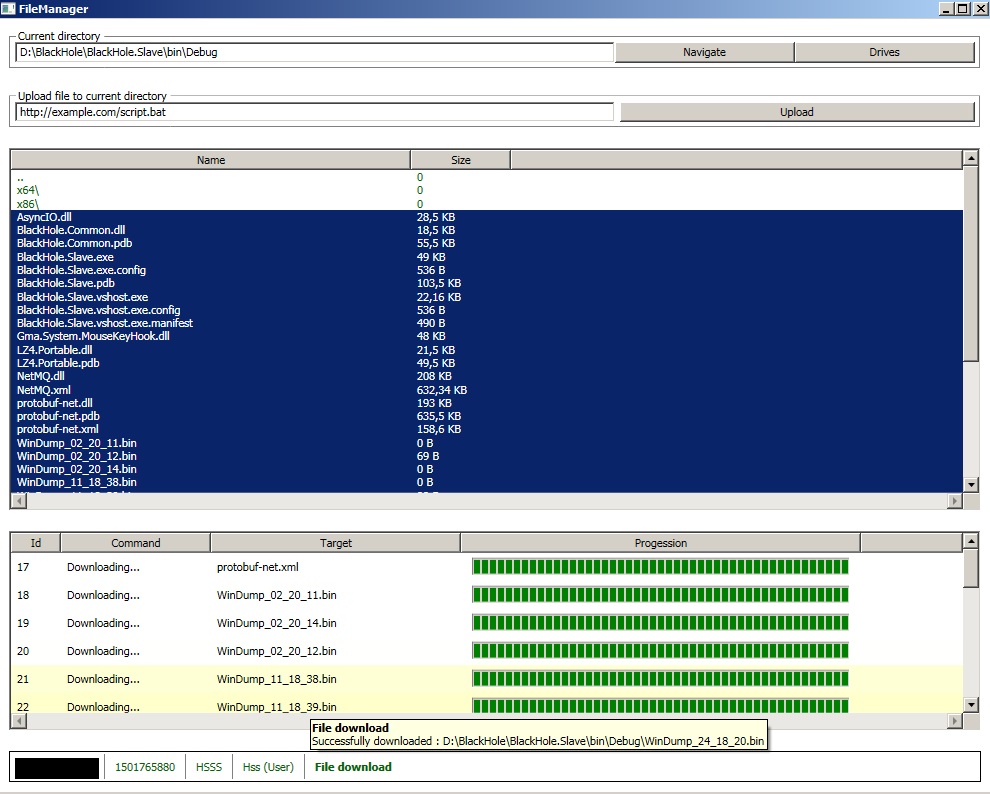 hussein-aitlahcen/blackhole
C# RAT (Remote Administration Tool)
 rumochnaya/openssh-cve-2024-6387.sh
openssh-cve-2024-6387.sh
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…
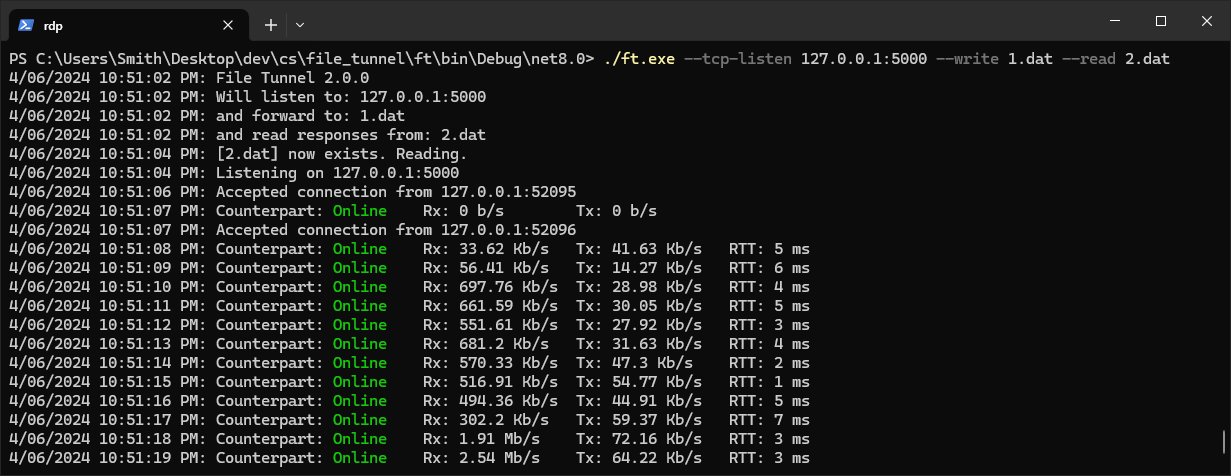 fiddyschmitt/file-tunnel
Tunnel TCP connections through a file
 mrterrestrial/cve-2023-50564
This script exploits the file upload feature in Pluck CMS v4.7.18 to upload a malicious PHP file, enabling remote access via a reverse shell. Once…
 mchoudhary15/cve-2022-22029-nfs-server-
Proof-of-concept exploit for CVE-2022-22029, a Windows NFS remote code execution vulnerability. Includes PowerShell commands to disable NFSV3 as a…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…