
gonc
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
command-and-controldata-exfiltrationencryption-decryption-tools+6
734
threatexpert/goncNetcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
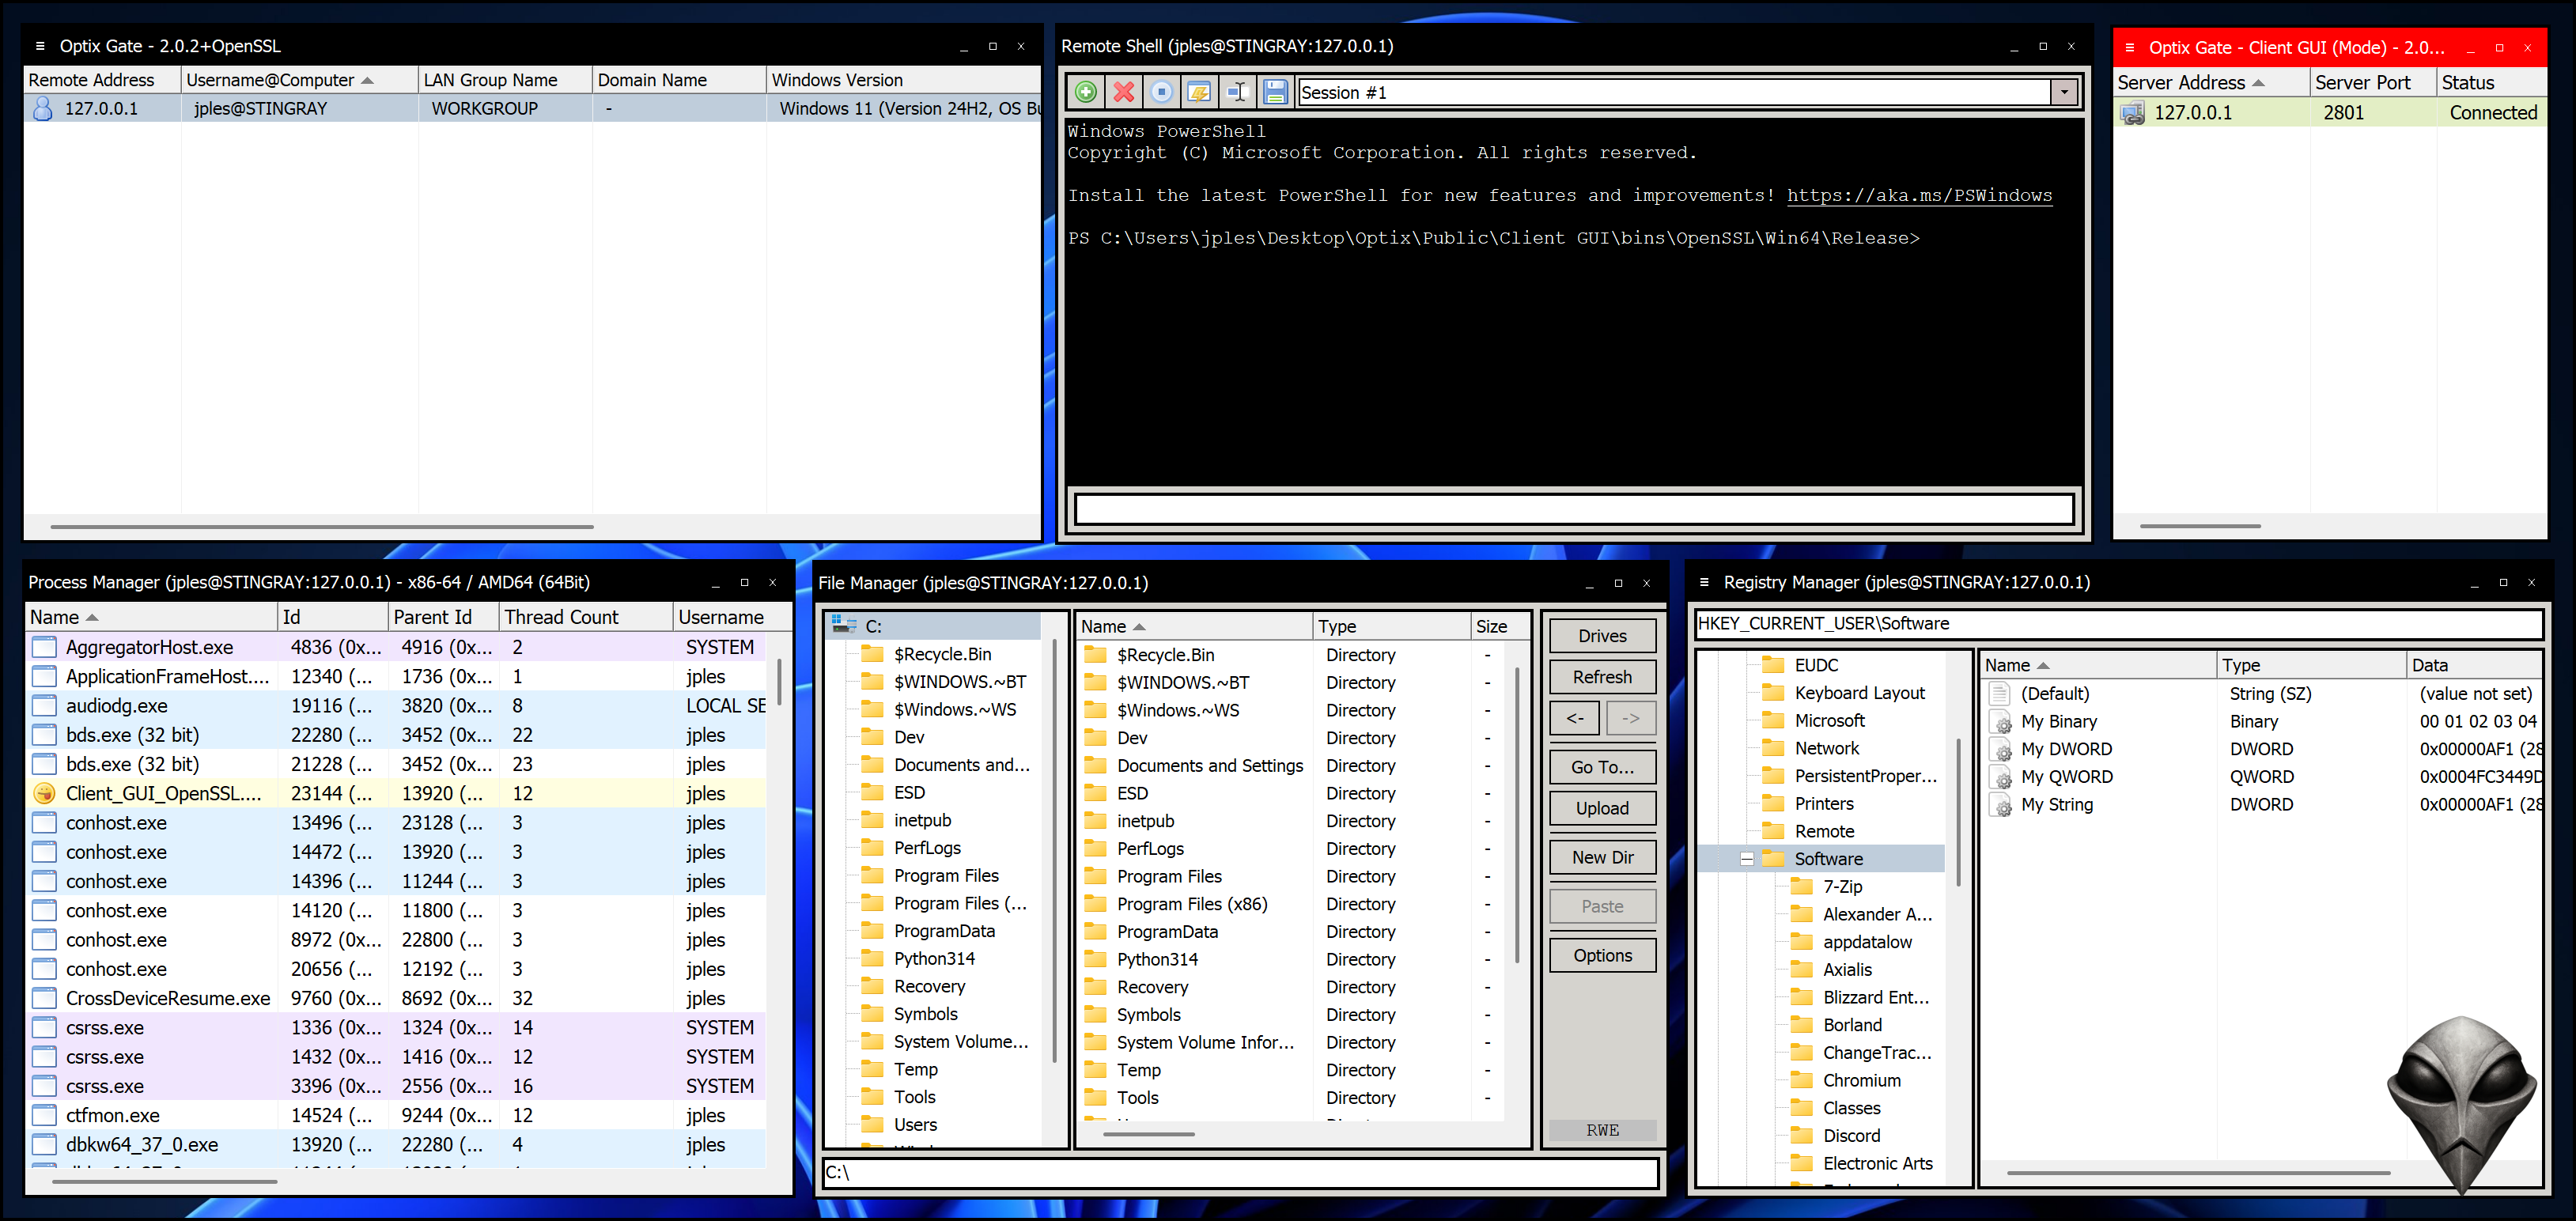 darkcodersc/optixgate
Open-source multi-purpose remote access tool for Microsoft Windows
 openssh/openssh-portable
Portable OpenSSH
 richlegrand/bitbang-cli
Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…
 openvpn/openvpn
Secure tunneling daemon implementing VPN protocols with TLS encryption, certificate authentication, and routing/firewall configuration for private…
 androvirus/blacknet
Free advanced and modern Windows botnet with a nice and secure PHP panel developed using VB.NET.
 bytedz/pclink
Cross-platform desktop app for secure remote PC control and management, featuring a lightweight built-in WebUI and API for local or remote access.
 nyan-x-cat/asyncrat-c-sharp
Open-Source Remote Administration Tool For Windows C# (RAT)
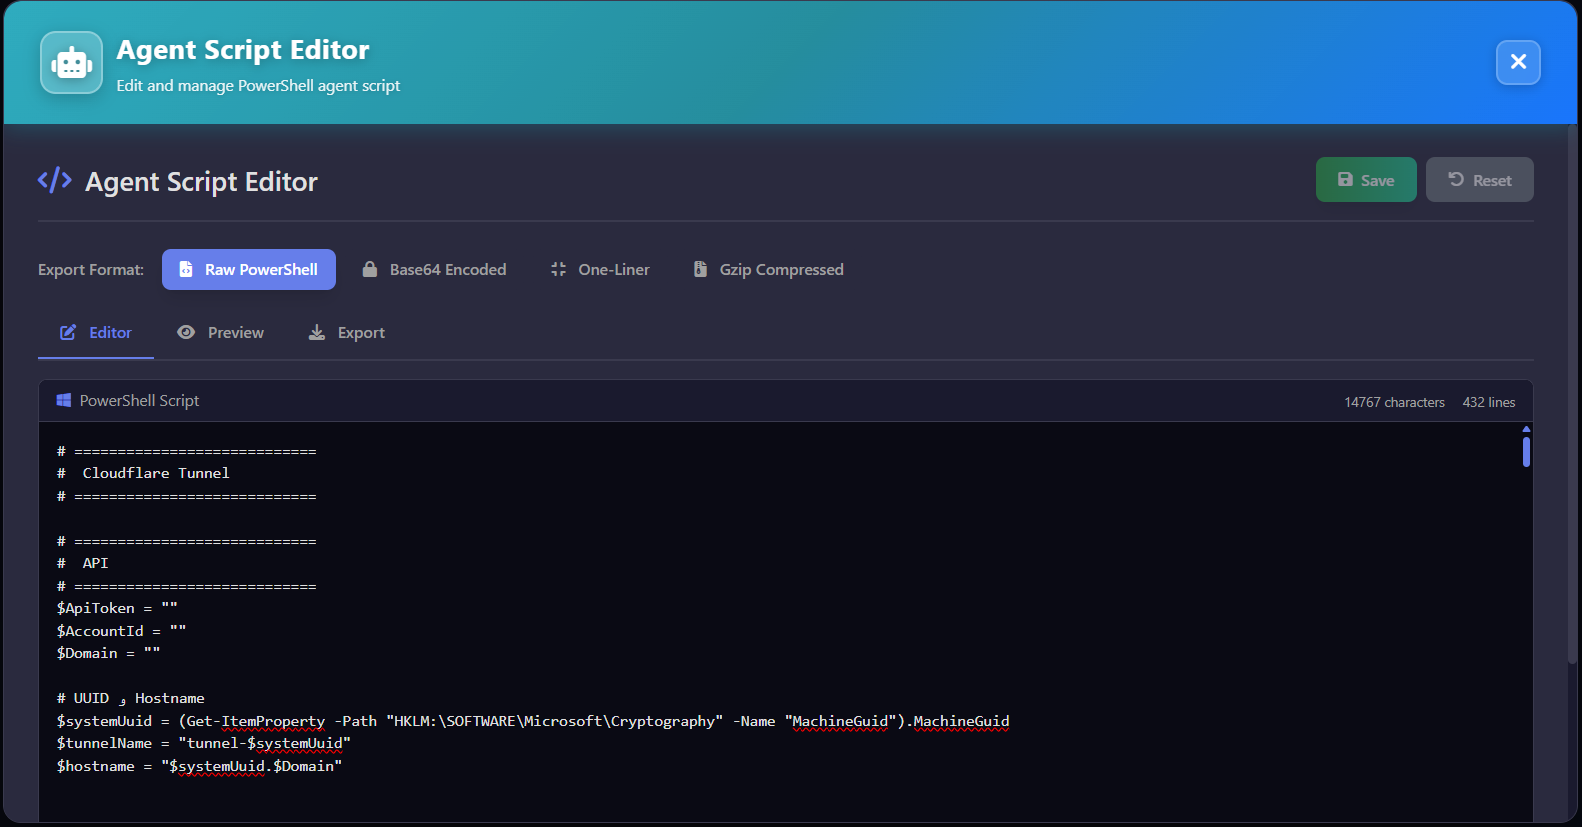 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 padsalatushal/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
 pwniel/ivanti_shell
CVE-2024-21887 Exploitation with Ngrok Reverse Shell
 lynk4/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 sfewer-r7/cve-2025-22457
PoC for CVE-2025-22457 - A remote unauthenticated stack based buffer overflow affecting Ivanti Connect Secure, Pulse Connect Secure, Ivanti Policy…
 saruman9/cve_2025_20265
PoC for CVE-2025-20265 Cisco Secure FMC Software RADIUS Remote Code Execution Vulnerability
 watchtowrlabs/cve-2025-0282
Ivanti Connect Secure IFT TLS Stack Overflow pre-auth RCE (CVE-2025-0282)
 sfewer-r7/cve-2025-0282
PoC for CVE-2025-0282: A remote unauthenticated stack based buffer overflow affecting Ivanti Connect Secure, Ivanti Policy Secure, and Ivanti Neurons…