
CVE-2026-86218
 super-meuw/cve-2026-86218
Python 3 proof-of-concept exploit for CVE-2026-86218, a pre-auth RCE in N-able N-central via a Struts multipart race condition, with command…
exploitationpayload-developmentpenetration-testing+5
super-meuw/cve-2026-86218Python 3 proof-of-concept exploit for CVE-2026-86218, a pre-auth RCE in N-able N-central via a Struts multipart race condition, with command…
 abraxas/cve-2026-18937
Proof-of-concept exploit and lab reproduction pack for CVE-2026-18937, an unauthenticated RCE in the Broken Link Checker WordPress plugin before…
 abraxas/cve-2026-77991
Proof-of-concept and lab pack for CVE-2026-77991, a privileged PHP file-write RCE in Joomla Event Manager through 5.0.0, with Docker lab and witness…
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
 darkpills/cve-2021-24307-all-in-one-seo-pack-admin-rce
Proof-of-concept exploit for CVE-2021-24307, an authenticated admin RCE in All in One SEO Pack <= 4.1.0.1 via PHP unserialization, enabling arbitrary…
 yassdev221608/cve-2024-6387_poc
Scans and exploits CVE-2024-6387 (regreSSHion) in OpenSSH servers. Features multi-threaded scanning, banner retrieval, grace time detection, and…
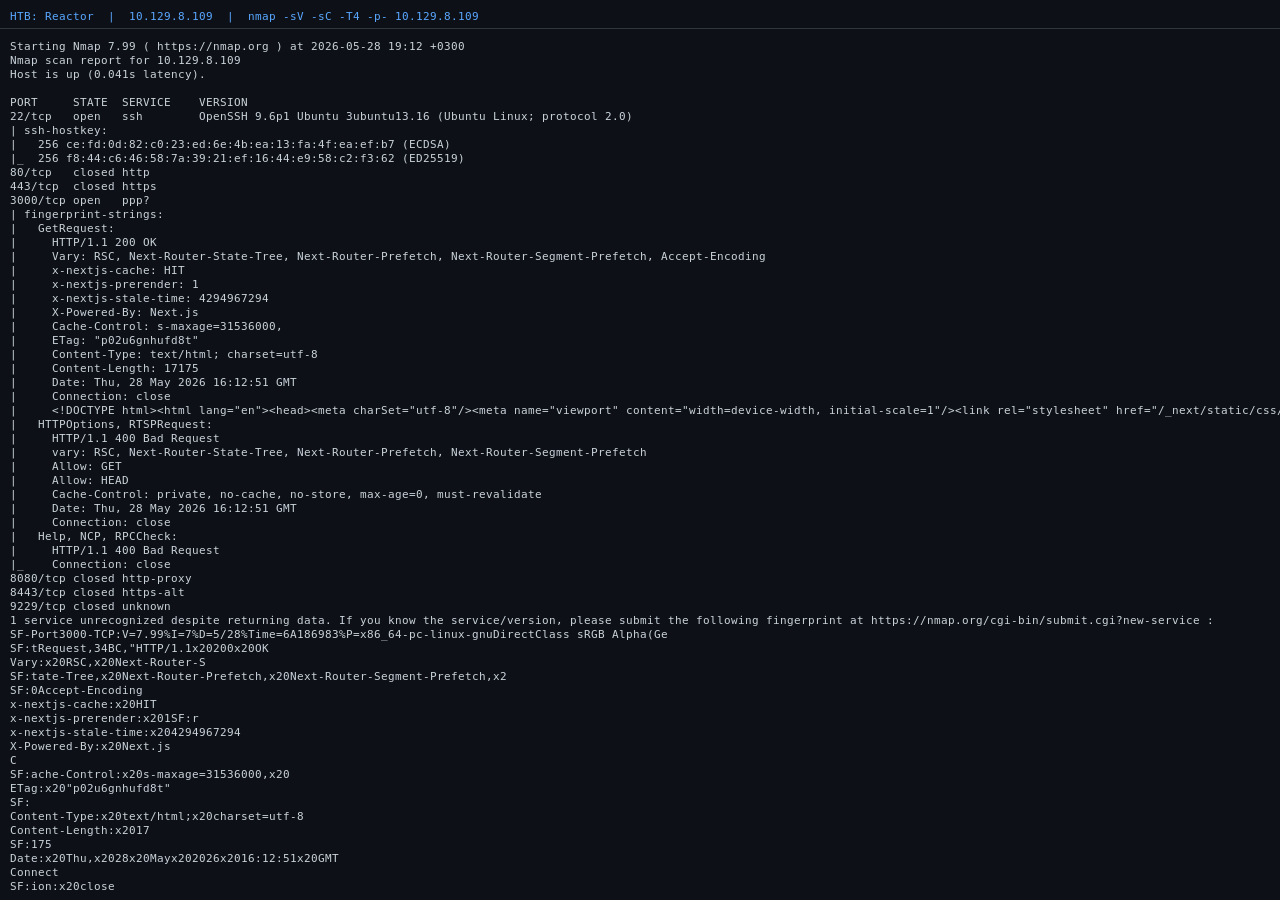 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
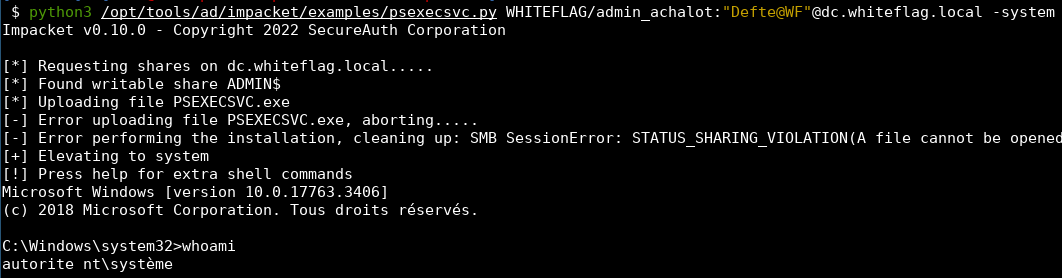 sensepost/susinternals
psexecsvc - a python implementation of PSExec's native service implementation
 thegeekht/loki.rat
Loki.Rat is a fork of the Ares RAT, it integrates new modules, like recording , lockscreen , and locate options. Loki.Rat is a Python Remote Access…
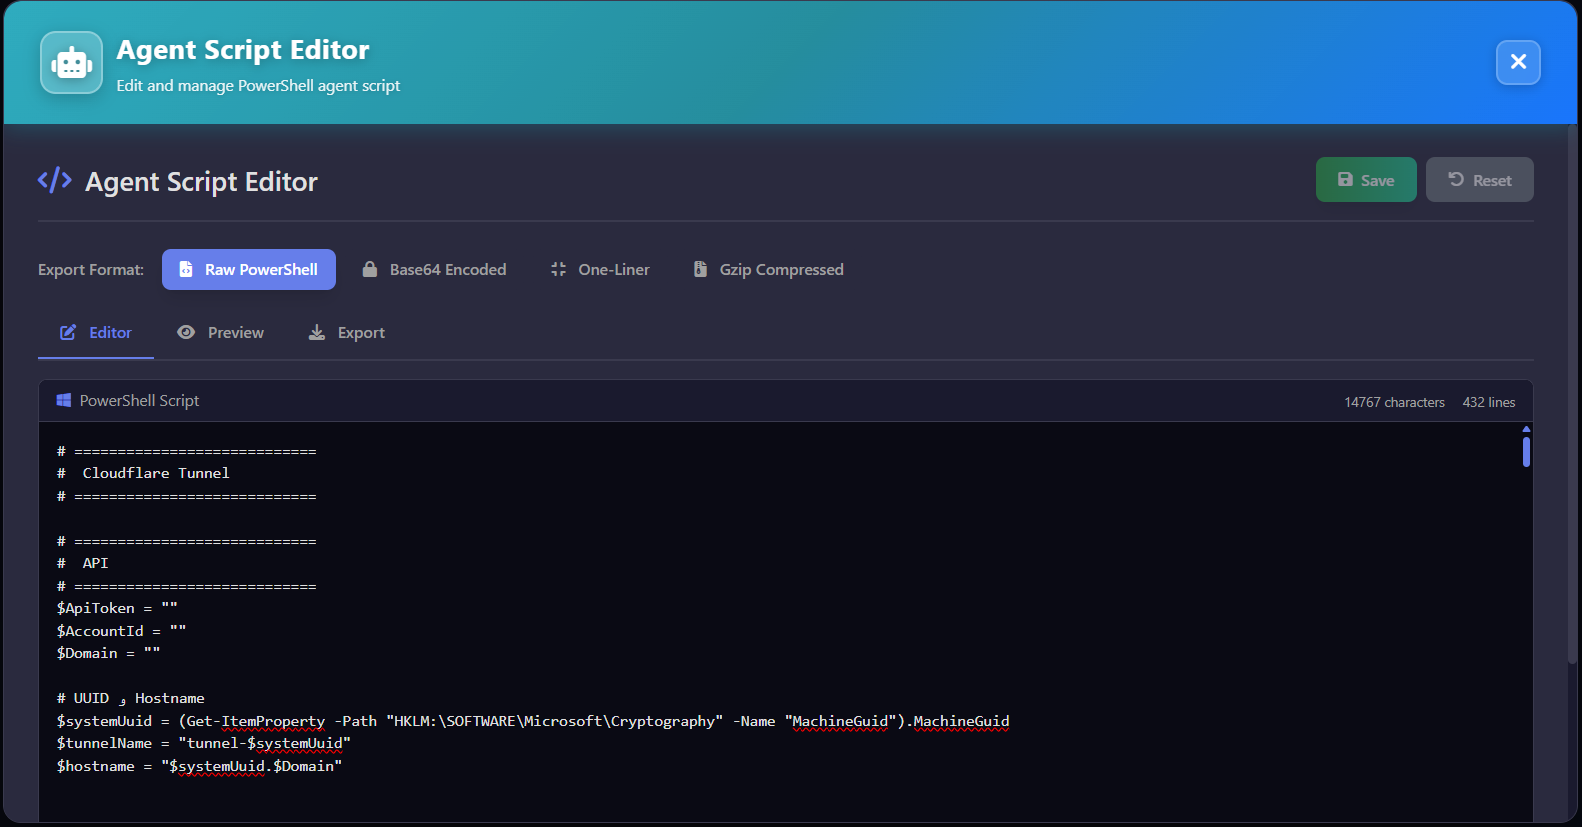 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 acrono/cve-2024-6387-poc
32-bit PoC for CVE-2024-6387 — mirror of the original 7etsuo/cve-2024-6387-poc
 prelearn-code/cve-2024-6387
Proof-of-concept exploit for CVE-2024-6387 (regreSSHion) targeting unauthenticated remote code execution in OpenSSH server via signal handler race…
 kre80r/webmin_cve-2019-12840_poc
A standalone POC for CVE-2019-12840
 lflare/cve-2024-6387-poc
MIRROR of the original 32-bit PoC for CVE-2024-6387 "regreSSHion" by 7etsuo/cve-2024-6387-poc
 t3rry327/cve-2024-6387-poc
Exploit for CVE-2024-6387 targeting a signal handler race condition in OpenSSH sshd on glibc-based Linux systems, enabling remote code execution as…
 dimamend/cve-2024-6387-poc
Exploit for CVE-2024-6387, a signal handler race condition in OpenSSH sshd, enabling remote code execution as root on glibc-based Linux systems.
 sxlmnwb/cve-2024-6387
Targeting a signal handler race condition in OpenSSH's server (sshd) on glibc-based Linux systems.
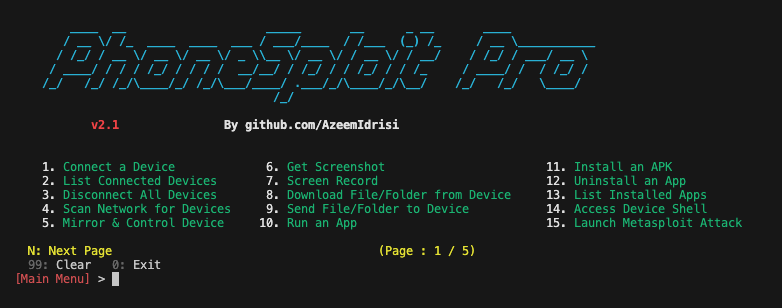 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.