
reactshell
 h4r335hr/reactshell
Interactive shell client for React Server Components RCE exploitation via __proto__ pollution (CVE-2025-55182)
exploitationpayload-generationpenetration-testing+2
h4r335hr/reactshellInteractive shell client for React Server Components RCE exploitation via __proto__ pollution (CVE-2025-55182)
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 hackedteam/rcs-db
Database components for RCS backend
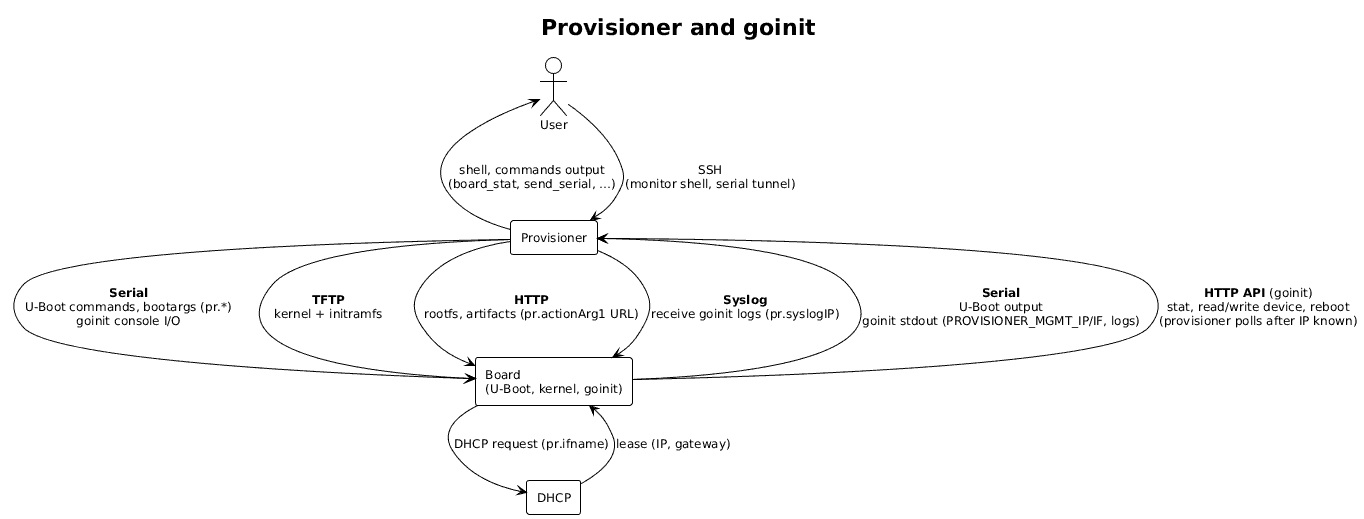 alessandrocarminati/provisioner
Provisioning and sharing system for SBCs
 chitoz1300/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182
 cyanitol/netgear-telenetenable
Telenet Enable for Netgear routers from svn checkout http://netgear-telnetenable.googlecode.com/svn/trunk/ netgear-telnetenable-read-only
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
 fullspectrumdev/rancidcrisco
Proof-of-concept exploit for CVE-2023-20126 targeting Cisco SPA phone adapters. Uploads malicious firmware to gain a root shell on port 23000/tcp via…
 r3vpwnx/cve-2025-55182
Standalone exploit for CVE-2025-55182 achieving unauthenticated RCE in Next.js App Router via React Server Components Flight deserialization, with…
 alyaapm/cve-2025-55182-shellinteractive
Interactive shell for exploiting CVE-2025-55182 in React Server Components, enabling remote command execution, file transfer, and vulnerability…
 mooowu/cve-2025-55182-poc
Lab environment and PoC exploit for CVE-2025-55182 (React2Shell), a critical RCE vulnerability in React Server Components. Includes vulnerable app,…
 shadowroot97/react2shell-cve-2025-55182
POC React2Shell-CVE-2025-55182
 khadafigans/react2shell
React2Shell - CVE-2025-66478 RCE Exploit
 carlosaruy/cve-2025-55182
a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…
 spiralbl0ck/bios-stuff-related-programming
Final OBJECTIVE:BIOS ROOTKIT AND RSHELL USING BIOS NETWORKING STACK
 yanoshercohen/react2shell_cve-2025-55182
React2Shell (CVE-2025-55182) Exploit
 ihsansencan/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182
 snawoot/hisilicon-dvr-telnet
PoC materials for article https://habr.com/en/post/486856/