
Archived
AhMyth-Android-RAT
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
android-securitycommand-and-controlpayload-generation+3
5.3k
ahmyth/ahmyth-android-ratAndroid Remote Administration Tool
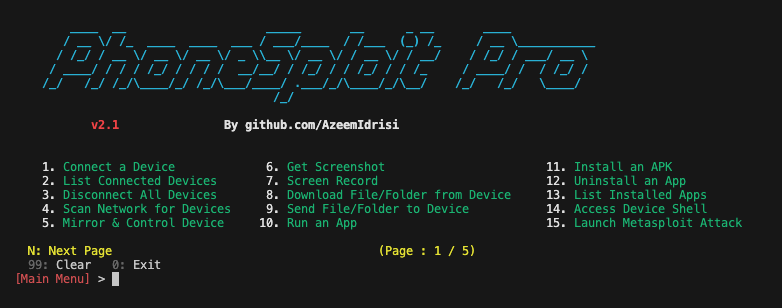 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 alphaseclab/awesome-rat
RAT And C&C Resources. 250+ Open Source Projects, 1200+ RAT/C&C blog/video.
 darthton/blackbone
Windows memory hacking library
 entysec/ghost
Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
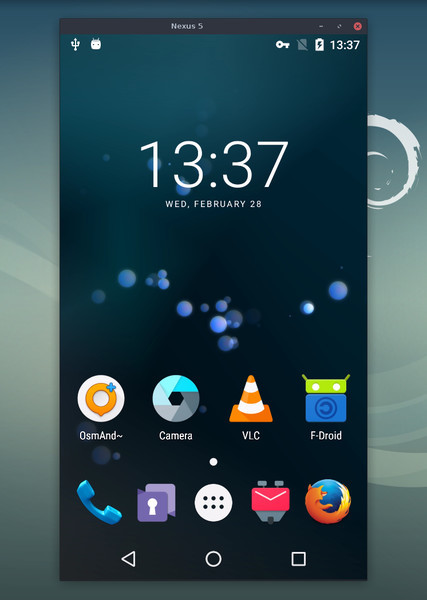 genymobile/scrcpy
Display and control your Android device

 lawndoc/mediator
An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
 tharana/android-vulnerability-exploitation
Google Android - 'Stagefright' Remote Code Execution - CVE-2015-1538
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 ireshchaminda1/android-privilege-escalation-remote-access-vulnerability-cve-2015-1805
AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…