
mouseserver-exploit
 lypd0/mouseserver-exploit
Mobile Mouse 3.6.0.4 - Remote Code Execution - CVE-2023-31902
exploitationpenetration-testingred-teaming+1
3
lypd0/mouseserver-exploitMobile Mouse 3.6.0.4 - Remote Code Execution - CVE-2023-31902
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 filipkarc/poc-ubuntutouch-pin-privesc
CVE-2022-40297 - Proof of Concept: Privilege escalation in Ubuntu Touch 16.04 - by PIN Bruteforce
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

 designativedave/androrat
Remote Administration Tool for Android devices
 androidmalware/android_hid
Use Android as Rubber Ducky against another Android device
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
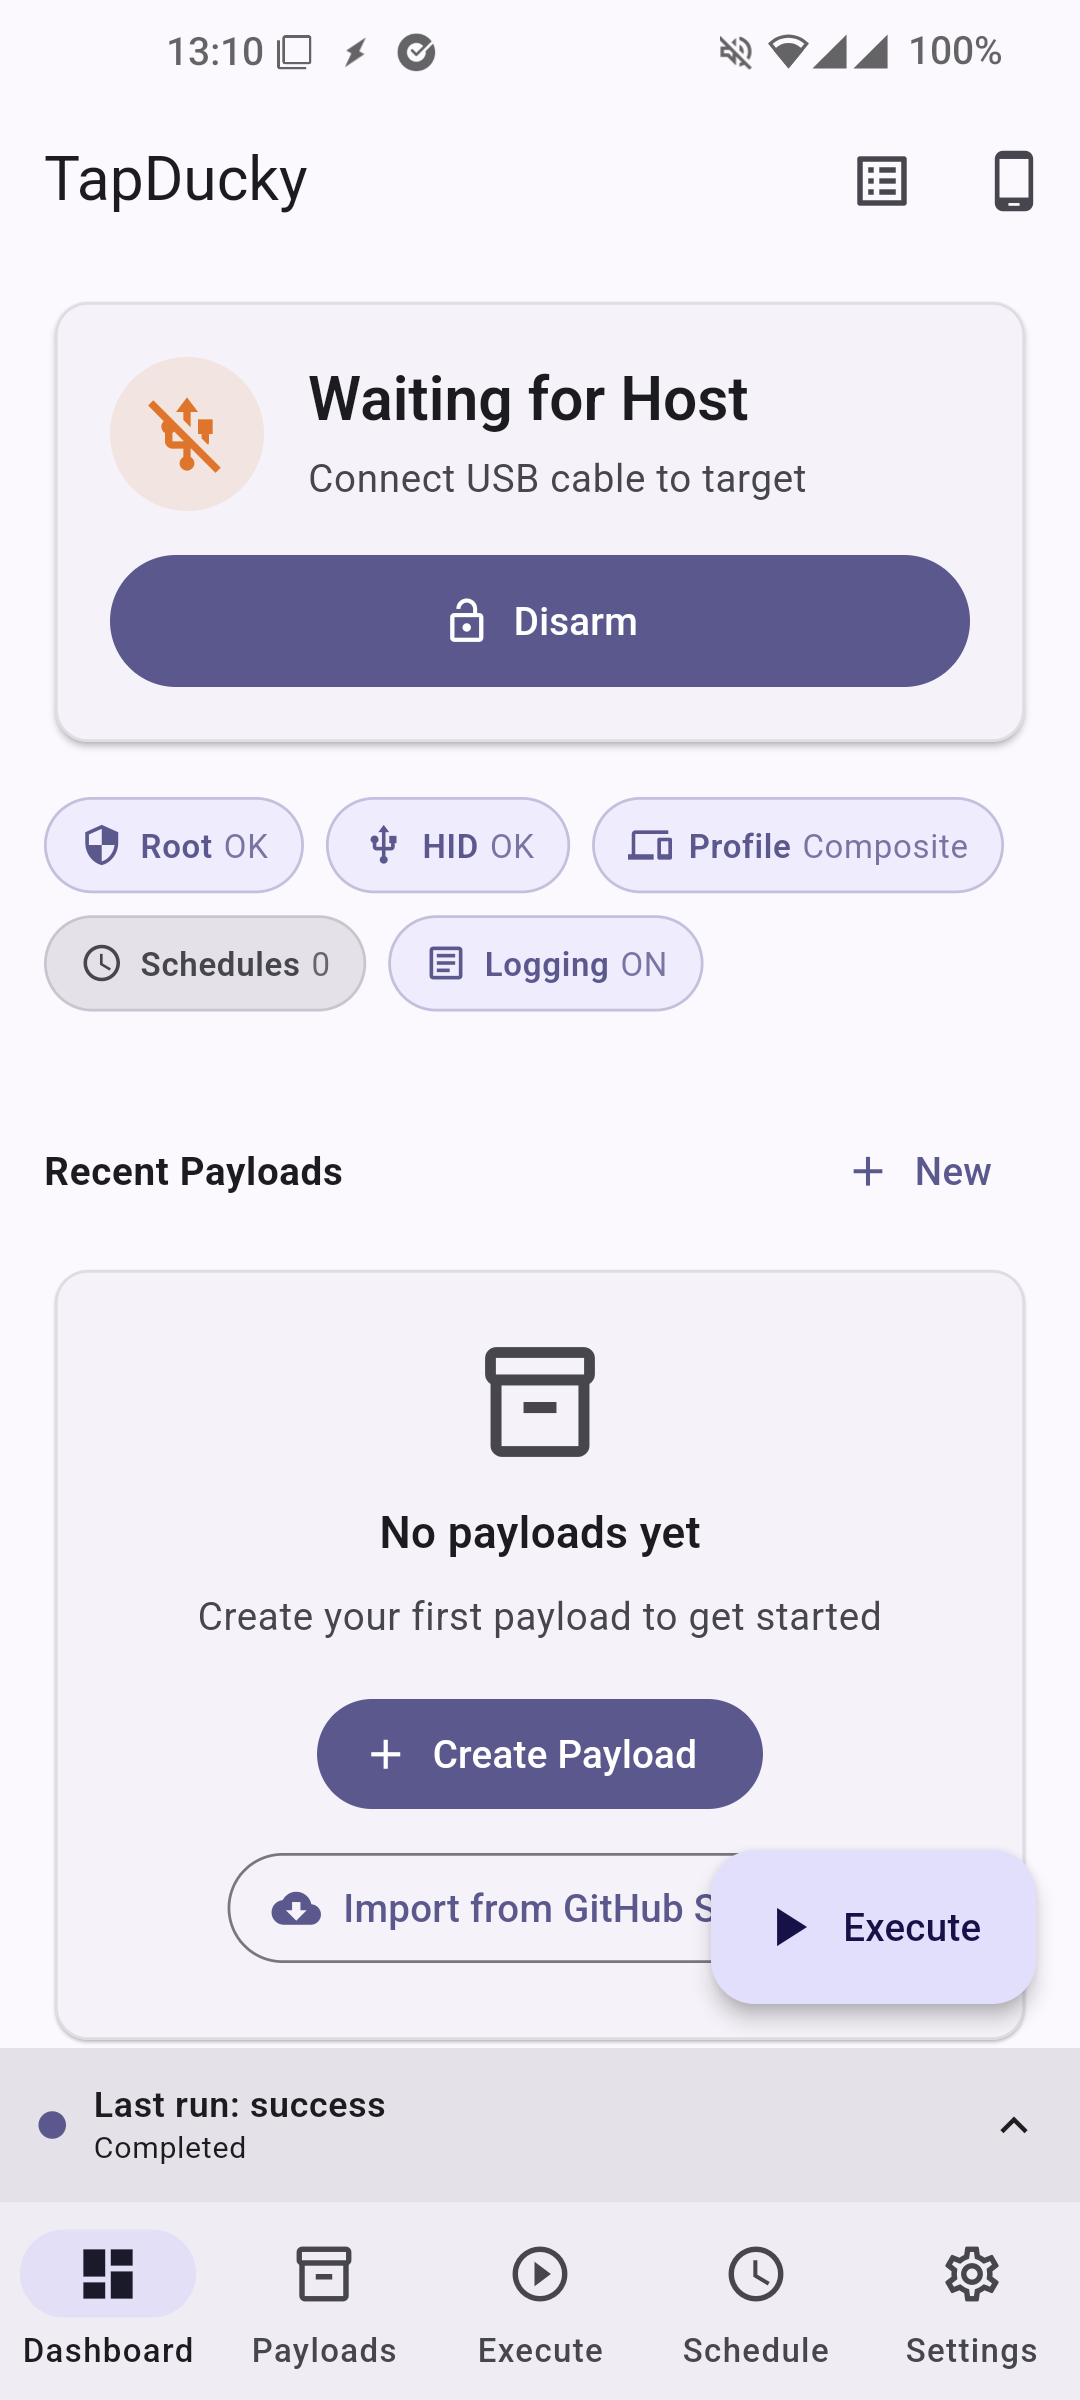 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 busung-dev/cve-2026-43499-s25u
Standalone CVE-2026-43499 PoC for Galaxy S25 Ultra SM-S938N S938NKSUACZF1
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 geekben/towelroot
Research of CVE-2014-3153 and its famous exploit towelroot on x86