CVE-2026-41089-Netlogon-RCE-PoC

Proof-of-concept exploit for CVE-2026-41089, a Netlogon remote code execution vulnerability in Windows Active Directory environments, for security…

Proof-of-concept exploit for CVE-2026-41089, a Netlogon remote code execution vulnerability in Windows Active Directory environments, for security…

TUI-based Active Directory data collector that ingests LDAP objects, performs remote RPC/SMB/HTTP collection, and generates BloodHound CE-compatible…

Python exploit tool for CVE-2022-29464, enabling unrestricted file upload and remote code execution on vulnerable WSO2 products via directory…

SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…

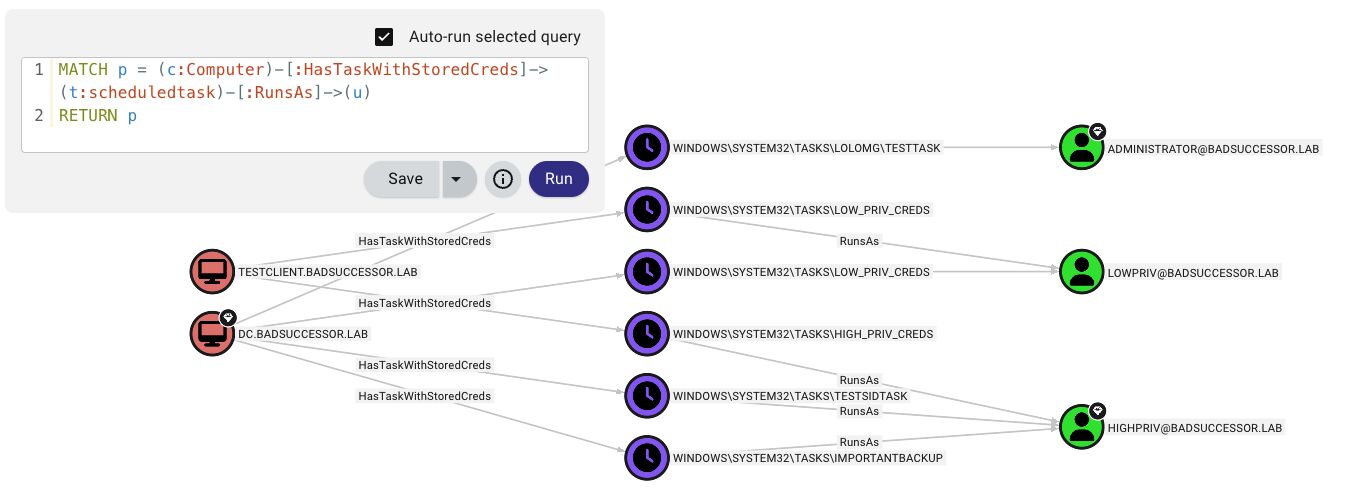
Tool to enumerate privileged Scheduled Tasks on Remote Systems

Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…

A script to automate keystrokes through a graphical desktop program.

Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…

Attack and defend active directory using modern post exploitation adversary tradecraft activity

Attack Graph Visualizer and Explorer (Active Directory) ...Who's *really* Domain Admin?

Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…

PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…

Powershell tool to automate Active Directory enumeration.

Gets plaintext Active Directory credentials if you're on the internal network but outside the AD environment

Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.

Post-exploitation tool for identifying, profiling, and attacking Microsoft SCCM assets within Active Directory domains, streamlining credential…

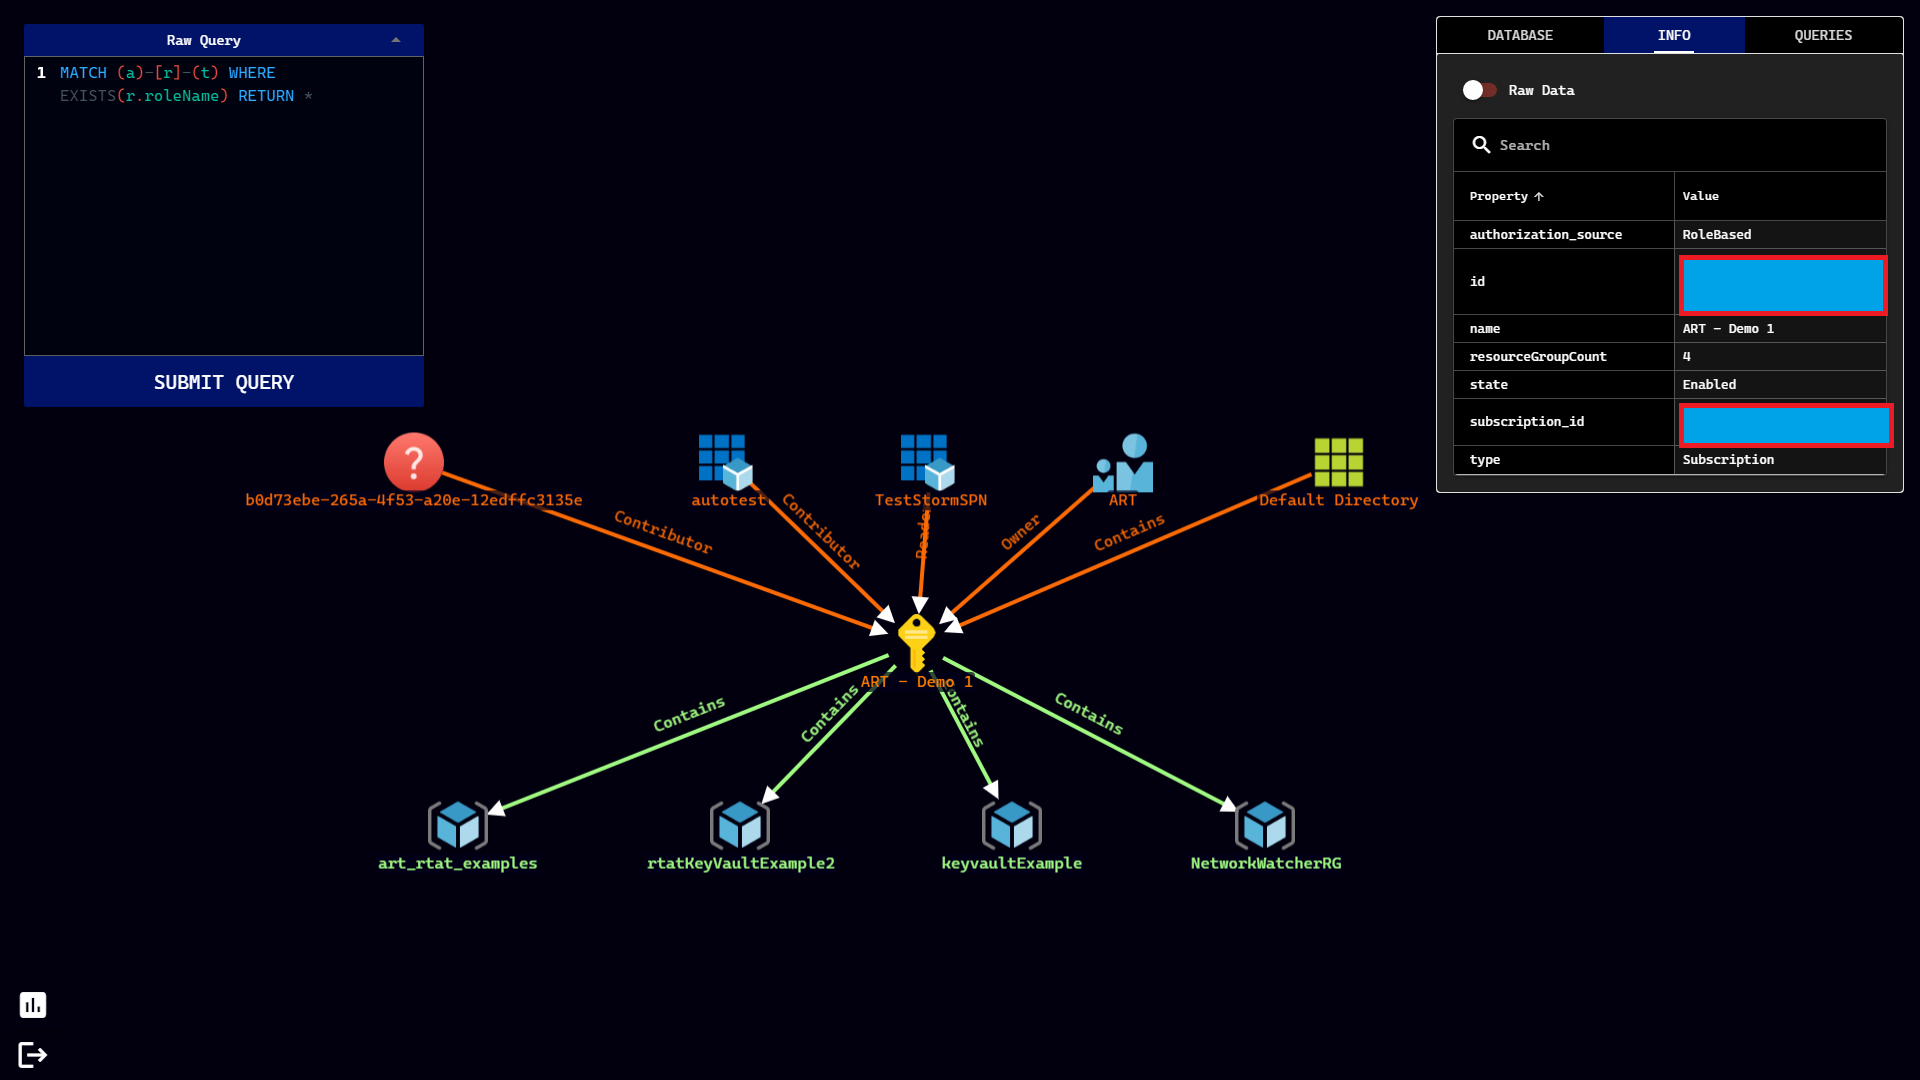
Azure Red Team tool for graphing Azure and Azure Active Directory objects

AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…