
POC-CVE-2026-23520
 augmaster/poc-cve-2026-23520
Proof-of-concept exploit for CVE-2026-23520, an authenticated RCE in Arcane Docker management via OS command injection in lifecycle labels. Includes…
educationexploitationpenetration-testing+3
2
augmaster/poc-cve-2026-23520Proof-of-concept exploit for CVE-2026-23520, an authenticated RCE in Arcane Docker management via OS command injection in lifecycle labels. Includes…
 copethomas/datapower-redis-rce-exploit
A POC for IBM Datapower Authenticated Redis RCE Exploit abusing the Test Message Function (CVE-2020-5014)
 toxy4ny/artaxerxes
Advanced Multi-Technology Stress Testing Framework Educational Cybersecurity Tool for High-Performance Network Testing
 realgam3/pymultitor
PyMultitor - Python Multi Threaded Tor Proxy
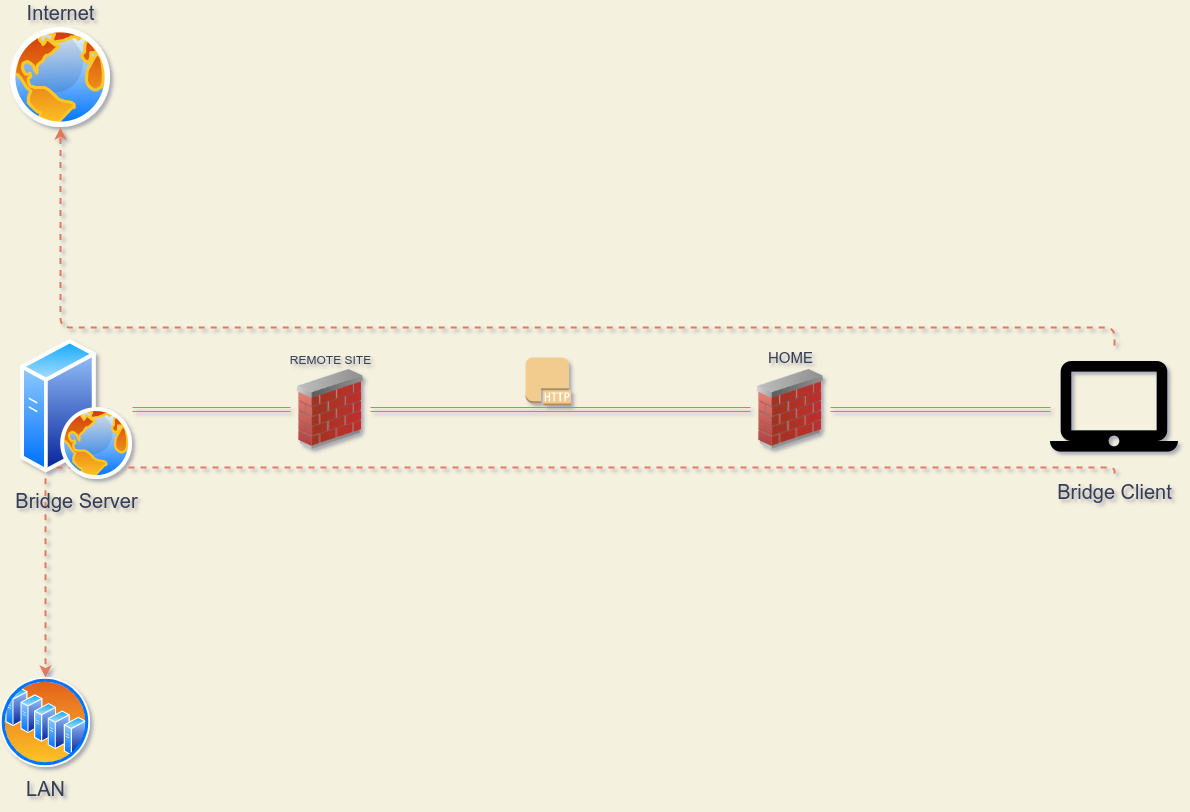 alejandro-llanes/http_bridge
SOCKS5-to-HTTP proxy bridge that tunnels arbitrary TCP streams (SSH, SMTP, TLS) through standard HTTP requests, enabling network traffic obfuscation…
 m4xsec/cve-2026-31431-rce-exploit
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…
 686f6c61/poc-aiowpm-cve-2026-19949
Reproducible Docker-based proof-of-concept for CVE-2026-19949, a second-order SQL injection in All-in-One WP Migration <= 7.109 that leaks the…
 boreas37/cve-2026-56705
PoC exploit for Adminer < 5.4.3 unauthenticated RCE via MSSQL PDO DSN injection, including Docker lab and negative test.
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…
 sastraadiwiguna-purpleeliteteaming/holistic-deconstruction-of-cve-2019-5736-
This repository provides a high-fidelity technical deconstruction and production-ready exploitation suite for CVE-2019-5736. It demonstrates how a…
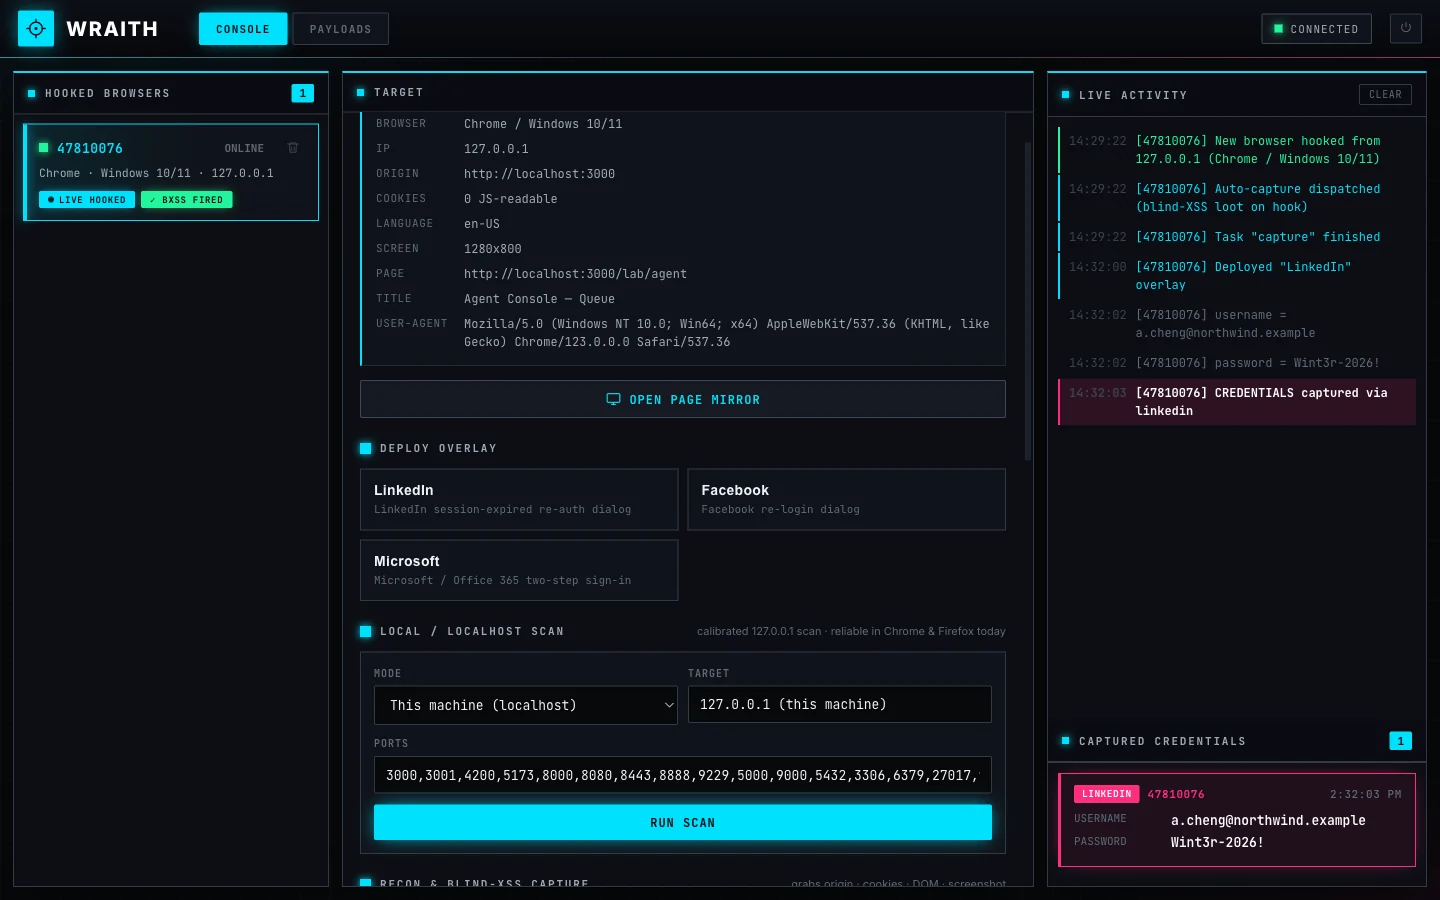 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 aleksamcode/preferred-network-list-sniffer
A reconnaissance tool for capturing and displaying SSIDs from device's Preferred Network List.
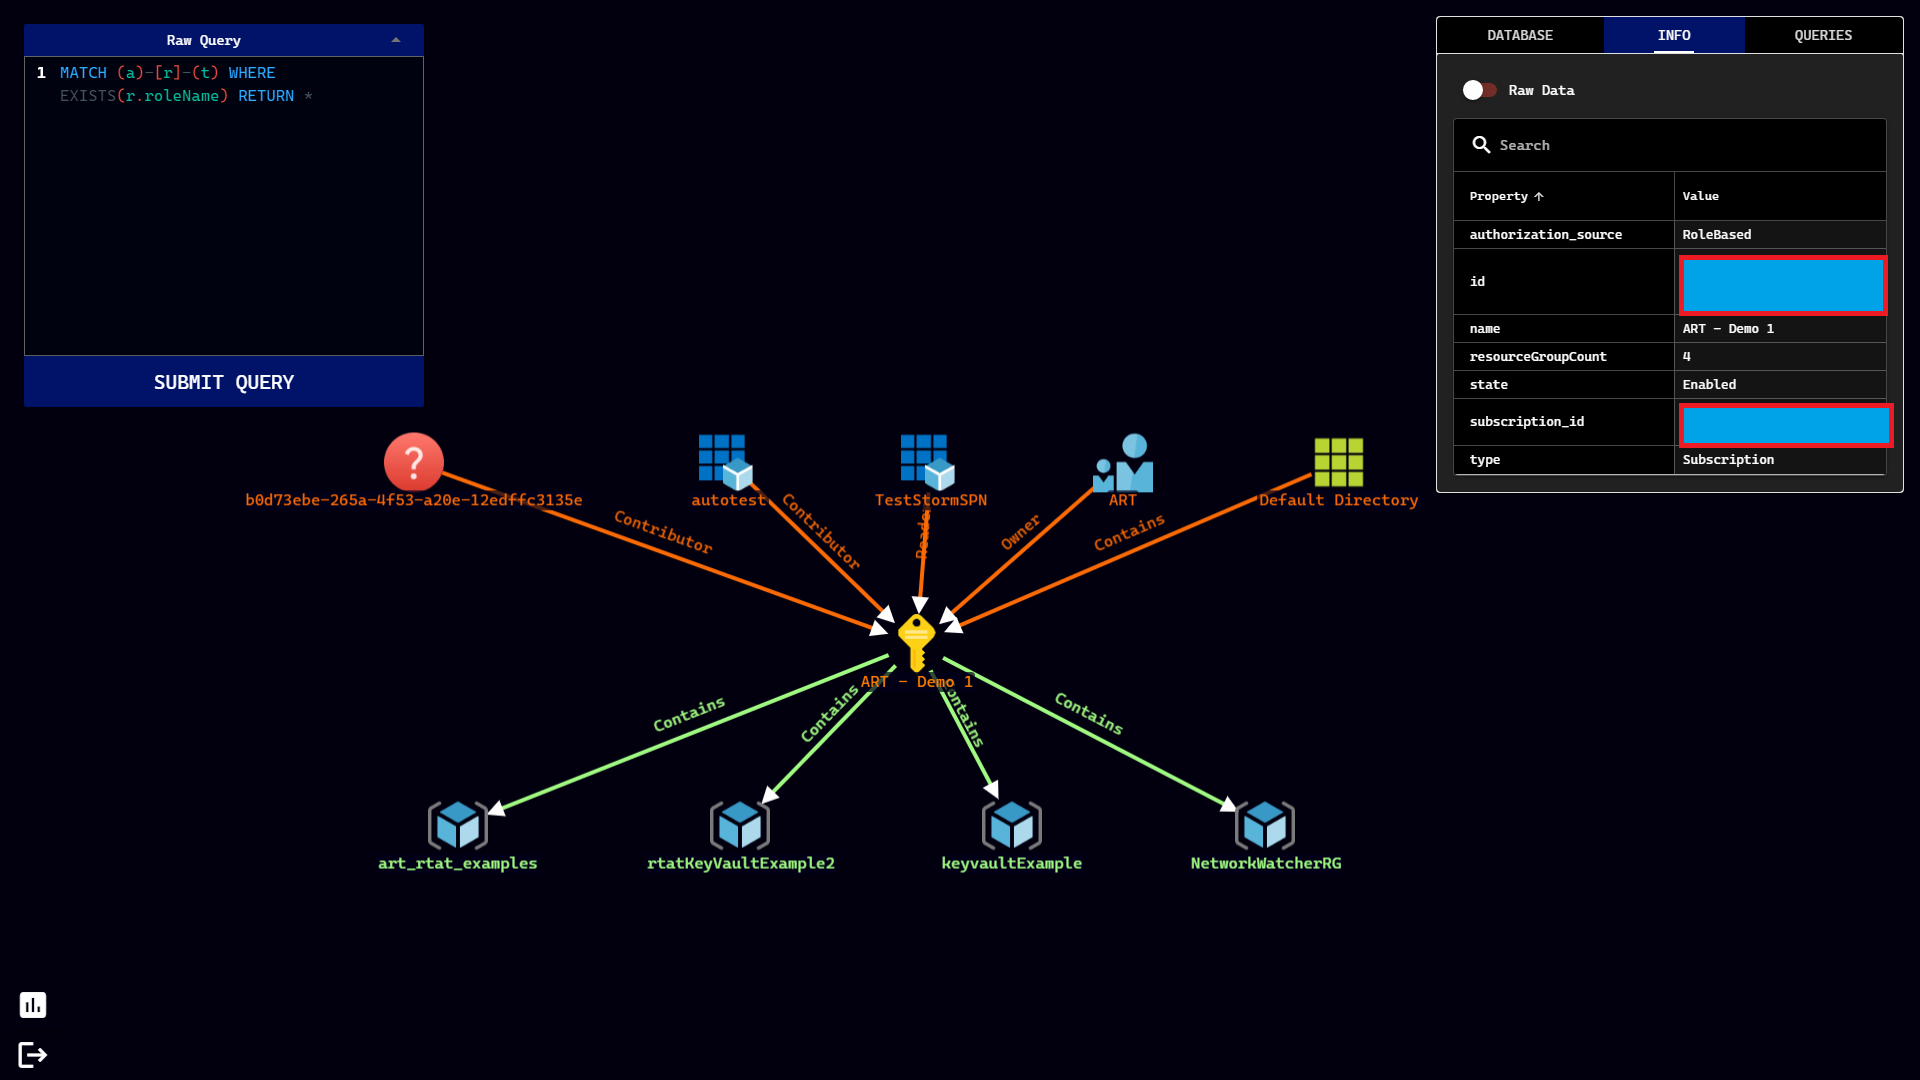 azure/stormspotter
Azure Red Team tool for graphing Azure and Azure Active Directory objects
 pumasecurity/serverless-prey
Serverless Functions for establishing Reverse Shells to Lambda, Azure Functions, and Google Cloud Functions
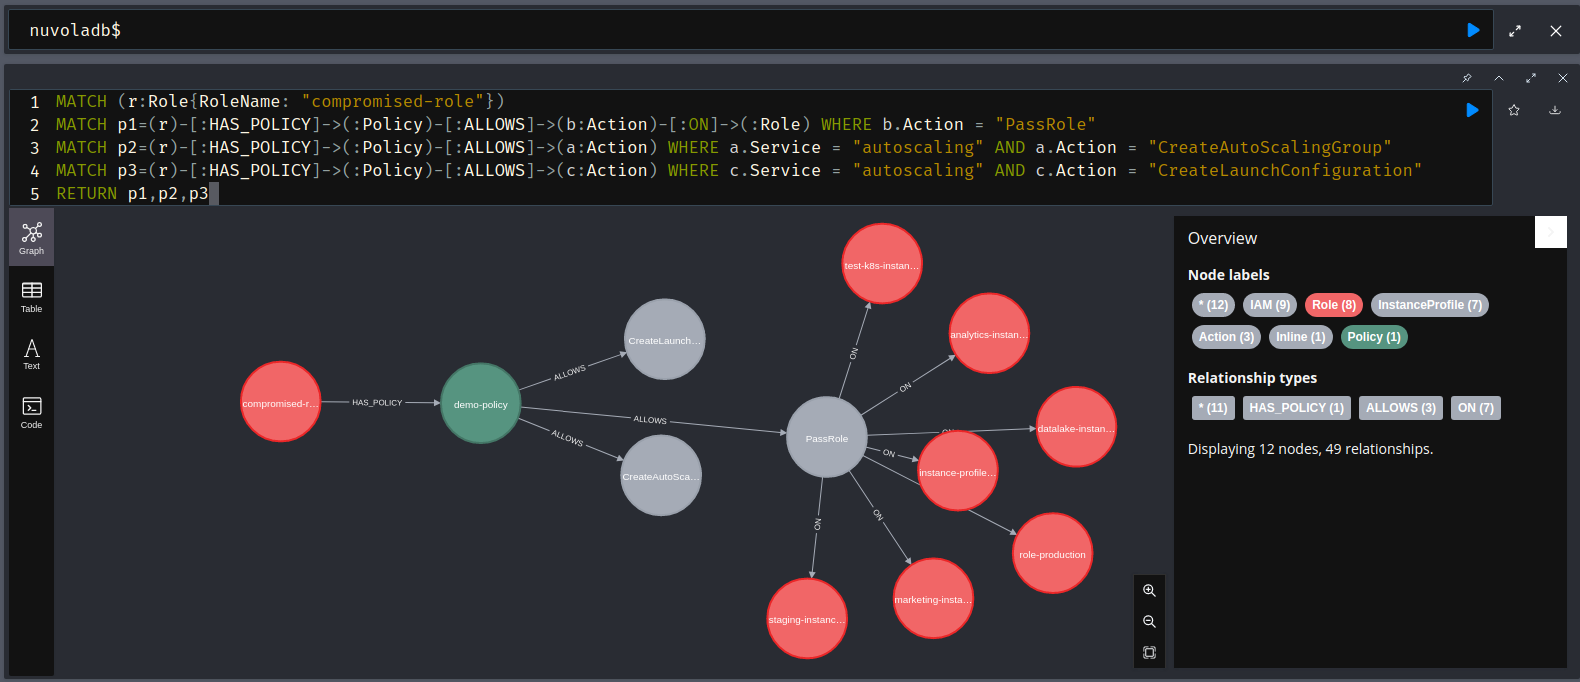 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 doyensec/malicious-devfile-registry
CVE-2024-0402 exploit for GitLab Workspaces using a malicious Devfile Registry with path-traversal archive to overwrite authorized_keys and gain SSH…
 d3vzer0/cnc-relay
Docker projects to retain beacon source IPs using C2 relaying infra