CVE-2019-14223
 mbadanoiu/cve-2019-14223
CVE-2019-14223: Open Redirect in Alfresco Share
exploitationinformation-gatheringpenetration-testing+3
mbadanoiu/cve-2019-14223CVE-2019-14223: Open Redirect in Alfresco Share
 r0xdb/cve-2024-23897
Jenkins 2.441 and earlier, LTS 2.426.2 and earlier does not disable a feature of its CLI command parser that replaces an '@' character followed by a…
 shimon03/explora-o-rce-n-o-autenticado-jetbrains-teamcity-cve-2024-27198-
Em fevereiro de 2024, foi identificado duas novas vulnerabilidades que afetam o servidor JetBrains TeamCity (CVE-2024-27198 e CVE-2024-27199)
 pumpkinpiteam/cve-2022-24716
Python exploit for CVE-2022-24716: arbitrary file disclosure in Icinga Web 2 versions <2.8.6, <2.9.6, <2.10. Usage: python3 exploit.py -u <url> -f…
 huzaifahussain98/cve-2020-23585
cross-site request forgery (CSRF) attack on "OPTILINK OP-XT71000N Hardware Version: V2.2 , Firmware Version: OP_V3.3.1-191028".
 h3x0v3rl0rd/cve-2019-14287
Shell script to detect CVE-2019-14287 sudo privilege escalation vulnerability. Scans systems for the flaw and reports affected configurations.
 exploitwritter/cve-2022-25063
This script exploits a vulnerability (XSS) in the TPLink WR840N router, using a field for injecting javascript code.
 aryanguenthner/darkfox
CTI Cyber Threat Intelligence OSINT Dark Web Deep Web Research. Ransomware gang information gathering tool.
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
 byt3bl33d3r/sprayingtoolkit
Scripts to make password spraying attacks against Lync/S4B, OWA & O365 a lot quicker, less painful and more efficient
 dievus/lnkbomb
Malicious shortcut generator for collecting NTLM hashes from insecure file shares.
 0x4d31/honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…
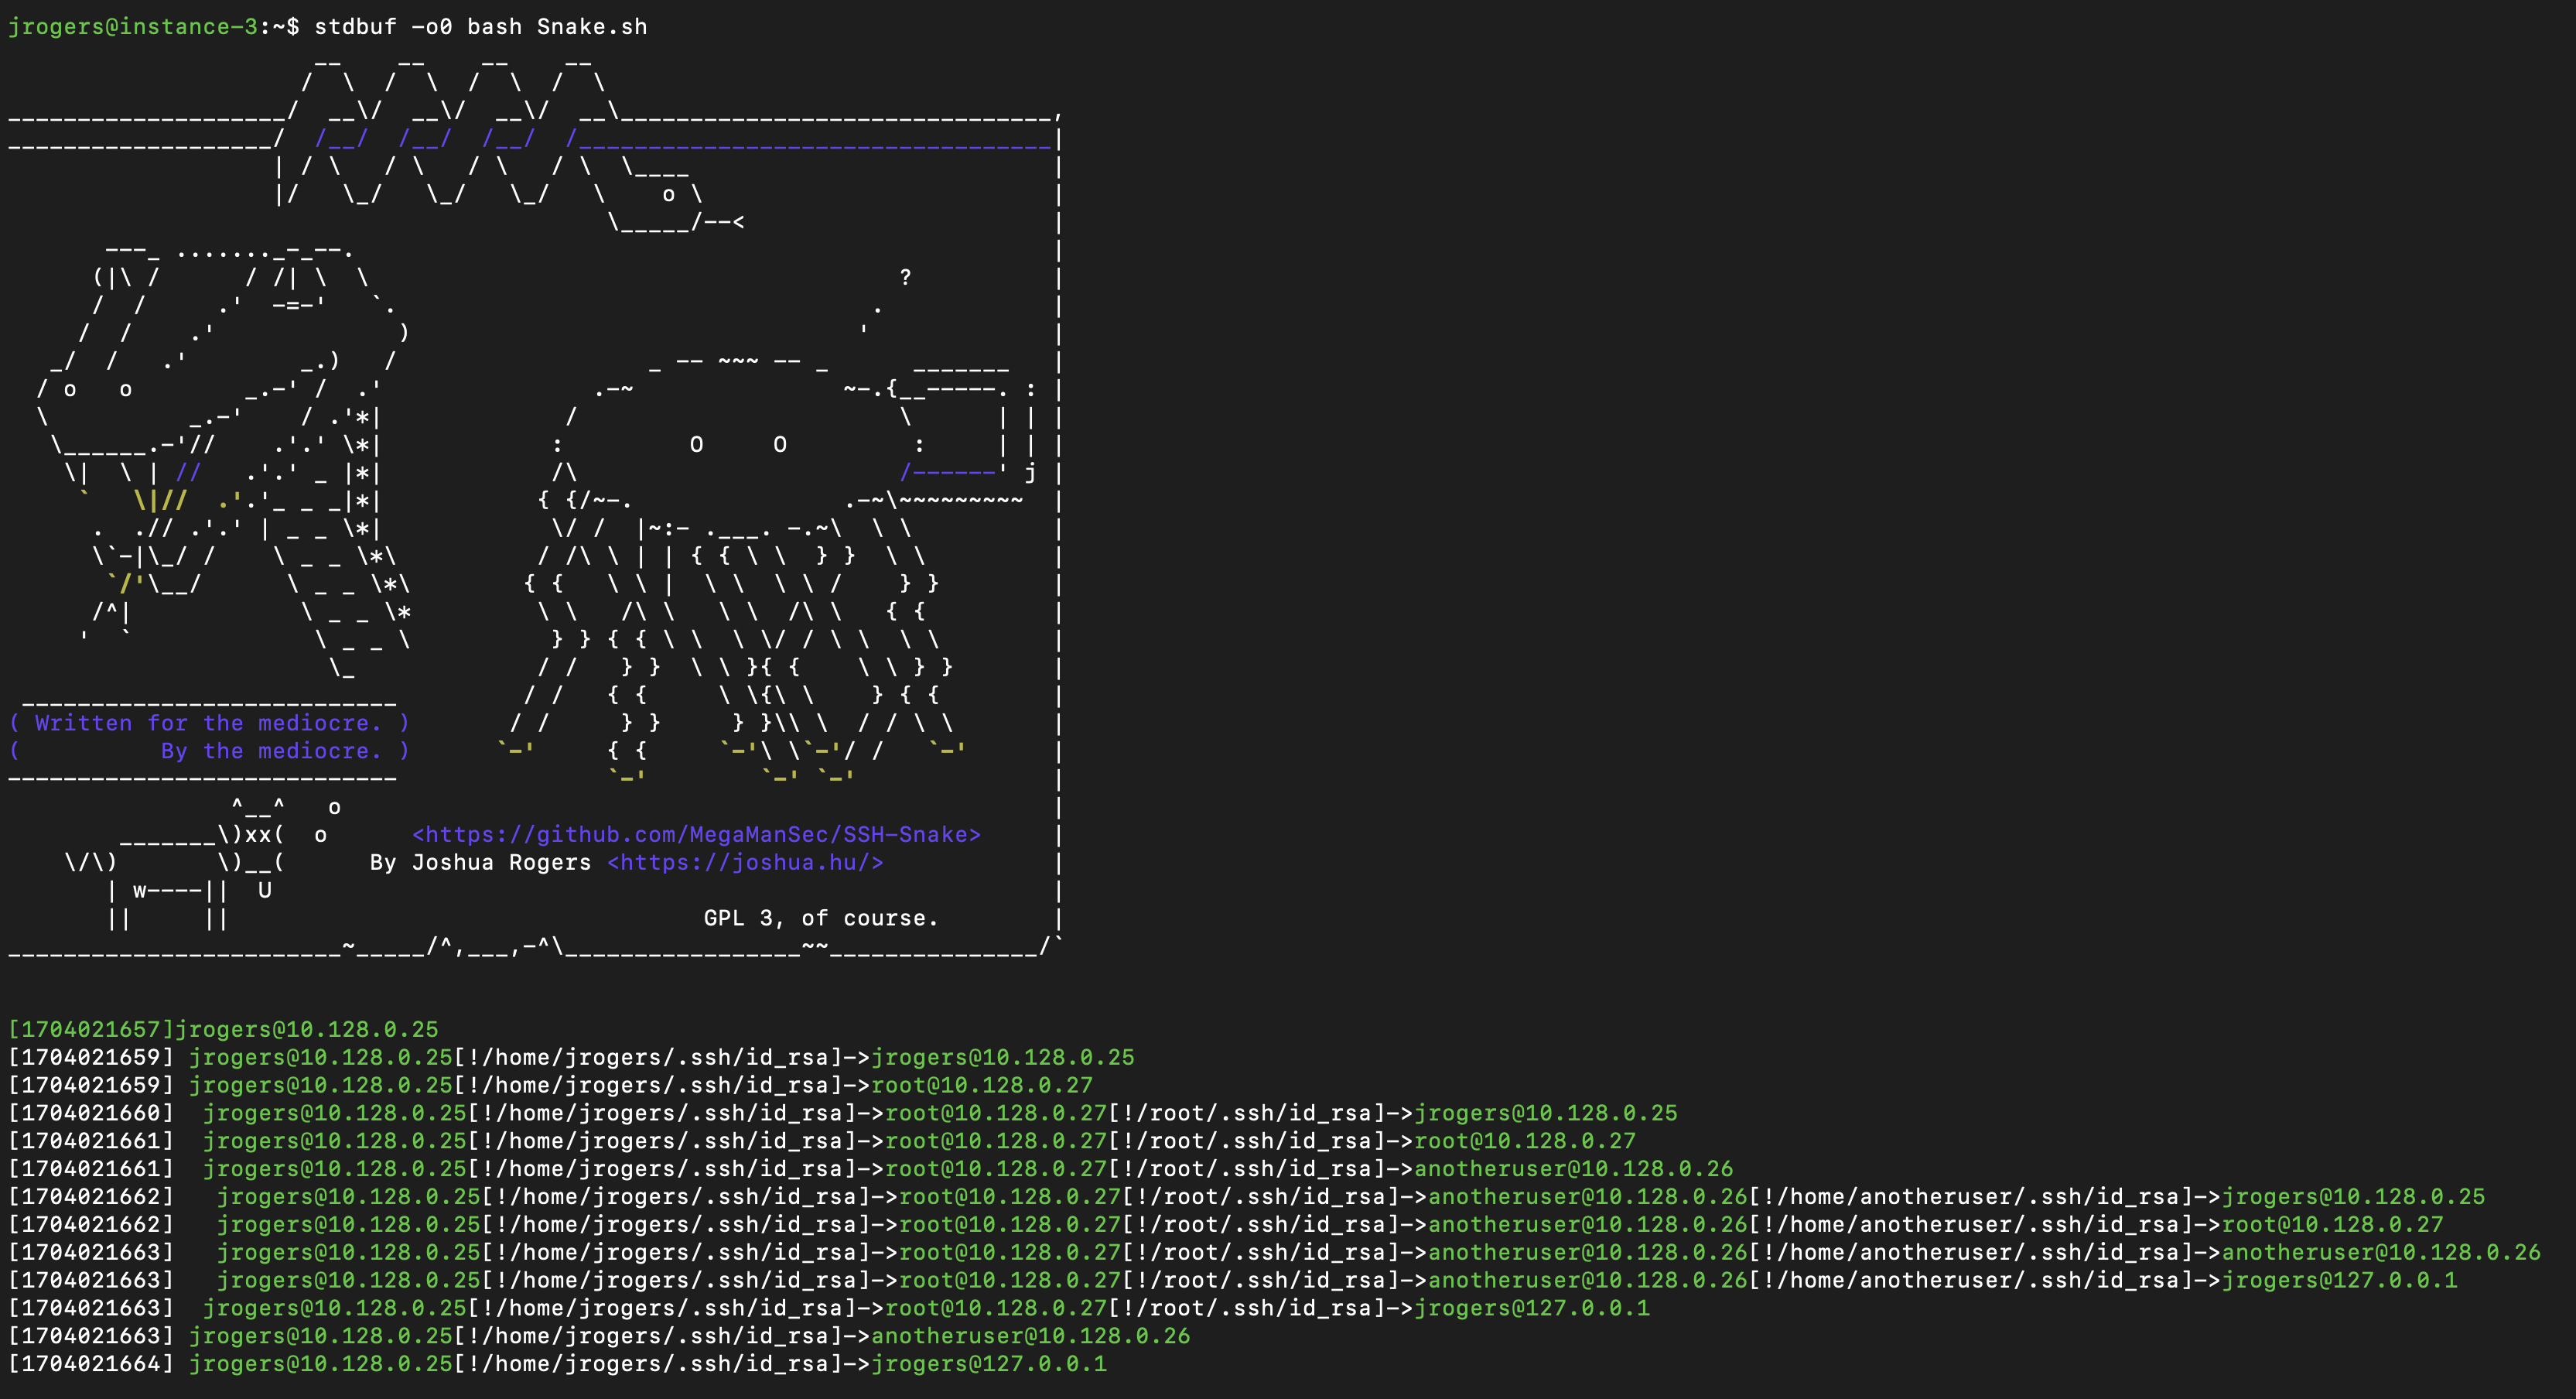 megamansec/ssh-snake
SSH-Snake is a self-propagating, self-replicating, file-less script that automates the post-exploitation task of SSH private key and host discovery.
 spiderlabs/portia
Portia aims to automate a number of techniques commonly performed on internal network penetration tests after a low privileged account has been…
 ivanvza/arpy
Mac OSX ARP spoof (MiTM) tool that can also plug into Gource
 bloodhoundad/sharphound3
C# Data Collector for the BloodHound Project, Version 3