
giskard-oss
 giskard-ai/giskard-oss
🐢 Open-Source Evaluation & Testing library for LLM Agents
adversarial-attackai-securityfuzzing+3
5.8k
giskard-ai/giskard-oss🐢 Open-Source Evaluation & Testing library for LLM Agents
 meshcore-dev/meshcore
A new lightweight, hybrid routing mesh protocol for packet radios
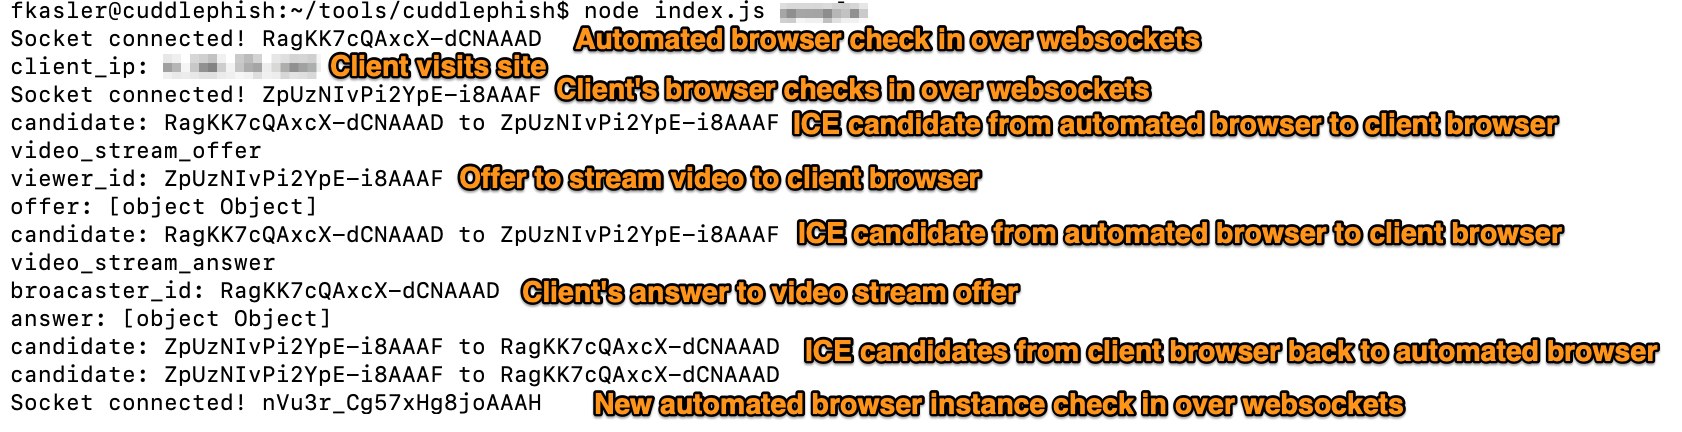 fkasler/cuddlephish
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 vampsecure-labs/vamp-forticheck
VampSecure Labs: FortiOS CVE scanner (CVE-2018-13379, CVE-2022-40684, CVE-2023-27997, CVE-2024-21762)
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.

 cognitive-functors/c4-meta-system
Production AI defense with 7-layer protection: mathematical constraints, object-capability access, distributed O2 consensus, SVETILO ethics. First…
 gmh5225/cheat-engine-undetectable
Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).
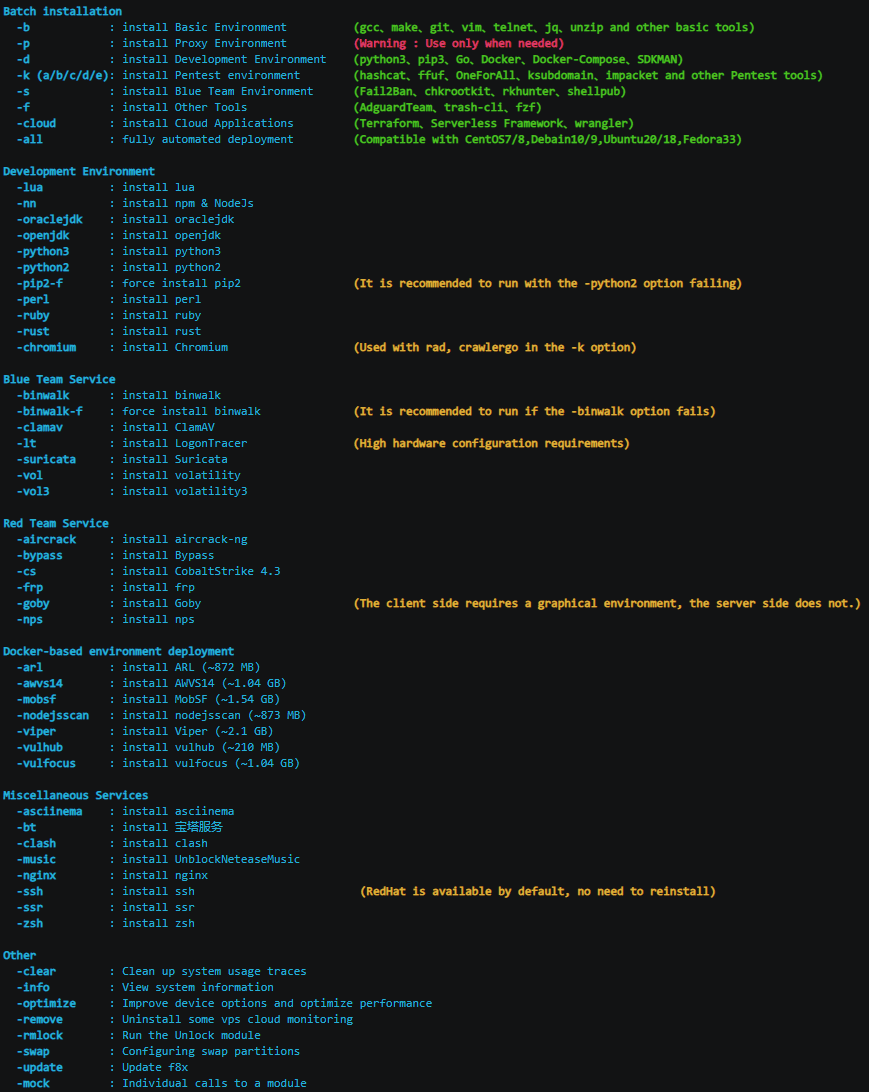 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 404tk/cloudtoolkit
Authorized cloud adversary simulation and validation toolkit
 portbuster1337/lpe-toolkit
Multi-architecture Linux privilege escalation toolkit with 24 pre-built and runtime-compilable exploits. Auto-detects kernel version, filters patched…
 fomovet/cve-2025-29384
POC for CVE-2025-29384
 zedxod/cve-2026-41940-poc
Proof-of-concept exploit for CVE-2026-41940, demonstrating authentication bypass in cPanel/WHM via CRLF injection and session poisoning to gain…
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 safelineman/agentic-soc-simulation
AI 驱动的 SOC 仿真平台
 sachinart/cve-2025-54322
CVE-2025-54322 - XSpeeder SXZOS Pre-Auth RCE 0day Finder Quick
 cybertechajju/r2c-cve-2025-55182-66478
🔥 React2Shell Toolkit - CVE-2025-55182 & CVE-2025-66478