
fuel-cms-cve-2018-16763-python3-port
 shadowr-root/fuel-cms-cve-2018-16763-python3-port
Maintained Python 3 port of the original FUEL CMS CVE-2018-16763 proof-of-concept.
educationexploitationpenetration-testing+3
shadowr-root/fuel-cms-cve-2018-16763-python3-portMaintained Python 3 port of the original FUEL CMS CVE-2018-16763 proof-of-concept.
 instructor-admin/multi-threaded-mass-exploiter-cve-2018-13379-poc
CVE-2018-13379 mass exploiter for Fortinet FortiOS SSL VPN. Extracts credentials instantly, saves to CSV + PostgreSQL. Multi-threaded, no bullshit…
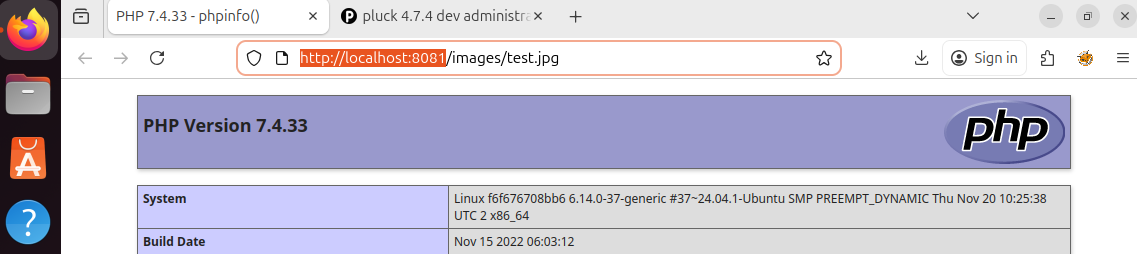 purgemebaby/cve-2018-11736
PoC exploit for CVE-2018-11736 affecting Pluck CMS versions prior to 4.7.7-dev2 with a File Upload Vulnerability
 lukehebe/cve-2018-1049-poc
Remote privilege escalation exploit for CVE-2018-1049 targeting VyOS via SSH-based command injection in a sudo-permitted Perl script, granting root…
 blueisbeautiful/cve-2018-19323
An exploitation framework for CVE-2018-19323 - GIGABYTE GDrv privilege escalation vulnerability with multi-architecture support and framework…
 hdbreaker/cve-2018-16119
TP-Link TL-WR1043ND - Authenticated Remote Code Execution
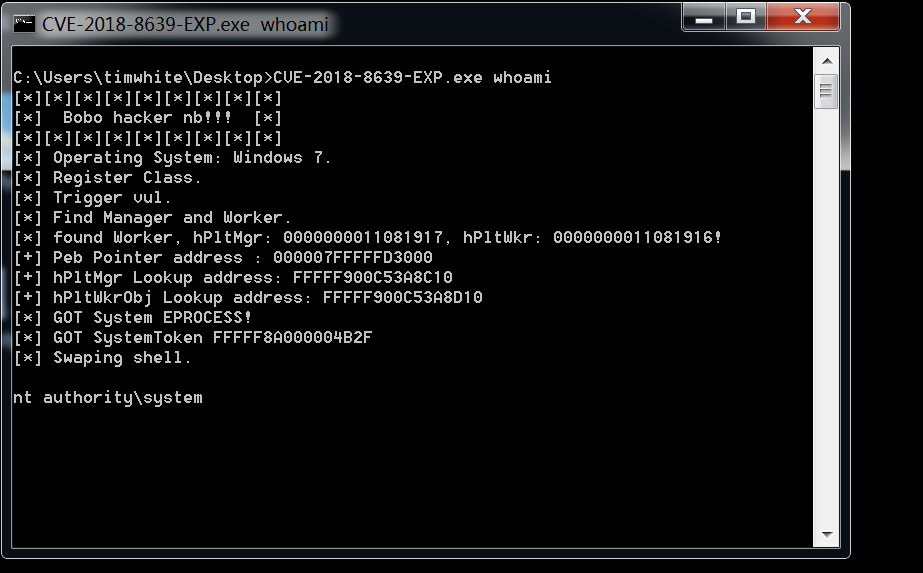 timwhitez/cve-2018-8639-exp
CVE-2018-8639-EXP
 axcheron/crestron_getsudopwd
Tool to exploit CVE-2018-13341 and recover hidden account password on Crestron devices
 scanfsec/cve-2018-15982
Aggressor Script to launch IE driveby for CVE-2018-15982.
 synacktiv/exim-cve-2018-6789
PoC materials to exploit CVE-2018-6789
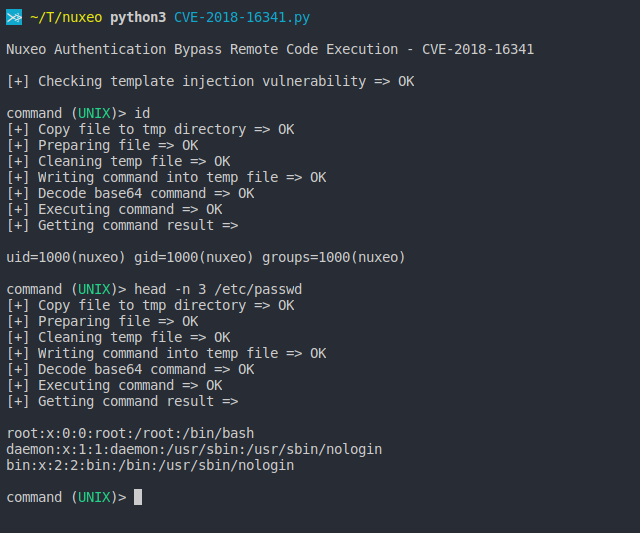 mpgn/cve-2018-16341
CVE-2018-16341 - Nuxeo Remote Code Execution without authentication using Server Side Template Injection
 arkangel-dev/cve-2018-20250-winrar-ace-gui
CVE-2018-20250-WINRAR-ACE Exploit with a UI
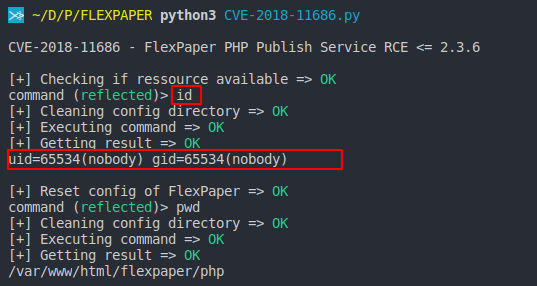 mpgn/cve-2018-11686
CVE-2018-11686 - FlexPaper PHP Publish Service RCE <= 2.3.6
 stigtsp/cve-2018-20162-digi-lr54-restricted-shell-escape
Proof-of-concept exploit for CVE-2018-20162: sandbox escape in Digi TransPort LR54 LTE router via SIGINT handling flaw, yielding root shell access.
 anonymouz4/apple-remote-crash-tool-cve-2018-4407
Crashes any macOS High Sierra or iOS 11 device that is on the same WiFi network