
pfsense-cp-ha-pfctl
 abraxas/pfsense-cp-ha-pfctl
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - CP HA host into pfctl
command-and-controlexploitationlabs-practice+4
abraxas/pfsense-cp-ha-pfctlpfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - CP HA host into pfctl

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 f0xox/cve-2026-32202
Technical analysis of CVE-2026-32202, a zero-click NTLM credential coercion via crafted .lnk Control Panel applet items in Windows Explorer.
 skander1337/winrar-exploit
C++ implementation of CVE-2025-8088 WinRAR exploit using Alternate Data Streams to drop payloads into Windows Startup folder for persistence.
 simoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover
Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
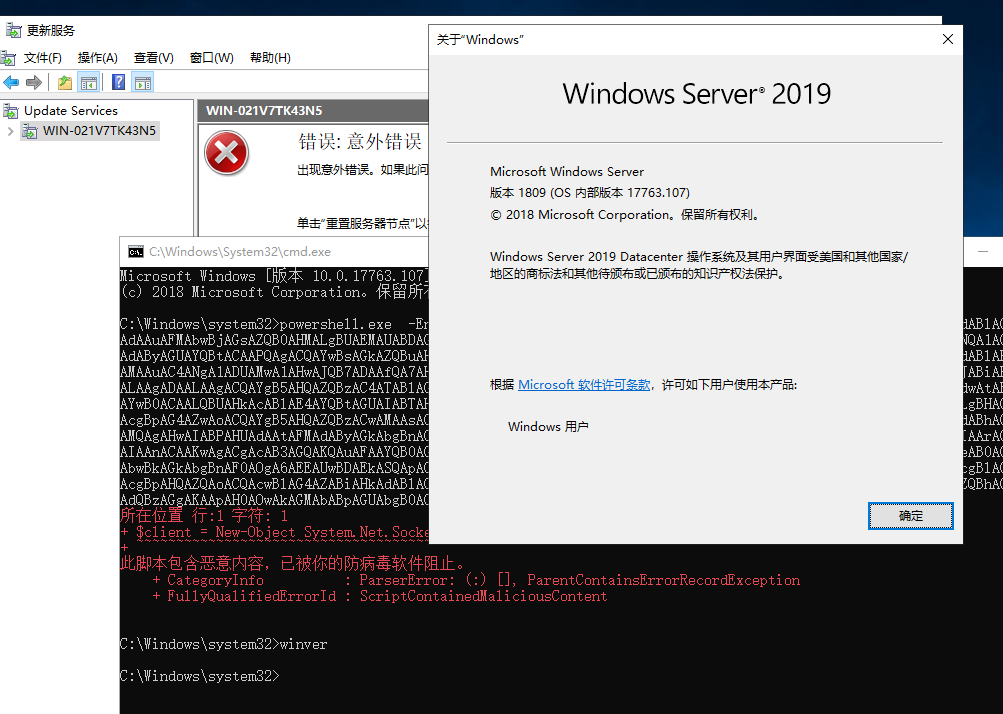 0x7556/cve-2025-59287
Exploit for CVE-2025-59287, injecting WolfShell memory webshell into WSUS servers to achieve remote code execution when the admin console is opened.
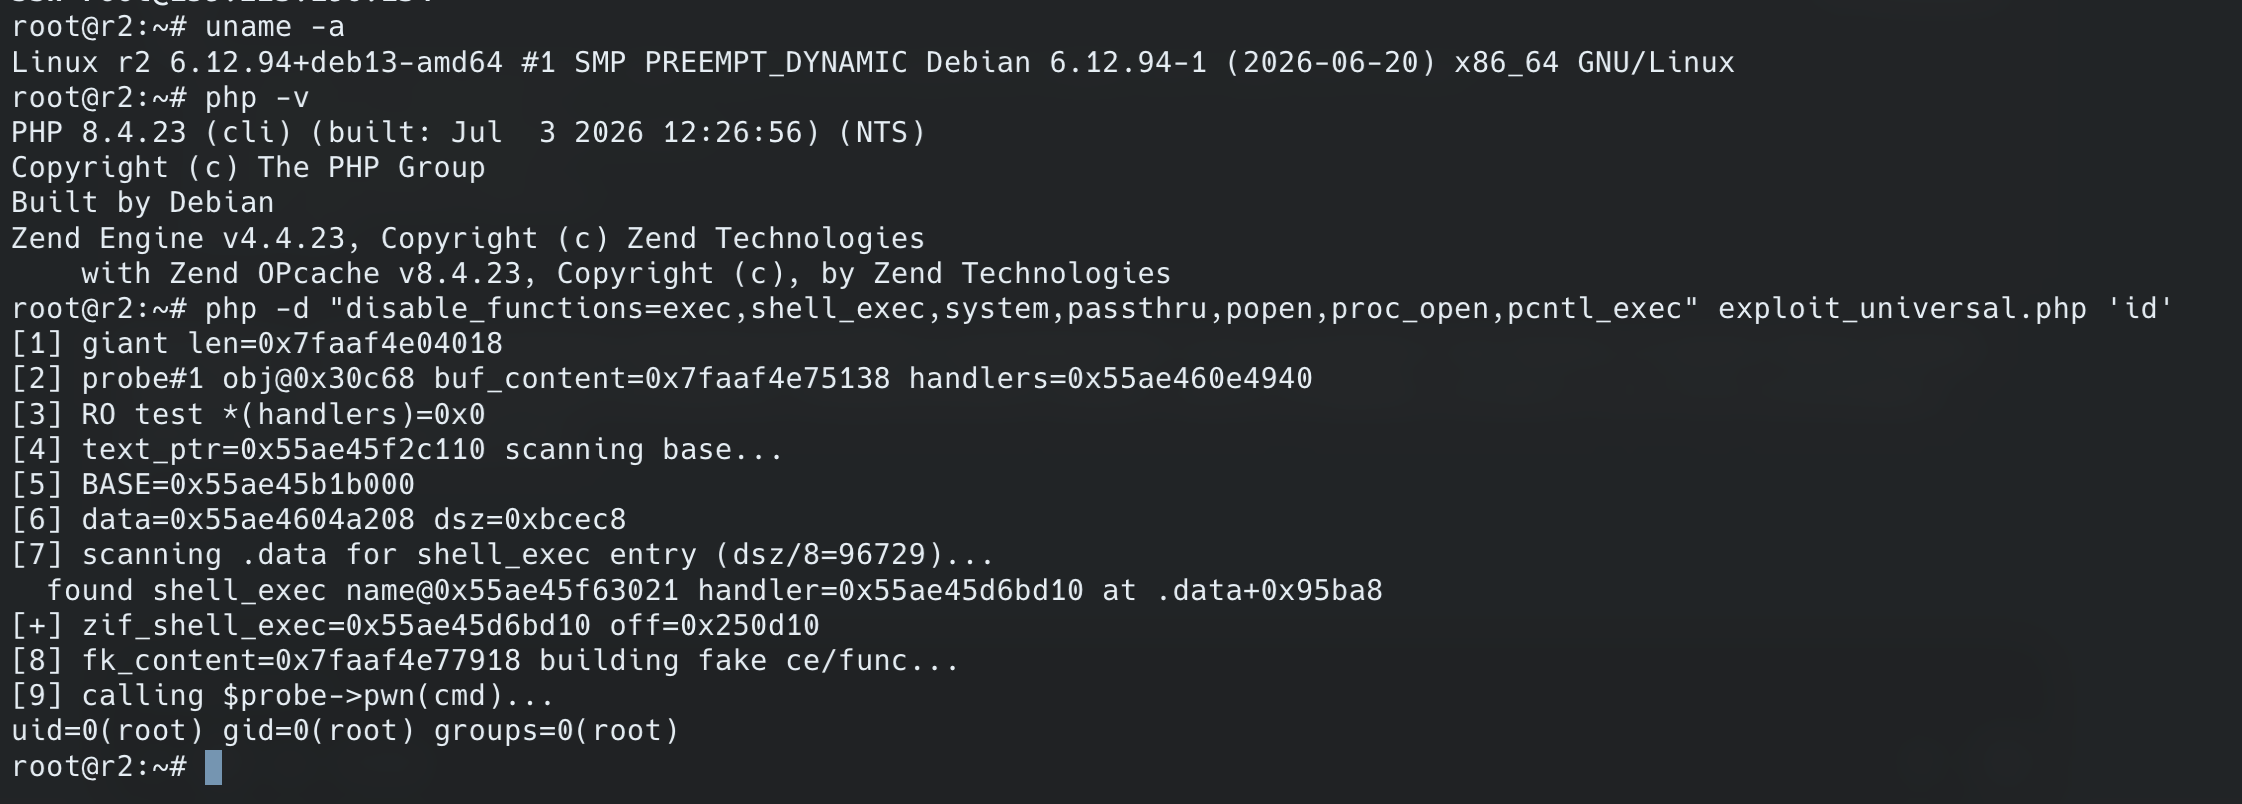 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
 codextf2/burp2malleable
Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 oscerd/cve-2026-49086
PoC reproducer for CVE-2026-49086 demonstrating a confused-deputy routing-header override in Apache Camel camel-dapr, enabling message redirection…
 mcipekci/wp2shell
Pre-auth RCE PoC for WordPress core — chains CVE-2026-63030 (REST /batch/v1 route-confusion desync) with CVE-2026-60137 (author__not_in SQLi) into an…
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 sofianeelhor/cve-2023-22621-poc
CVE-2023-22621: SSTI to RCE by Exploiting Email Templates affecting Strapi Versions <=4.5.5
 tzwlhack/cve-2018-20250
Automated exploit script for CVE-2018-20250 (WinRAR ACE extraction code execution) that generates a malicious archive file embedding a payload into…
 shinthink/cve-2026-57517
💉 Blind SQL Injection → RCE exploit for Control Web Panel (CWP) ≤ 0.9.8.1224 — userRes POST → INTO DUMPFILE → cwpsvc shell
 mayaseven/cve-2019-12562
Stored Cross-Site Scripting in DotNetNuke (DNN) Version before 9.4.0 | XSS to RCE
 ozcanpng/cve-2025-57819-freepbx-rce2root
Full-chain CVE-2025-57819 PoC for FreePBX 15, 16, and 17: unauthenticated SQLi to RCE and root takeover.