

begal-c2
 xsanflip/begal-c2
Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
command-and-controldata-exfiltrationeducation+6
8
xsanflip/begal-c2Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 yahiahamza/cve-2026-25099
Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…
 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
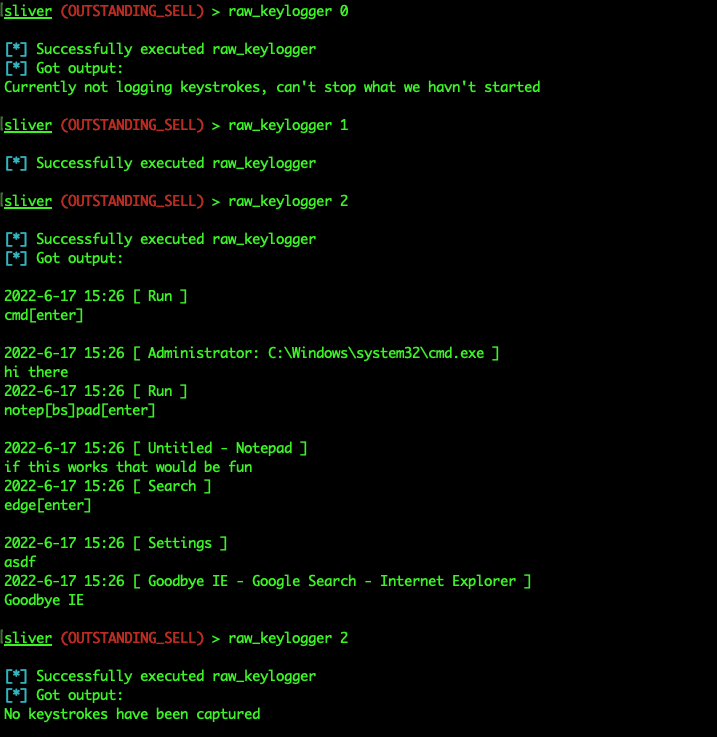 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 daddycocoaman/azbelt
AAD related enumeration in Nim
 al1ex/extensionhijack
ExtensionHijack
 synacktiv/extloader
A chromium extension exploitation toolkit
 und3rf10w/external_c2_framework
Python api for usage with cobalt strike's External C2 specification
 xorrior/apfell-chrome-extension-c2server
Apfell C2 Server for the Google Chrome Extension Payload
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
 shinthink/cve-2026-48939
Pre-auth arbitrary file upload RCE exploit for iCagenda Joomla extension < 4.0.8 (CVSS 10.0)
 nephila016/cve-2025-55319-poc
PoC for CVE-2025-55319
 nxploited/cve-2024-31114
Shortcode Addons <= 3.2.5 - Authenticated (Admin+) Arbitrary File Upload
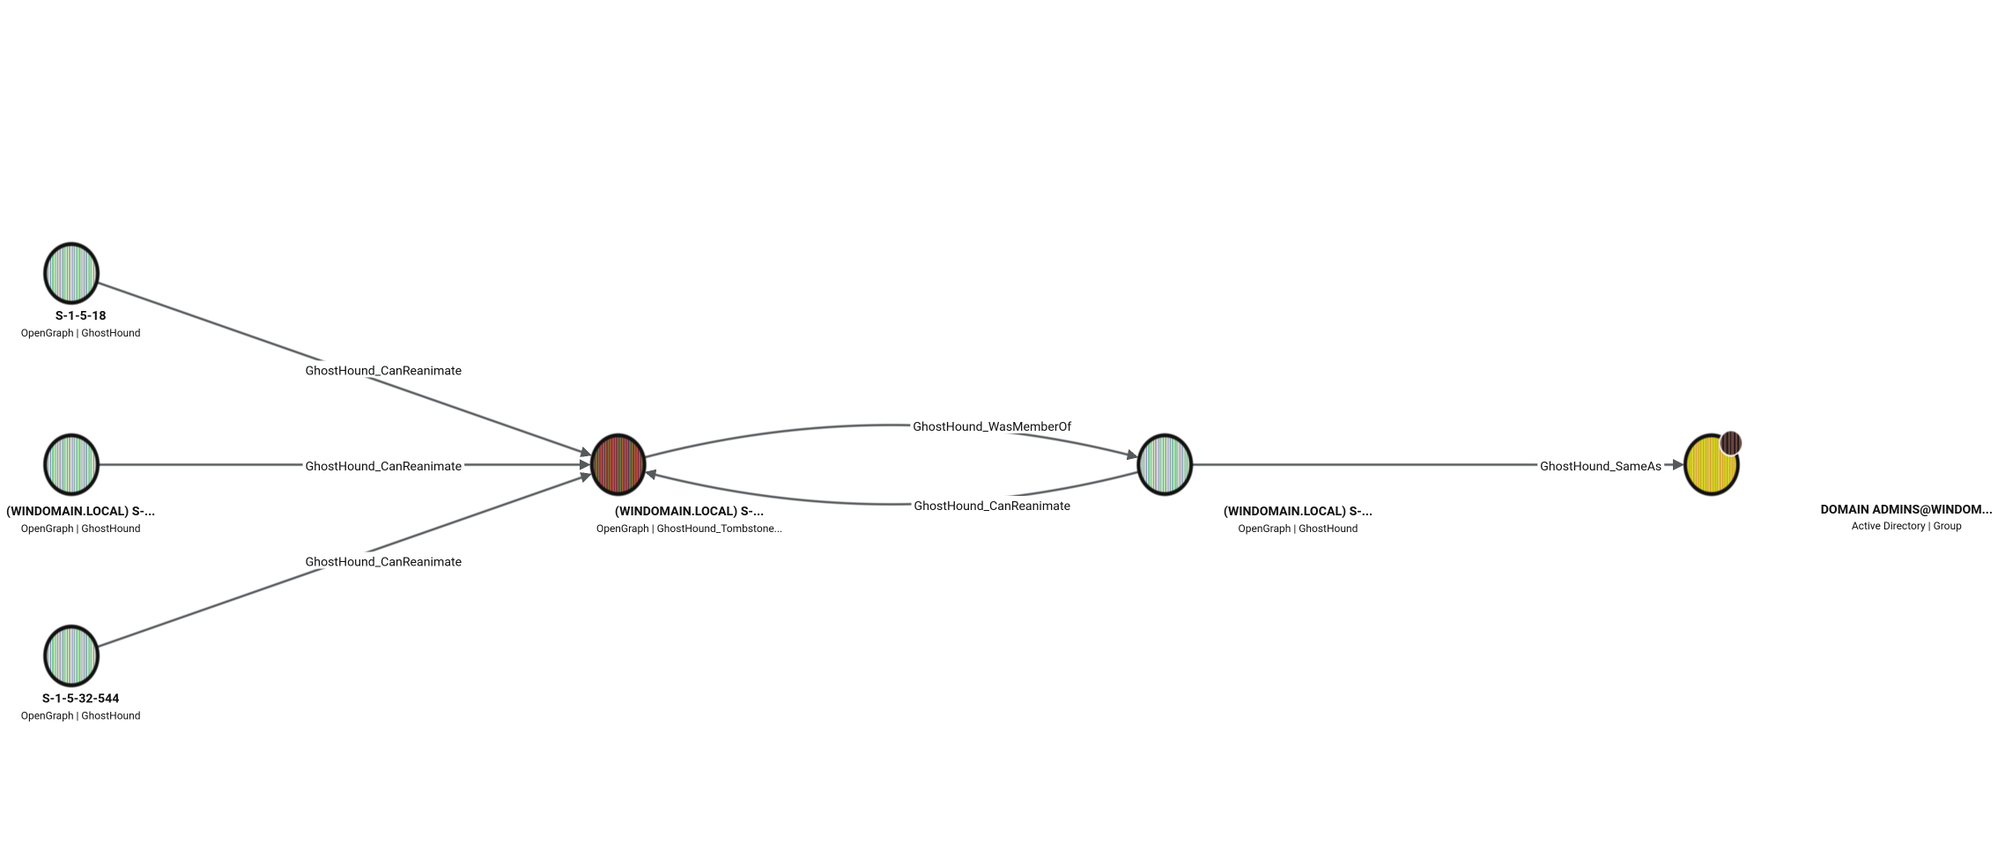 jvbotelho/ghosthound
GhostHound is a BloodHound OpenGraph extension that surfaces Active Directory tombstone reanimation as a first-class attack path, enumerating deleted…
 chiefyoru/cve-2026-48907_poc
Unauthenticated Remote Code Execution (RCE) vulnerability in the JCE (Joomla Content Editor) extension for Joomla