Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
13 results
xz-utils-backdoor-case-study preview

xz-utils-backdoor-case-study

GitHubmichel-dv/xz-utils-backdoor-case-study

Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…

educationincident-responsemalware-analysis+6
19 days ago
cve-2026-64638-banner-poc preview

cve-2026-64638-banner-poc

GitHubxal6/cve-2026-64638-banner-poc

Generates a self-submitting HTML trigger page that exploits a reflected HTML injection in WordPress login (CVE-2026-64638) to display a custom…

exploitationpenetration-testingred-teaming+3
1 month ago
GraphSpy preview

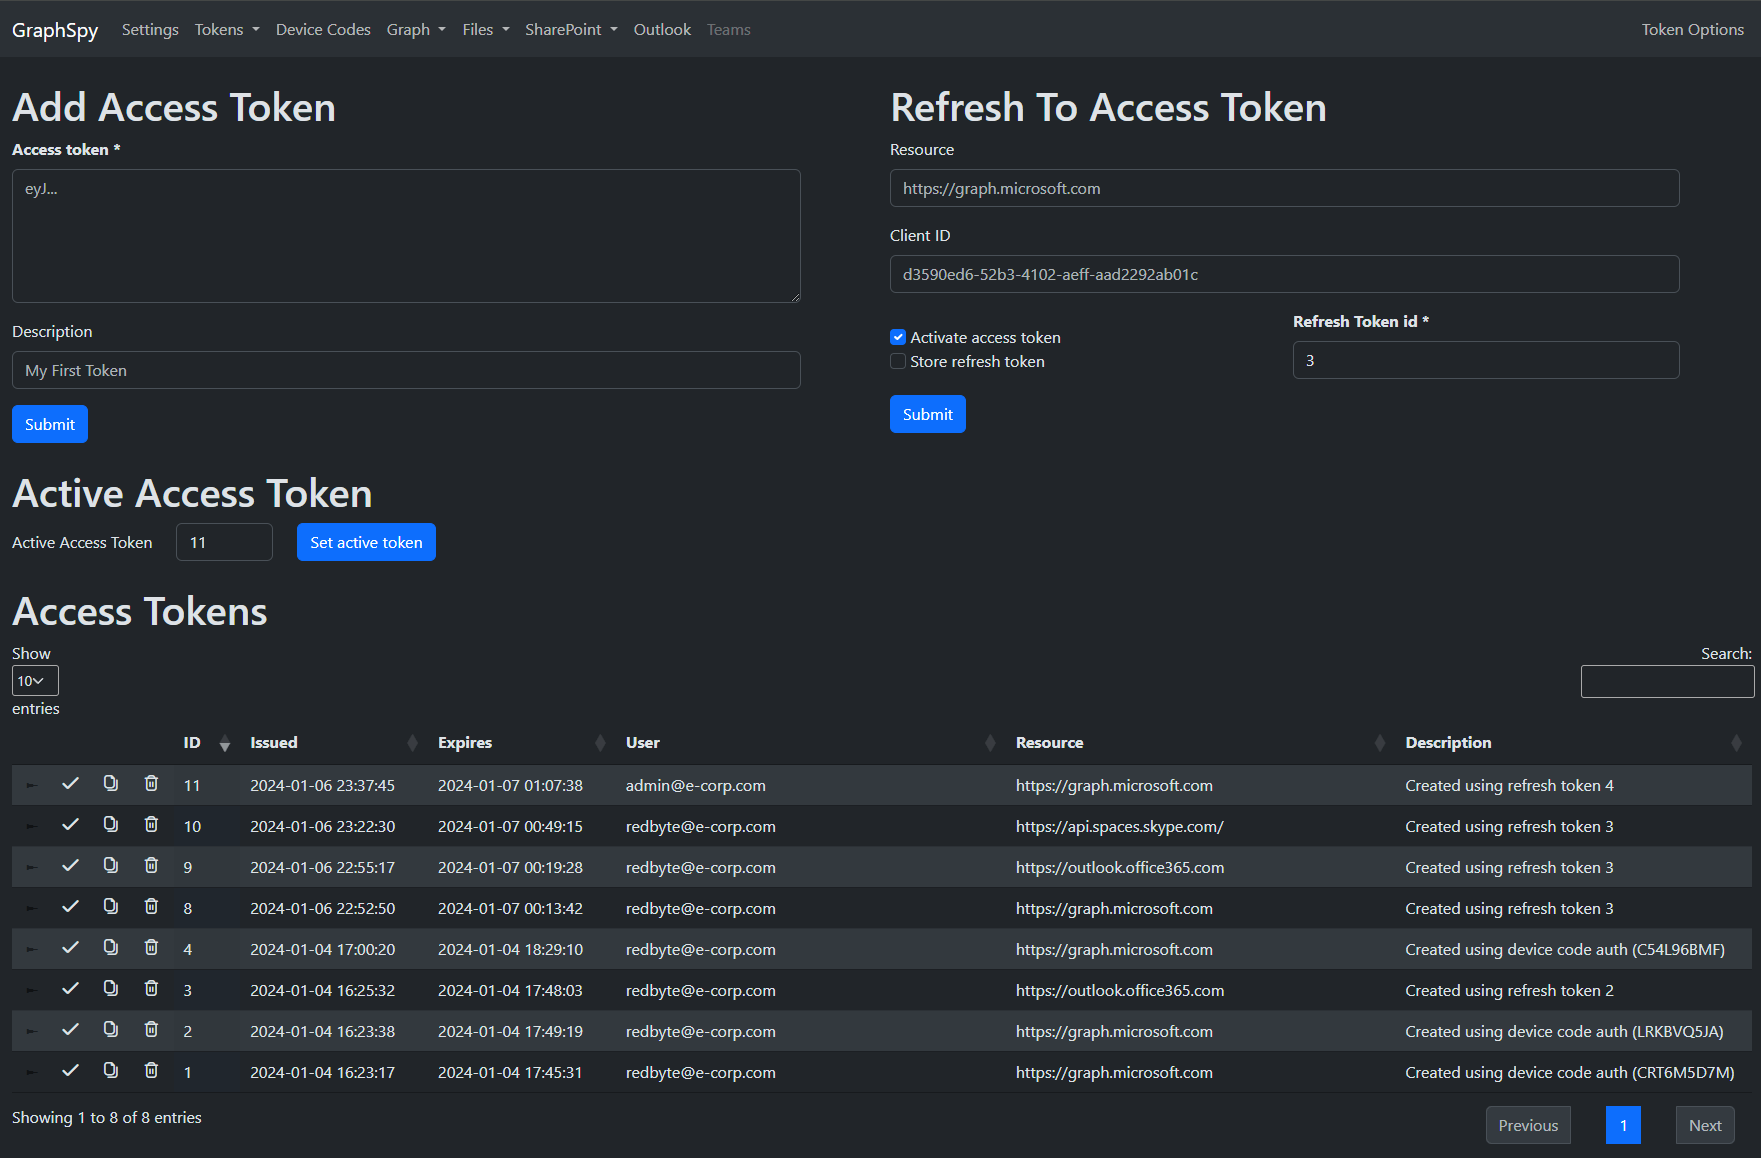
GraphSpy

GitHubredbyte1337/graphspy

Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI

authenticationcloud-securitydata-exfiltration+6
1.4k1 month ago
airecon preview

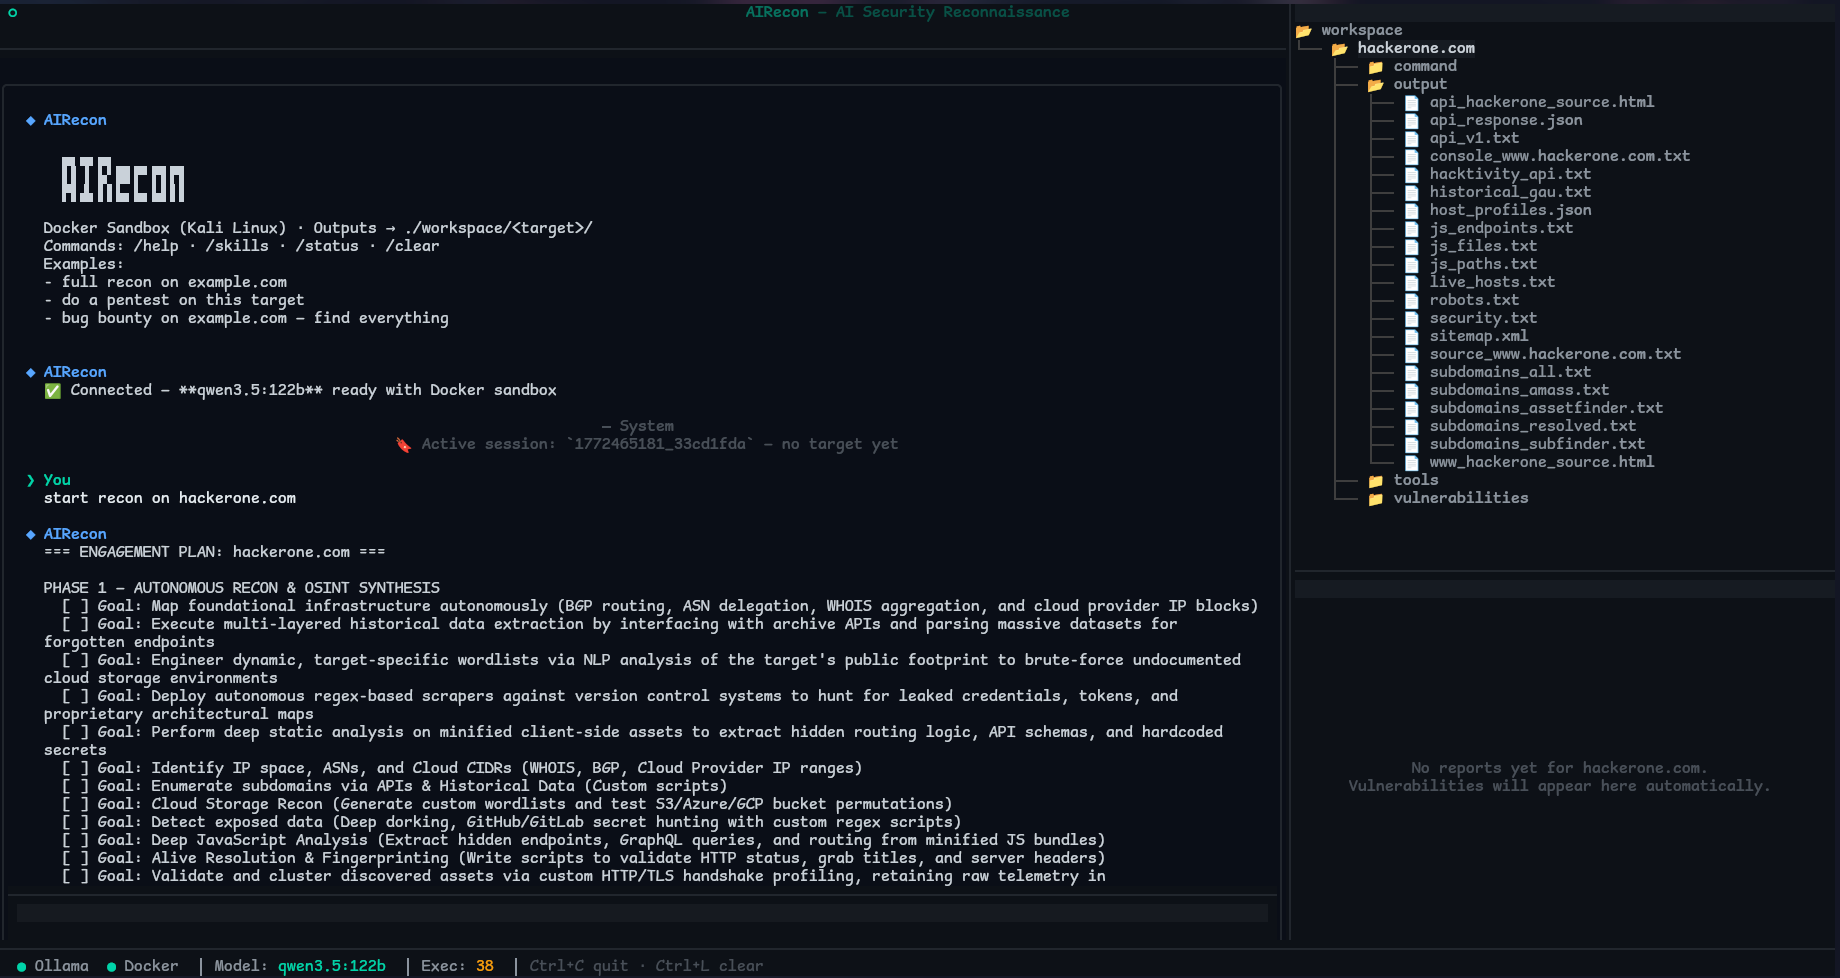
airecon

GitHubpikpikcu/airecon

AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…

ai-securityeducationexploitation+6
1.1k23 days ago
CVE-2025-9074-Docker-Desktop-API-Escape-PoC preview

CVE-2025-9074-Docker-Desktop-API-Escape-PoC

GitHubmedaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc

Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…

cloud-securitycontainer-escapeexploitation+3
4 months ago
malicious-devfile-registry preview

malicious-devfile-registry

GitHubdoyensec/malicious-devfile-registry

CVE-2024-0402 exploit for GitLab Workspaces using a malicious Devfile Registry with path-traversal archive to overwrite authorized_keys and gain SSH…

exploitationpenetration-testingred-teaming+3
151 year ago
ClickOnceBlobber preview

ClickOnceBlobber

GitHubdazzyddos/clickonceblobber

Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…

command-and-controlpayload-developmentred-teaming+1
1687 months ago
AlanFramework preview

AlanFramework

GitHubenkomio/alanframework

A C2 post-exploitation framework

command-and-controlencryption-decryption-toolslateral-movement+7
4852 years ago
SharpFtpC2 preview

SharpFtpC2

GitHubdarkcodersc/sharpftpc2

A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.

adversarial-attackcommand-and-controleducation+3
912 years ago
OffensiveRust preview

OffensiveRust

GitHubtrickster0/offensiverust

Rust Weaponization for Red Team Engagements.

binary-exploitationcommand-and-controleducation+9
3.0k3 years ago
sdk preview

sdk

GitLabcosignet/sdk

Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.

api-securityauthenticationauthentication-authorization+3
2 months ago
proxy.py preview

proxy.py

GitHubabhinavsingh/proxy.py

💫 Ngrok FRP Alternative • ⚡ Fast • 🪶 Lightweight • 0️⃣ Dependency • 🔌 Pluggable • 😈 TLS interception • 🔒 DNS-over-HTTPS • 🔥 Poor Man's VPN • ⏪…

penetration-testingred-teamingutilities-frameworks+1
3.6k1 year ago
LAZYPARIAH preview
Archived

LAZYPARIAH

GitHuboctetsplicer/lazypariah

A tool for generating reverse shell payloads on the fly.

command-and-controlctfexploitation+5
16 months ago