
giskard-oss
 giskard-ai/giskard-oss
🐢 Open-Source Evaluation & Testing library for LLM Agents
adversarial-attackai-securityfuzzing+3
giskard-ai/giskard-oss🐢 Open-Source Evaluation & Testing library for LLM Agents
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
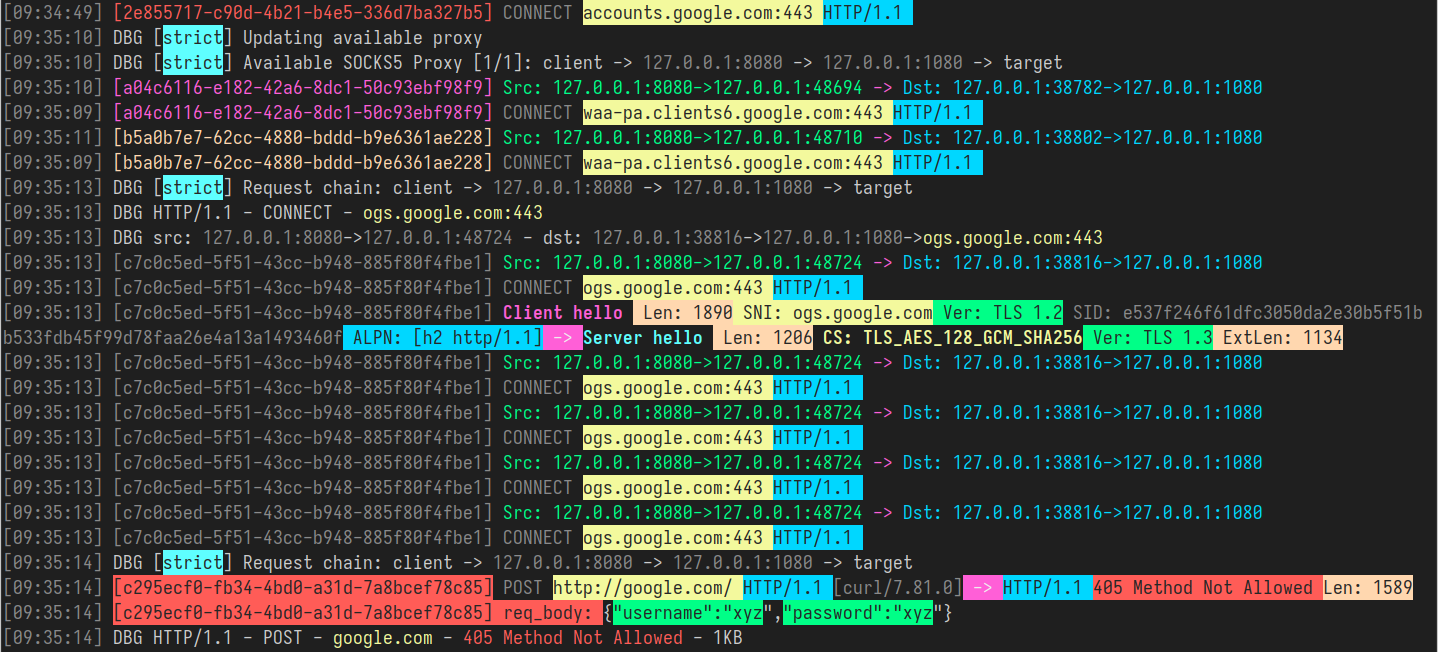 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
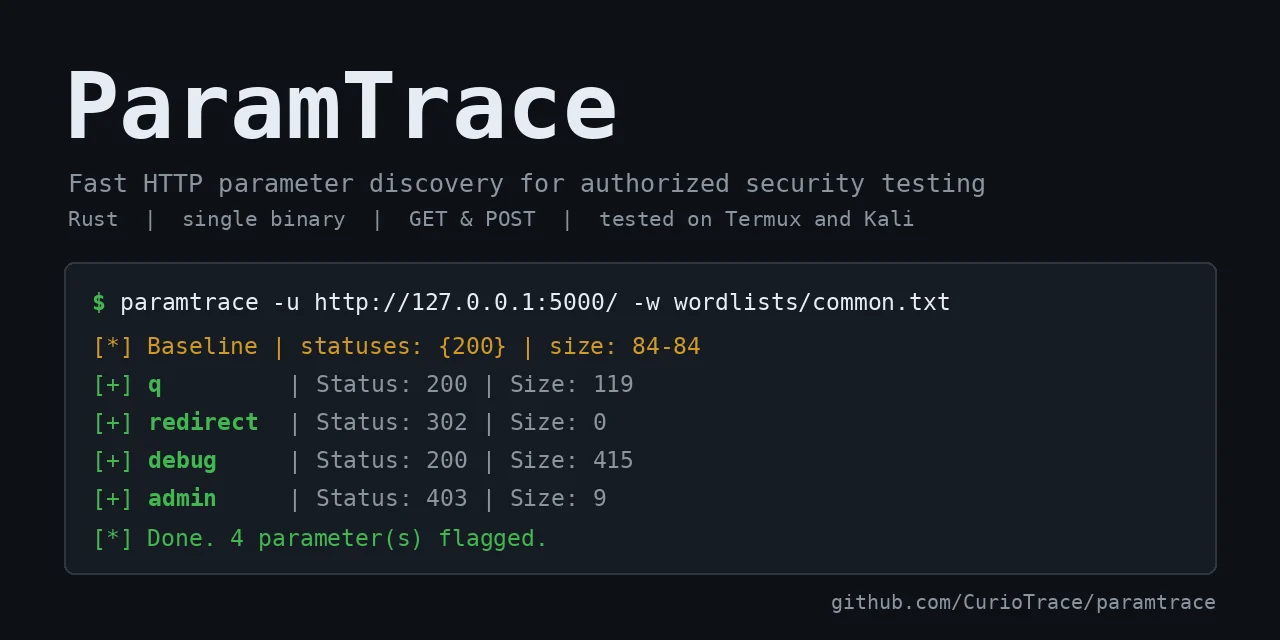 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
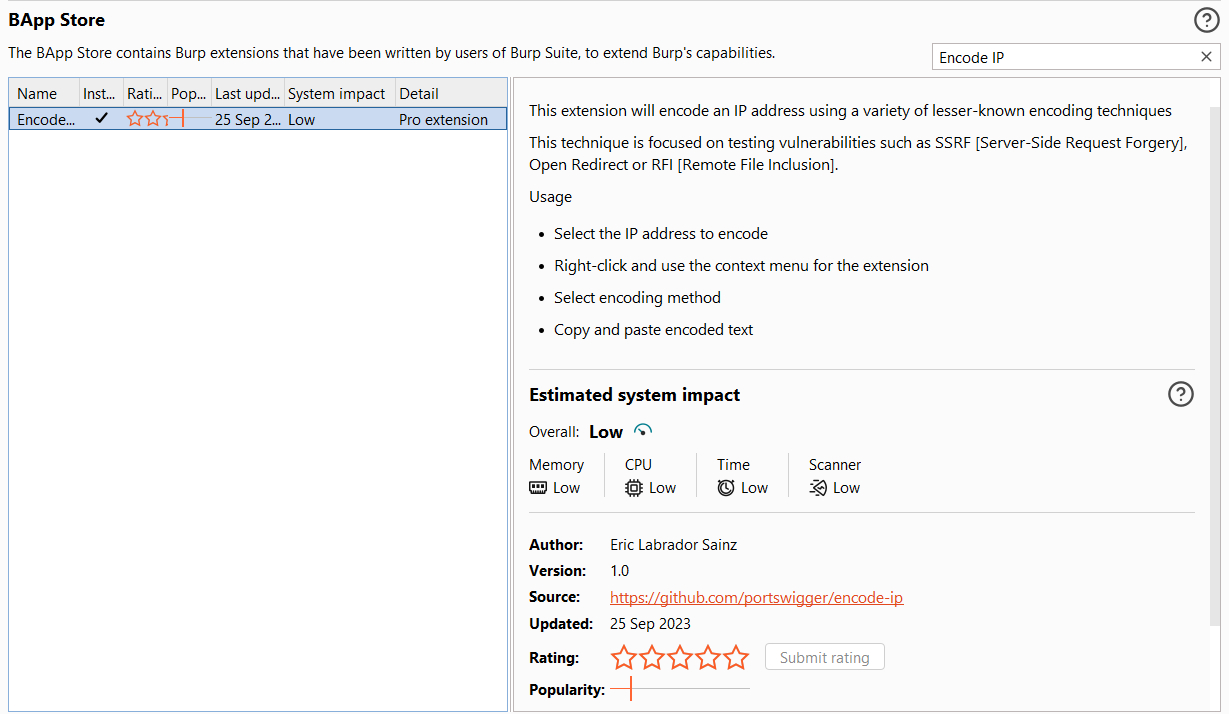 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 ustayready/fireprox
AWS API Gateway management tool for creating on the fly HTTP pass-through proxies for unique IP rotation
 wattocyber/lm-fingerprint
Fingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.
 halit/isip
Interactive sip toolkit for packet manipulations, sniffing, man in the middle attacks, fuzzing, simulating of dos attacks.
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
 dsecuredcom/ffufpostprocessing
Golang tool which helps dropping the irrelevant entries from your ffuf result file.
 mandatoryprogrammer/judasdns
Nameserver DNS poisoning attacks made easy
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
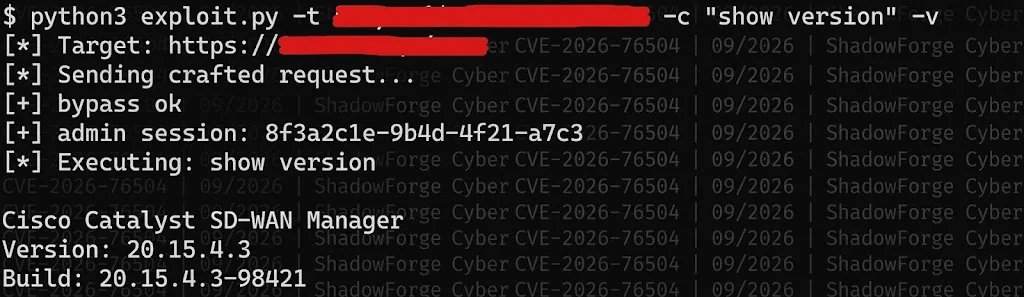 shadowforge-cyber/cve-2026-76504-proof-of-concept
EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)
 randomrobbiebf/kong-pwn
Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls